
dicerosbicornis
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
command-and-controldata-exfiltrationencryption-decryption-tools+5
16
maldevel/dicerosbicornisA fully featured Windows backdoor that uses email as a C&C server
 d4op/cve-2023-51764-poc
Python 3 proof-of-concept for CVE-2023-51764 SMTP smuggling vulnerability, enabling email spoofing via crafted SMTP sessions.
 aramosf/cve-2026-54433
Configurable Python PoC for CVE-2026-54433, a stored XSS in Roundcube's plain-text email renderer. Generates crafted .eml, sends via SMTP, and…
 polosss/by-poloss..-..cve-2026-18080
Exploit for CVE-2026-18080, an unauthenticated arbitrary file upload leading to RCE in ERP Complete HR, Accounting & CRM Suite. Includes Python and…
 marcorosa/cnc-botnet-in-python
C&C Botnet written in Python with fabric
 robertdavis1/pix-c2
Ping Exfiltration Command and Control (PiX-C2)
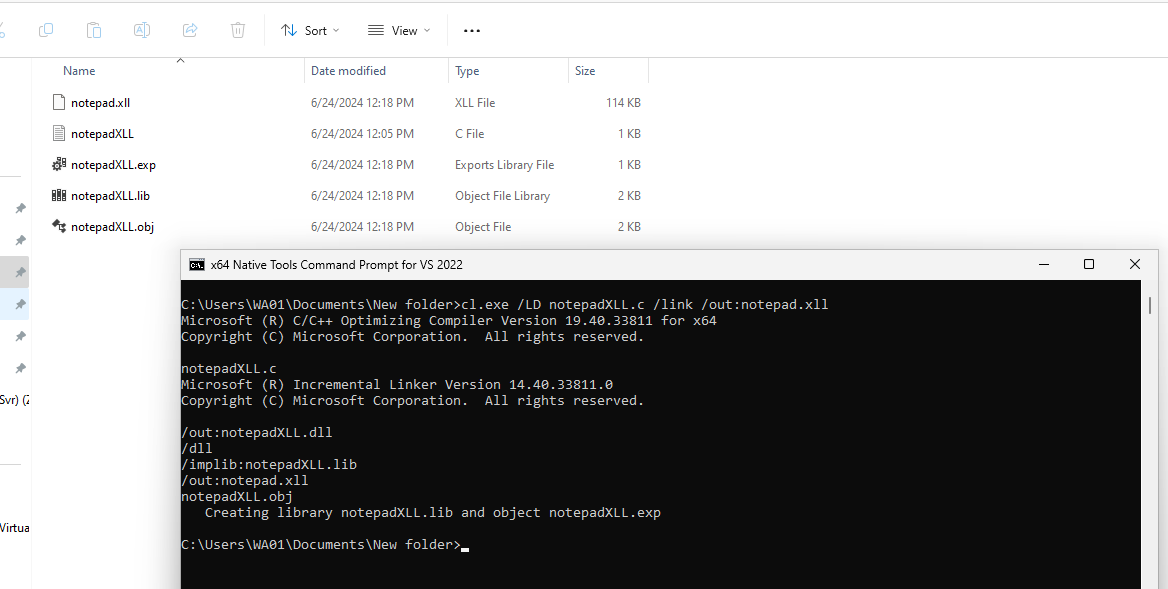 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
 dshabani96/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP email delivery, malicious RTF attachment generation, and optional…
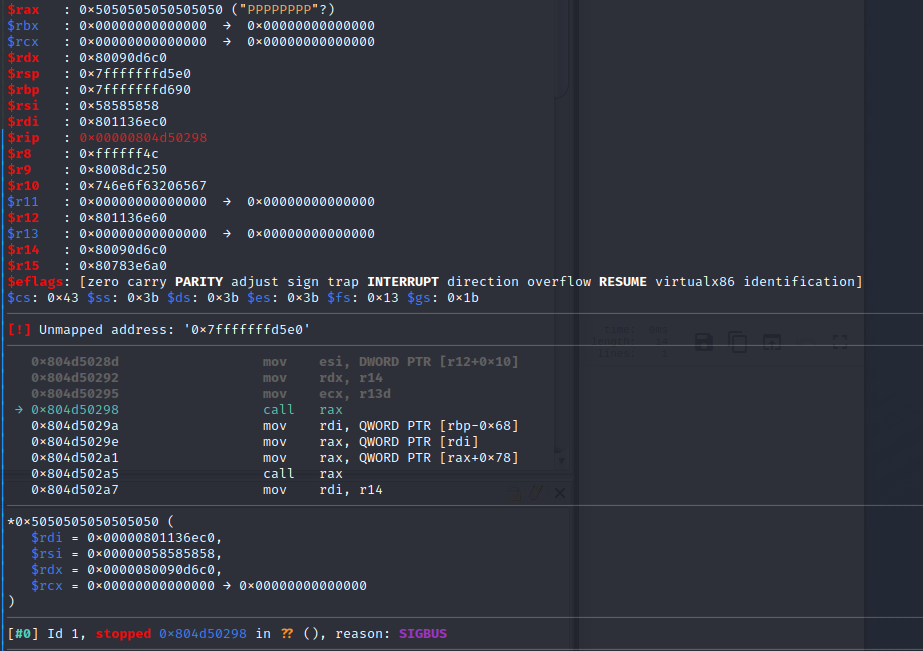 ly1g3/cisco-cve-2023-31488
Cisco Email Security Appliance: Email to zero-click RCE as root - Remote Code Execution/Memory Corruption/ROP-chain
 fathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 sofianeelhor/cve-2023-22621-poc
CVE-2023-22621: SSTI to RCE by Exploiting Email Templates affecting Strapi Versions <=4.5.5
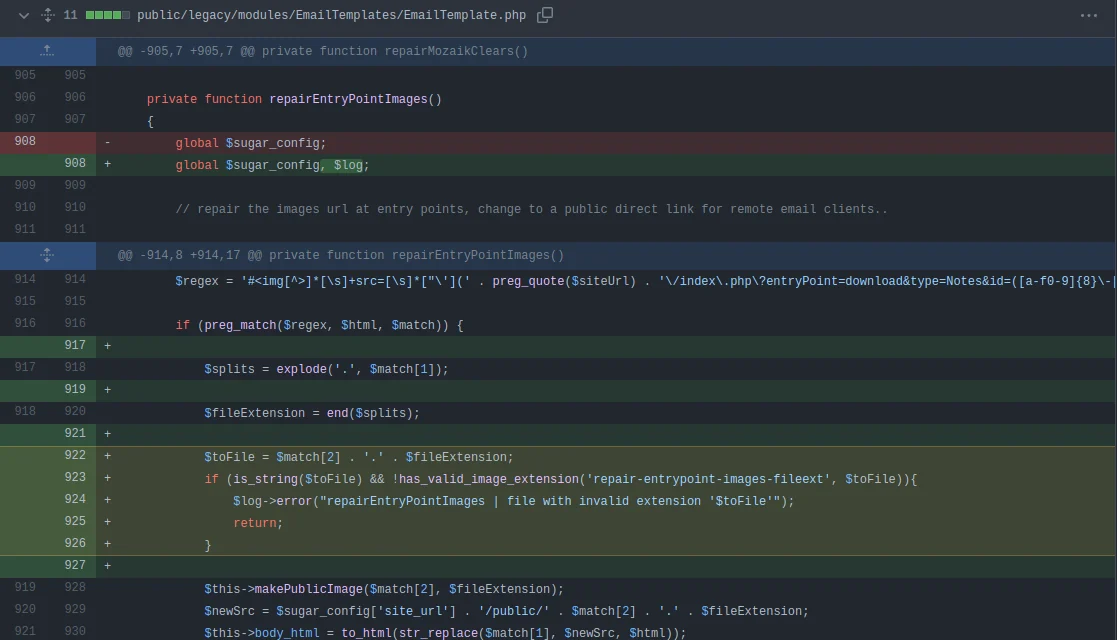 manuelz120/cve-2021-45897
Authenticated RCE exploit for SuiteCRM <= 8.0.1 via email template image upload, planting a PHP webshell for remote command execution.
 d0rb/cve-2024-21378
This repository contains an exploit for targeting Microsoft Outlook through Exchange Online, leveraging a vulnerability to execute arbitrary code via…
 ly1g3/proofpoint-cve-2023-0089
Proofpoint Email Gateway: Low level authenticated user to admin RCE
 symbolexe/cve-2023-23397
CVE-2023-23397: Remote Code Execution Vulnerability in Microsoft Outlook
 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability