
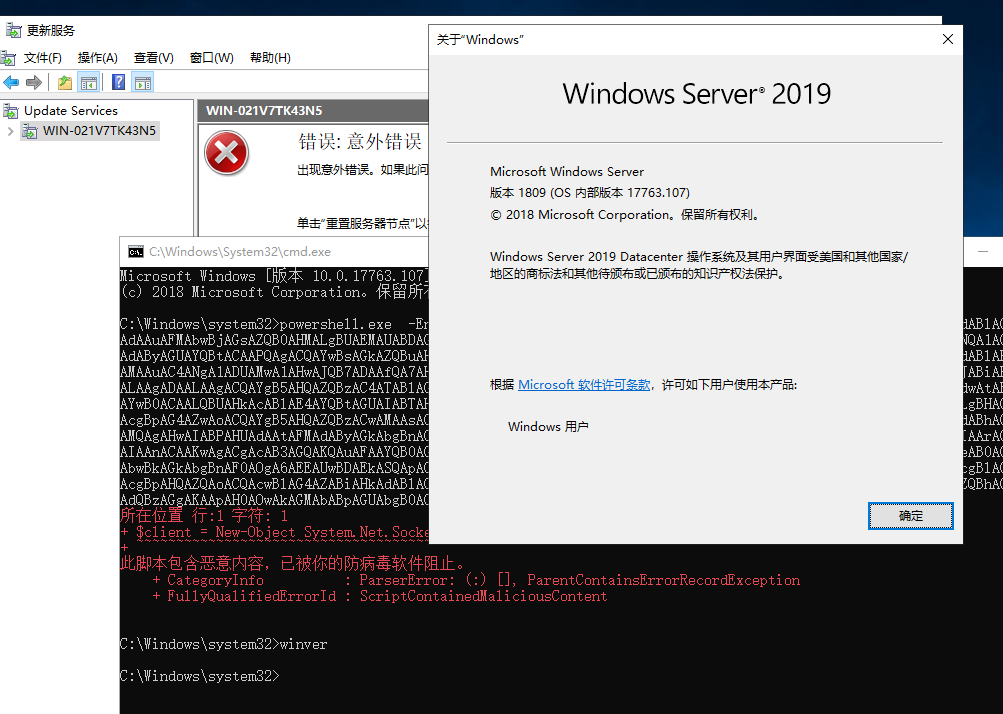
CVE-2025-59287
 0x7556/cve-2025-59287
Exploit for CVE-2025-59287, injecting WolfShell memory webshell into WSUS servers to achieve remote code execution when the admin console is opened.
exploitationpayload-developmentpenetration-testing+3
7
0x7556/cve-2025-59287Exploit for CVE-2025-59287, injecting WolfShell memory webshell into WSUS servers to achieve remote code execution when the admin console is opened.
 vikaran101/cve-2022-31854
CodoForum v5.1 - File Upload Bypass to RCE (Authenticated) exploit code
 dorkerdevil/cve-2021-27850_poc
A Proof of concept for CVE-2021-27850 affecting Apache Tapestry and leading to unauthencticated remote code execution.
 crowsec-edtech/cve-2026-87902
Python PoC exploiting CVE-2026-87902, an unauthenticated path traversal in WordPress locate_template() leading to LFI and PEAR-based RCE, with safe…
 vulncheck-oss/cve-2023-22527
Three go-exploits exploiting CVE-2023-22527 to execute arbitrary code in memory
 4627488/cve-2026-98260-nezha
CVE-2026-98260: Xiaomi 17 Ultra (nezha) temporary root + KernelSU PoC - scripts, docs and logs only; exploit built from upstream source
 witaqua-tools/root-my-device
KSU installer for supported firmware with CVE-2026-43499
 eqstlab/cve-2026-111497
Proof-of-concept exploit for CVE-2026-111497 (Node2Shell) that triggers remote code execution via a crafted upload and delivers a reverse shell, with…
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
 e4zyy/project-cve-2026-75604
Python-based exploitation framework for CVE-2026-75604, enabling authorized pentesters to validate Next.js Windows cache traversal vulnerabilities…
 diyiqiuye/cve-2025-21479-fx5p
Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
 manojcode/foxit-reader-rce-with-virualalloc-and-shellcode-for-cve-2018-9948-and-cve-2018-9958
Foxit Reader version 9.0.1.1049 Use After Free with ASLR and DEP bypass on heap
 xsanflip/begal-c2
Flask and Socket.IO command-and-control panel with a rogue browser extension agent that harvests credentials, exfiltrates files via Telegram, and…
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 34zy/cve-2026-86950
Exploitation framework for CVE-2026-86950, a CoreGraphics integer overflow: crafts malicious TrueType fonts and PDFs, extracts ASLR leaks, and builds…
 freax13/cve-2024-21980-poc
Exploit for CVE-2024-21980 targeting AMD SEV firmware to decrypt arbitrary memory of decommissioned SEV-SNP guests via a command buffer enforcement…
 1n53c/cve-2021-3156-poc
Heap-based buffer overflow exploit for CVE-2021-3156 in sudo, offering local privilege escalation to root on vulnerable Linux systems.