
ABL_ROP
 boredpentester/abl_rop
Experimenting with CVE-2022-20120 (Pixel Bootloader / ABL) using Unicorn, derived from eShard's emulator at…
android-securitybinary-exploitationembedded-systems-security+4
boredpentester/abl_ropExperimenting with CVE-2022-20120 (Pixel Bootloader / ABL) using Unicorn, derived from eShard's emulator at…
 bugel/cve-2026-43499-m3q-azf1
This package is not a complete root. It flips SELinux to Permissive and holds reclaim long enough for follow-on work. Host `uid=0` is not achieved…
 diyiqiuye/cve-2025-21479-fx5p
Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
 ariyanpegu/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 huaguiqi/asus-i005-cve-2026-43499
CVE-2026-43499 (GhostLock) adaptation for ASUS ROG Phone 5S — UAF trigger + pselect stack reclaim, KASLR leak blocked
 c0d331ng/blackash-cve-2025-48593
CVE-2025-48593
 deaurity/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 yutori-natsu/cve-2023-6931-pipa
Kernel LPE exploit for CVE-2023-6931 on Xiaomi Pad 6 (pipa), chaining a perf read_size overflow to root and disabling SELinux via data-only…
 newazbenalam/root-my-galaxy-payloads
Device-specific CVE-2026-43499 root payloads and KernelSU artifacts for Samsung Galaxy models, with firmware profiles, exploit source, and a support…
 begitdj/cve-2019-2215-markw
Exploit for CVE-2019-2215 to gain temporary root on Xiaomi MIUI devices, enabling bootloader unlock and system modifications.
 pirosap/aquos-r7-ghostlock
Device-specific Linux 5.10 kernel root exploit for Sharp AQUOS R7 (CVE-2026-43499), granting temporary UID 0 with SELinux permissive and an su daemon.
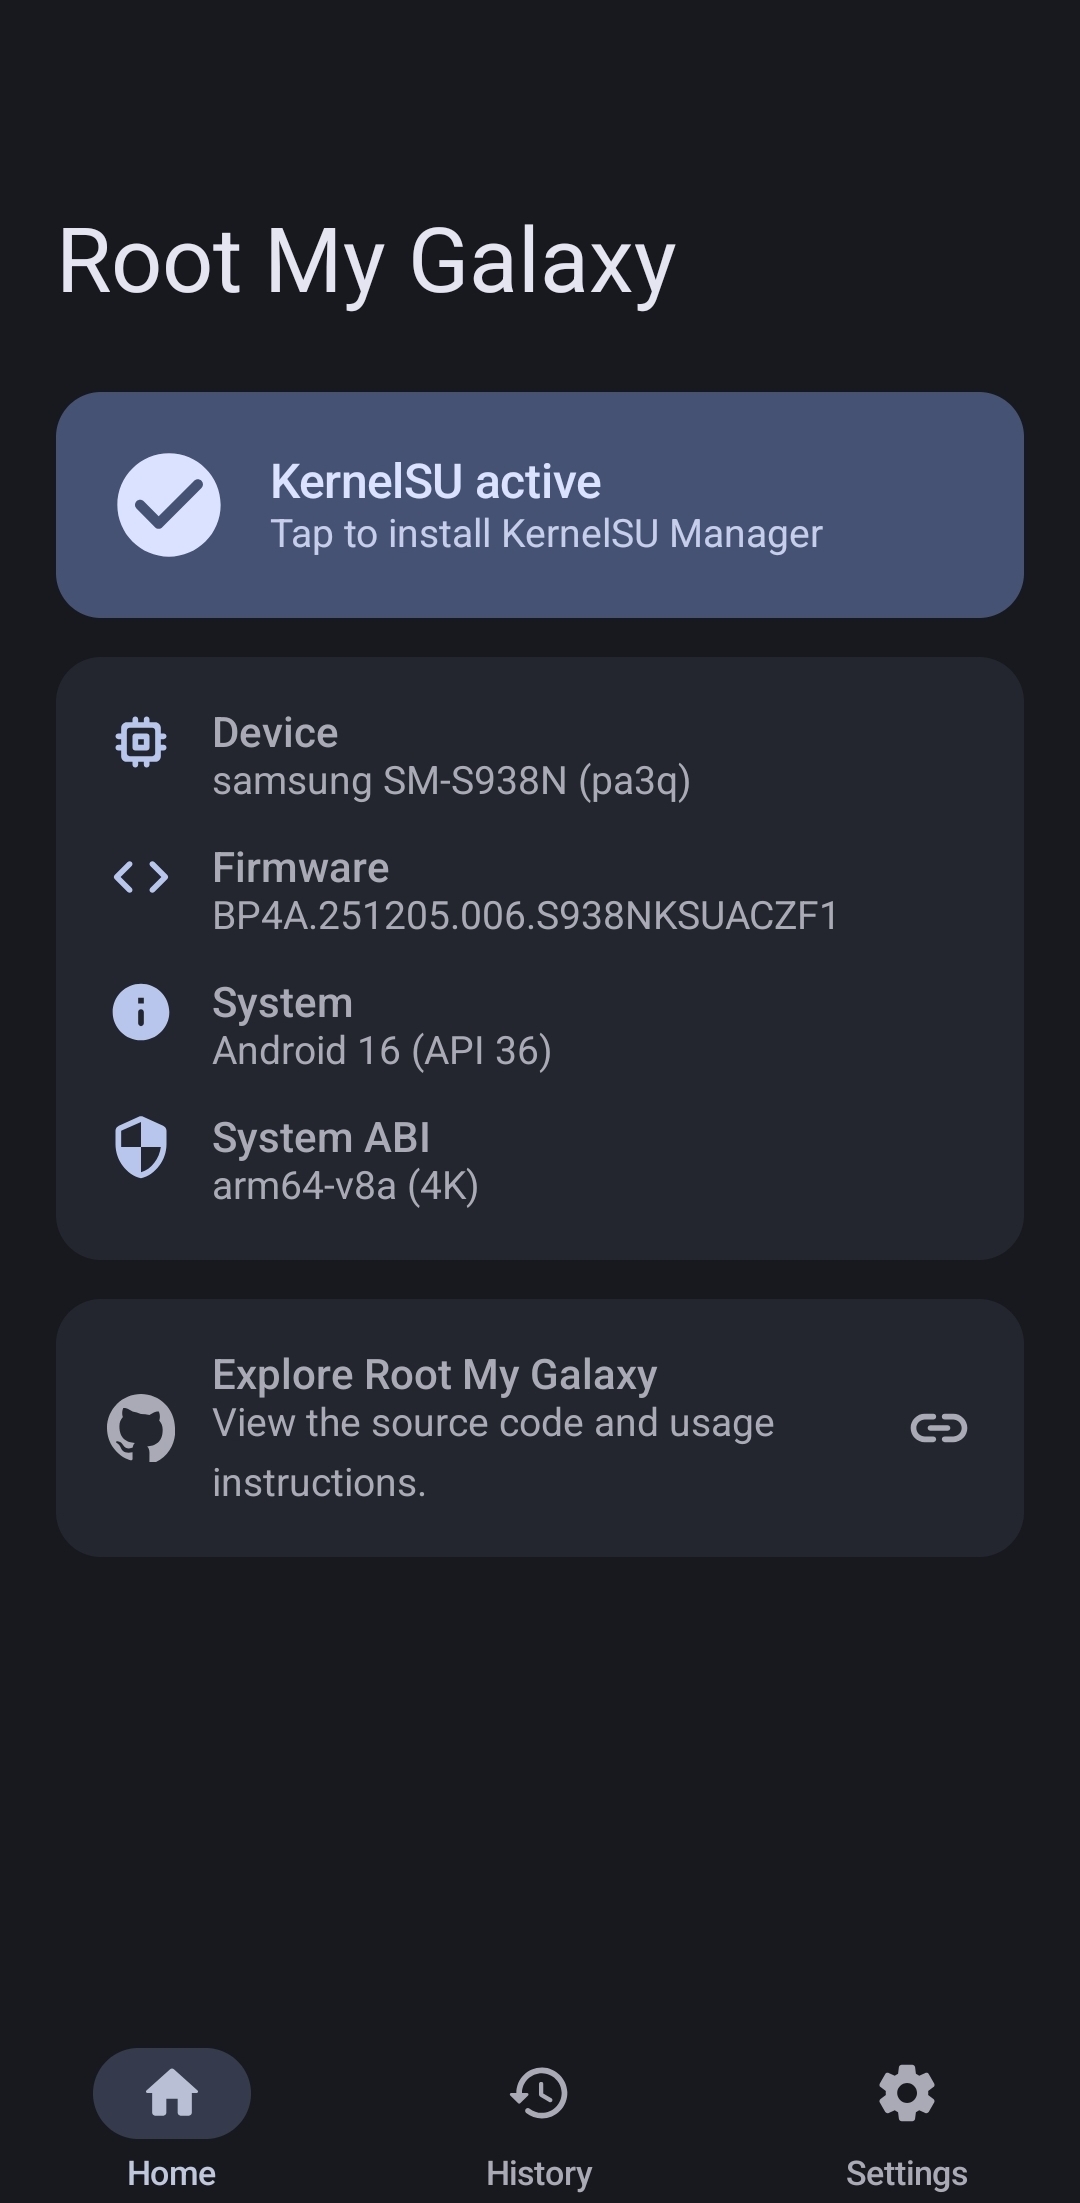 witaqua-tools/root-my-device
KSU installer for supported firmware with CVE-2026-43499
 artur9010/amazon-mustang-hack
Kernel exploit research achieving temporary root on Amazon Fire 7 (Fire OS 7.3.3.1) via the Mali kbase JIT use-after-free CVE-2022-38181, with a…
 cxlfhx/ghostlock-pfem10
GhostLock (CVE-2026-43499 / IonStack) research for OPPO Find X5 Pro (PFEM10): exploit chain, progress, blocker log, and OPPO 5-series kernel notes
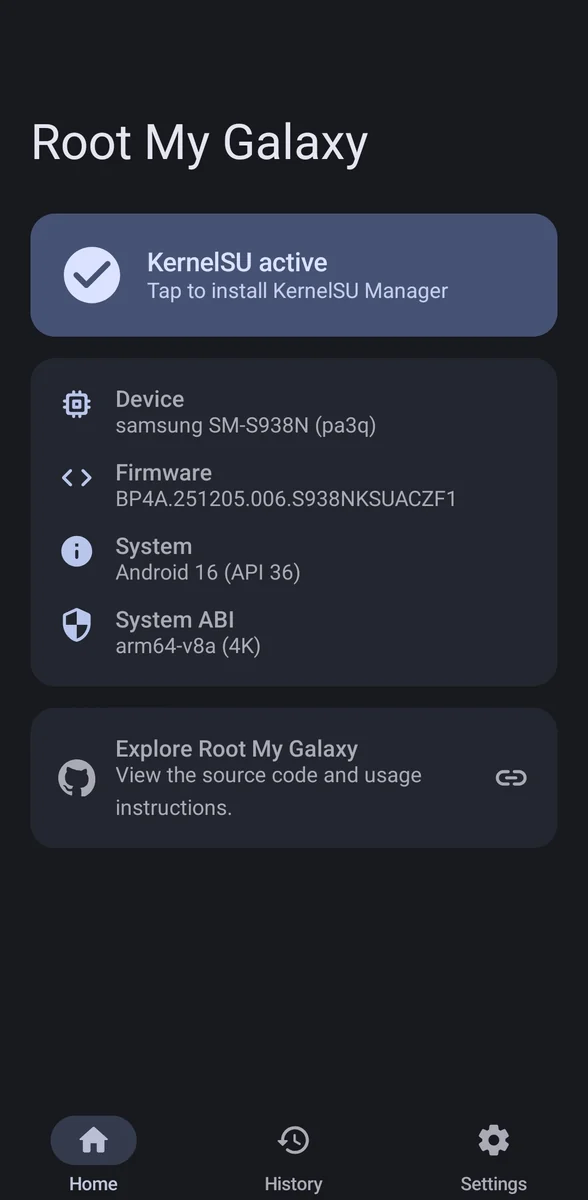 alk601/root-my-galaxy
KSU installer for supported Samsung Galaxy firmware with CVE-2026-43499
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…
 pwnaccelerator/stagefright-cve-2015-3864
PoC - Binary patches for CVE-2015-3864 (NOT for production, use at your own risk)
 abdgalaxy36-code/rmgp-complete-handoff
Complete RMGP (CVE-2026-43499) workspace + experiment-state handoff for SM-A376B/A376BXXU1AZB7