ReflectiveDLLInjection

Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…

Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…

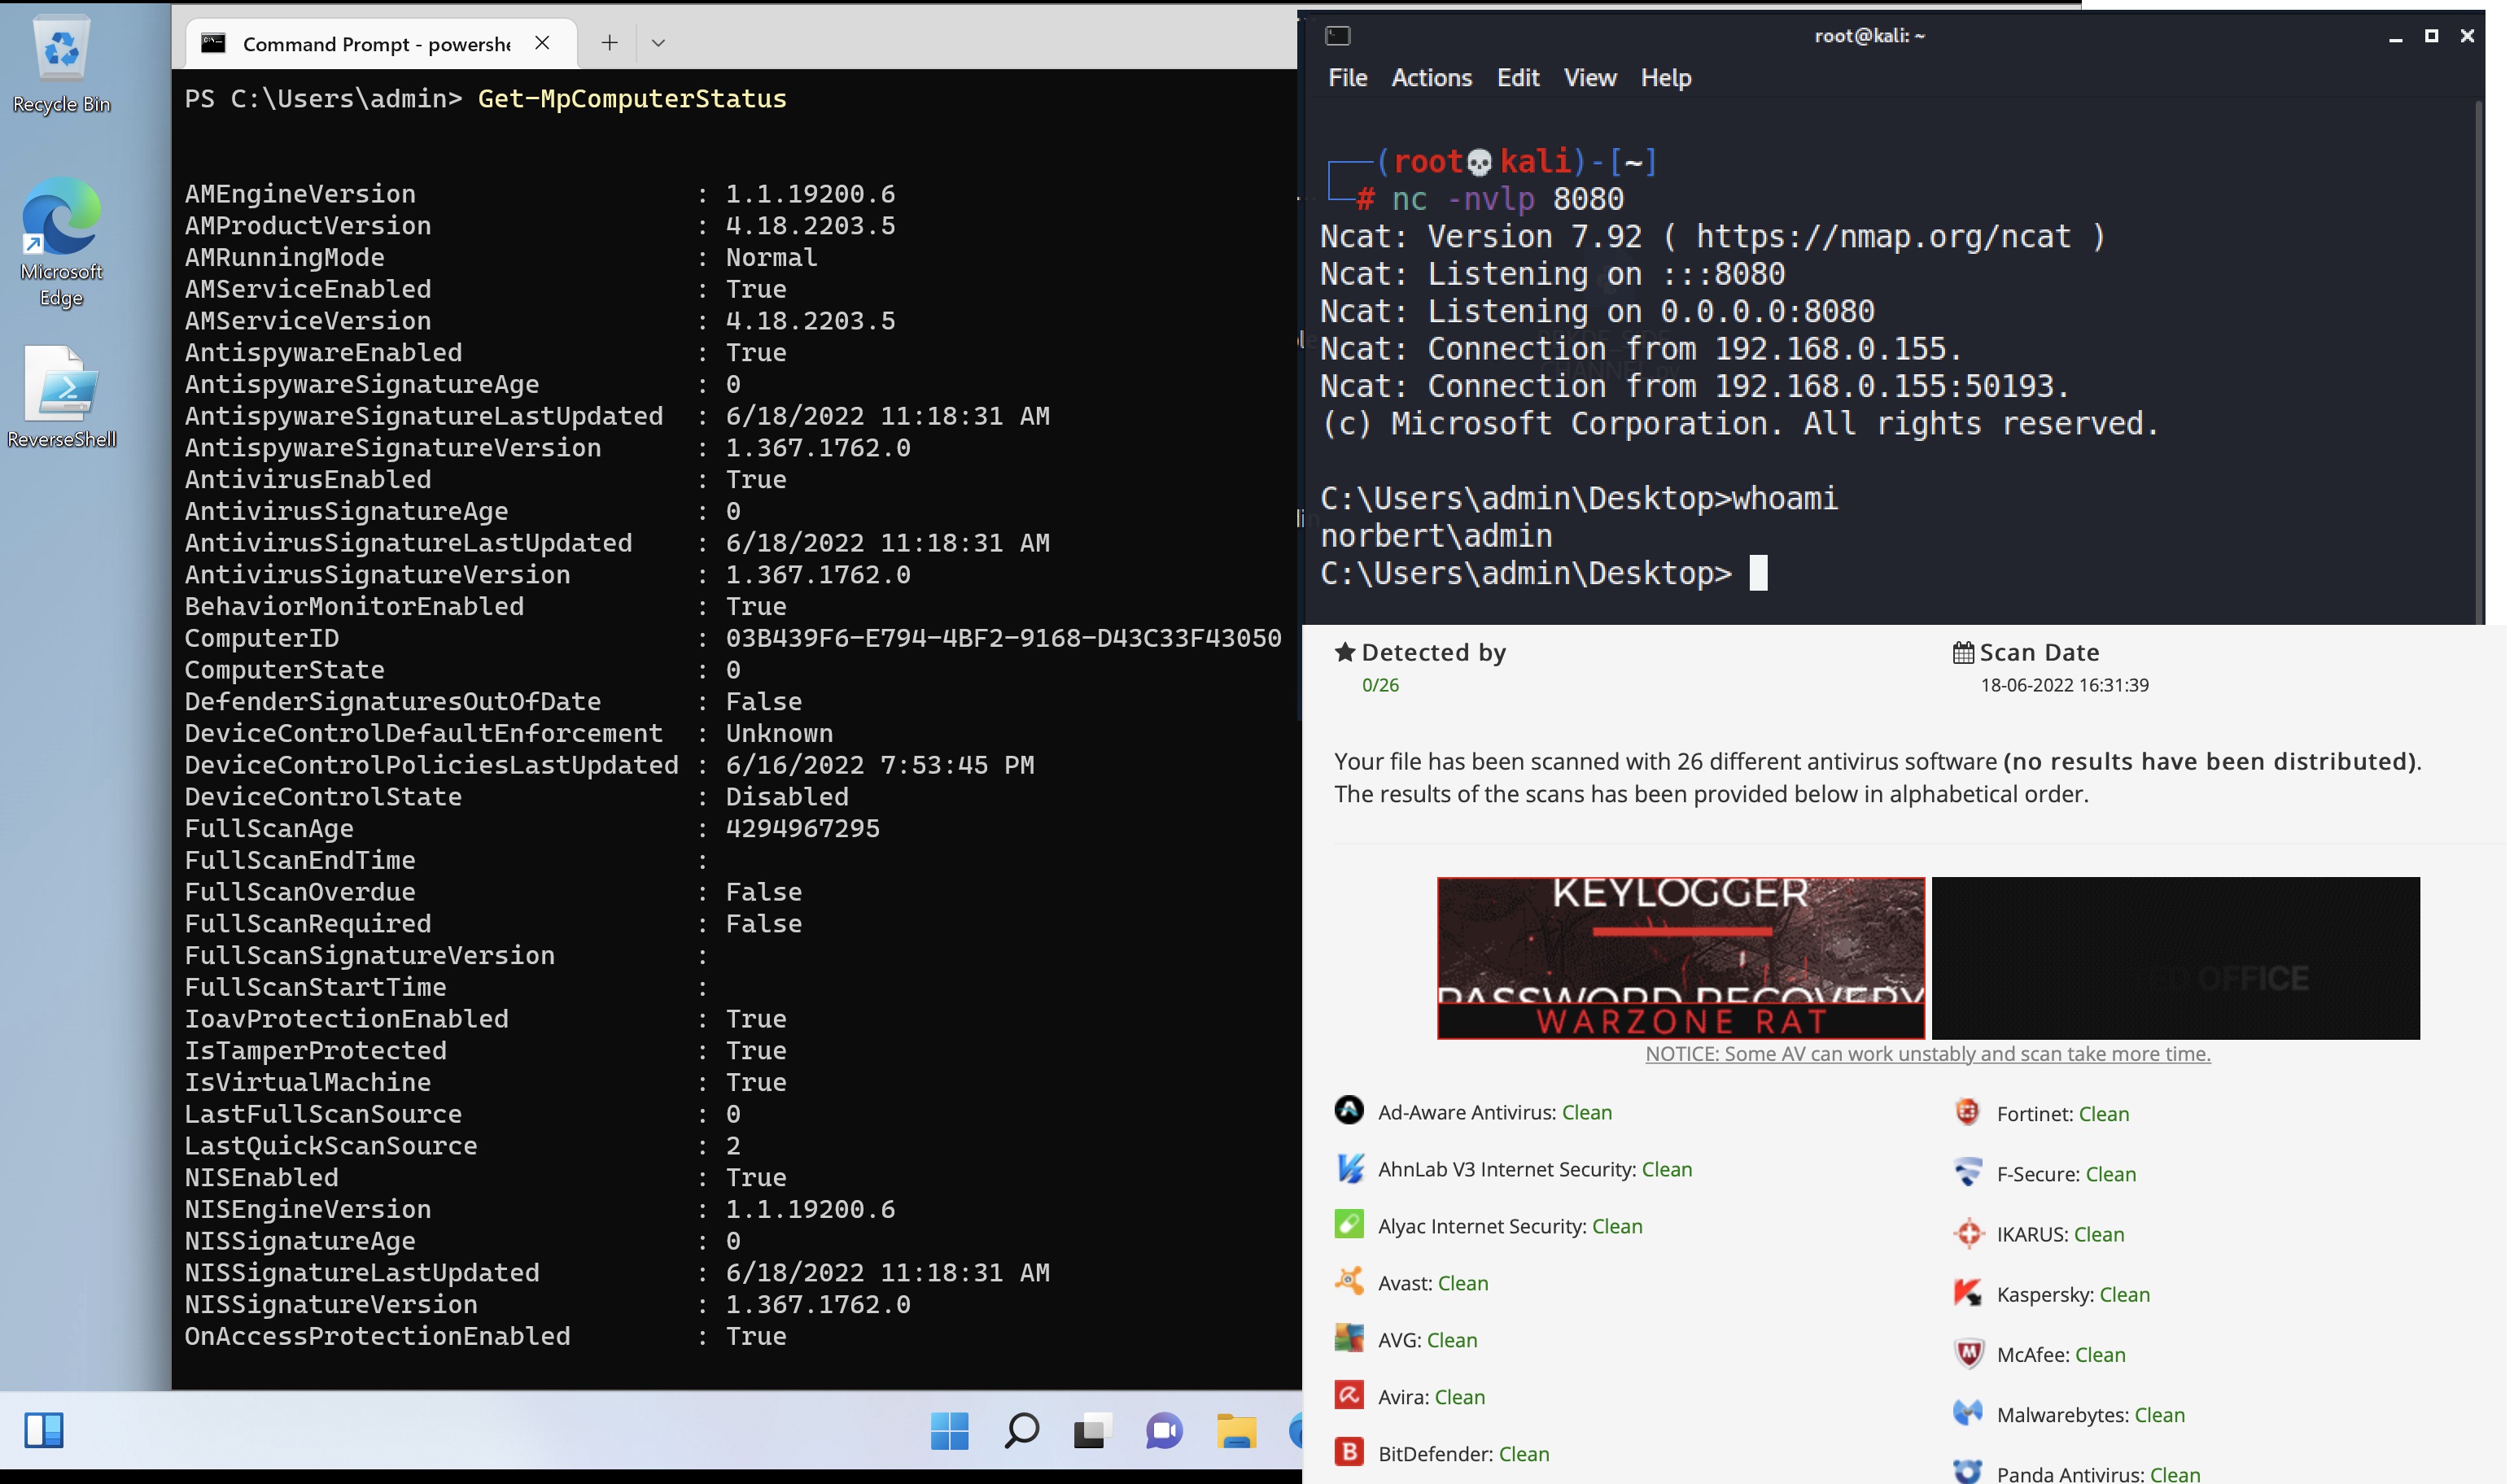
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode

The swiss army knife of LSASS dumping

A public release of the Steal My Bitcoin challenge

Malleable C2 is a domain specific language to redefine indicators in Beacon's communication. This repository is a collection of Malleable C2 profiles…

Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…

This repository is a collection of powershell functions every hacker should know

A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.

Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…

Educational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…

Curated collection of offensive security tools and commands for Active Directory attacks, C2, privilege escalation, obfuscation, and web pentesting.

A collection of techniques, examples and a little bit of theory for manually obfuscating PowerShell scripts to achieve AV evasion, compiled for…

PoCs and tools for investigation of Windows process execution techniques

Working POC of Mikrotik exploit from Vault 7 CIA Leaks

Cobalt Strike - Malleable C2 Profiles. A collection of profiles used in different projects using Cobalt Strike https://www.cobaltstrike.com/.

Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…

A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…