
skills
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
command-and-controleducationexploitation+9
738
specterops/skillsReusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
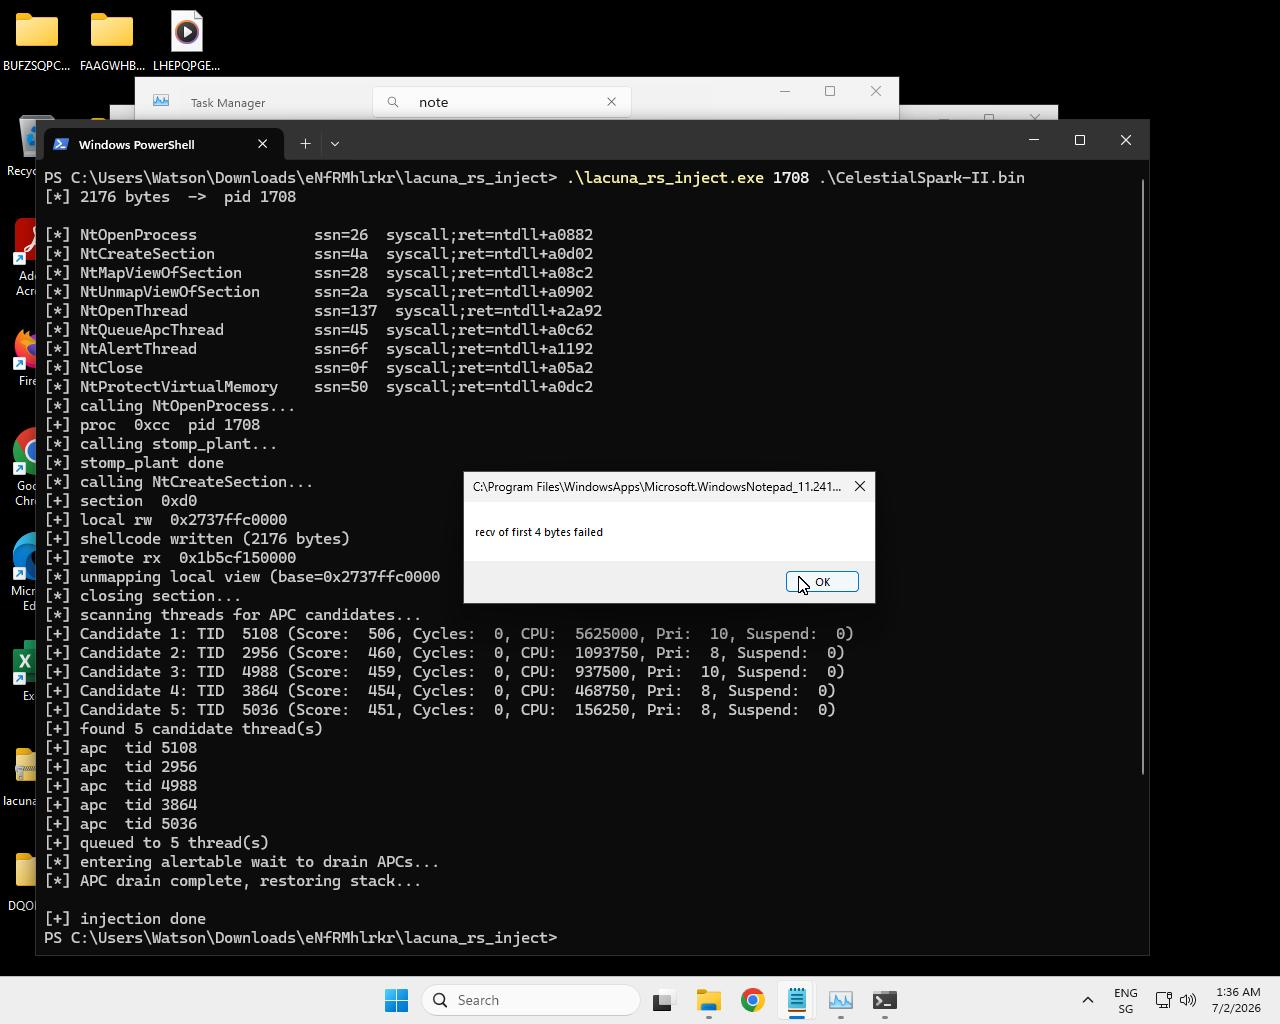 karkas66/lacuna-rs
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…
 gh-ost00/cve-2024-4577-rce
Exploit for PHP CGI Argument Injection (CVE-2024-4577) enabling remote code execution on vulnerable Windows servers running Apache and PHP-CGI.…
 10cks/cve-2024-32002-exp
Bash PoC for CVE-2024-32002 that exploits Git clone with malicious submodules and symlinks to execute arbitrary commands on Windows and macOS.
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…
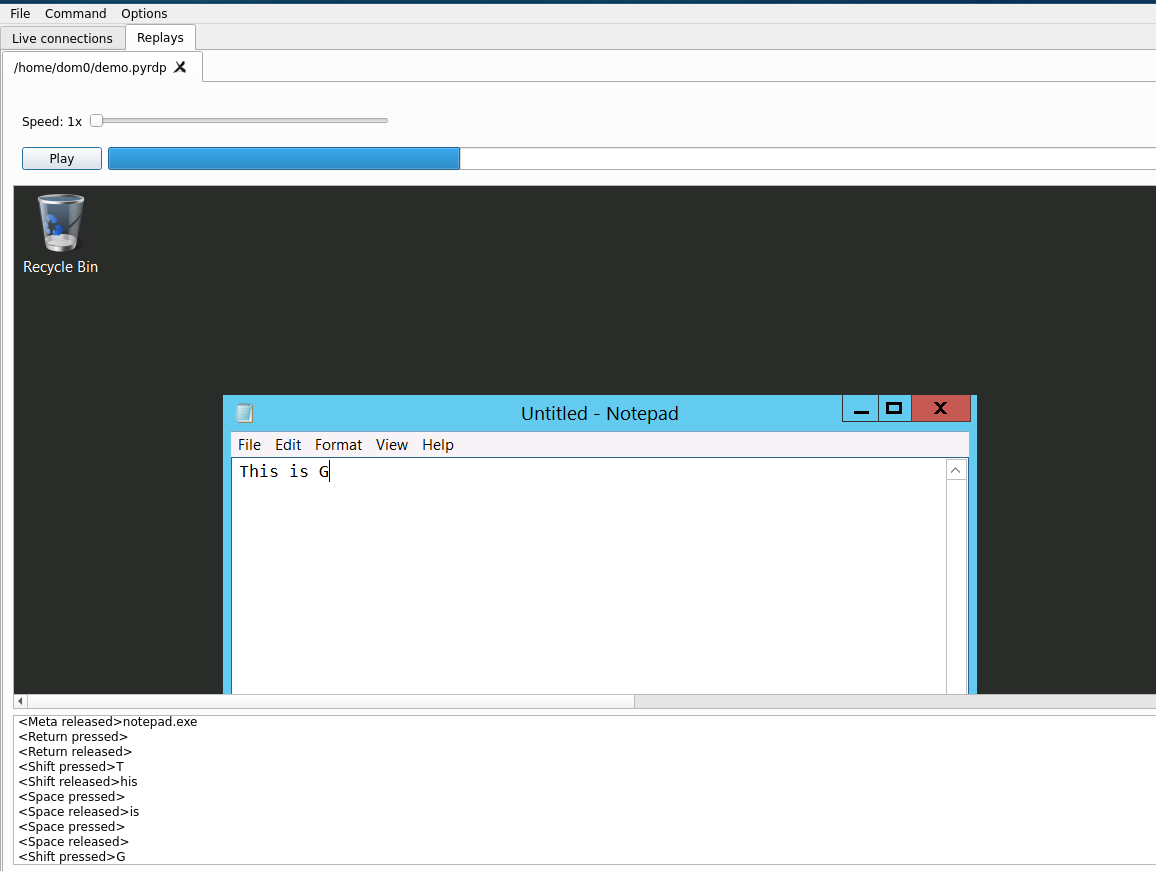 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 ghostlyrootb2h/cve-2026-82222
Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
 geozstevenzz/cve-2024-30804
Windows LPE PoC exploiting the AsInsHelp64.sys driver via arbitrary physical memory read/write to overwrite kernel tokens and gain SYSTEM privileges.
 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
 toxy4ny/bl00dym4ry
Educational trojan simulator for cybersecurity training, simulating phishing attacks with social engineering, system reconnaissance, anti-sandbox…
 blacksnufkin/litterbox
A self-hosted sandbox for red teams to test payloads against modern detection before deployment. MCP integration lets an LLM agent drive analysis end…
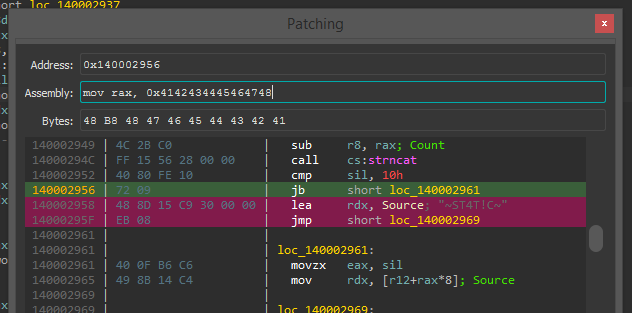 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 r3nhat/grat2
We developed GRAT2 Command & Control (C2) project for learning purpose.
 m01n-team/headerlesspe
Memory PE loading technique for file-less attacks, enabling in-memory execution of EXEs without DOS/PE headers, supporting relocation and import…