
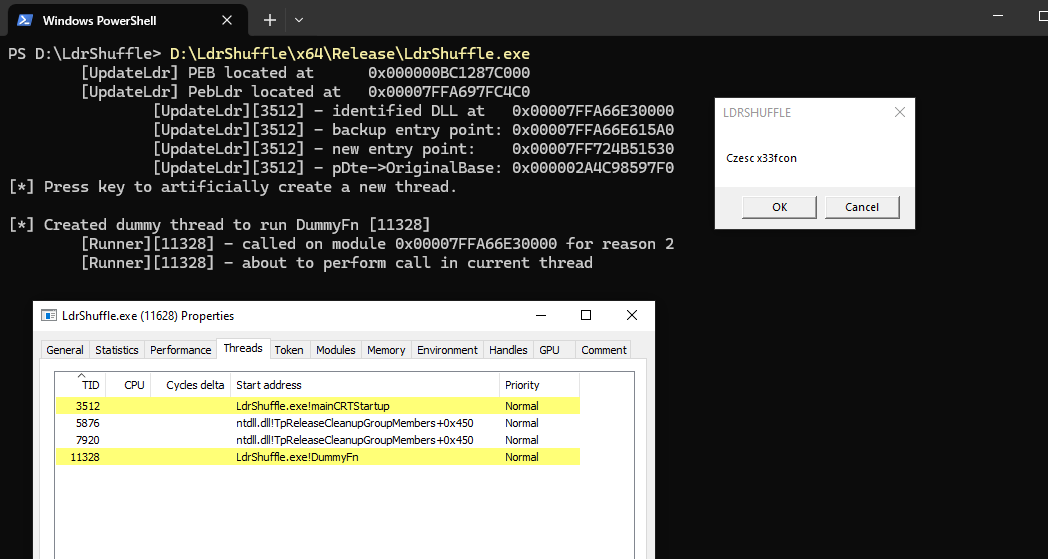
LdrShuffle
 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
binary-exploitationcode-analysisexploitation+6
2881 year ago
rwxstoned/ldrshuffleCode execution/injection technique using DLL PEB module structure manipulation
 zcgonvh/cve-2017-7269
fixed msf module for cve-2017-7269
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
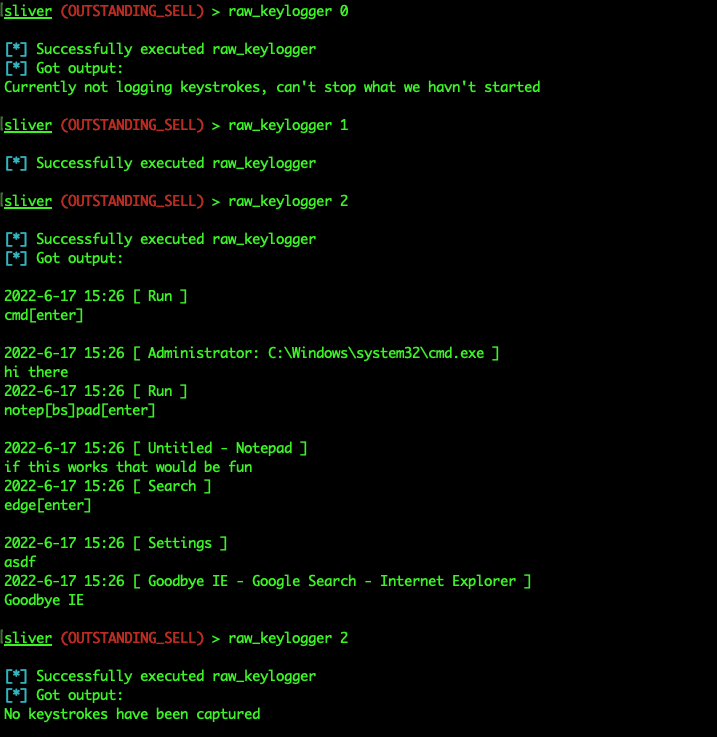 trustedsec/sliverkeylogger
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
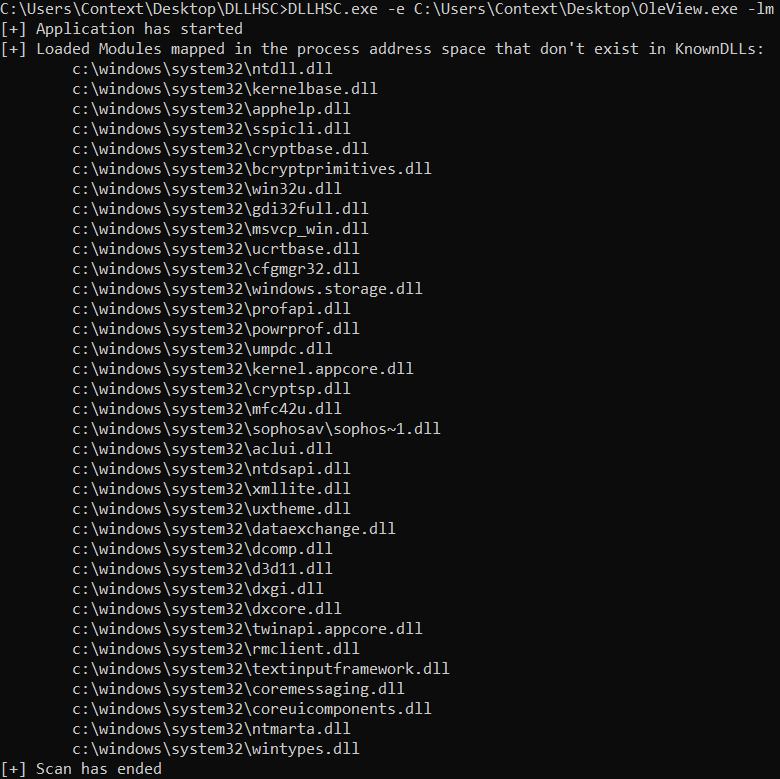 ctxis/dllhsc
Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 rickgeex/msf-module-cve-2019-0708
Metasploit module for CVE-2019-0708 (BlueKeep) - https://github.com/rapid7/metasploit-framework/tree/5a0119b04309c8e61b44763ac08811cd3ecbbf8d/modules/…
 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 securifera/cve-2015-2900-exploit
Proof-of-concept exploit and Metasploit module for CVE-2015-2900 targeting the MEDCIN Engine (medcinserv.exe) versions prior to 2.22.20142.166.
 jelasin/cve-2026-42945
Proof-of-concept exploit for CVE-2026-42945, a heap buffer overflow in NGINX's rewrite module enabling unauthenticated remote code execution via…
 jirojo2/drupalgeddon2
MSF exploit module for Drupalgeddon 2 (CVE-2018-7600 / SA-CORE-2018-002)
 mekhalleh/exchange_proxylogon
Module pack for #ProxyLogon (part. of my contribute for Metasploit-Framework) [CVE-2021-26855 && CVE-2021-27065]
 tiagob0b/cve-2021-22005
Metasploit module for CVE-2021-22005 VMware vCenter arbitrary file upload vulnerability with proof-of-concept and remote code execution exploit.
 debajyoti0-0/cve-2026-27654-poc
Proof-of-Concept and technical analysis for CVE-2026-27654, a heap-based buffer overflow vulnerability in the NGINX HTTP WebDAV module, including…
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
 0x00-0x00/cve-2015-3224
Modification of Metasploit module for RCE in Ruby-On-Rails Console CVE-2015-3224
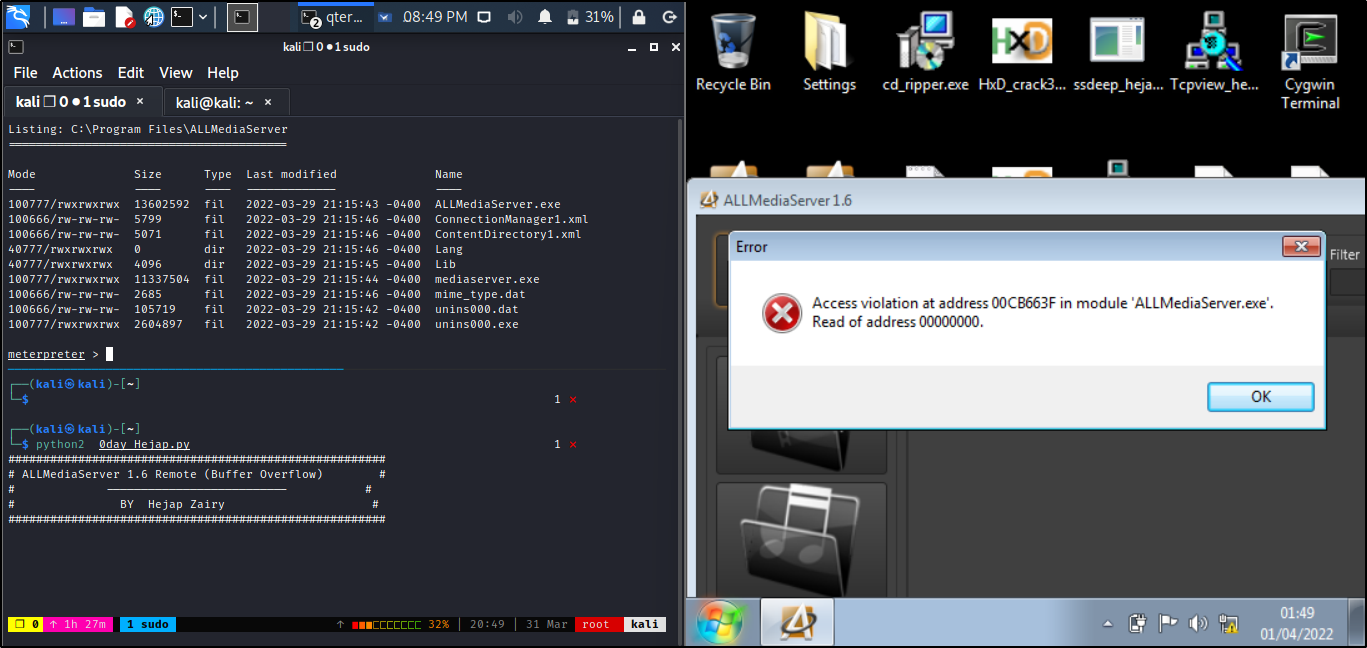 matrix07ksa/allmediaserver-1.6-buffer-overflow
Remote buffer overflow exploit with SEH overwrite for ALLMediaServer 1.6, provided as a Metasploit module targeting CVE-2022-28381.