Commander
 voukatas/commander
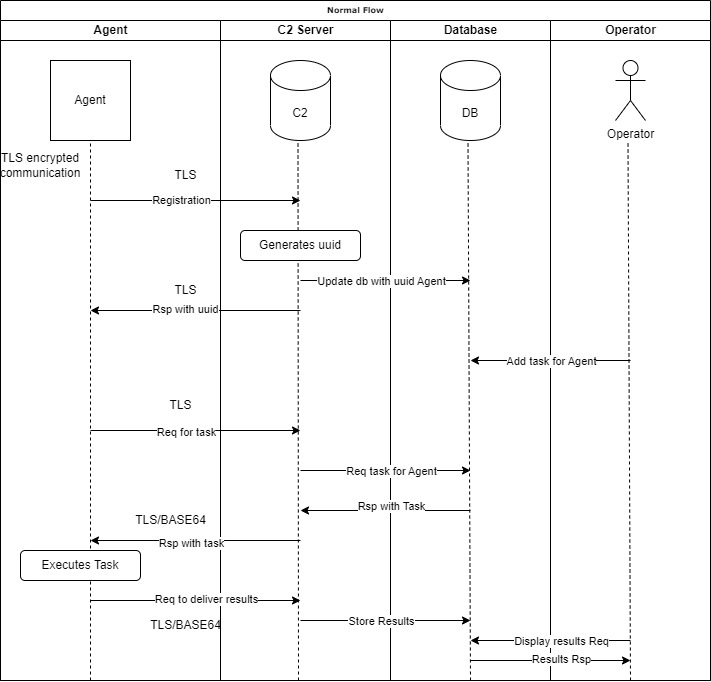
Python-based command and control framework with encrypted TLS communication, multiple agent support (Python/C), interactive sessions, file transfer,…
command-and-controlencryption-decryption-toolspayload-development+3
65
voukatas/commanderPython-based command and control framework with encrypted TLS communication, multiple agent support (Python/C), interactive sessions, file transfer,…
 averagesecurityguy/c2
A simple, extensible C&C beaconing system.
 psmths/reave
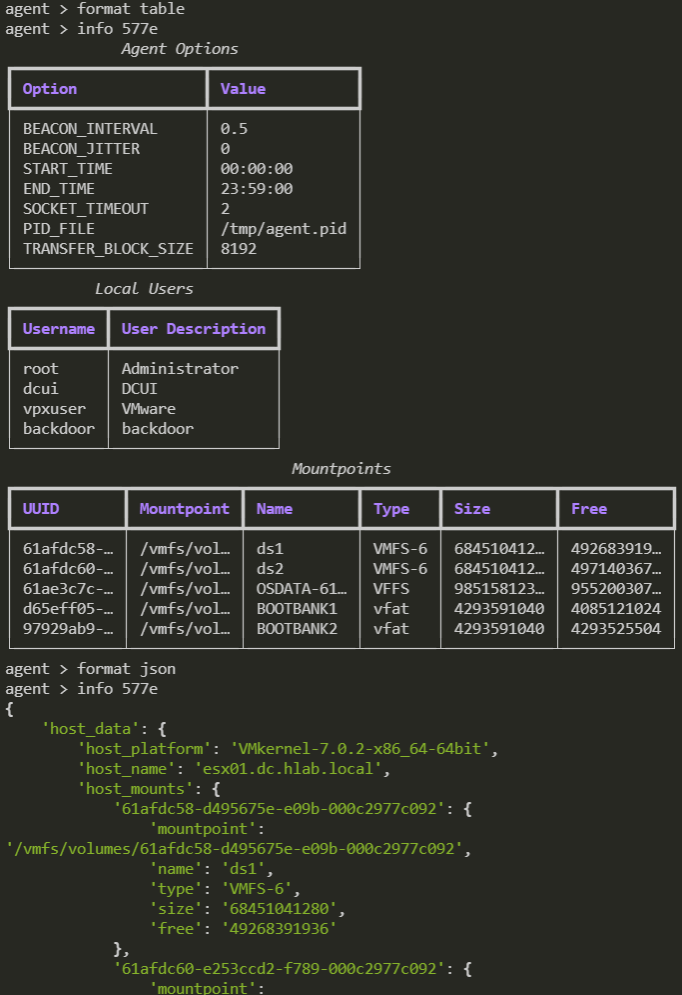
WIP Post-exploitation framework tailored for hypervisors.
 secforce/cve-2017-3599
Proof of concept exploit for CVE-2017-3599
 secforce/cve-2018-8941
D-Link DSL-3782 Code Execution (Proof of Concept)
 secforce/wptimecapsulepoc
An authentication bypass was recently discovered (https://www.webarxsecurity.com/vulnerability-infinitewp-client-wp-time-capsule/) on WP Time Capsule…
 symbolexe/cve-2024-6387
SSH Exploit for CVE-2024-6387 : RCE in OpenSSH's server, on glibc-based Linux systems
 dereeqw/netspy
NetSpyC2 – Python C2 Server with RSA Key Exchange and AES-GCM Encrypted Sessions
 umbertodellamonica/linksys-wrt54gl-exploitation
From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)
 nhas/cve-2024-45337-poc
Proof of concept (POC) for CVE-2024-45337

 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 dragon56yt/revshell
A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…
 joshuavanderpoll/cve-2025-32433
Go PoC for CVE-2025-32433 — unauthenticated RCE in Erlang/OTP SSH.
 edu0x01/hack-tools
Project that brings together several pentest tools
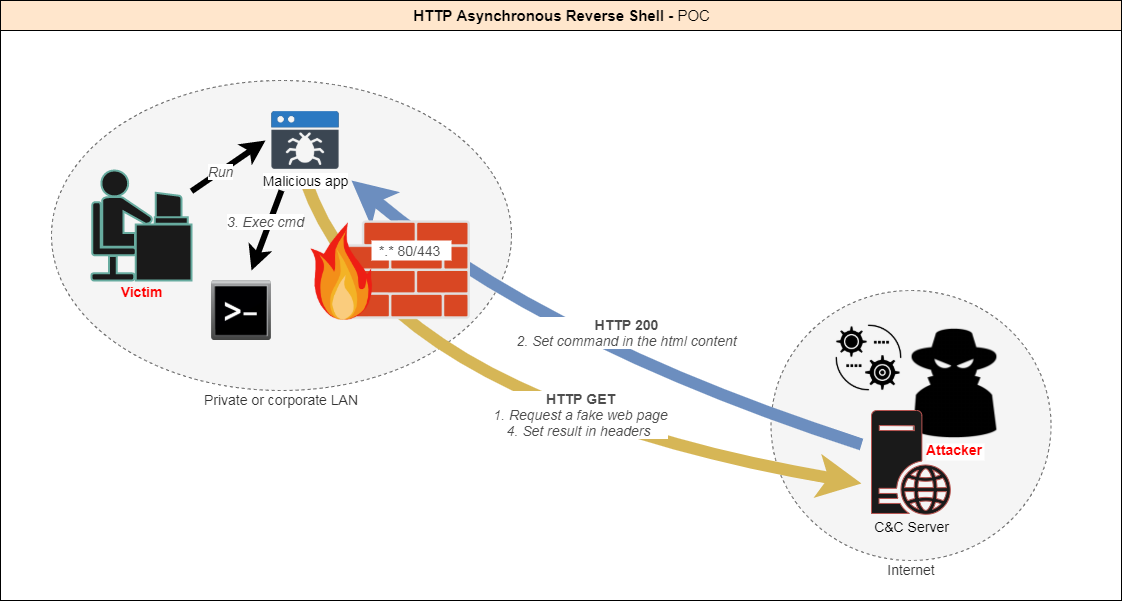 onsec-fr/http-asynchronous-reverse-shell
[POC] Asynchronous reverse shell using the HTTP protocol.
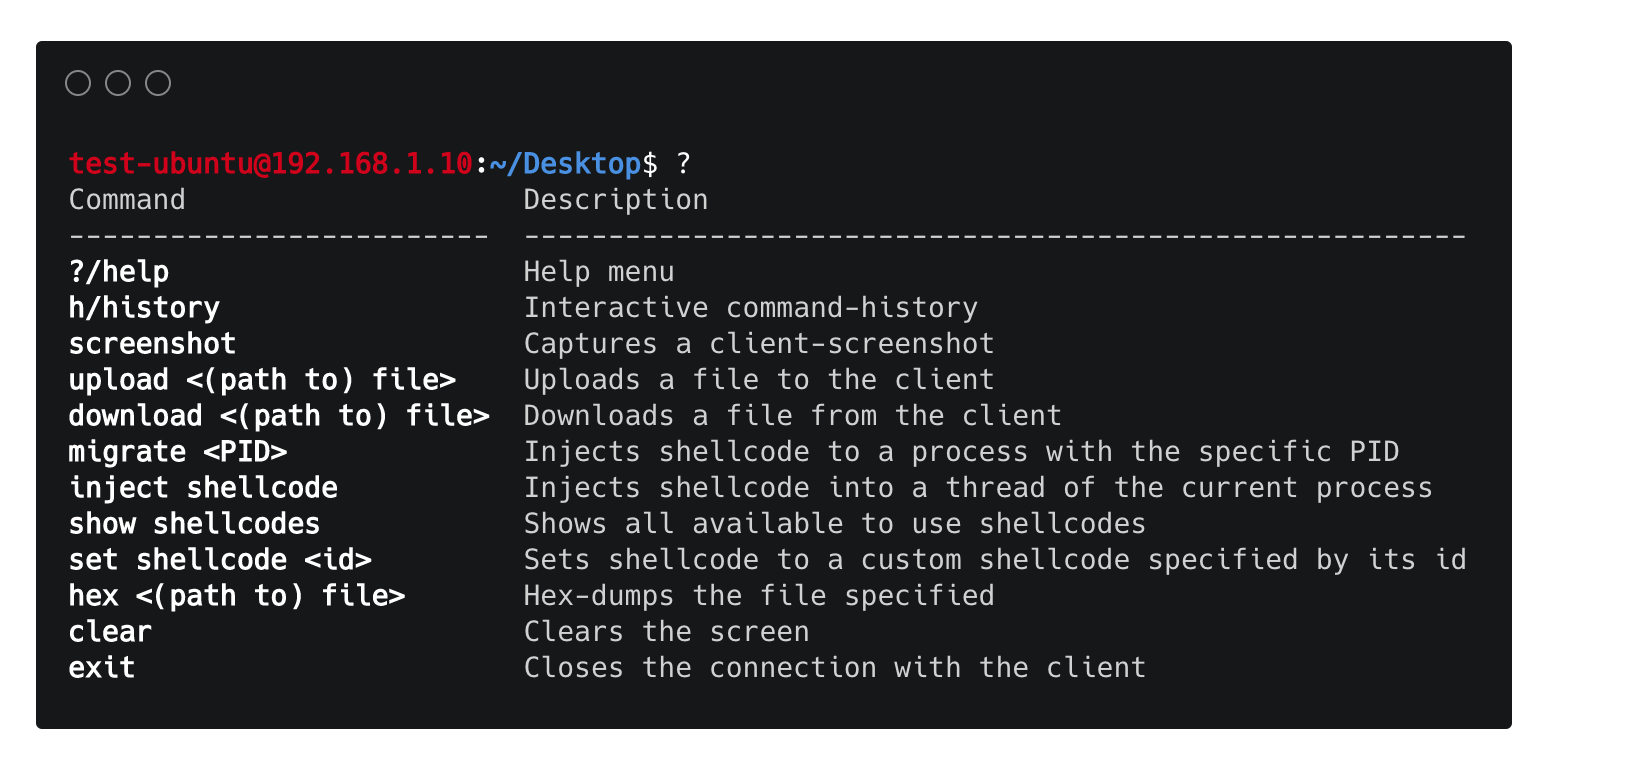 chrispetrou/hrshell
HRShell is an HTTPS/HTTP reverse shell built with flask. It is an advanced C2 server with many features & capabilities.
 proviesec/xss-payload-list
Curated collection of cross-site scripting payloads, polyglots, and injection test rules for web application penetration testing and bug bounty…