
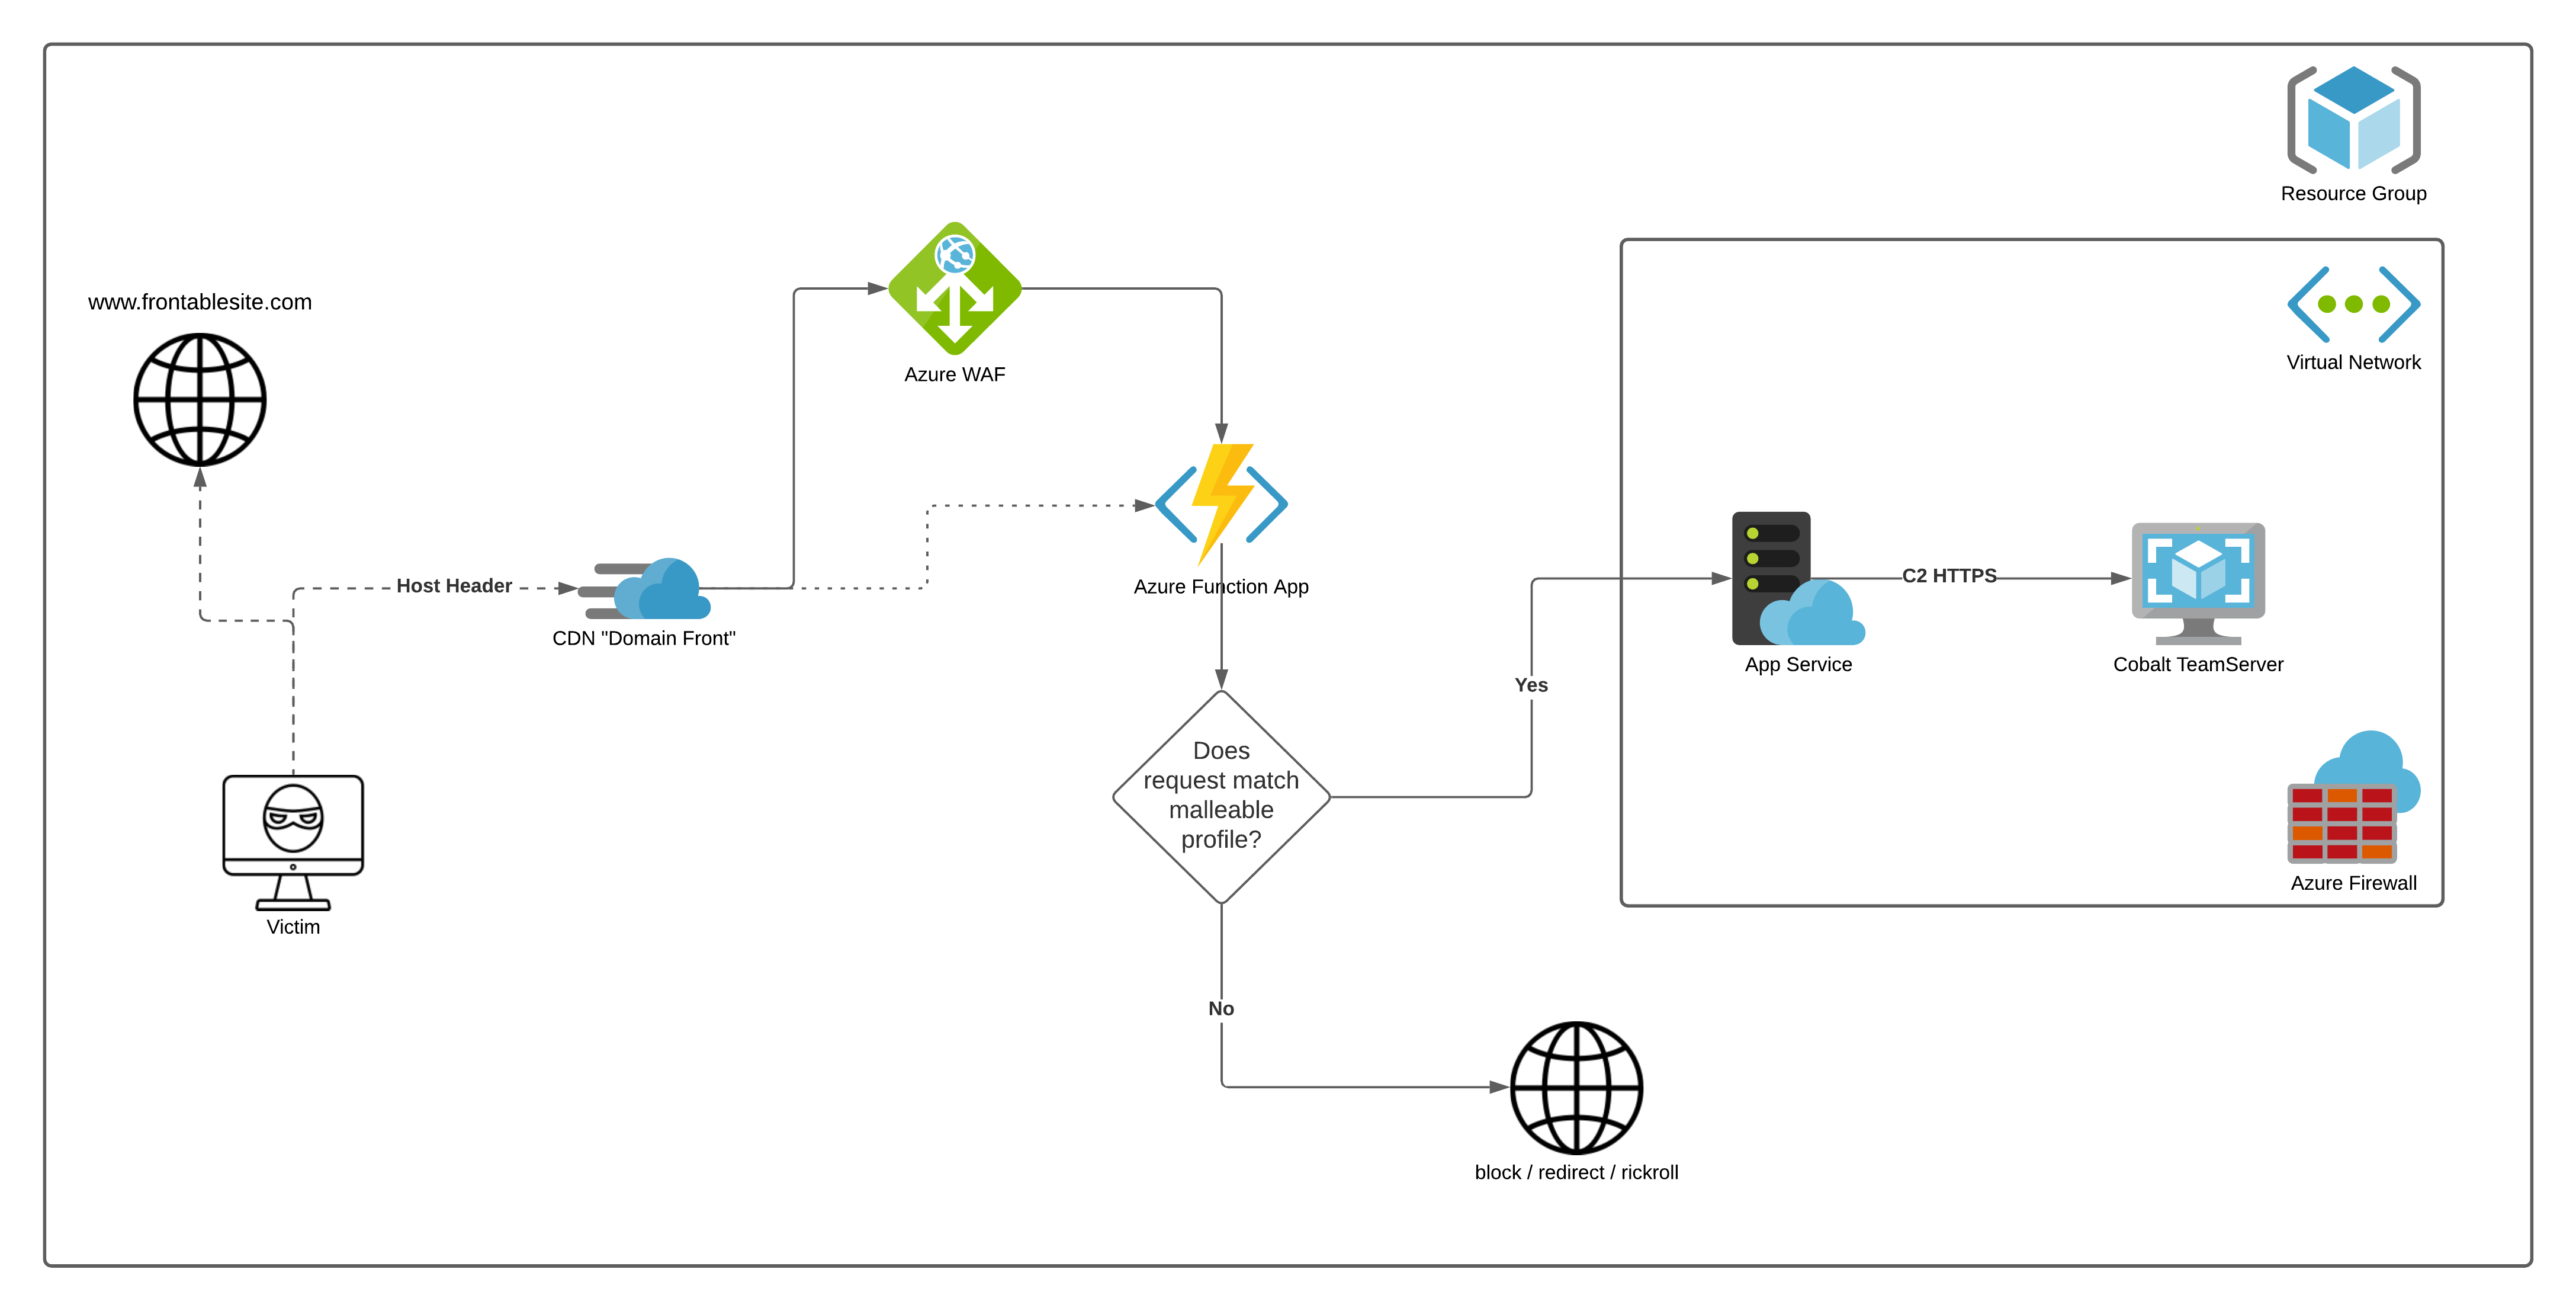
AzureC2Relay
 flangvik/azurec2relay
Azure Function that validates and relays Cobalt Strike beacon traffic using malleable C2 profiles, redirecting invalid requests to a decoy site and…
cloud-securitycommand-and-controlids-ips-evasion+2
233
flangvik/azurec2relayAzure Function that validates and relays Cobalt Strike beacon traffic using malleable C2 profiles, redirecting invalid requests to a decoy site and…
 flangvik/cobaltbus
Cobalt Strike External C2 Integration With Azure Servicebus, C2 traffic via Azure Servicebus
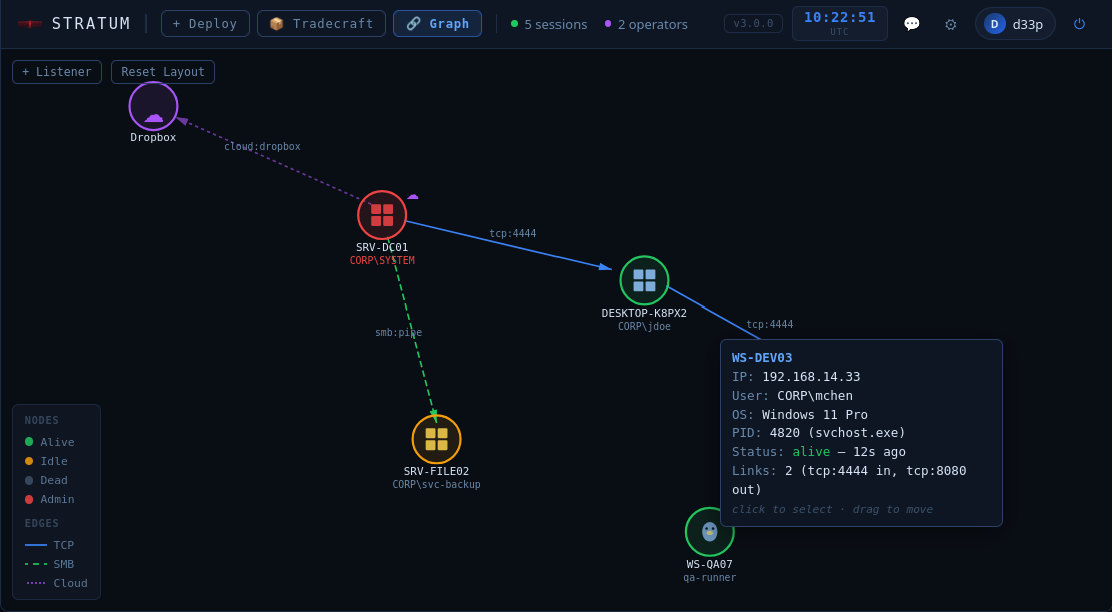 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
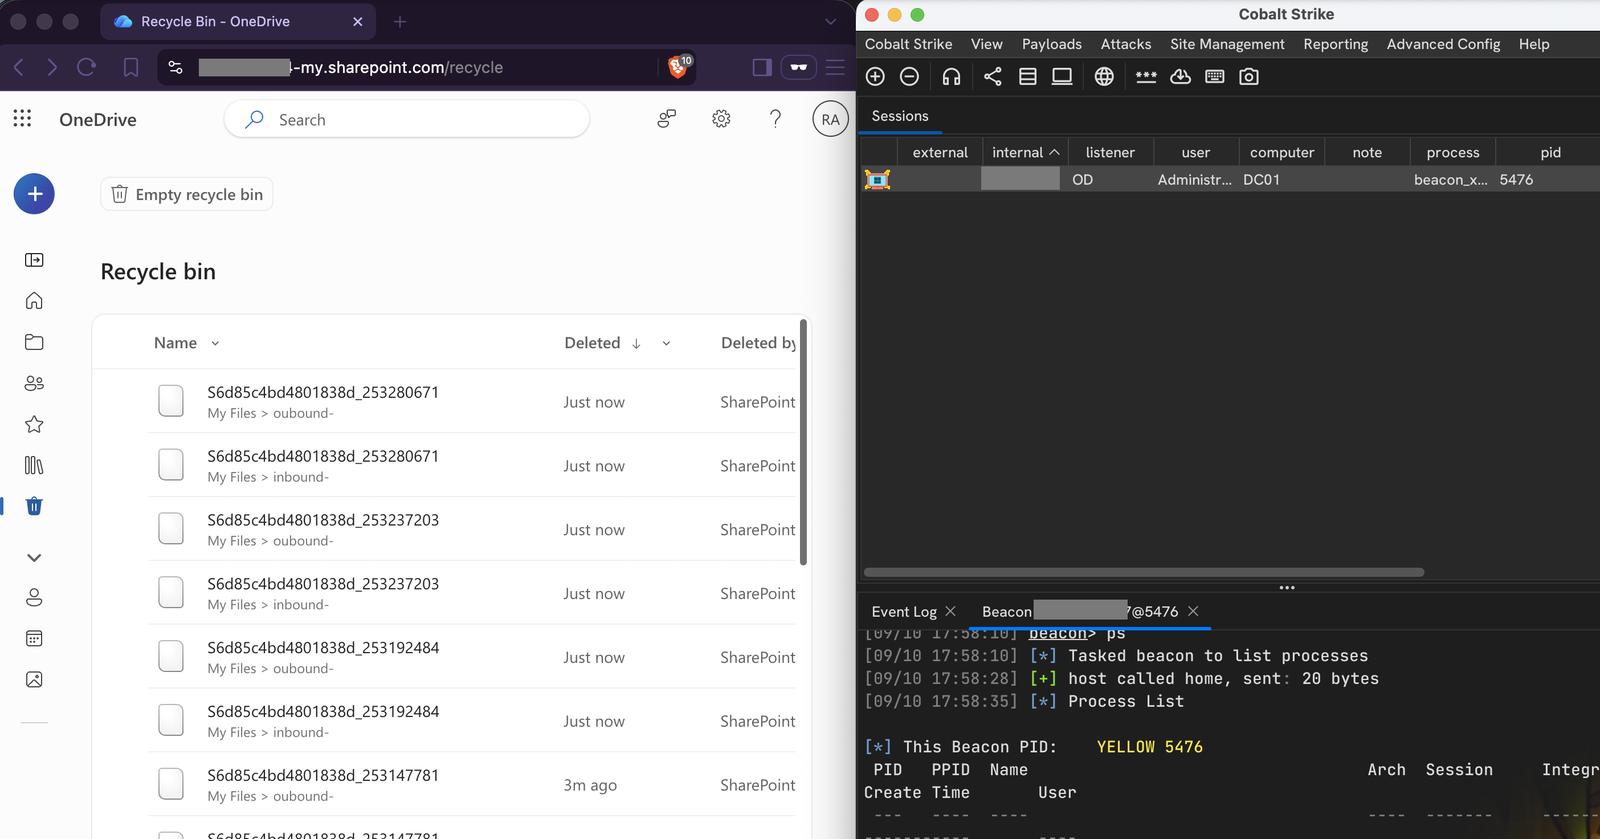 nmht3t/onedrive-udc2
OneDrive as a covert C2 transport for Cobalt Strike
 rvrsh3ll/azure-app-tools
Collection of tools to use with Azure Applications
 esonhugh/ingressnightmare-cve-2025-1974-exps
IngressNightmare POC. world first non-blind remote execution exploitation with multi-advanced exploitation methods. allow on disk exploitation.…
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.
 cenobyte-vincit/slot2
UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…
 offseckit/cve-2026-24207
CVE-2026-24207 — NVIDIA Triton SageMaker auth bypass to unauth RCE. Detection script, bypass demo, RCE-chain PoC, and IDS rules.
 chhhd/cve-2025-1974
Proof-of-concept exploit for CVE-2025-1974 (IngressNightmare) targeting Kubernetes Ingress-NGINX Admission Controller to achieve remote code…
 i3r1h0n/ingressnightterror
My view on IngressNightmare vulnerability (CVE-2025-1974)
 simoesctt/ctt-serverless-rce-v1.0---convergent-time-theory-enhanced-mcp-exploit
Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…
 scumfrog/fiberbreak
React2Shell Exploitation Tool (CVE-2025-55182)
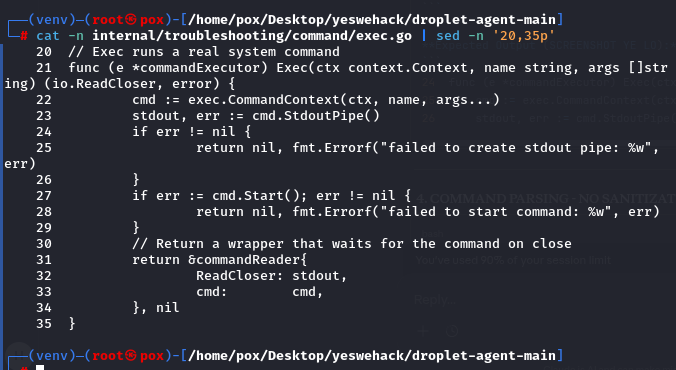 poxsky/cve-2026-24516-digitalocean-rce.
Technical analysis and PoC for CVE-2026-24516: Unauthenticated Root Remote Code Execution in DigitalOcean Droplet Agent (CVSS 10.0).