
CVE-2024-57394
 cwjchoi01/cve-2024-57394
Proof-of-concept exploit for CVE-2024-57394: low-privilege file restoration to System32 enabling DLL hijacking and local privilege escalation to…
binary-exploitationexploitationlateral-movement+4
cwjchoi01/cve-2024-57394Proof-of-concept exploit for CVE-2024-57394: low-privilege file restoration to System32 enabling DLL hijacking and local privilege escalation to…
 hwbp/clr-unhook
Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…
 withsecurelabs/doublepulsar-usermode-injector
A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…
 hackerhouse-opensource/nofaxgiven
Code Execution & Persistence in NETWORK SERVICE FAX Service
 mekitoci/cve-2023-6401
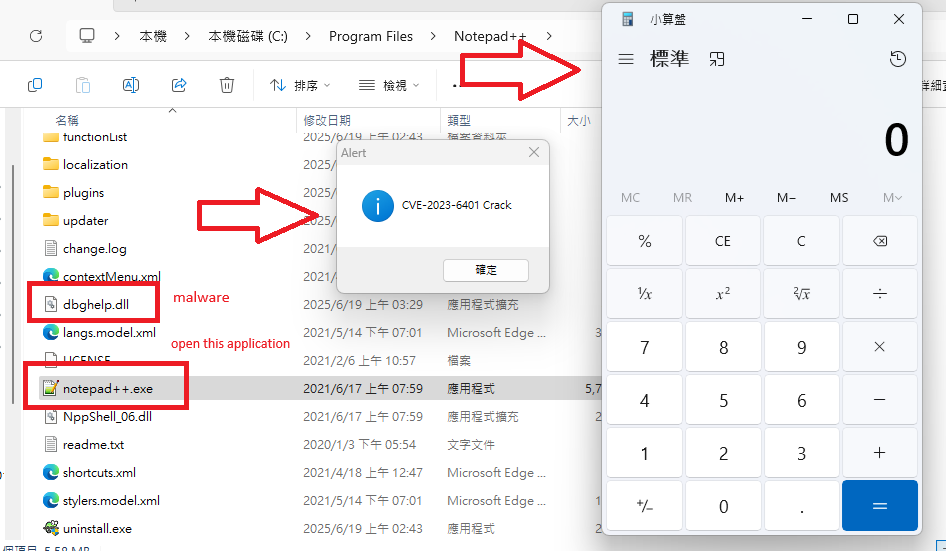
CVE-2023-6401 is a DLL hijacking vulnerability that allows attackers to execute arbitrary code by placing a malicious `dbghelp.dll` file in the…
 stephenfewer/reflectivedllinjection
Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
 s3c/globalprotect-ca-cert-ipc
Proof-of-concept exploit for CVE-2025-0117 in GlobalProtect, achieving privilege escalation to SYSTEM via a backdoored installer and DLL injection.
 muhammad-ali007/localpotato_cve-2023-21746
Proof-of-concept exploit for Windows local privilege escalation (CVE-2023-21746) abusing NTLM local authentication to gain SYSTEM privileges via SMB…
 trailer2/corsair---dll-planting-cve-2023-38822
DLL Planting in the Corsair iCUE v.5.3.102 CVE-2023-38822
 trailer2/cod-mw-warzone-2---cve-2023-38821
DLL Planting in the CoD MW Warzone 2 - CVE-2023-38821
 trailer2/dll-planting-slack-4.33.73-cve-2023-38820
DLL Planting in the Slack 4.33.73 - CVE-2023-38820
 shubham0d/zoom-dll-hijacking
A dll hijacking vulnerability in zoom meeting < 5.1.4. CVE-2020-9767
 surajhacx/helakuruv.1.1-dllhijack
Helakuru Version 1.1 DLL Hijack - CVE-2024-48605
 knight0x07/bumblecrypt
A Bumblebee-inspired Crypter
 killtr0/cve-2021-1675-printnightmare
PowerShell exploit for CVE-2021-1675 (PrintNightmare) performing local privilege escalation via Print Spooler, with custom DLL payload injection and…
 malwaretech/uacelevator
Passive UAC elevation using dll infection
 restdone/cve-2024-31771
Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…
 egebalci/amber
Reflective PE packer.