

LSTAR-EN
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
command-and-controlexploitationids-ips-evasion+9
moscowchill/lstar-enLSTAR - CobaltStrike Translated to EN
 momika233/cve-2024-21006
Proof-of-concept exploit for CVE-2024-21006 targeting Oracle WebLogic Server via T3/IIOP, enabling unauthenticated remote access to critical data.
 murataydemir/cve-2020-14883
[CVE-2020-14882] Oracle WebLogic Server Authenticated Remote Code Execution (RCE)
 momollax/cve-2025-53772-iis-webdeploy-rce
Proof-of-concept exploit for CVE-2025-53772, a remote code execution vulnerability in IIS WebDeploy via unsafe deserialization. Includes customizable…
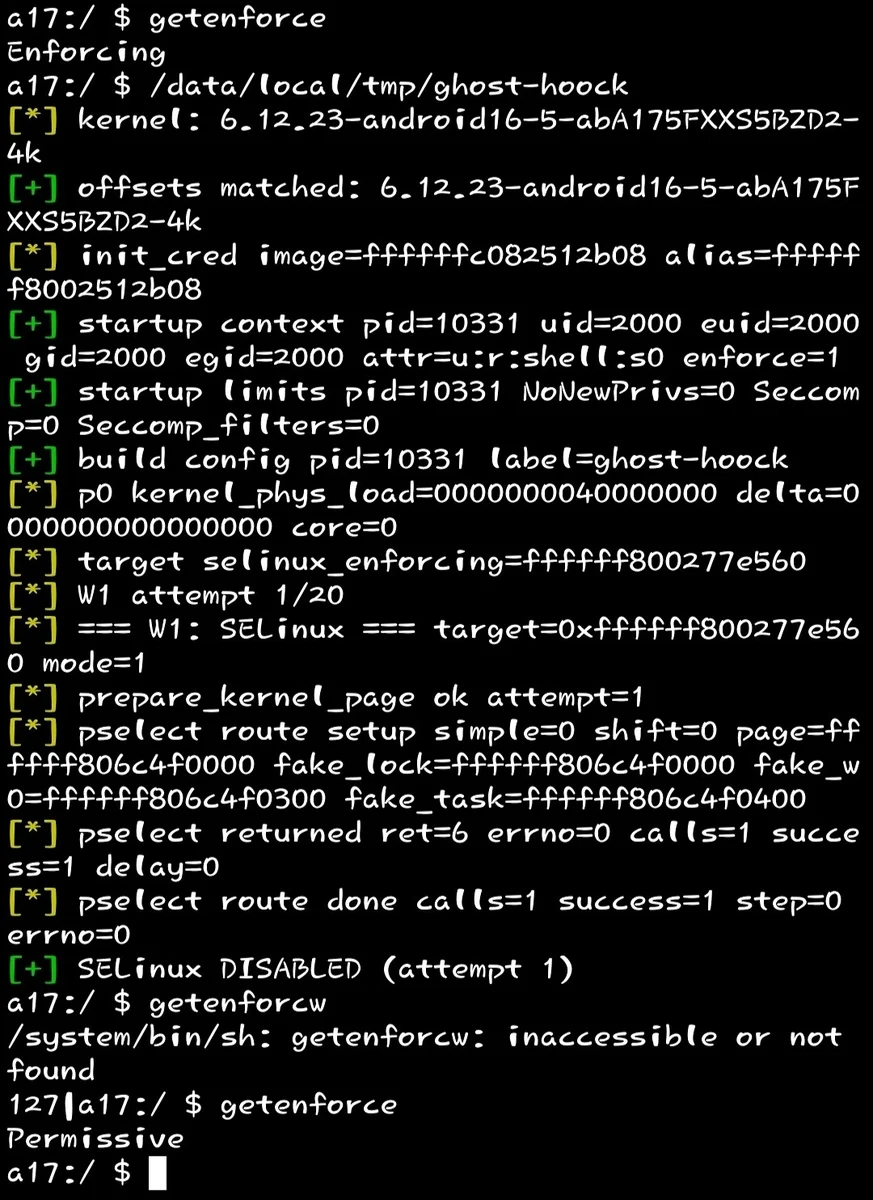 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 r3vpwnx/cve-2025-55182
Standalone exploit for CVE-2025-55182 achieving unauthenticated RCE in Next.js App Router via React Server Components Flight deserialization, with…
 kuzeyardabulut/cve-2024-1065
Proof-of-concept exploit for CVE-2024-1065, demonstrating page cache exploitation via a use-after-free in the ARM Mali GPU kernel driver to achieve…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 bugel/cve-2026-43499-m3q-azf1
This package is not a complete root. It flips SELinux to Permissive and holds reclaim long enough for follow-on work. Host `uid=0` is not achieved…
 ben-slates/cve-2024-37054
Proof-of-concept exploit for CVE-2024-37054, a pickle deserialization RCE in MLflow Tracking Server. Authenticated attackers can overwrite model…
 biitts/roundcube-cve-2025-49113
Proof-of-concept to CVE-2025-49113
 kondukto-io/vulnerable-next-js-poc
Proof-of-concept exploit for CVE-2025-55182 (React2Shell), a critical RCE vulnerability in React Server Components via unsafe deserialization.…
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 vr00mm/cve-2025-49144
PoC CVE-2025-49144
 manhndd/cve-2019-6329
Local Privilege Escalation in HP Support Assistant
 fortbridge-uk/libheif-grid-nextjs-rce
Private Fortbridge PoC for the CVE-2026-32740 Next.js/sharp leak-to-memcpy-GOT RCE chain
 gl1tch0x1/dirtyclone
Proof-of-concept local privilege escalation tool exploiting a kernel XFRM/ESP vulnerability (CVE-2026-43503) via crafted AES-CBC encrypted payloads…
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit