

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
16 results
emp3r0r preview

emp3r0r

GitHubjm33-m0/emp3r0r

Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
anti-botcommand-and-controlids-ips-evasion+10
1.8k
8h 1m ago
Stuxnet preview

Stuxnet

GitHubsadpainy/stuxnet

Educational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…
educationexploitationlateral-movement+4
59014 days ago
Silverseal preview

Silverseal

GitHubidov31/silverseal

Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
binary-exploitationexploitationmalware-analysis+4
17323 days ago
rvbbit-arsenal preview

rvbbit-arsenal

GitHubbuter-chkalova/rvbbit-arsenal

Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
command-and-controldefensive-toolseducation+5
161 month ago
Furtex preview

Furtex

GitHubmatheuzsecurity/furtex

Post-exploitation and evasion research toolkit for Linux.
binary-analysiscommand-and-controlexploitation+6
2933 months ago
Nidhogg preview

Nidhogg

GitHubidov31/nidhogg

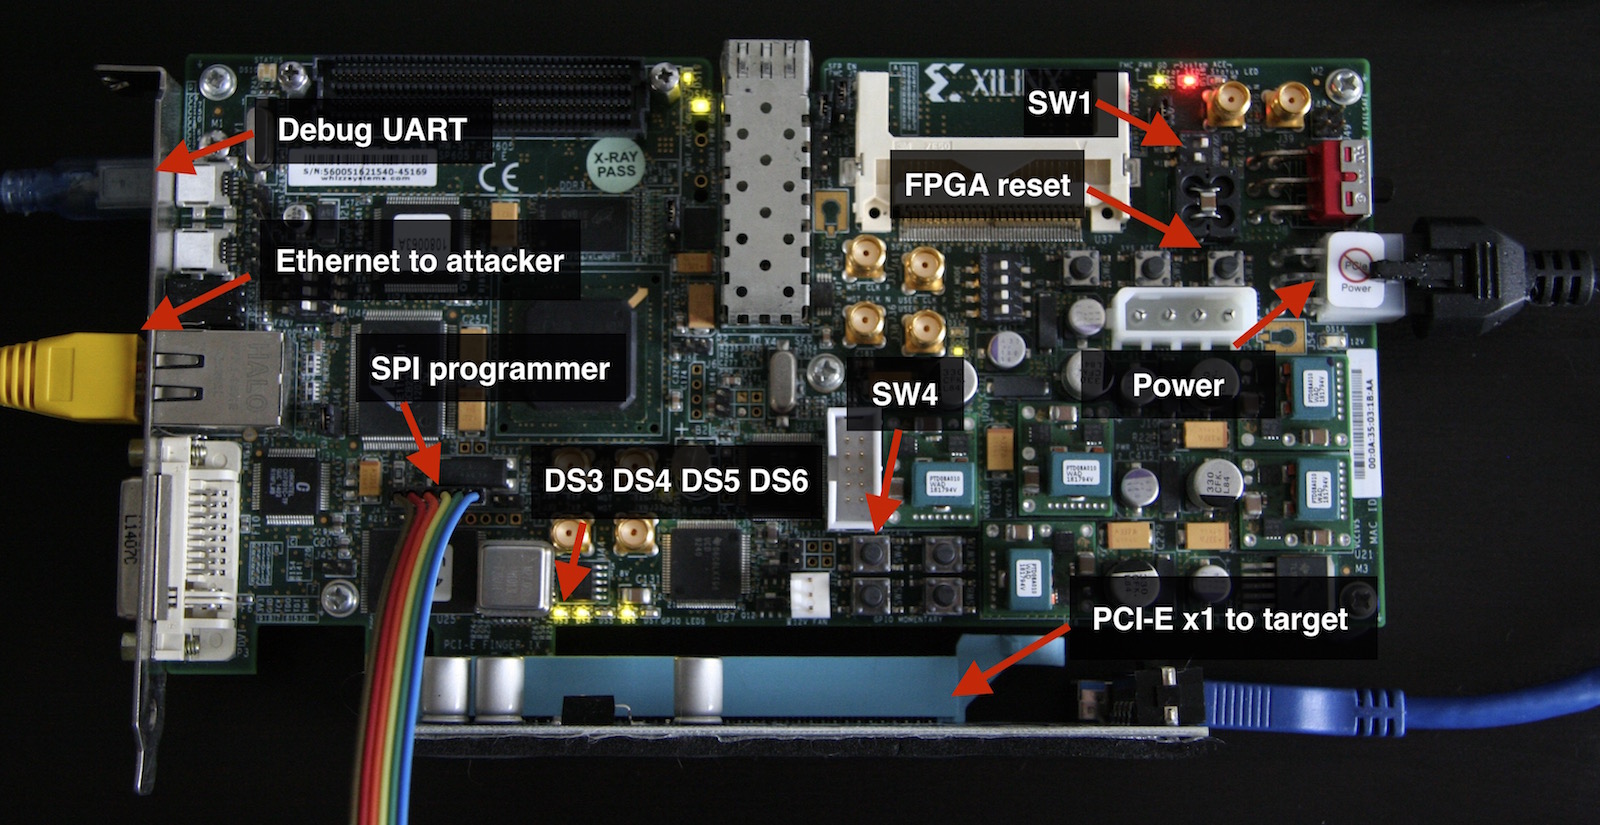
Windows rootkit for Intel x64 with 25+ features, demonstrating rootkit techniques compatible with all Windows 10 and Windows 11 versions.
command-and-controlpayload-developmentprivilege-escalation+1
2.5k4 months ago
s6_pcie_microblaze preview

s6_pcie_microblaze

GitHubcr4sh/s6_pcie_microblaze

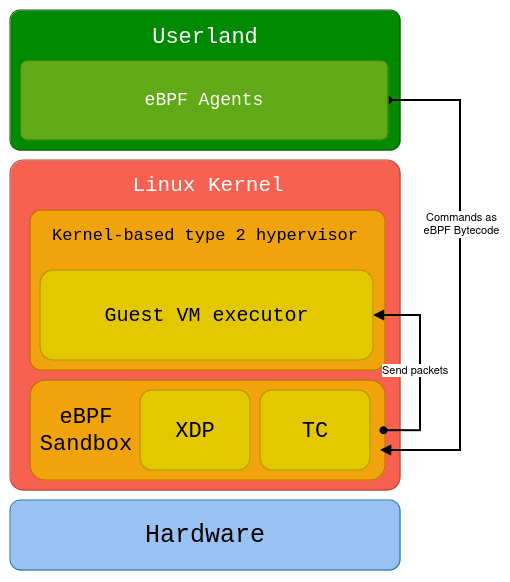
PCI Express DIY hacking toolkit for Xilinx SP605. This repository is also home of Hyper-V Backdoor and Boot Backdoor, check readme for links and info
command-and-controldata-exfiltrationexploitation+4
8967 months ago
blackpill preview
Archived

blackpill

GitHubshard77/blackpill

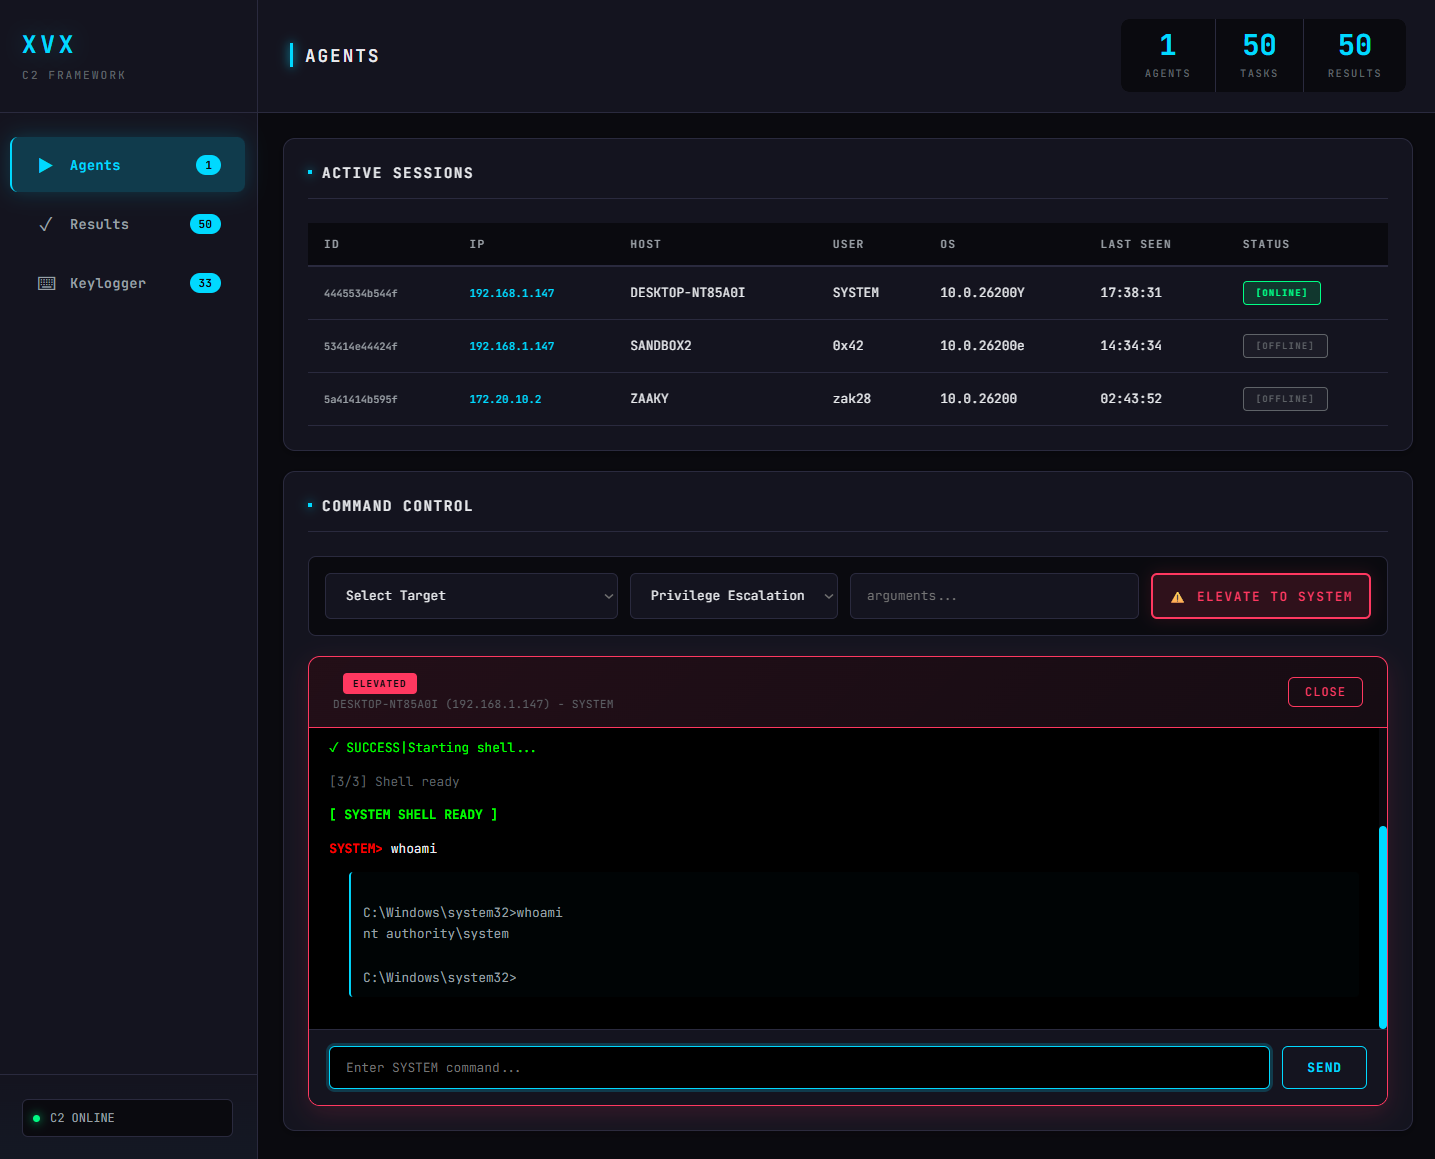
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
binary-exploitationcommand-and-controlids-ips-evasion+7
3418 months ago
PULSE-C2 preview

PULSE-C2

GitHub28zaaky/pulse-c2

HTTPS C&C Framework with encrypted beacons, web dashboard, and Windows agent.
command-and-controlencryption-decryption-toolspayload-development+2
538 months ago
cve-2017-5123 preview

cve-2017-5123

GitHubnabilboudra/cve-2017-5123

Educational demonstration of CVE-2017-5123 kernel exploit, ICMP-based rootkit command-and-control, and OS command injection vulnerable web…
binary-exploitationcommand-and-controleducation+5
10 months ago
talkingBen preview

talkingBen

GitHubm4rm0k/talkingben

UEFI rootkit under development focusing on privilege escalation, C2 integration, and anti-EDR/AV evasion for real-world malware deployment.
command-and-controlexploitationmalware-analysis+4
11 year ago
Jormungandr preview

Jormungandr

GitHubidov31/jormungandr

Jormungandr is a kernel implementation of a COFF loader, allowing kernel developers to load and execute their COFFs in the kernel.
adversarial-attackpayload-developmentpost-exploitation+1
2423 years ago
Kernel-Process-Hollowing preview
Archived

Kernel-Process-Hollowing

GitHubxaff-xaff/kernel-process-hollowing

Windows x64 kernel mode rootkit process hollowing POC.
ids-ips-evasionpayload-developmentpost-exploitation+1
1943 years ago
kli-ex preview

kli-ex

GitHubgmh5225/kli-ex

Extended kernel lazy importer for Windows drivers that resolves APIs at runtime with encrypted, cached import names to hide kernel function usage…
binary-analysiscryptographydefensive-tools+4
343 years ago
Umbra preview

Umbra

GitHubh3xduck/umbra

A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
command-and-controleducationencryption-decryption-tools+6
1385 years ago
WindowsRegistryRootkit preview
Archived

WindowsRegistryRootkit

GitHubcr4sh/windowsregistryrootkit

Kernel rootkit, that lives inside the Windows registry values data

command-and-controlexploitationmalware-analysis+2
5049 years ago