

metasploit-payloads
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
command-and-controlexploitationexploit-frameworks+9
2.1k
rapid7/metasploit-payloadsUnified repository for different Metasploit Framework payloads
 aipeacs/sc3010-computer-security
Using Struts2 and PowerShell to recreate CVE-2017-5638 OGNL Injection vulnerability.
 gu-007/struts2-tool
Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool
 14free/log4j2-vuln-lab
CVE-2021-44228 (Log4Shell) 漏洞复现靶场 | SpringBoot + Log4j2 2.14.1 | 3 个攻击向量 PoC 验证
 hypnguyen1209/log4j2-rce
Pre-auth RCE via FilteredObjectInputStream MarshalledObject bypass in Apache Log4j 2
 velessecurity/cve-2020-14882-weblogic-analysis
Technical analysis and clean Java Thread Echo PoC for Oracle WebLogic Server vulnerability chain.
 gutierre0x80/cve-2026-59827
Technical analysis and proof of concept for CVE-2026-59827, a critical unsafe Java deserialization vulnerability in Metabase leading to remote code…
 jiahong-guan/log4j-shell-poc
A Proof-Of-Concept for the CVE-2021-44228 vulnerability.
 joaovicdev/exploit-cve-2026-40901
Automated exploit for DataEase: 4-vulnerability chain (auth bypass, JDBC blocklist bypass, SQL injection, Java deserialization) achieving…
 oscerd/cve-2026-40859
Reproducer for CVE-2026-40859 — Apache Camel camel-netty-http / camel-vertx-http producer-side unsafe deserialization of HTTP response bodies (RCE)
 oscerd/cve-2026-27172
Reproducer for CVE-2026-27172: Apache Camel camel-consul ConsulRegistry Java deserialization (RCE)
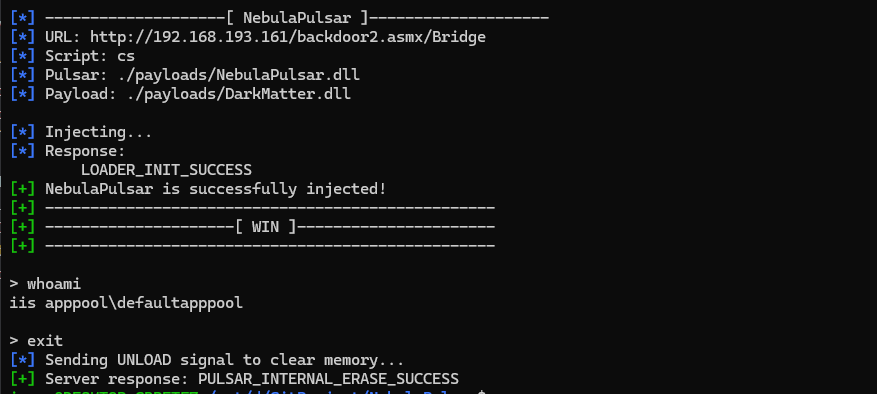 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 biitts/cve-2026-58138-conductor-unauth-rce
CVE-2026-58138 — Conductor (3.21.21..<3.30.2) unauthenticated RCE via INLINE GraalVM evaluator (HostAccess.ALL). Lab + PoC, verified e2e (root).
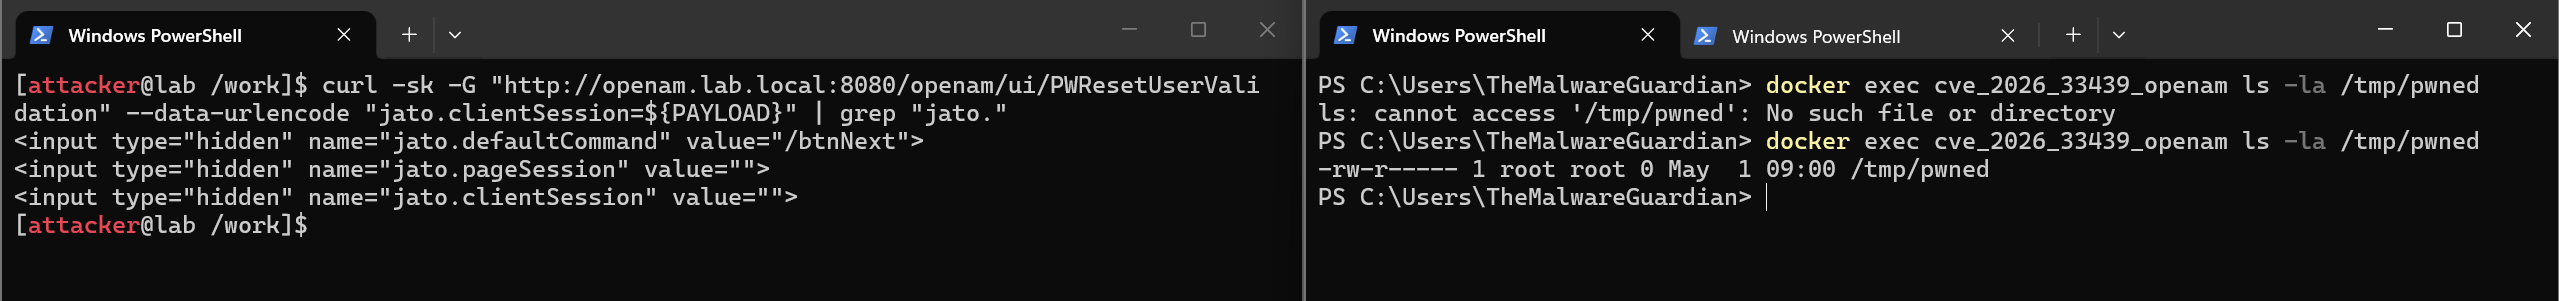 themalwareguardian/cve-2026-33439
First publicly shared exploit implementation for CVE-2026-33439 (OpenAM pre-auth RCE via jato.clientSession deserialization).
 ibonok/cve-2026-33439-poc
Exploit for OpenAM pre-auth RCE (CVE-2026-33439) using a Java deserialization gadget chain to execute commands and return output directly in the HTTP…
 azefzafyoussef/cve-2026-33229
Proof-of-concept exploit for CVE-2026-33229, an XWiki RCE via Apache Velocity sandbox bypass, with technical details and a working payload.
 seahcy/cve-2025-24813
Instructions for rapid deployment of Tomcat v9.0.90 with java 25.0.1 2025-10-21 LTS on Windows Server 2019 Standard for lazy researchers.
 matejsmycka/cve-2018-14324-exploit
Hacking Eclipse GlassFish - CVE-2018-14324