

emp3r0r
 jm33-m0/emp3r0r
Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
anti-botcommand-and-controlids-ips-evasion+10
1.8k0 days ago
jm33-m0/emp3r0rSelf‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
 cenobyte-vincit/dyen
In-memory Mach-O dylib loader for stock macOS Python; decrypts, maps, and runs payloads without dlopen or writing to disk, with optional encrypted…
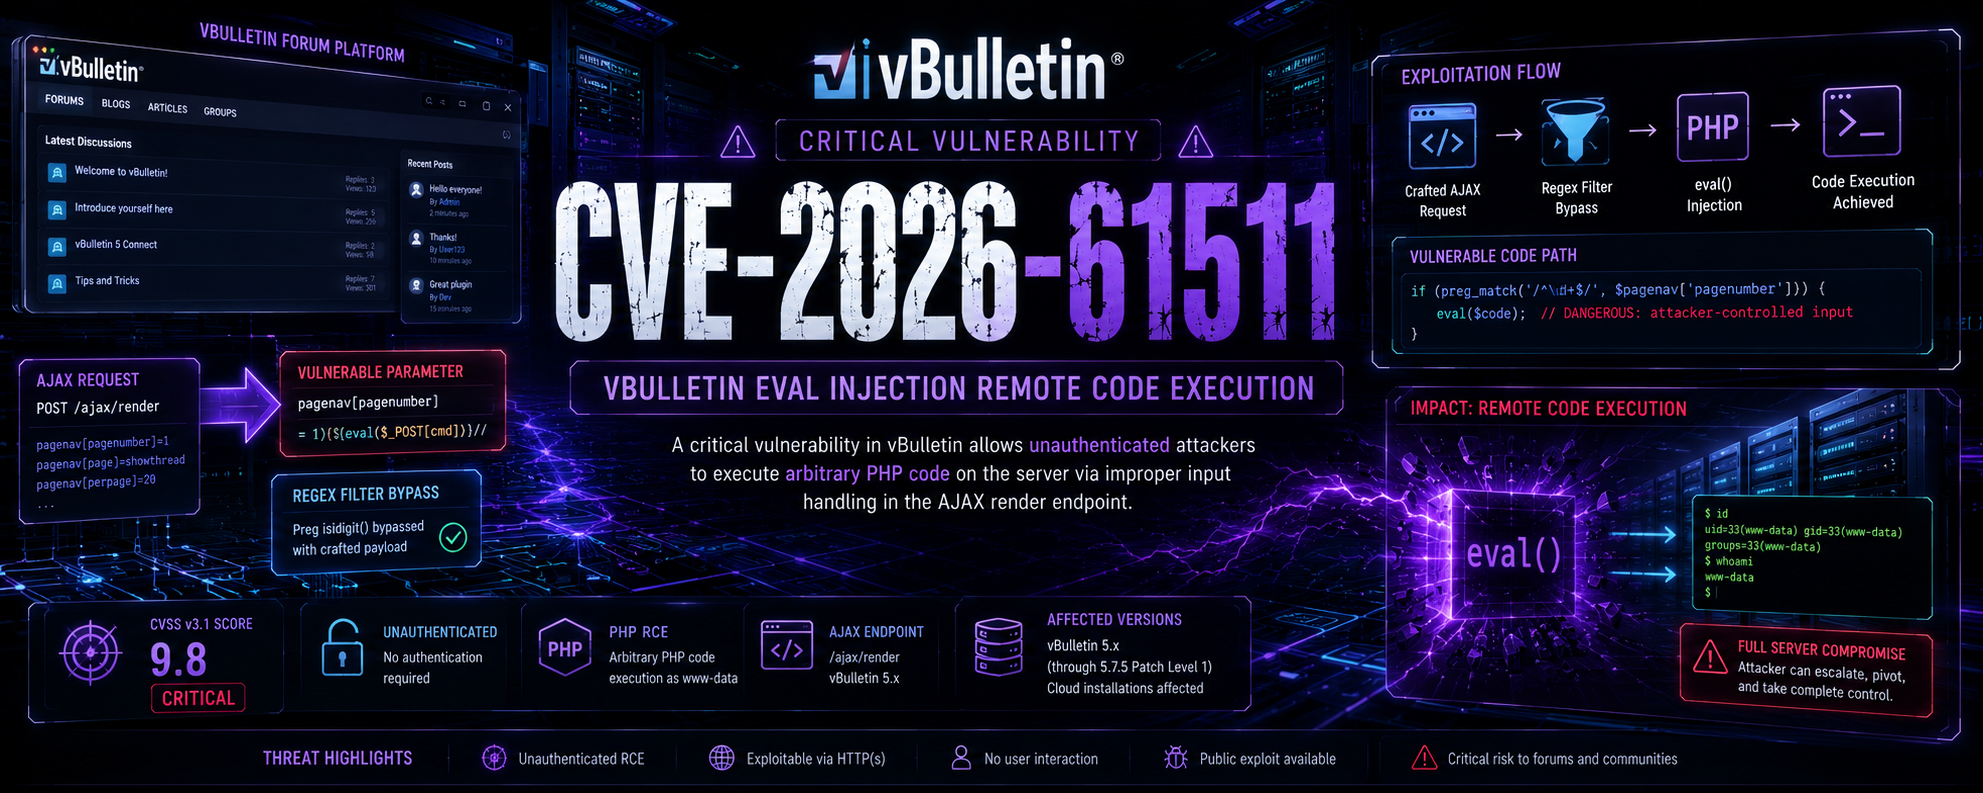 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
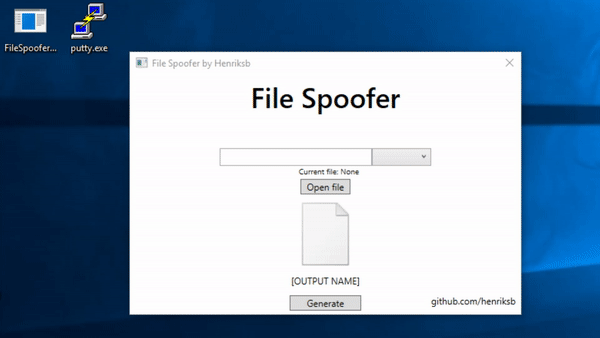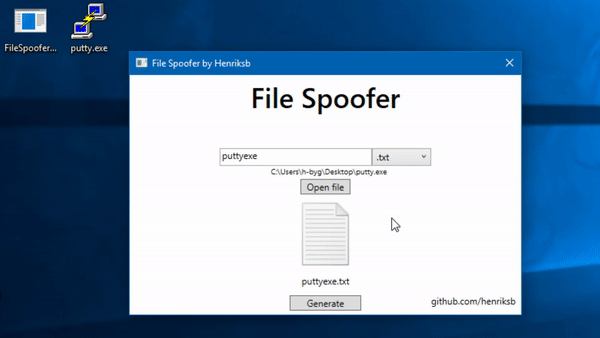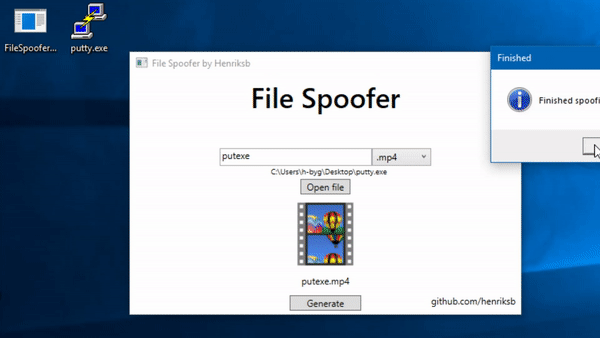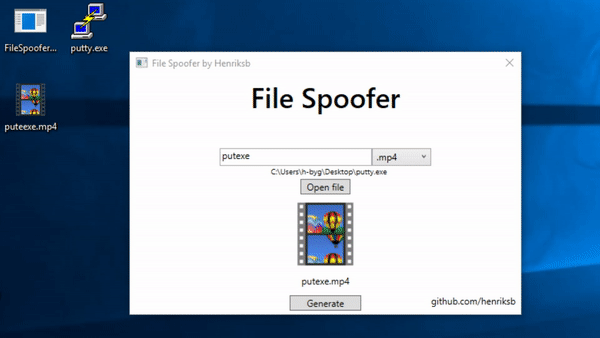 henriksb/extensionspoofer
Spoof file icons and extensions in Windows
 egebalci/sgn
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…
 icecubesandwich/caddysmith
Generate Caddy redirector configs from Cobalt Strike or Sliver C2 profiles.
 kudaes/dinvoke_rs
Dynamically invoke arbitrary unmanaged code
 sentinelxofficial/cve-2025-55182
Pre-authentication RCE exploit for CVE-2025-55182 (React2Shell) targeting React Server Components. Features scanning, OAST verification, WAF bypass,…
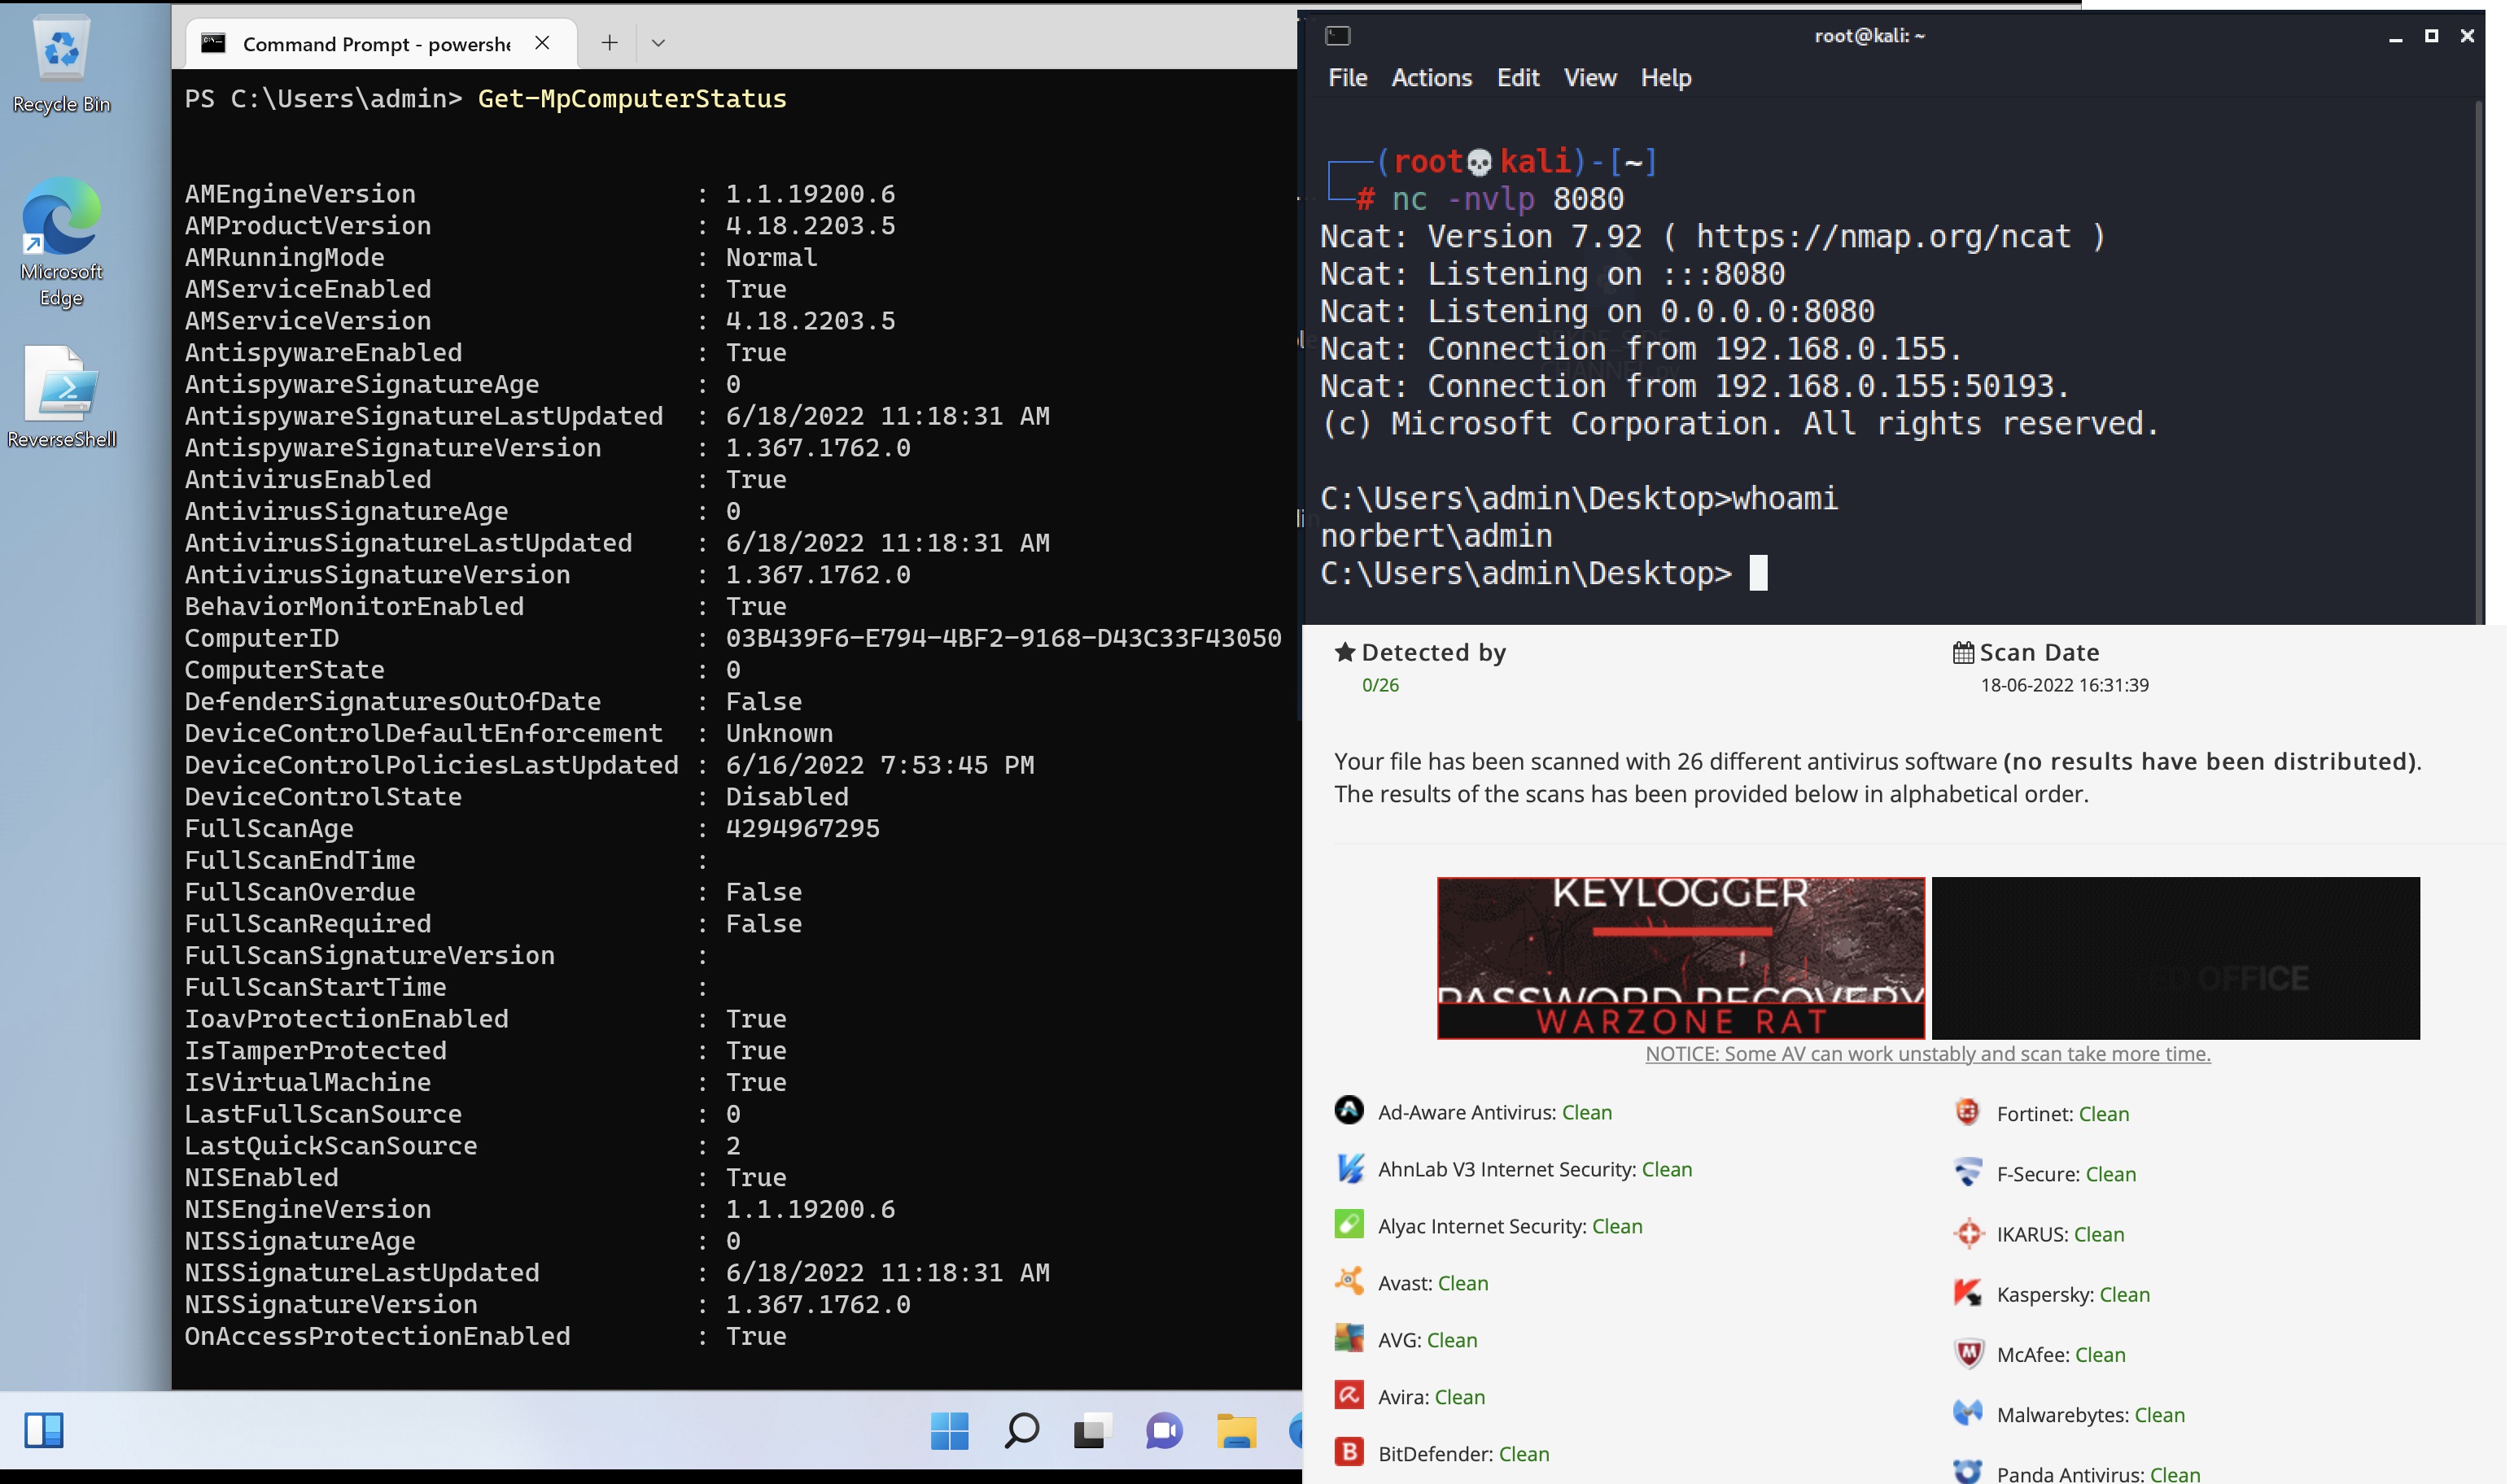 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).
 mein-0/cve-2026-0828
Proof-of-concept exploit for CVE-2026-0828, a BYOVD vulnerability in Safetica ProcessMonitorDriver.sys allowing unprivileged termination of…
 rasta-mouse/crystal-kit
Evasion kit for Cobalt Strike
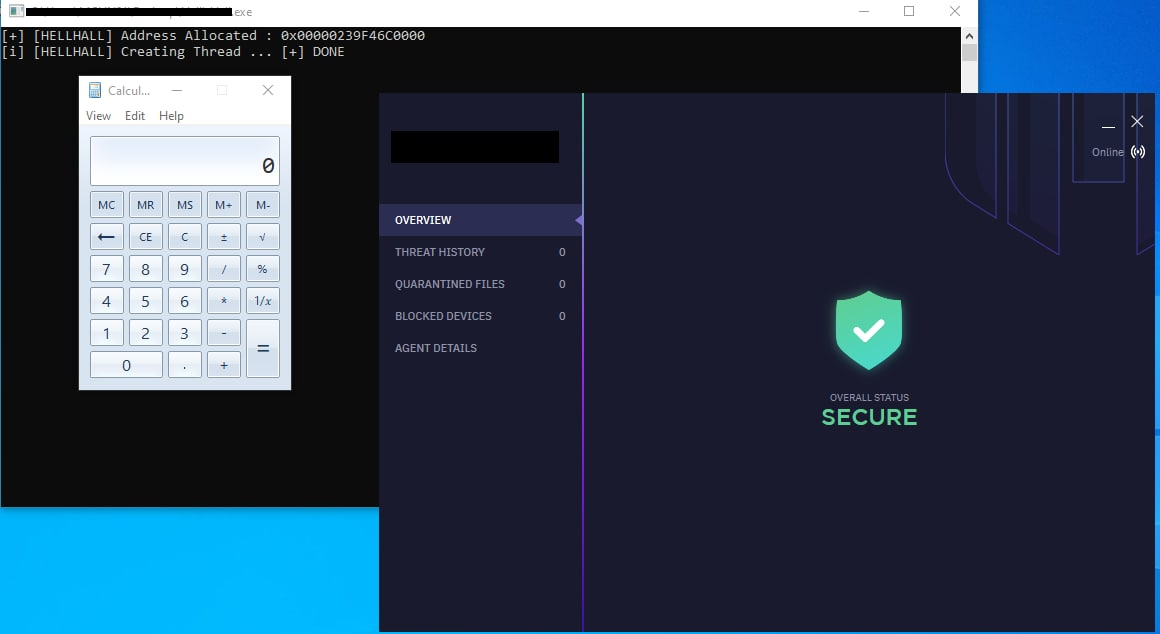 maldev-academy/hellhall
Performing Indirect Clean Syscalls
 rasta-mouse/crystal-loaders
A small collection of Crystal Palace PIC loaders designed for use with Cobalt Strike
 simoesctt/-ctt-pan-os-exploit-cve-2024-340
CTT-PAN-OS-Exploit – CVE-2024-3400 (CVSS 10.0) with Convergent Time Theory enhancement. Uses α = 0.0302011 temporal dispersion, 33-layer phase…
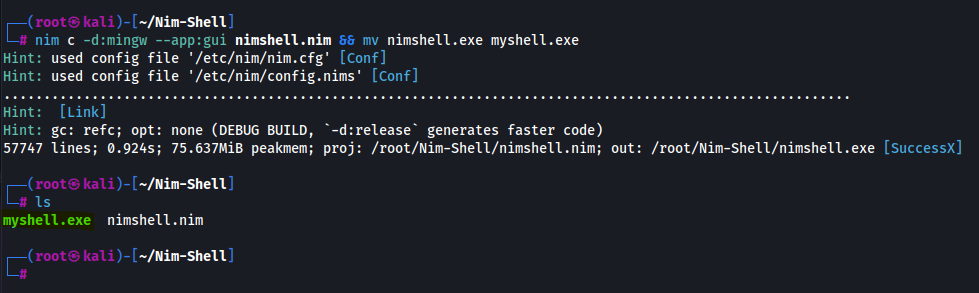 emrekybs/nim-shell
Reverse shell that can bypass windows defender detection
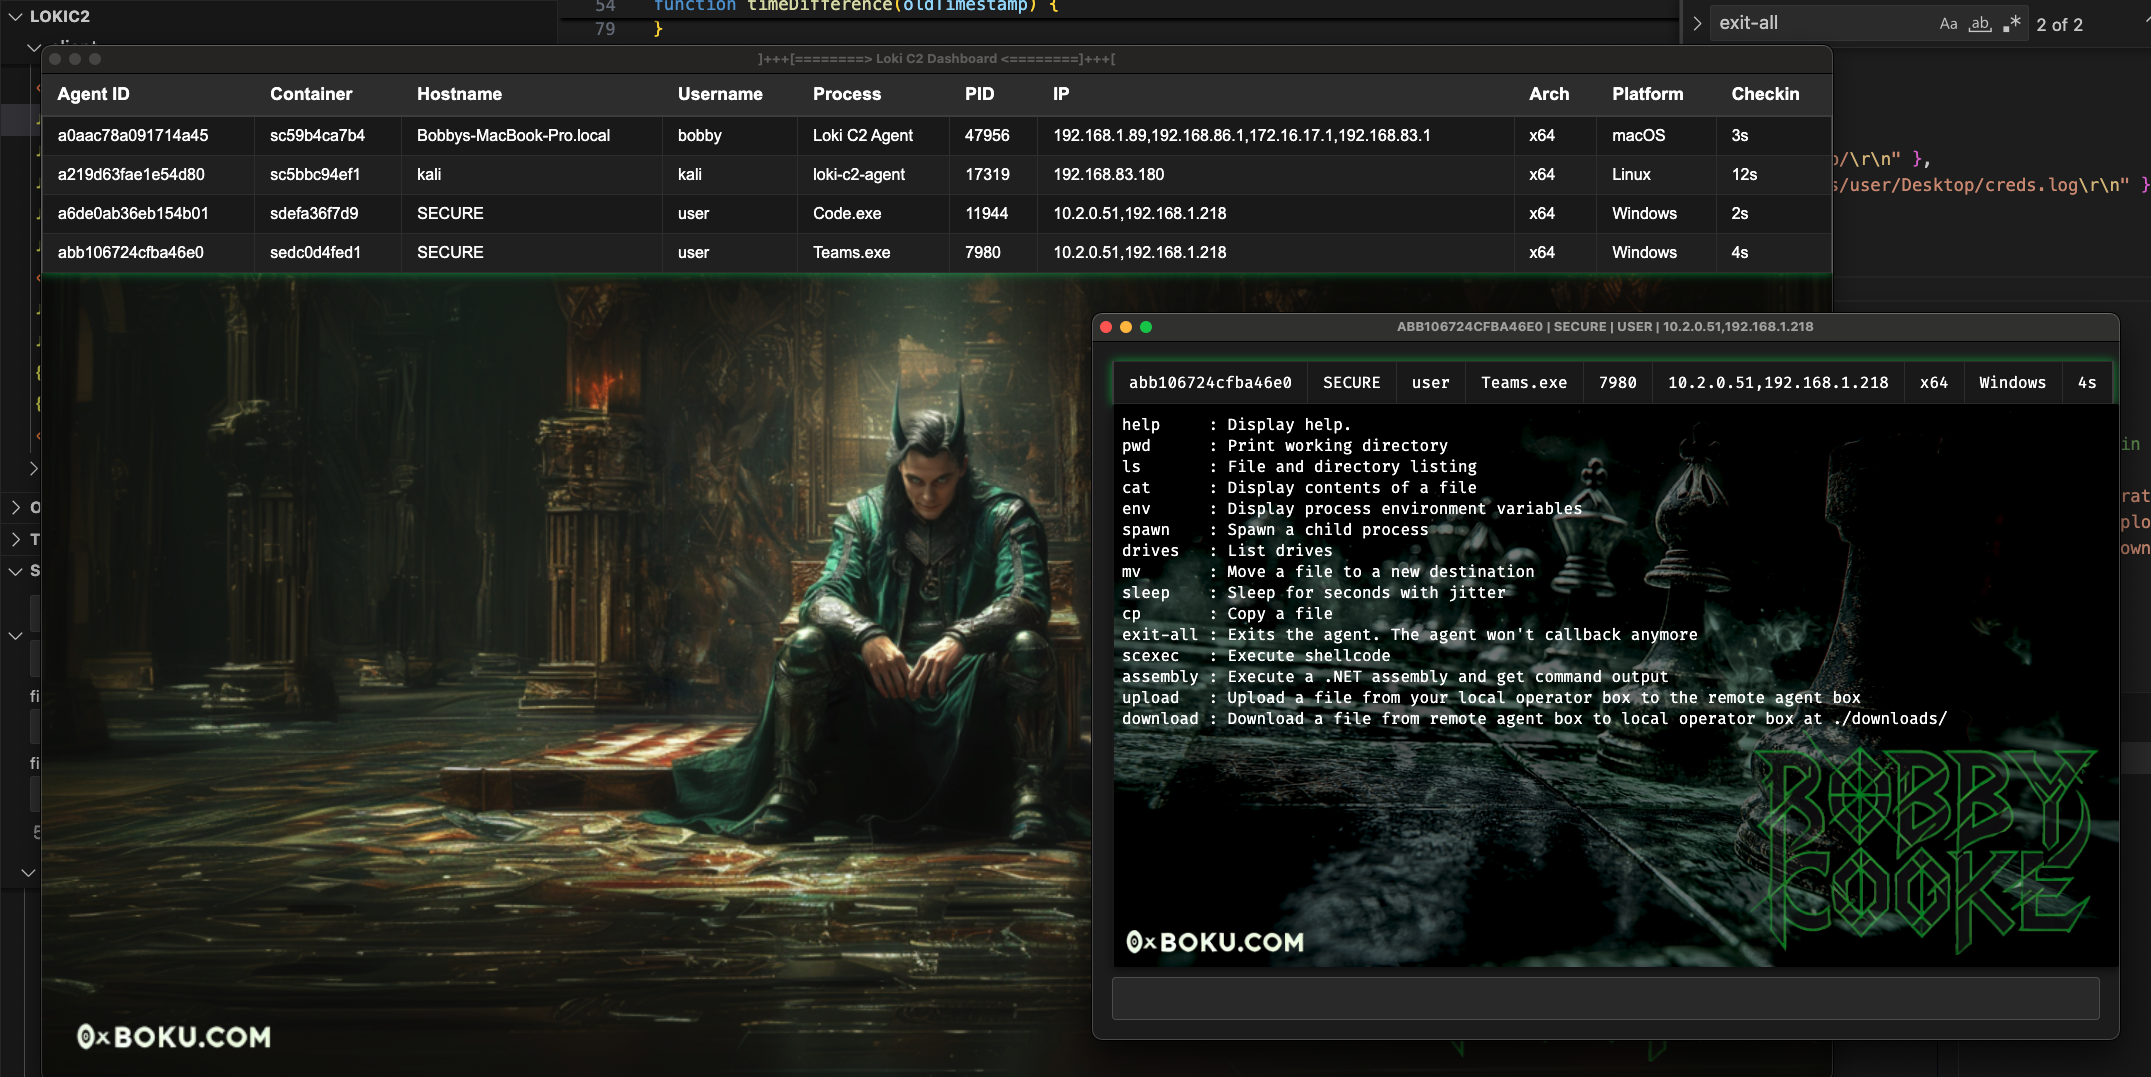 boku7/loki
🧙♂️ Node.js Command & Control for Script-Jacking Vulnerable Electron Applications
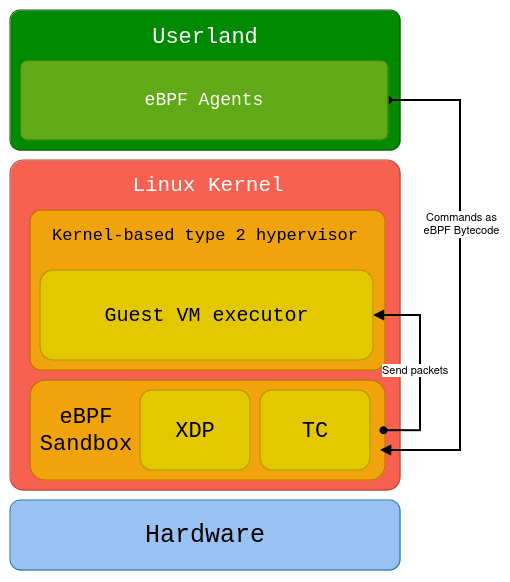 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 hackerhouse-opensource/offensivelua
Offensive Lua.