
ExtensionSpoofer
 henriksb/extensionspoofer
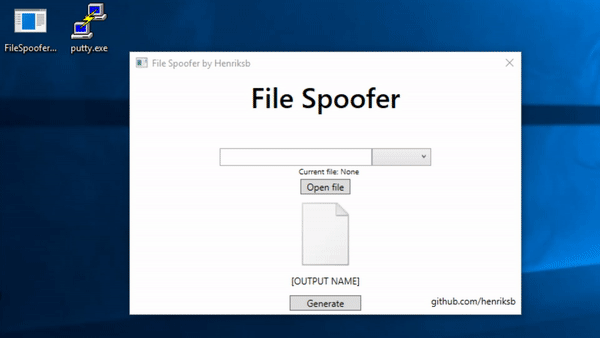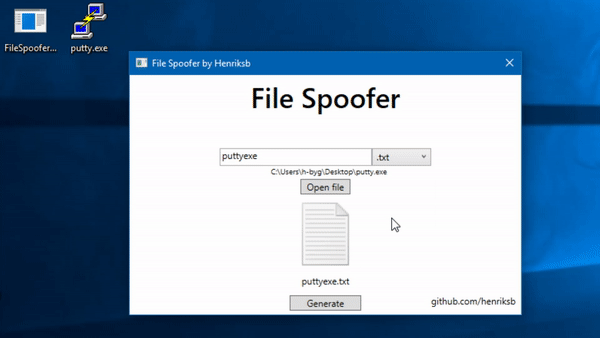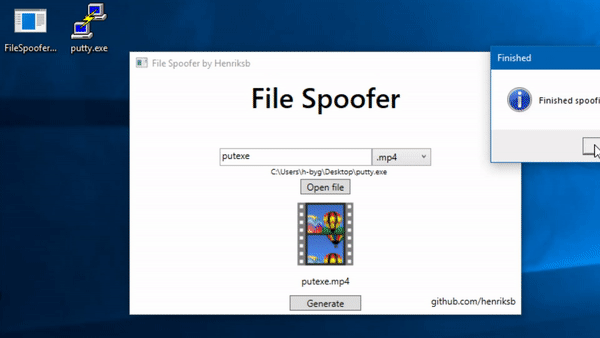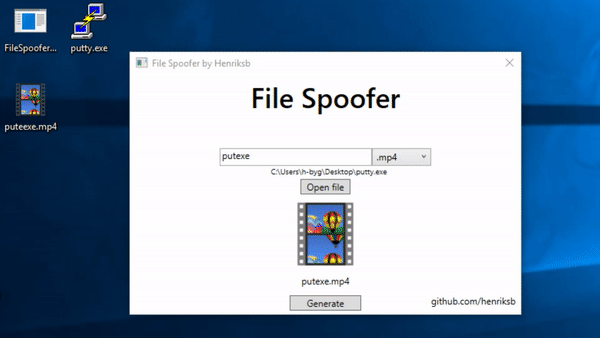
Spoof file icons and extensions in Windows
ids-ips-evasionimpersonation-toolsmalware-analysis+3
1872 months ago
henriksb/extensionspooferSpoof file icons and extensions in Windows
 bridgeralderson/cve-2026-58424
A flaw in Gitea Open Source Git Server’s approval‑gate logic allows a pull request that originates from a permanent fork to merge without satisfying…
 rat5ak/cve-2026-50343-installservice-eop
CVE-2026-50343 InstallService StaticPluginMap EoP - standard user to SYSTEM
 stuub/appsmith-1.98-stored-xss-exploit
Automating the exploitation of CVE-2026-7299 - Stored XSS via Database Table/Column Names in SQL Autocomplete within Appsmith =>1.99. Initial…
 bytereaper77/cve-2025-47917
PoC exploit for CVE-2025-47917: Use-After-Free in mbedTLS leading to remote code execution.
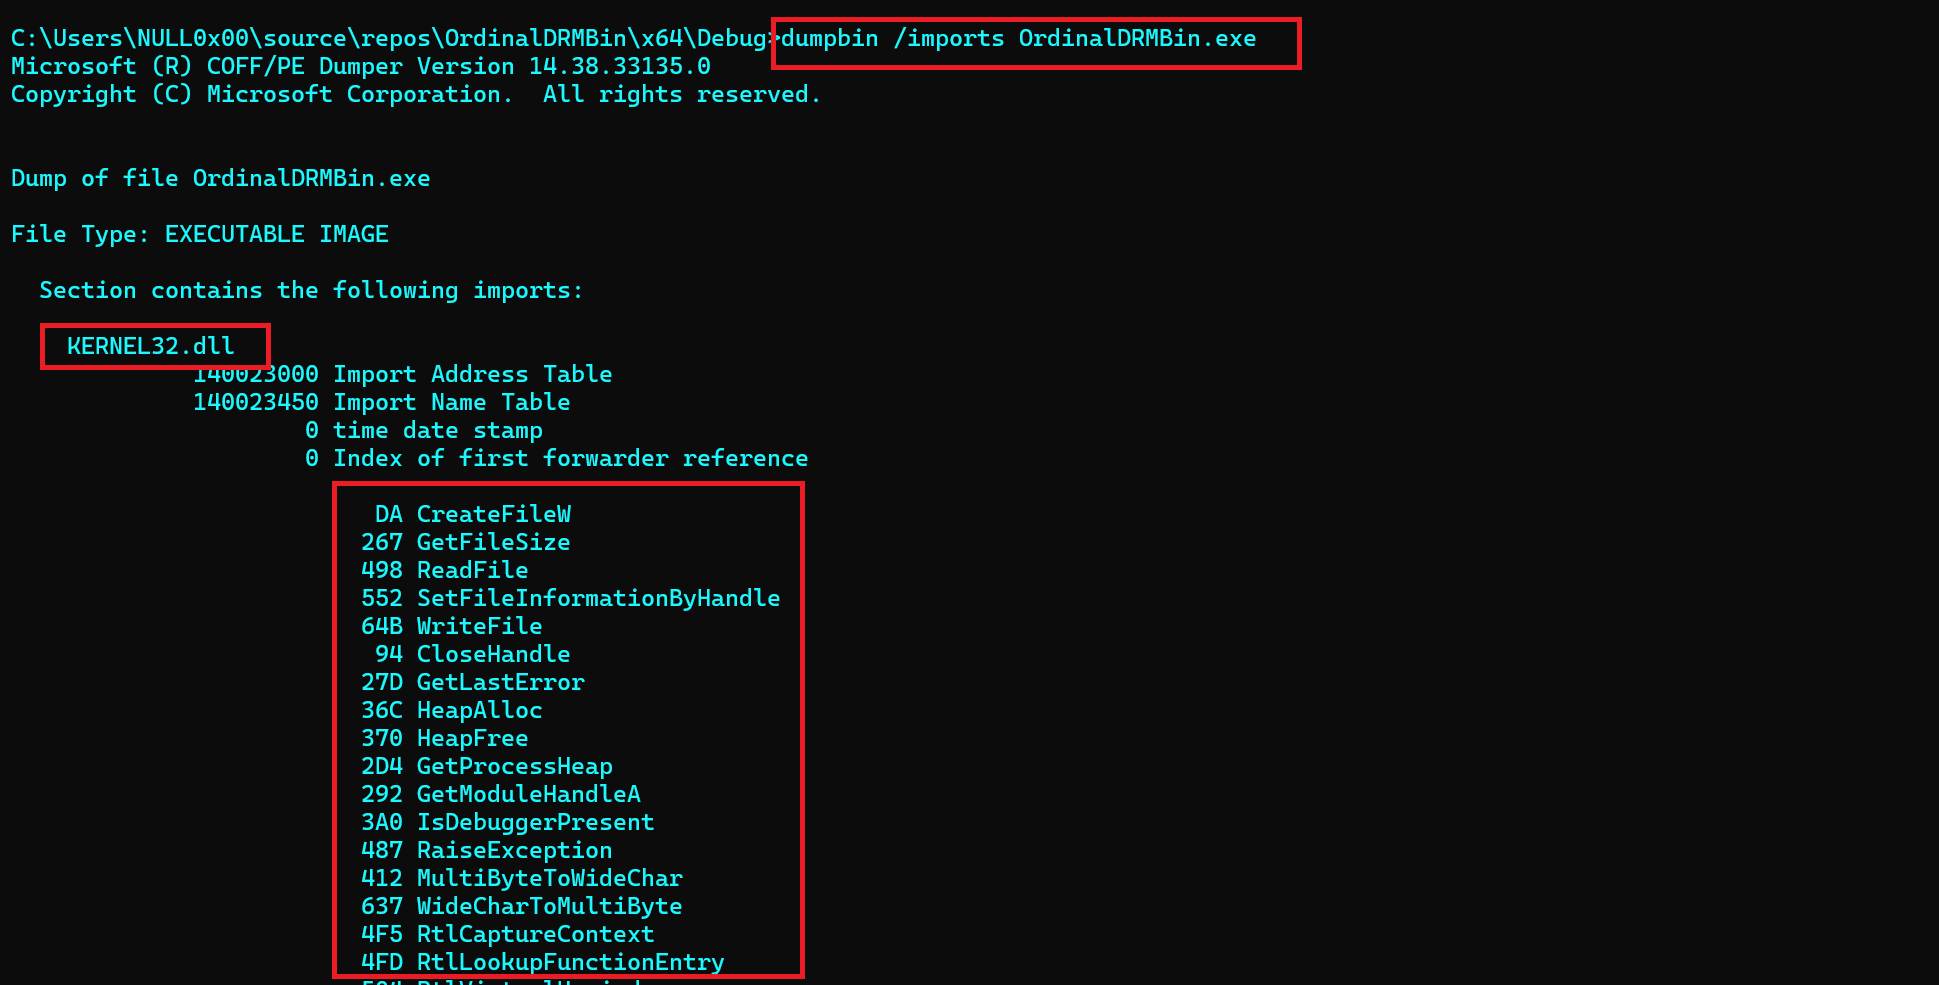 maldev-academy/drmbinviaordinalimports
Create Anti-Copy DRM Malware
 mbadanoiu/cve-2023-51518
CVE-2023-51518: Preauthenticated Java Deserialization via JMX in Apache James
 nettitude/aladdin
Generates initial access payloads abusing AddInProcess.exe via .NET deserialization, supporting HTA, VBA, JS, and CHM templates for in-memory code…
 gmh5225/kli-ex
Extended kernel lazy importer for Windows drivers that resolves APIs at runtime with encrypted, cached import names to hide kernel function usage…
 tremwil/ds3-nrssr-rce
Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
 ustayready/casperstager
PoC for persisting .NET payloads in Windows Notification Facility (WNF) state names using low-level Windows Kernel API calls.
 v-p-b/buherablog-cve-2013-1488
PoC Java exploit based on http://www.contextis.com/research/blog/java-pwn2own/