

khaos-c2
 28zaaky/khaos-c2
KHAOS is a modern C2 framework that routes agent traffic through cloud services already trusted by enterprise networks.
command-and-controllateral-movementpayload-development+5
238
28zaaky/khaos-c2KHAOS is a modern C2 framework that routes agent traffic through cloud services already trusted by enterprise networks.
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
 razureink/fucker
Penetration testing framework with AI-driven decision engine
 jakobfriedl/tgt-monitor-bof
Async BOF to automatically extract or renew Kerberos TGTs on a target system.
 davidcarliez/cve-2026-58635-poc
PoC for CVE-2026-58635: Windows Narrator Braille Local Privilege Escalation
 synacktiv/dcomillusionist
DCOM in memory and fileless lateral movement techniques through .Net deserilization
 octoberfest7/dscourier_bof
BOF POC of the DSCourier project / invoking WinGet via COM
 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 jacobtaylor3/cve-2021-21220
Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.
 spaceplant/fortilpe
Local privilege escalation exploit for CVE-2025-62676.
 0xsh3llf1r3/coldwer
Cobalt Strike BOF to freeze EDR/AV processes and dump LSASS using WerFaultSecure.exe PPL bypass
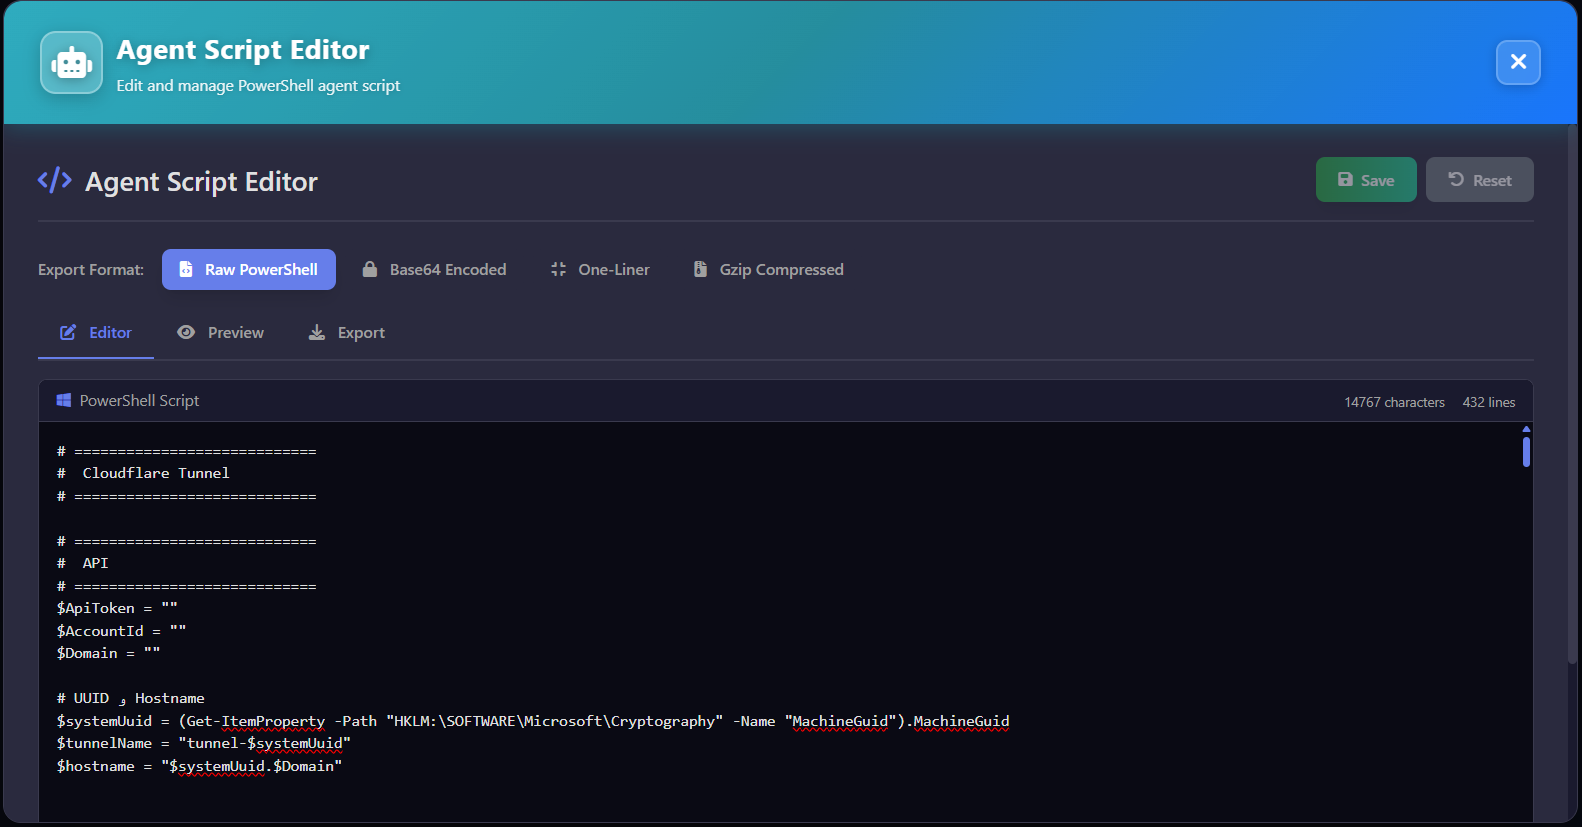 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
 irjfifndn-prog/blackash-cve-2025-33073
CVE-2025-33073
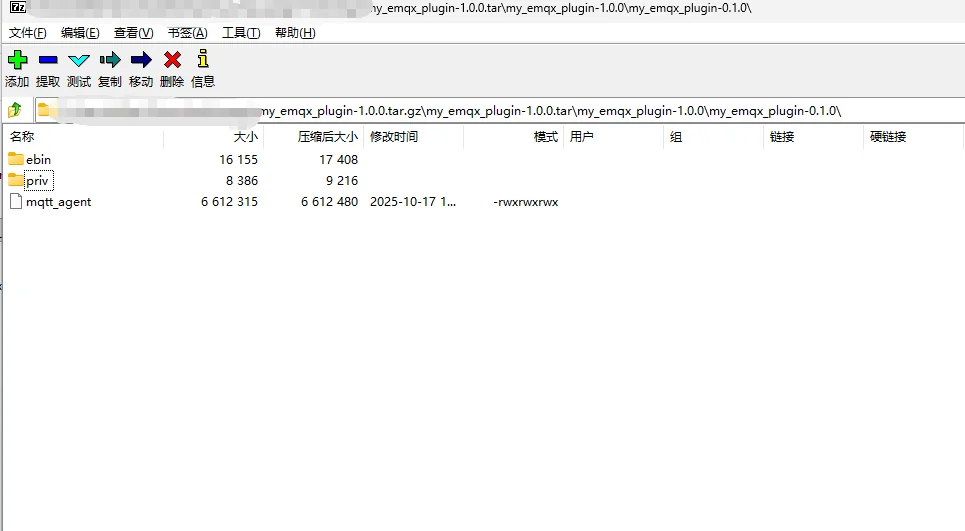 f1r3k0/cve-2025-52136
Exploit for CVE-2025-52136 enabling RCE on EMQX control panel via plugin upload, with MQTT-based command agent and SOCKS5 tunnel for out-of-band C2…
 a0yami/cve-2025-50505
Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
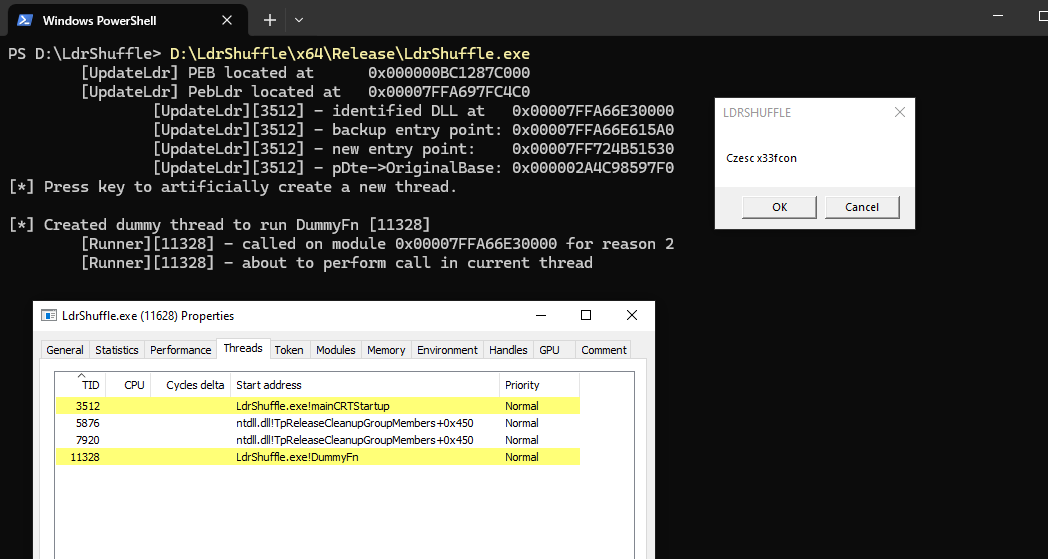 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 cwjchoi01/cve-2024-57394
Proof-of-concept exploit for CVE-2024-57394: low-privilege file restoration to System32 enabling DLL hijacking and local privilege escalation to…