
ransomwhere
 hazcod/ransomwhere
A PoC ransomware sample to test out your ransomware response strategy.
adversarial-attackencryption-decryption-toolsincident-response+3
220
hazcod/ransomwhereA PoC ransomware sample to test out your ransomware response strategy.

 toxy4ny/bl00dym4ry
Educational trojan simulator for cybersecurity training, simulating phishing attacks with social engineering, system reconnaissance, anti-sandbox…
 xm0kht4r/ven0m-ransomware
Fully undetectable and evasive ransomware written in Rust, leveraging a BYOVD technique to disable AV/EDR solutions on the infected systems.
 vortexcry-organization/vortexcry-ransomware-release
Advanced ransomware using process injection and kernel driver loading via CVE-2019-16098 to encrypt files, disable recovery, and demand ransom. For…
 afanpan/cve-2025-29824-exploit
Use after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.
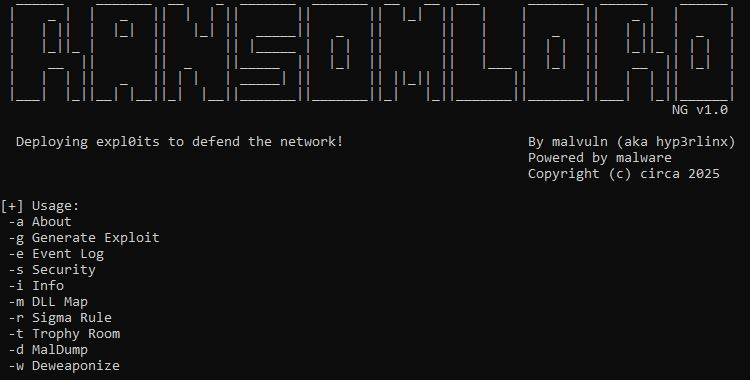 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
 zorvithonleo/exploit-cve-2014-4210-
Exploit for CVE-2014-4210 targeting WebLogic deserialization, with post-exploitation features including ransomware deployment, C2 integration, and…
 ahmetramazank/cve-2024-4577
Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…
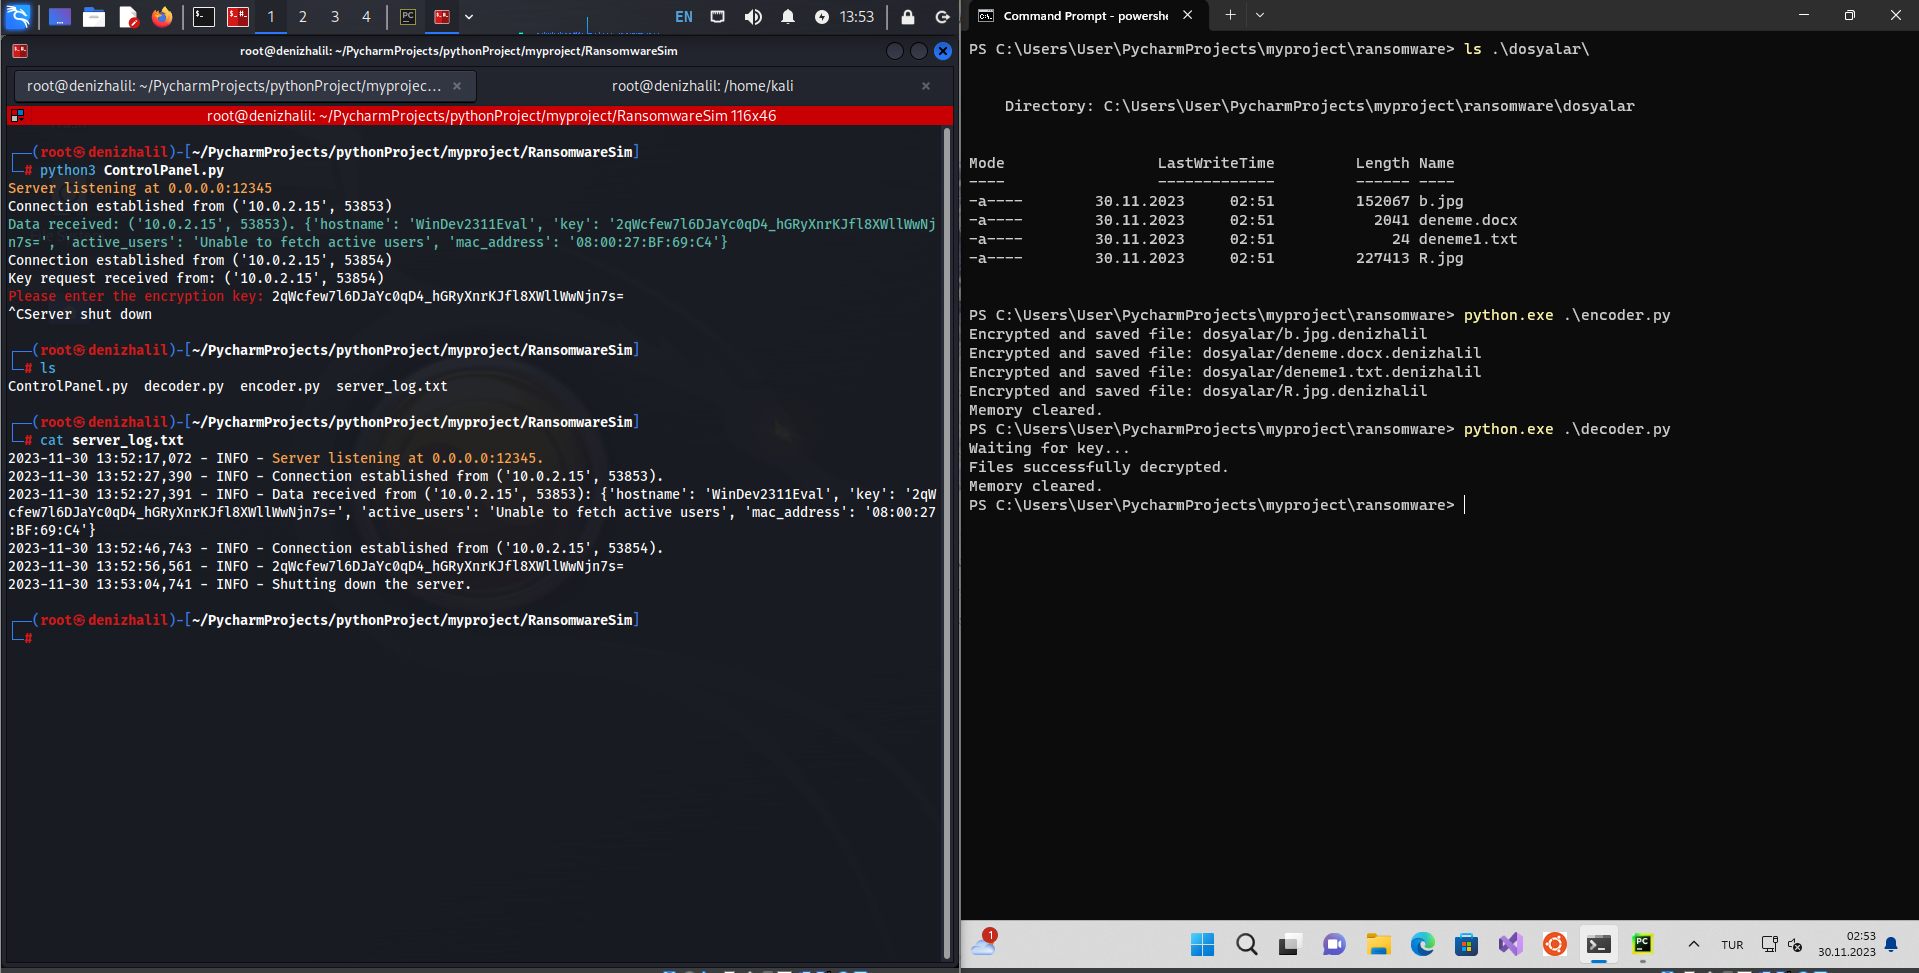 halildeniz/ransomwaresim
Educational ransomware simulator demonstrating file encryption, C2 communication, and decryption for cybersecurity training and malware analysis.
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
 whichbuffer/lockbit-black-3.0
Ransomware source code artifact for analyzing encryption routines, payload mechanics, and building detection and incident-response countermeasures.
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
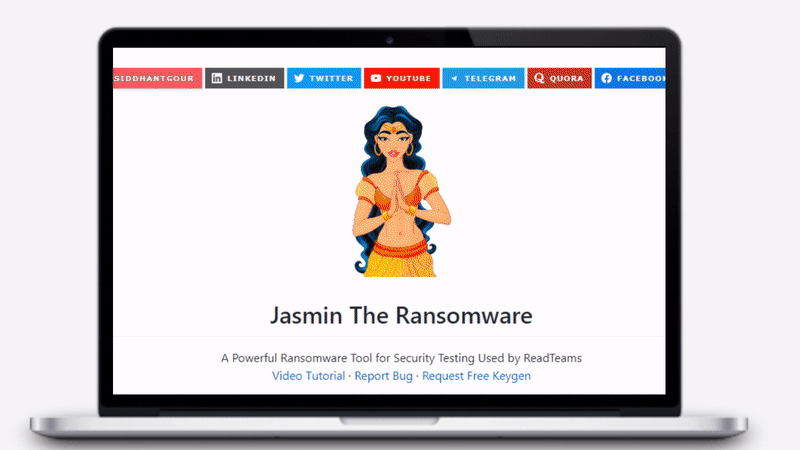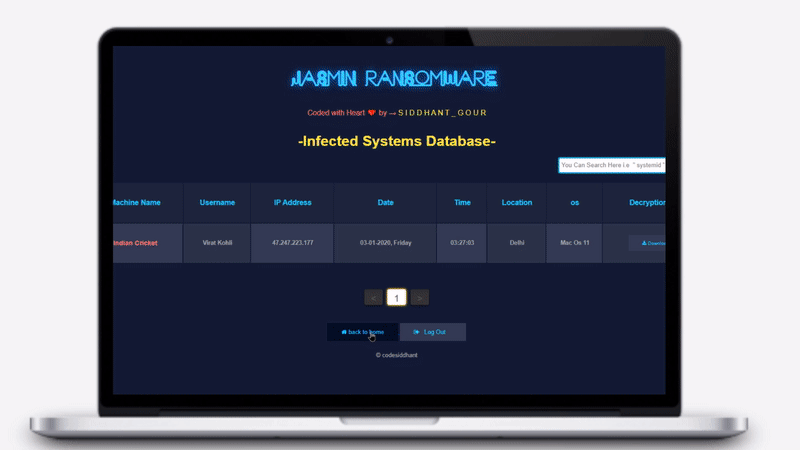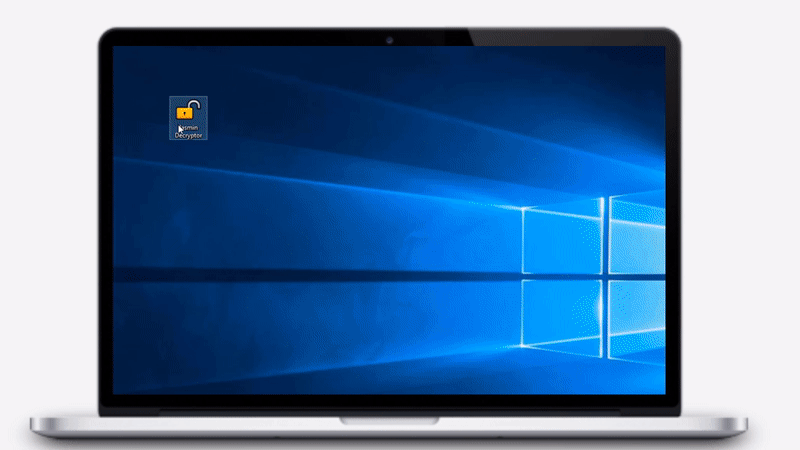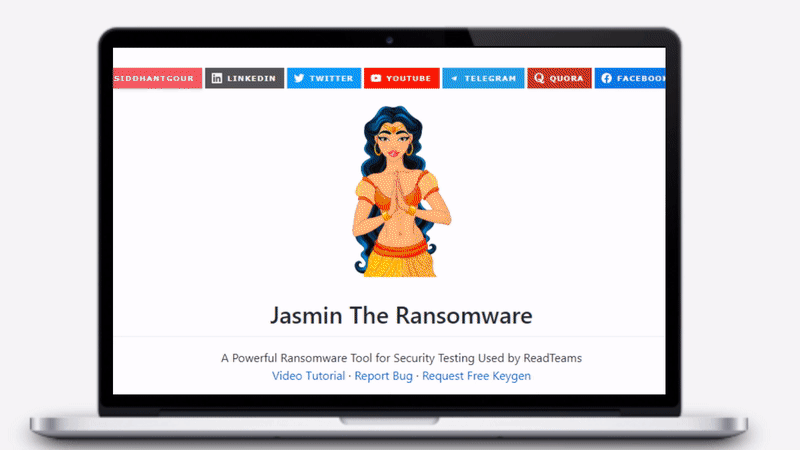 codesiddhant/jasmin-ransomware
Jasmin Ransomware is an advanced red team tool (WannaCry Clone) used for simulating real ransomware attacks. Jasmin helps security researchers to…
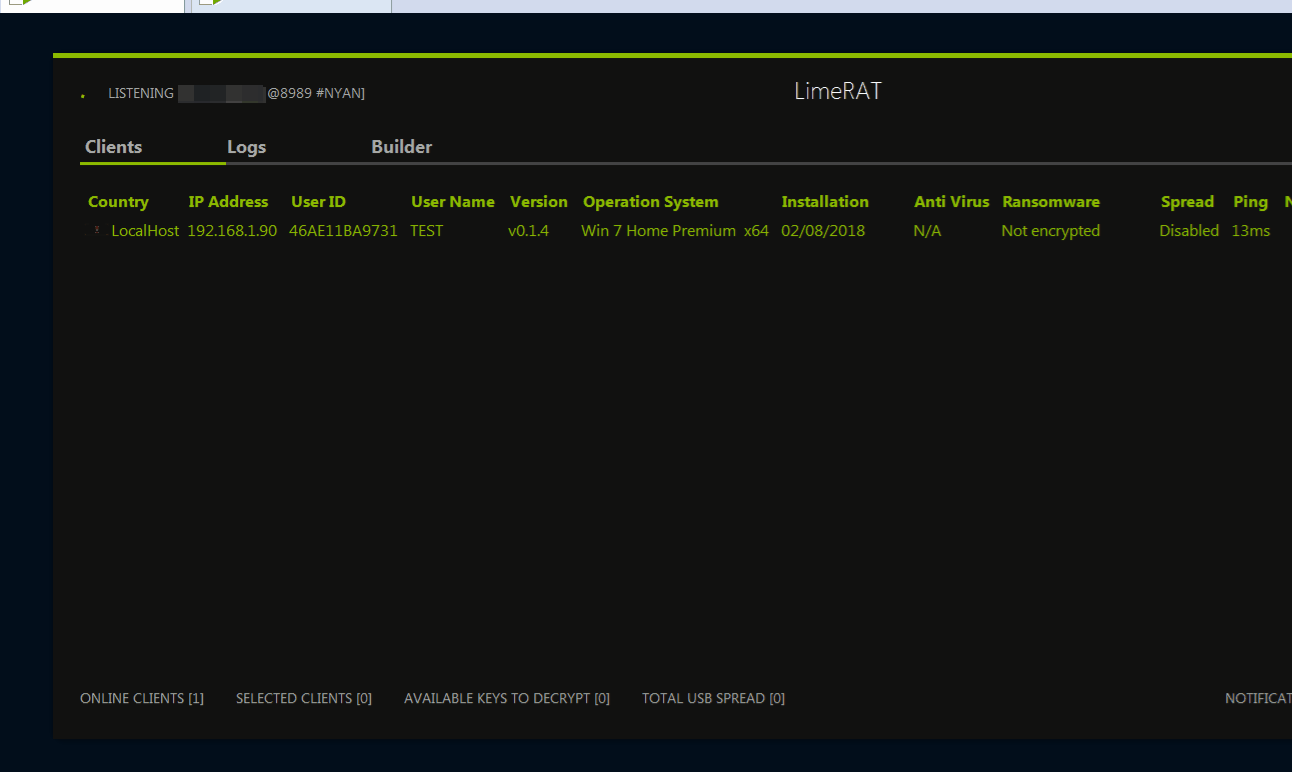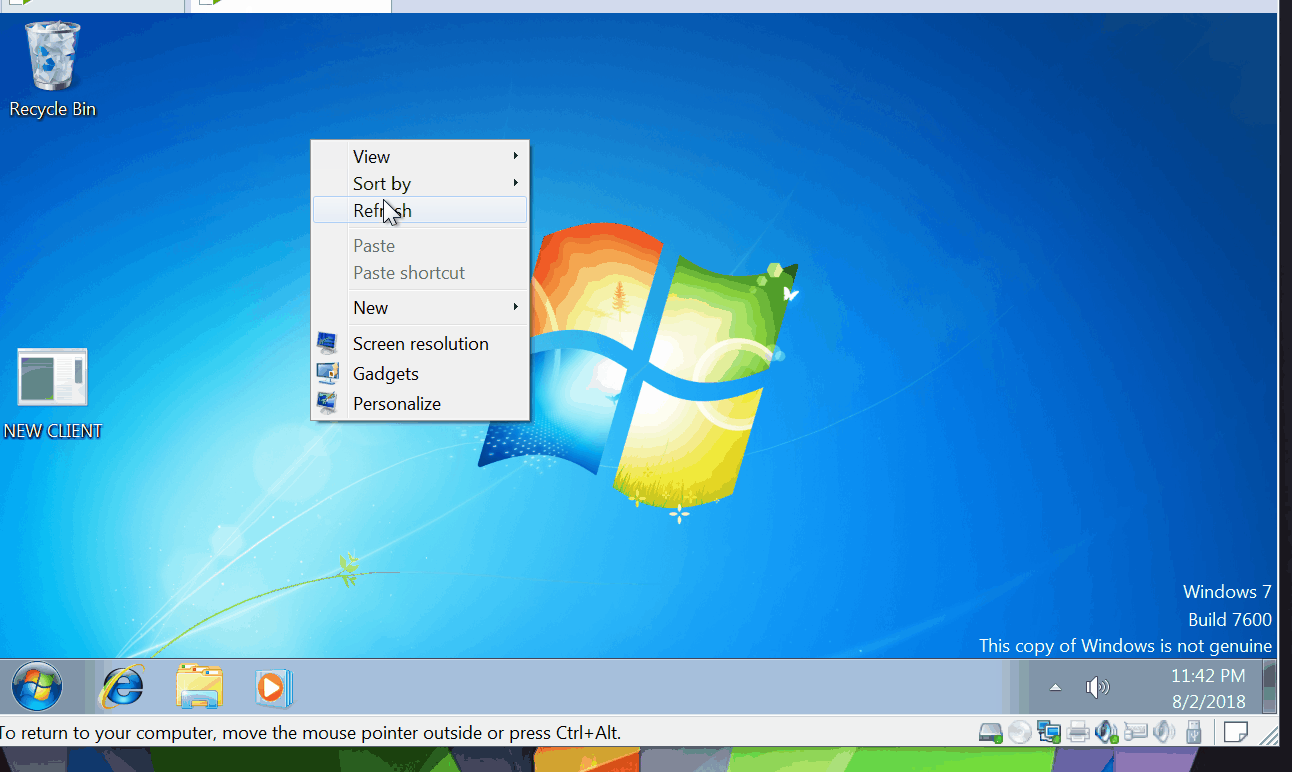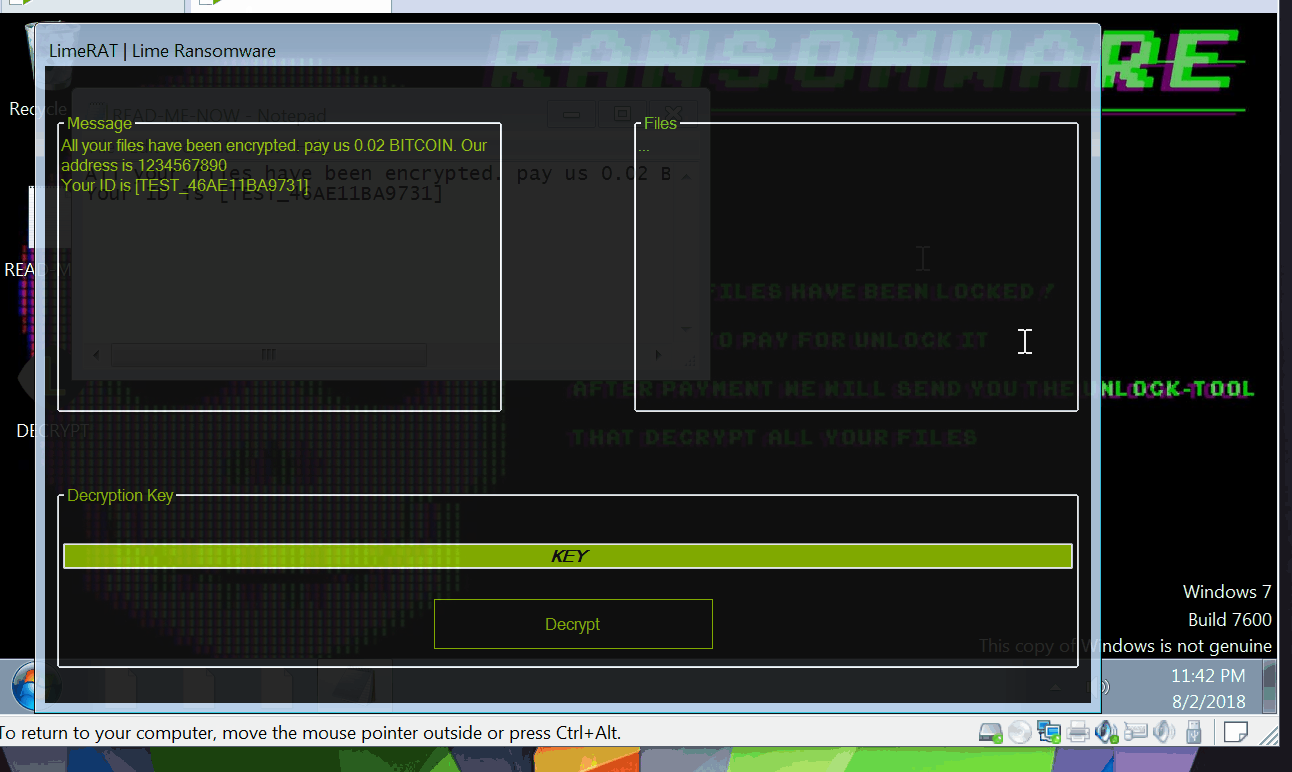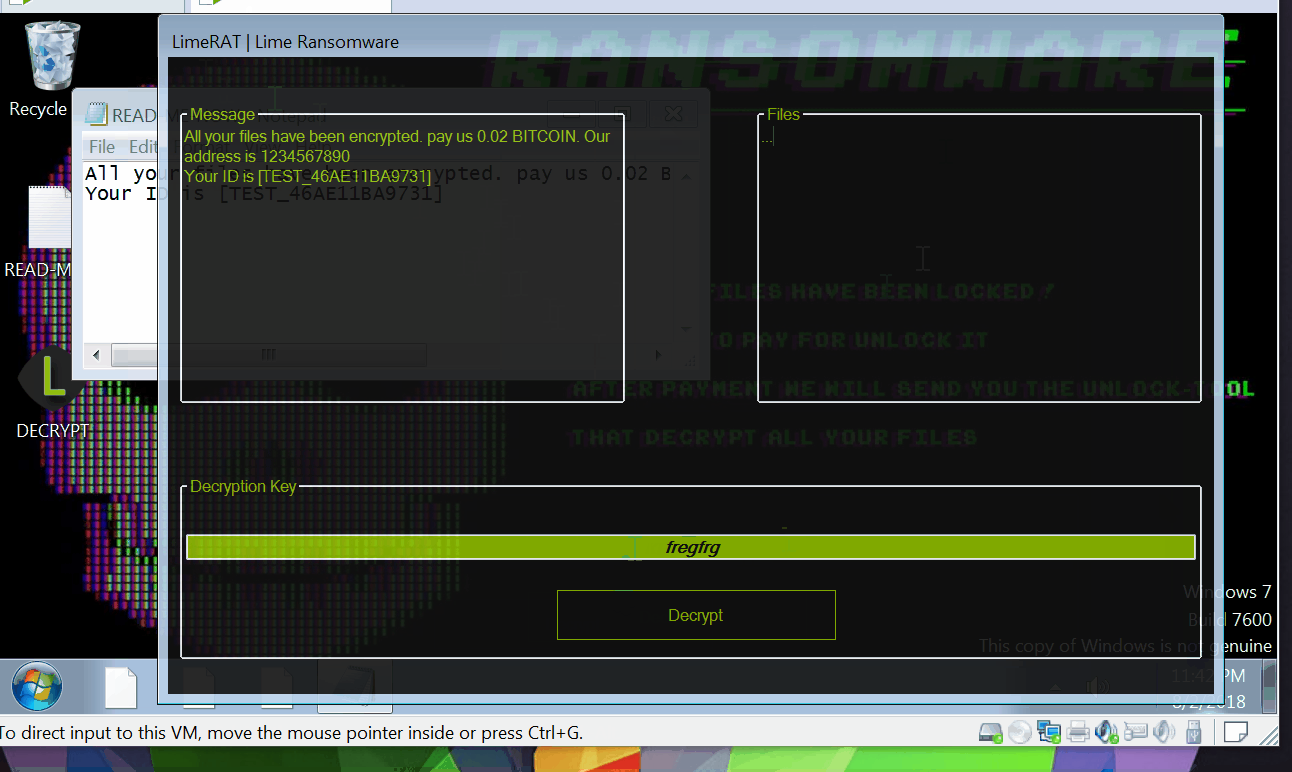 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
 guibacellar/nxransomware
A next generation of ransomware. Fully written using a .Net Framework + C&C System