
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/halildeniz/ransomwaresim
Encryption/Decryption ToolsMalware AnalysisPenetration TestingCommand and ControlLearning & EducationPayload Development
GitHubhalildeniz/ransomwaresim

RansomwareSim

Educational ransomware simulator demonstrating file encryption, C2 communication, and decryption for cybersecurity training and malware analysis.

View Repository
17640542 years agoReviewed by Kitploit
Share
Website

RansomwareSim

Overview

RansomwareSim is a simulated ransomware application developed for educational and training purposes. It is designed to demonstrate how ransomware encrypts files on a system and communicates with a command-and-control server. This tool is strictly for educational use and should not be used for malicious purposes.

Buy Me A Coffee

Features

  • Encrypts specified file types within a target directory.
  • Changes the desktop wallpaper (Windows only).
  • Creates&Delete a README file on the desktop with a simulated ransom note.
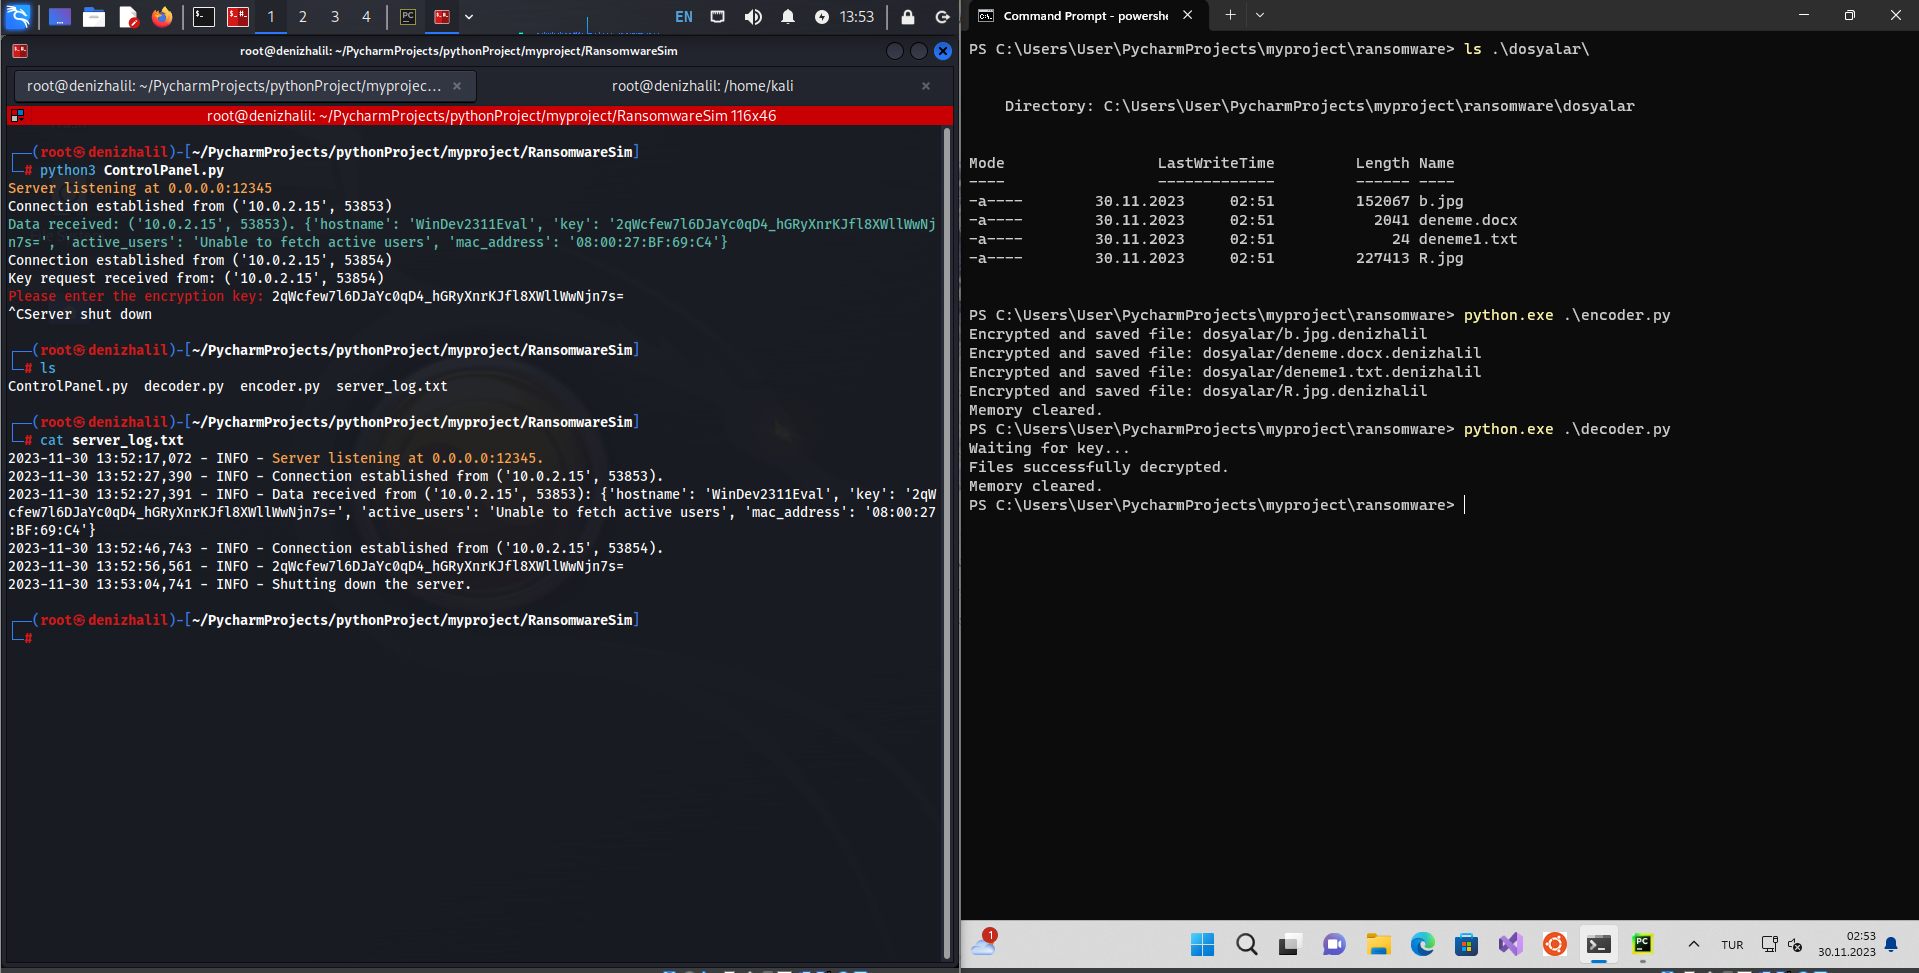
  • Simulates communication with a command-and-control server to send system data and receive a decryption key.
  • Decrypts files after receiving the correct key.

Usage

Important: This tool should only be used in controlled environments where all participants have given consent. Do not use this tool on any system without explicit permission. For more, read SECURE

Requirements

  • Python 3.x
  • cryptography
  • colorama

Installation

  1. Clone the repository:

    git clone https://github.com/HalilDeniz/RansomwareSim.git
    
  2. Navigate to the project directory:

    cd RansomwareSim
    
  3. Install the required dependencies:

    pip install -r requirements.txt
    

📖 My Book

  • Mastering Scapy: A Comprehensive Guide to Network Analysis
  • Python Learning Roadmap in 30 Days: here
  • Beginning Your Journey in Programming and Cybersecurity - Navigating the Digital Future

DepNot: BackDoorSim

If you are interested in tools like RansomwareSim, be sure to check out my recently released BackDoorSim tool

Running the Control Server

  1. Open controlpanel.py.
  2. Start the server by running controlpanel.py.
  3. The server will listen for connections from RansomwareSim and the Decoder.

Running the Simulator

  1. Navigate to the directory containing RansomwareSim.
  2. Modify the main function in encoder.py to specify the target directory and other parameters.
  3. Run encoder.py to start the encryption process.
  4. Follow the instructions displayed on the console.

Running the Decoder

  1. Run decoder.py after the files have been encrypted.
  2. Follow the prompts to input the decryption key.

Disclaimer

RansomwareSim is developed for educational purposes only. The creators of RansomwareSim are not responsible for any misuse of this tool. This tool should not be used in any unauthorized or illegal manner. Always ensure ethical and legal use of this tool.

Contributing

Contributions, suggestions, and feedback are welcome. Please create an issue or pull request for any contributions.

  1. Fork the repository.
  2. Create a new branch for your feature or bug fix.
  3. Make your changes and commit them.
  4. Push your changes to your forked repository.
  5. Open a pull request in the main repository.

Contact

For any inquiries or further information, you can reach me through the following channels:

  • LinkedIn : Halil Ibrahim Deniz
  • TryHackMe: Halilovic
  • Instagram: deniz.halil333
  • YouTube : Halil Deniz
  • Email : [email protected]

💰 You can help me by Donating

Thank you for considering supporting me! Your support enables me to dedicate more time and effort to creating useful tools like RansomwareSim and developing new projects. By contributing, you're not only helping me improve existing tools but also inspiring new ideas and innovations. Your support plays a vital role in the growth of this project and future endeavors. Together, let's continue building and learning. Thank you!"
BuyMeACoffee Patreon

License

RansomwareSim is released under the MIT License. See LICENSE for more information.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    891
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    547
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    369
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    309
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    282

Explore all tools

Browse our collection of tools

View all tools →






