

begal-c2
 xsanflip/begal-c2
Flask and Socket.IO command-and-control panel with a rogue browser extension agent that harvests credentials, exfiltrates files via Telegram, and…
command-and-controldata-exfiltrationeducation+6
8
xsanflip/begal-c2Flask and Socket.IO command-and-control panel with a rogue browser extension agent that harvests credentials, exfiltrates files via Telegram, and…
 gmh5225/definitelynotphishing
Contains evilginx phislets, gophish templates, burp suite extensions etc.
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 toxy4ny/bl00dym4ry
Educational trojan simulator for cybersecurity training, simulating phishing attacks with social engineering, system reconnaissance, anti-sandbox…
 rosesecurity/anti-virus-evading-payloads
During the exploitation phase of a pen test or ethical hacking engagement, you will ultimately need to try to cause code to run on target system…
 nuky-alt/cve-2025-8088
Proof-of-concept exploit and technical analysis for a WinRAR path traversal vulnerability enabling code execution via crafted archives with binary…
 shndnth/cve-2022-30190
Educational Proof-of-Concept for the CVE-2022-30190 (Follina) vulnerability.
 mrk336/cve-2021-3456
A practical chain that starts with an innocuous PDF file and ends up in a reverse shell on an AWS EC2 instance
 mexeck88/csrf-via-stored-xss-for-privesc
Chamilo-LMS (v2.0) CVE-2025-26153
 lewis-ricardo/amaranth-project
CVE-2025-8088 exploitation chain + Quasar C2 multi-stage payload delivery
 martinastarone/cve-2026-2441
Detailed proof-of-concept and technical analysis for CVE-2026-2441, a Chrome CSS use-after-free vulnerability enabling sandboxed renderer RCE via…
 d0rb/cve-2024-21378
This repository contains an exploit for targeting Microsoft Outlook through Exchange Online, leveraging a vulnerability to execute arbitrary code via…
 ahmetkarakayaoffical/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Bu betik, Microsoft Outlook'ta keşfedilen ve CVSS değeri 9.8 olan önemli bir güvenlik açığı olan CVE-2024-21413 için bir kavram kanıtı (PoC)…
 vr00mm/cve-2025-49144
PoC CVE-2025-49144
 thestingr/cve-2025-68613-poc
Public PoC + Scanner and research for CVE-2025-68613: Critical RCE in n8n Workflow Automation via Expression Injection (CVSS 10.0). Includes…
 simonschoeni/cve-2020-7247-poc
Proof of concept for CVE-2020-7247 for educational purposes.
 s3cur3th1ssh1t/offensivevba
This repo covers some code execution and AV Evasion methods for Macros in Office documents
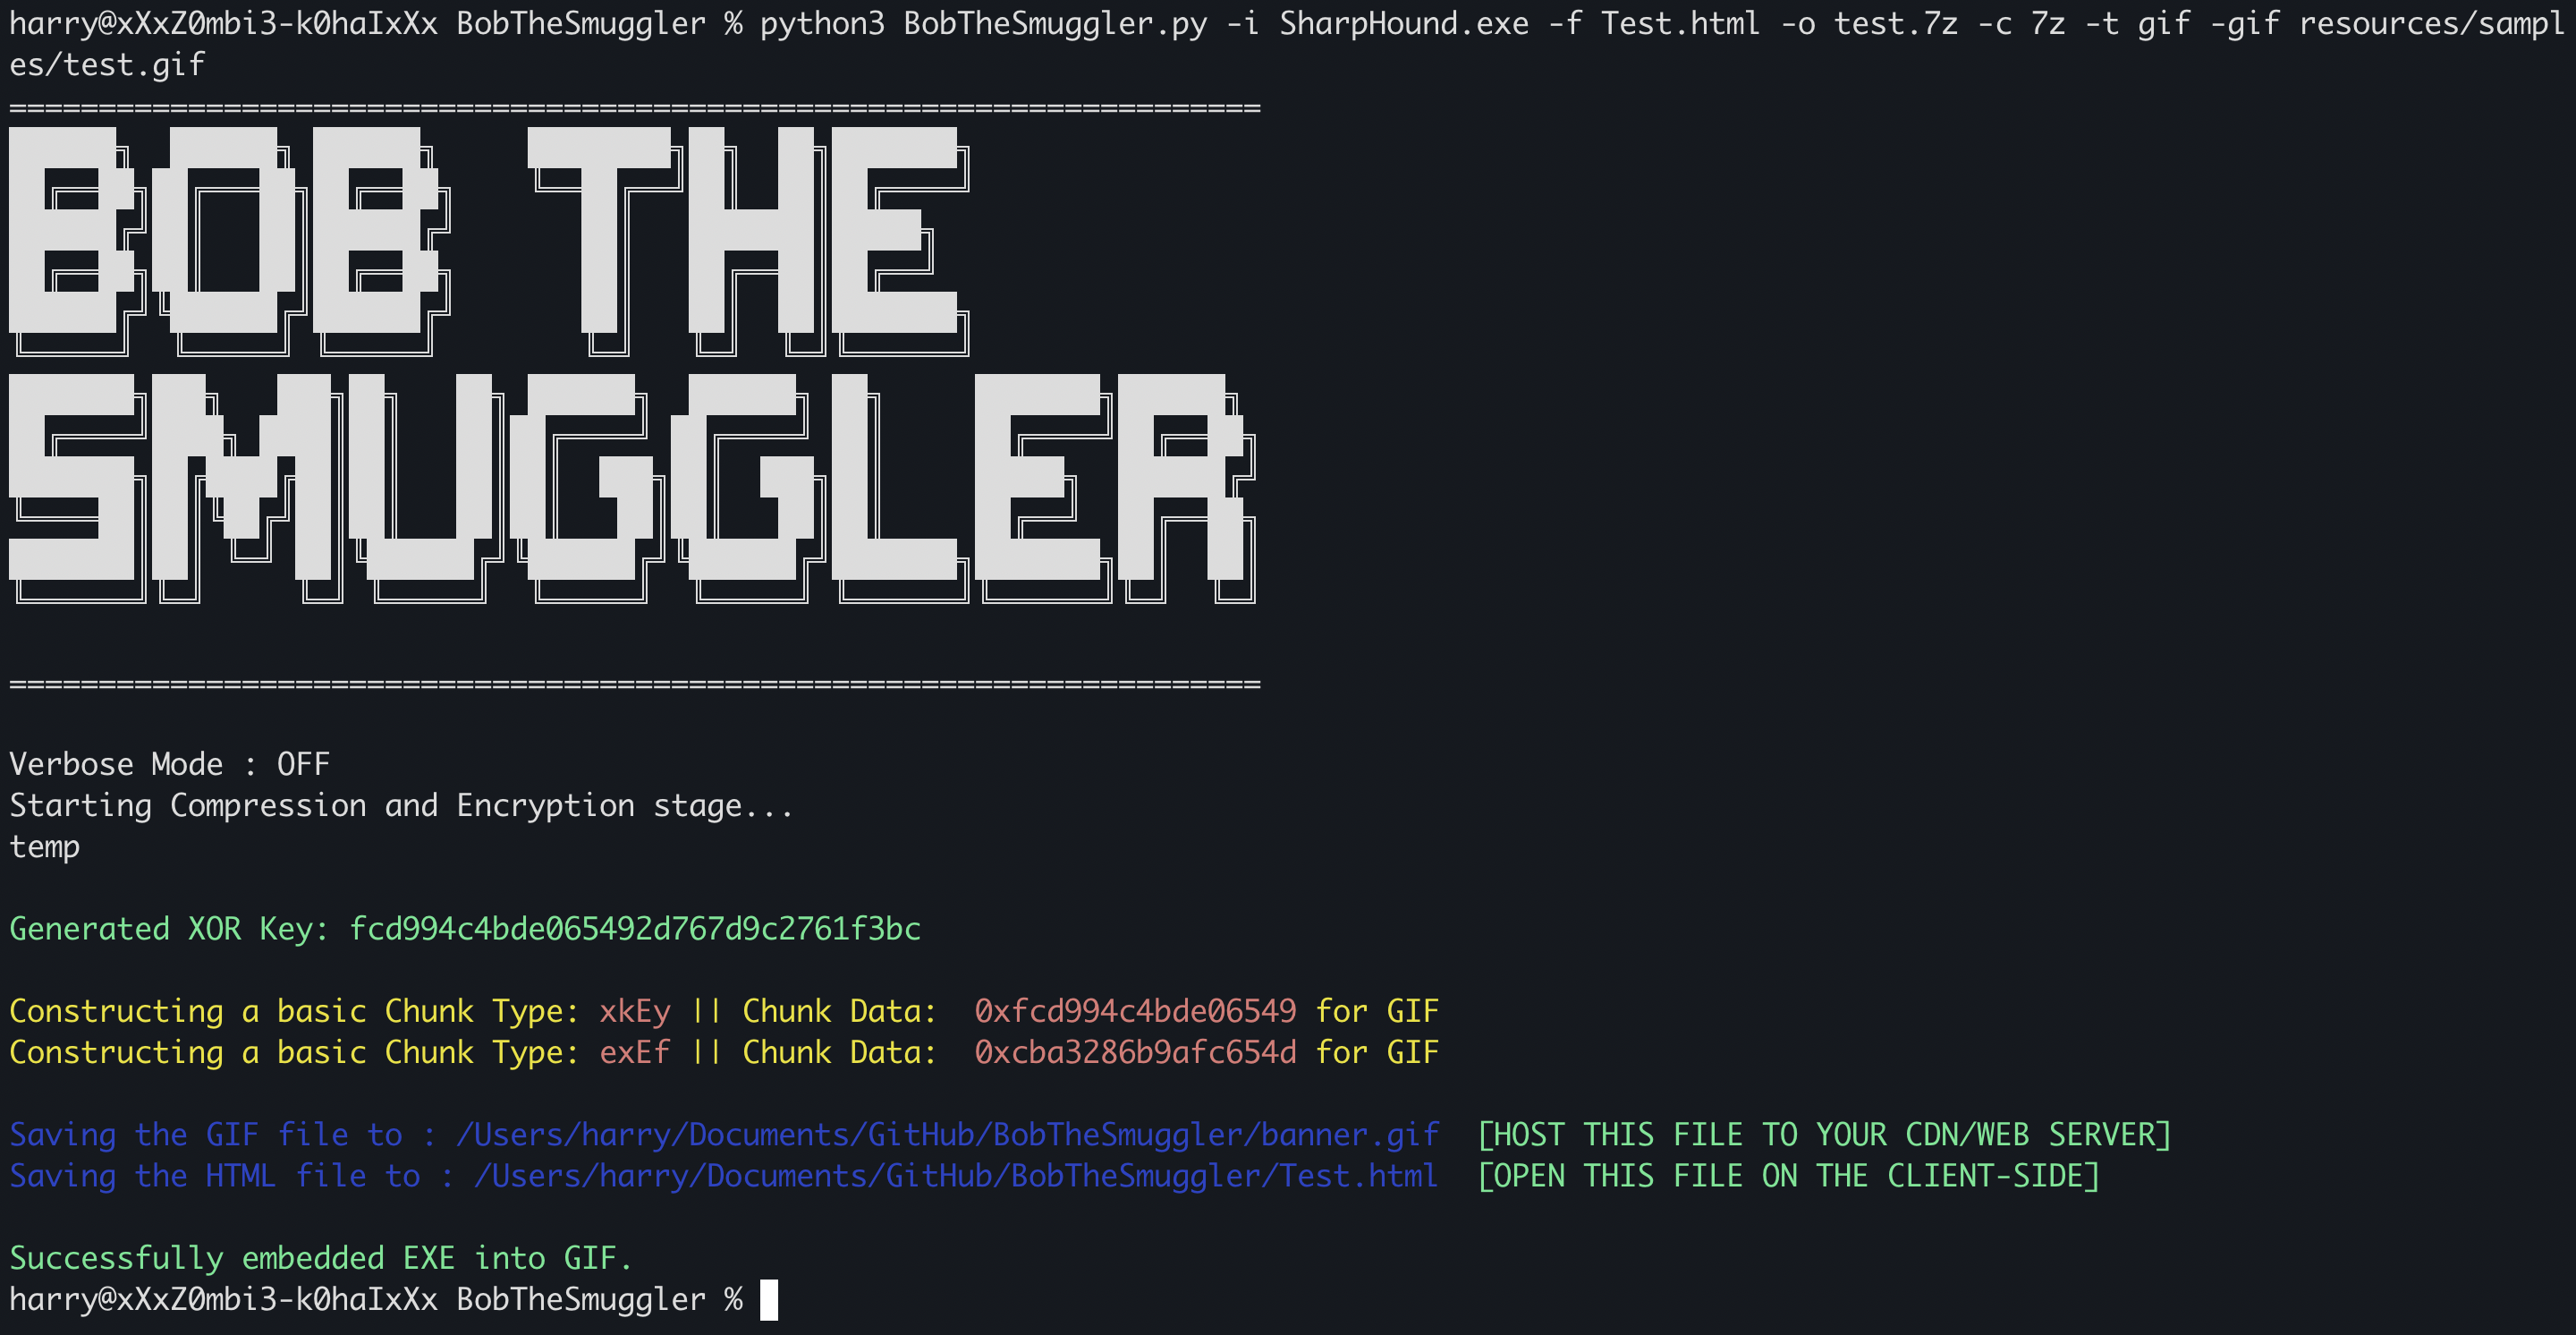 thecyb3ralpha/bobthesmuggler
"Bob the Smuggler": A tool that leverages HTML Smuggling Attack and allows you to create HTML files with embedded 7z/zip archives. The tool would…