
DeepSleep
 theflink/deepsleep
A variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC
exploitationmemory-forensicspayload-development+1
3754 years ago
theflink/deepsleepA variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC
 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 asepsaepdin/cve-2010-1240
Educational proof-of-concept demonstrating how to embed a Meterpreter backdoor into a PDF file exploiting CVE-2010-1240, with step-by-step Metasploit…
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
 openpixelsystems/c-copy-fail
C-based exploit for CVE-2026-31431 in the Linux Kernel Crypto API, targeting aarch64 and amd64 architectures with shellcode generation and ancillary…
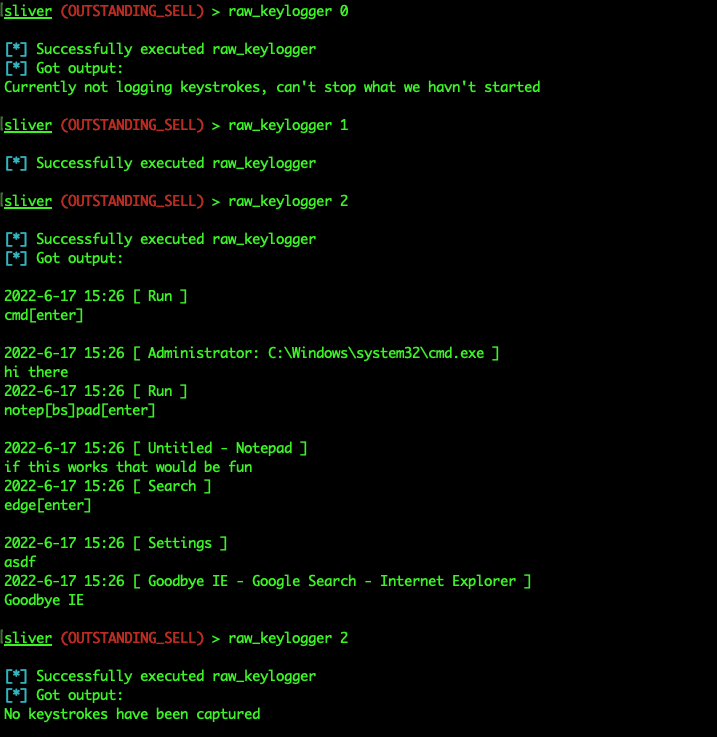 trustedsec/sliverkeylogger
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…
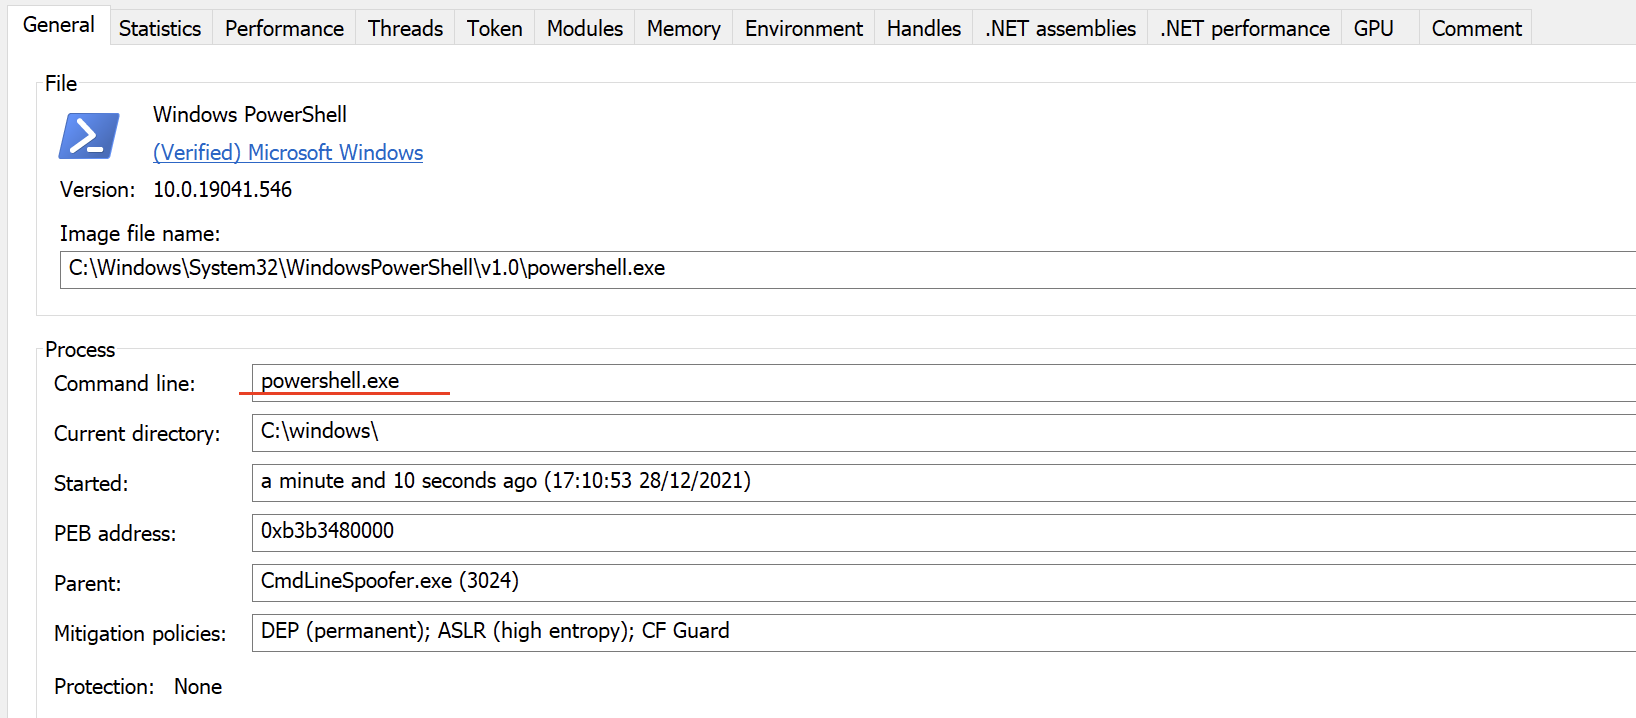 plackyhacker/cmdlinespoofer
How to spoof the command line when spawning a new process from C#.
 ally-petitt/cve-2024-48990-exploit
My exploit for CVE-2024-48990. Full details of how I made this are on my blog.
 nova-master/cve-2022-21894-payload-new
C-based payload for CVE-2022-21894 that maps a second stage payload to call EFI services, extending the original PoC for Secure Boot bypass…
 rizemon/exploit-writing-for-oswe
Tips on how to write exploit scripts (faster!)
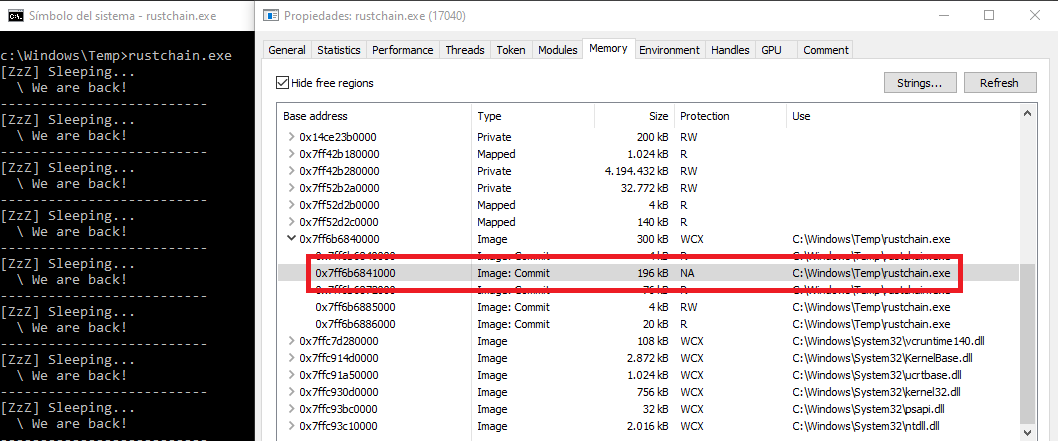 kudaes/rustchain
Hide memory artifacts using ROP and hardware breakpoints.
 xpn/blockchainc2
A POC C2 server and agent to explore just if/how the Ethereum blockchain can be used for C2
 laskdjlaskdj12/cve-2024-35106-poc
Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…
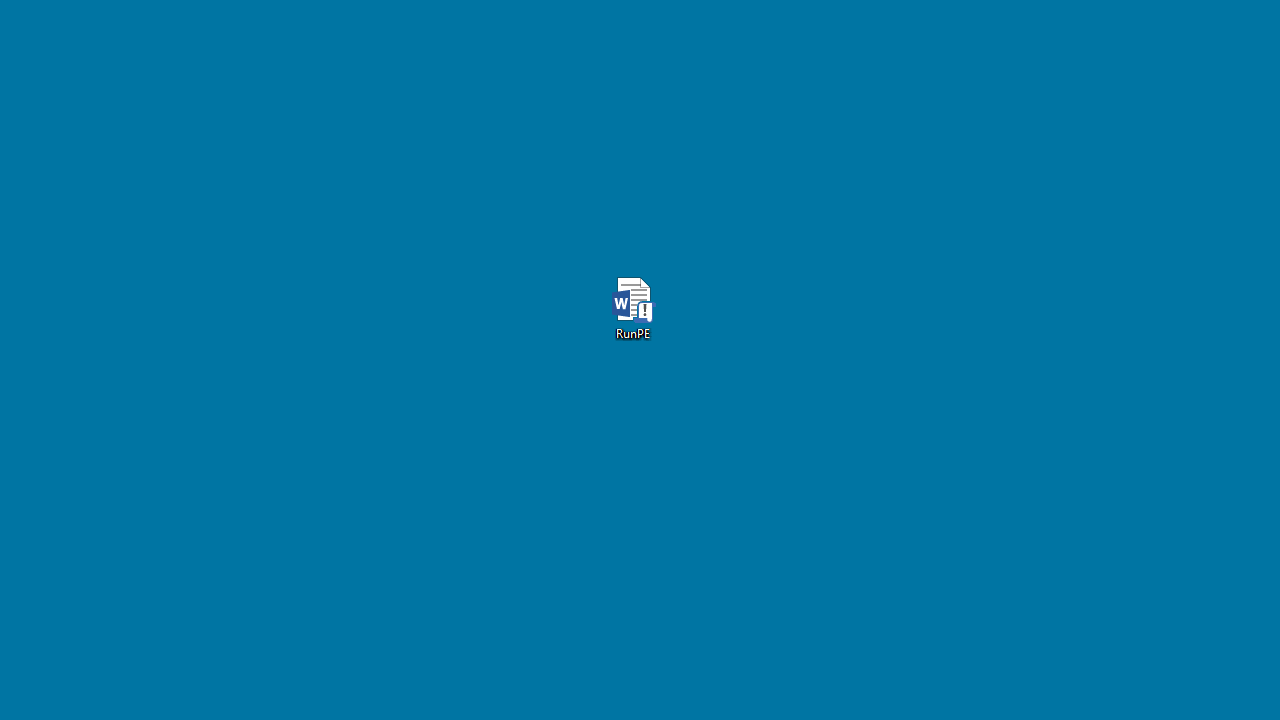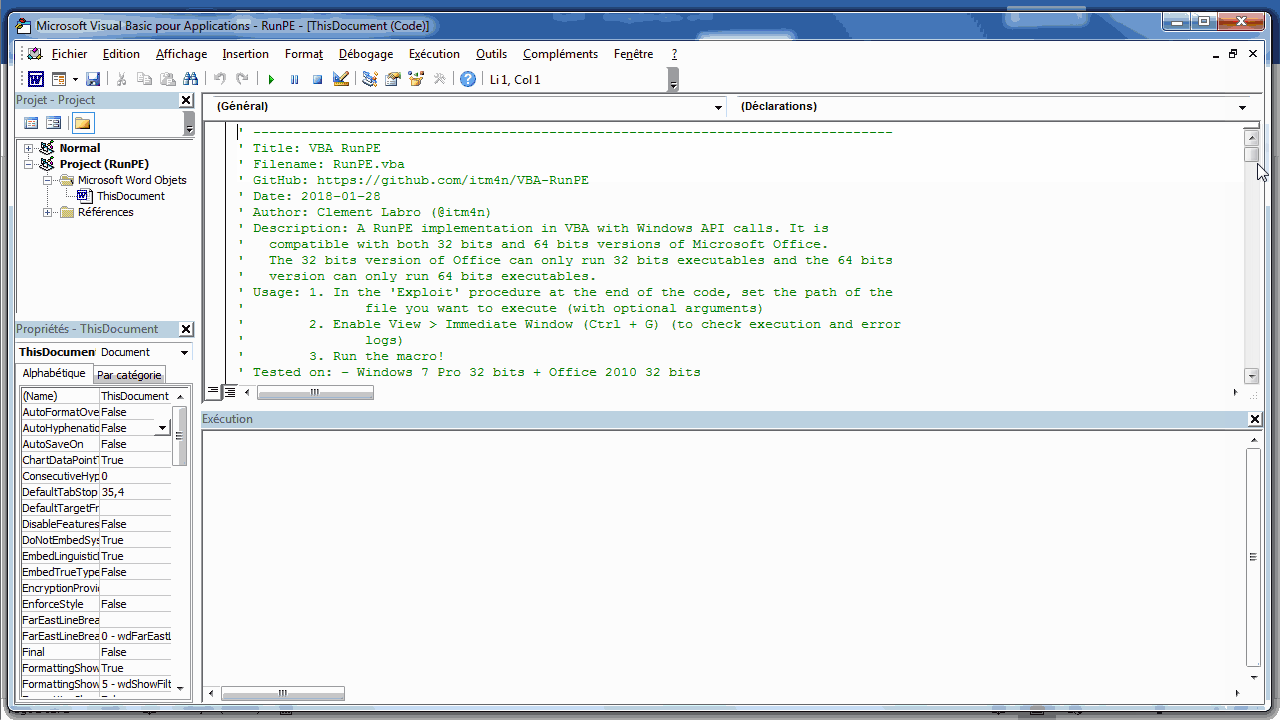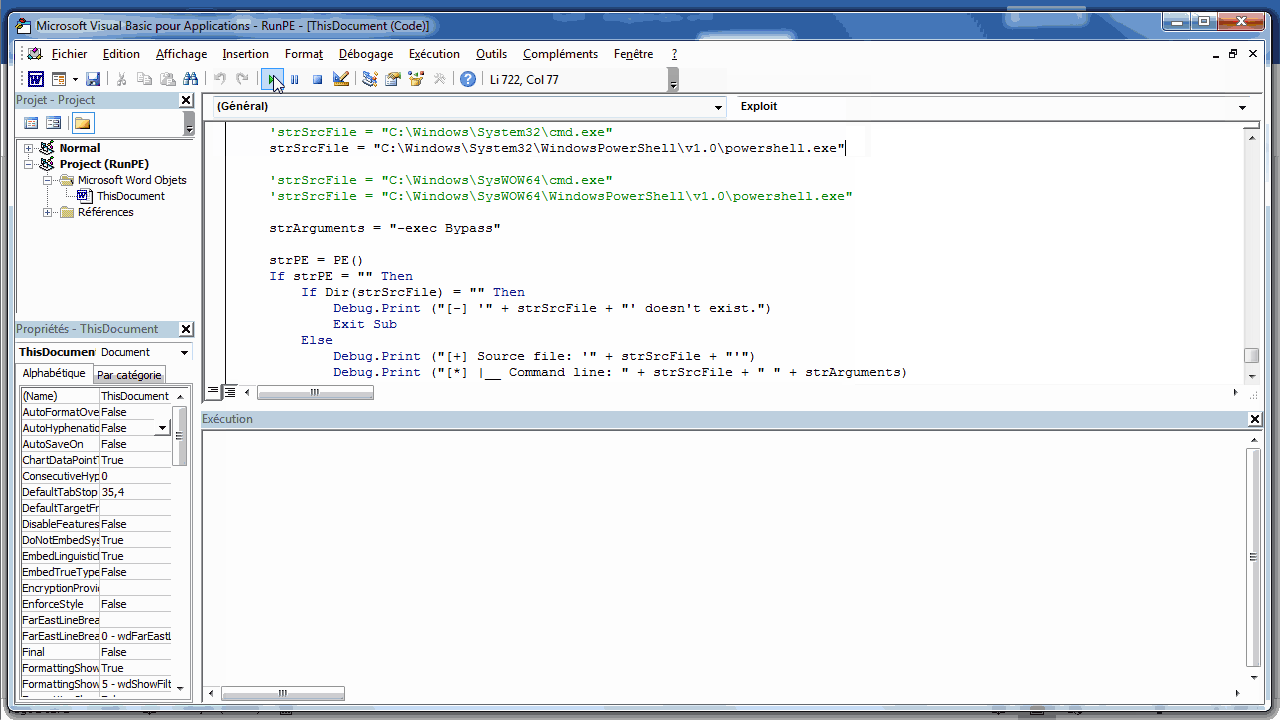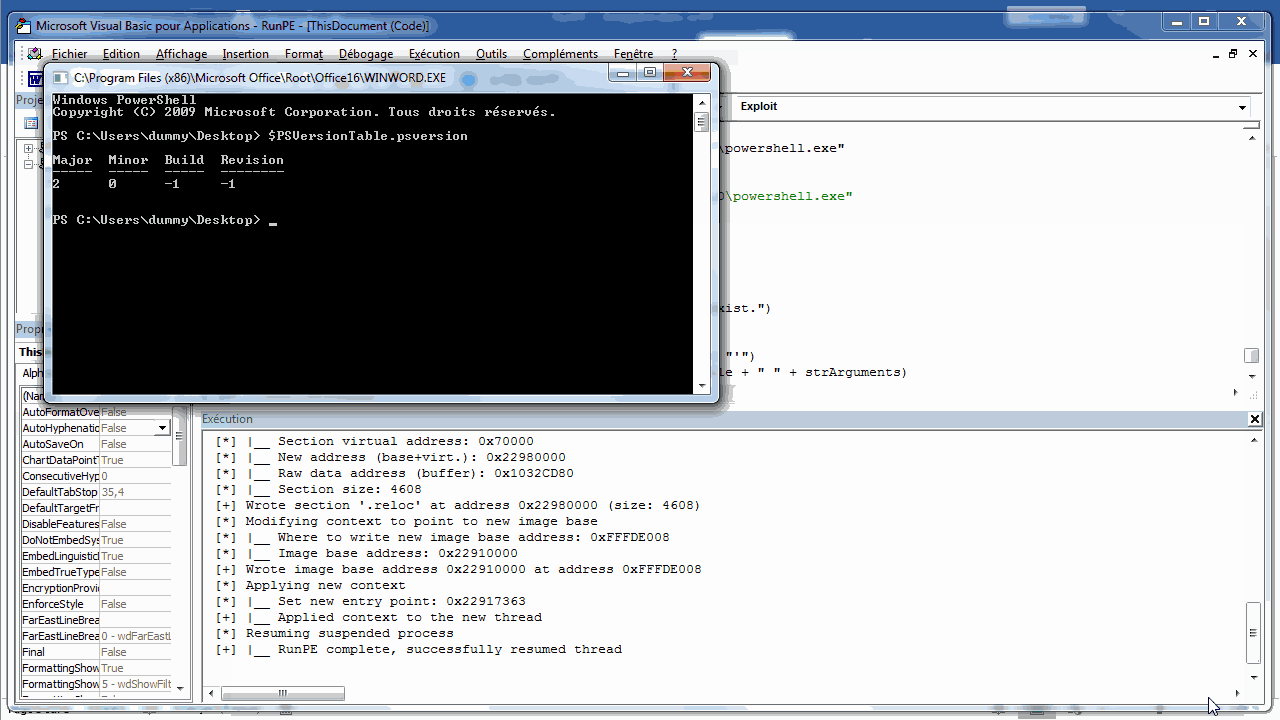 itm4n/vba-runpe
A VBA implementation of the RunPE technique or how to bypass application whitelisting.
 geek-repo/c2-blockchain
This is a concept poc of command and control server implemented over blockchain
 ahmadf77/cve-2026-23744
Python exploit script for CVE-2026-23744 that delivers a reverse shell to a specified target URL, requiring a netcat listener for command-and-control.
 dinosn/cve-2026-25243
CVE-2026-25243 — Redis RESTORE zipmap double-free → remote code execution (ASLR on).