
CVE-2024-43451-POC
 ronf98/cve-2024-43451-poc
CVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.
exploitationmalware-analysispassword-cracking+3
15
ronf98/cve-2024-43451-pocCVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.
 nathanlopez/stitch
Python Remote Administration Tool (RAT)
 jimywork/cromos
Cromos is a tool for downloading legitimate extensions of the Chrome Web Store and inject codes in the background of the application.
 peewpw/invoke-wcmdump
PowerShell Script to Dump Windows Credentials from the Credential Manager
 desireeontrial76/yellowkey-bitlocker
Manage and recover BitLocker encrypted drives with this tool for Windows 11 recovery key management and educational study of CVE-2026-45585.
 gentilkiwi/mimikatz
A little tool to play with Windows security
 synacktiv/cachedata_decrypt
A simple Toolkit to BF and decrypt Windows EntraId CacheData
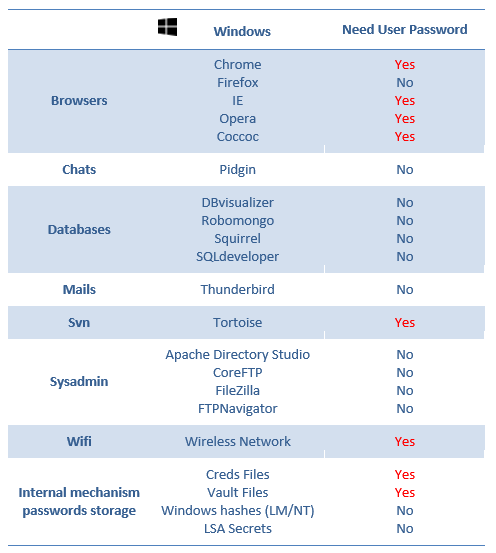 alessandroz/lazagneforensic
Windows passwords decryption from dump files
 rubbxalc/cve-2025-24071
Generates a ZIP file exploiting CVE-2025-24071 to capture netNTLMv2 credentials from Windows Explorer via malicious .library-ms files, intended for…
 jfjallid/go-secdump
Tool to remotely dump secrets from the Windows registry
 qax-a-team/mscache
a tool to manipulate dcc(domain cached credentials) in windows registry, based mainly on the work of mimikatz and impacket
 abdelrahman0sayed/cve-2025-24071
This is a python PoC scripts for CVE-2025-24071 which is a vulnerability in Windows File Explorer that allows unauthorized access to sensitive…
 c3rrberu5/zerologon-to-shell
Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.
 joelgmsec/autordpwn
The Shadow Attack Framework
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
 chryzsh/darthsidious
Building an Active Directory domain and hacking it
 looky243/cve-2025-24071-poc
CVE-2025-24071 Proof Of Concept
 grepstrength/cve-2026-92680
Proof-of-concept decrypting Araxis Merge's DPAPI-protected server credentials (CVE-2026-92680), demonstrating insufficiently protected credential…