

nishang
 samratashok/nishang
Nishang - Offensive PowerShell for red team, penetration testing and offensive security.
command-and-controldata-exfiltrationexploitation+9
10.1k3 years ago
samratashok/nishangNishang - Offensive PowerShell for red team, penetration testing and offensive security.
 magicbytes/magicarch
MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 ayham-megdadi/zero-day-legacy
A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…
 d1se0/cve-2024-21413-vulnerabilidad-outlook-lab
Educational lab demonstrating CVE-2024-21413 Outlook vulnerability exploitation with Python email exploit tool and Responder for NTLM credential…
 nu11secur1ty/complete-google-dorks
Curated collection of Google dork queries for advanced search engine reconnaissance, uncovering exposed databases, configuration files, admin panels,…
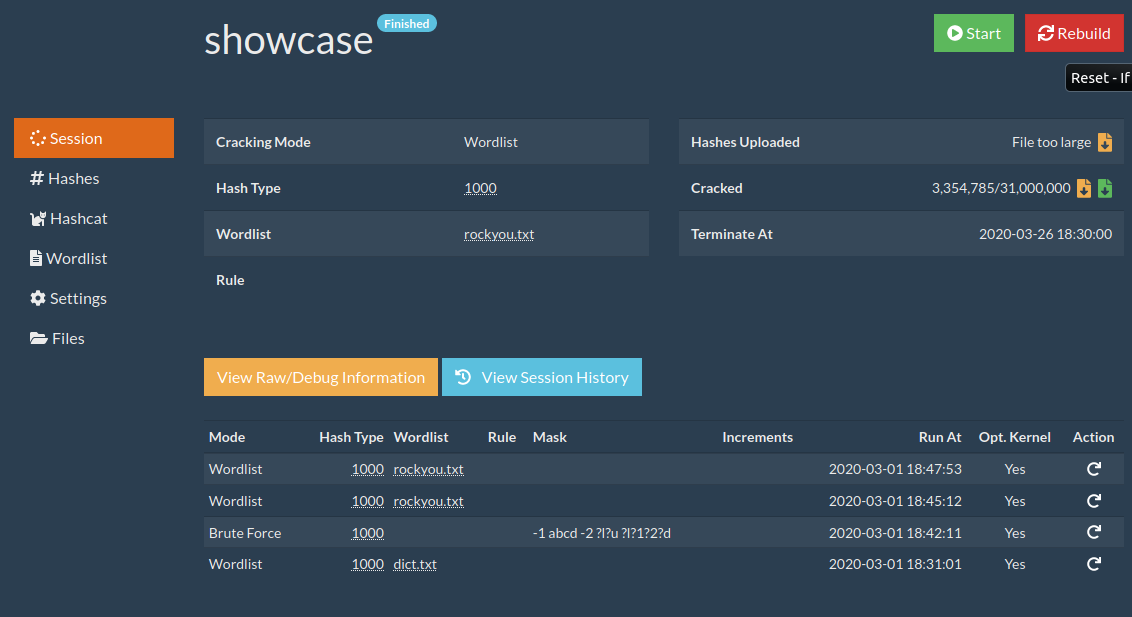 ctxis/crackerjack
CrackerJack / Hashcat Web Interface / Context Information Security
 krishnakanthb13/password_generator
A production-ready, cryptographically secure password generator CLI with 17 generation modes, entropy transparency, and comprehensive customization…
 fevra-dev/claimjumper
Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…
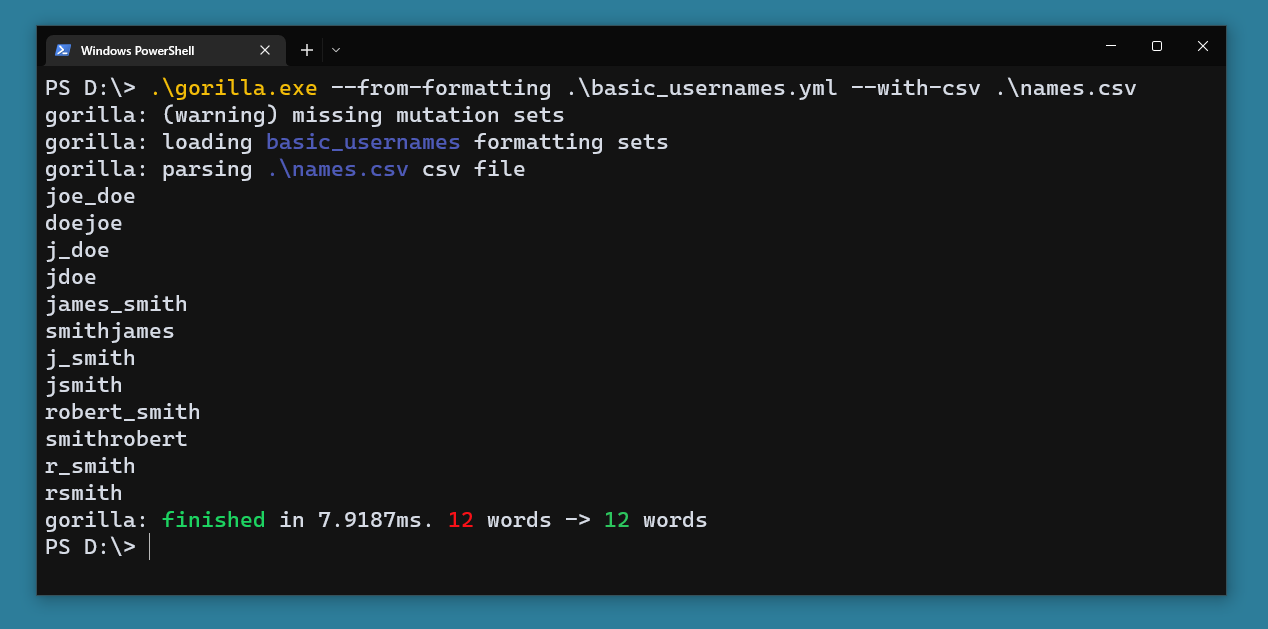 andreiverse/gorilla
tool for generating wordlists or extending an existing one using mutations.
 dariusztytko/words-scraper
Selenium based web scraper to generate passwords list
 al0ne/vxscan
python3写的综合扫描工具,主要用来存活验证,敏感文件探测(目录扫描/js泄露接口/html注释泄露),WAF/CDN识别,端口扫描,指纹/服务识别,操作系统识别,POC扫描,SQL注入,绕过CDN,查询旁站等功能,主要用来甲方自测或乙方授权测试,请勿用来搞破坏。
 rndinfosecguy/scavenger
Crawler (Bot) searching for credential leaks on paste sites.
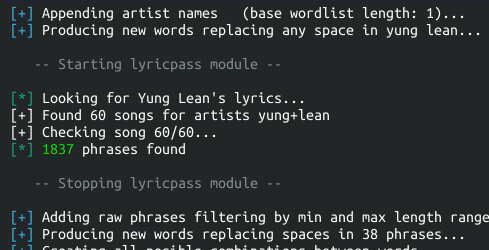 r3nt0n/bopscrk
Generates targeted password wordlists by combining personal info, applying case/leet transforms, and scraping artist lyrics for enhanced cracking…
 nox-project/nox-framework
High-performance OSINT/CTI framework for automated identity pivoting and risk analysis across 120+ sources.
 s0md3v/sqlmate
A friend of SQLmap which will do what you always expected from SQLmap.
 hashview/hashview
A web front-end for password cracking and analytics
 nitinronge91/extracting-user-credentials-for-web-portal-and-wifi-ap-for-hathway-router-cve-2024-44815-
CVE-2024-44815