
ZeroCrumb
 internetangel/zerocrumb
Dumping App Bound Protected Credentials & Cookies Without Privileges.
command-and-controldata-exfiltrationexploitation+6
1691 year ago
internetangel/zerocrumbDumping App Bound Protected Credentials & Cookies Without Privileges.
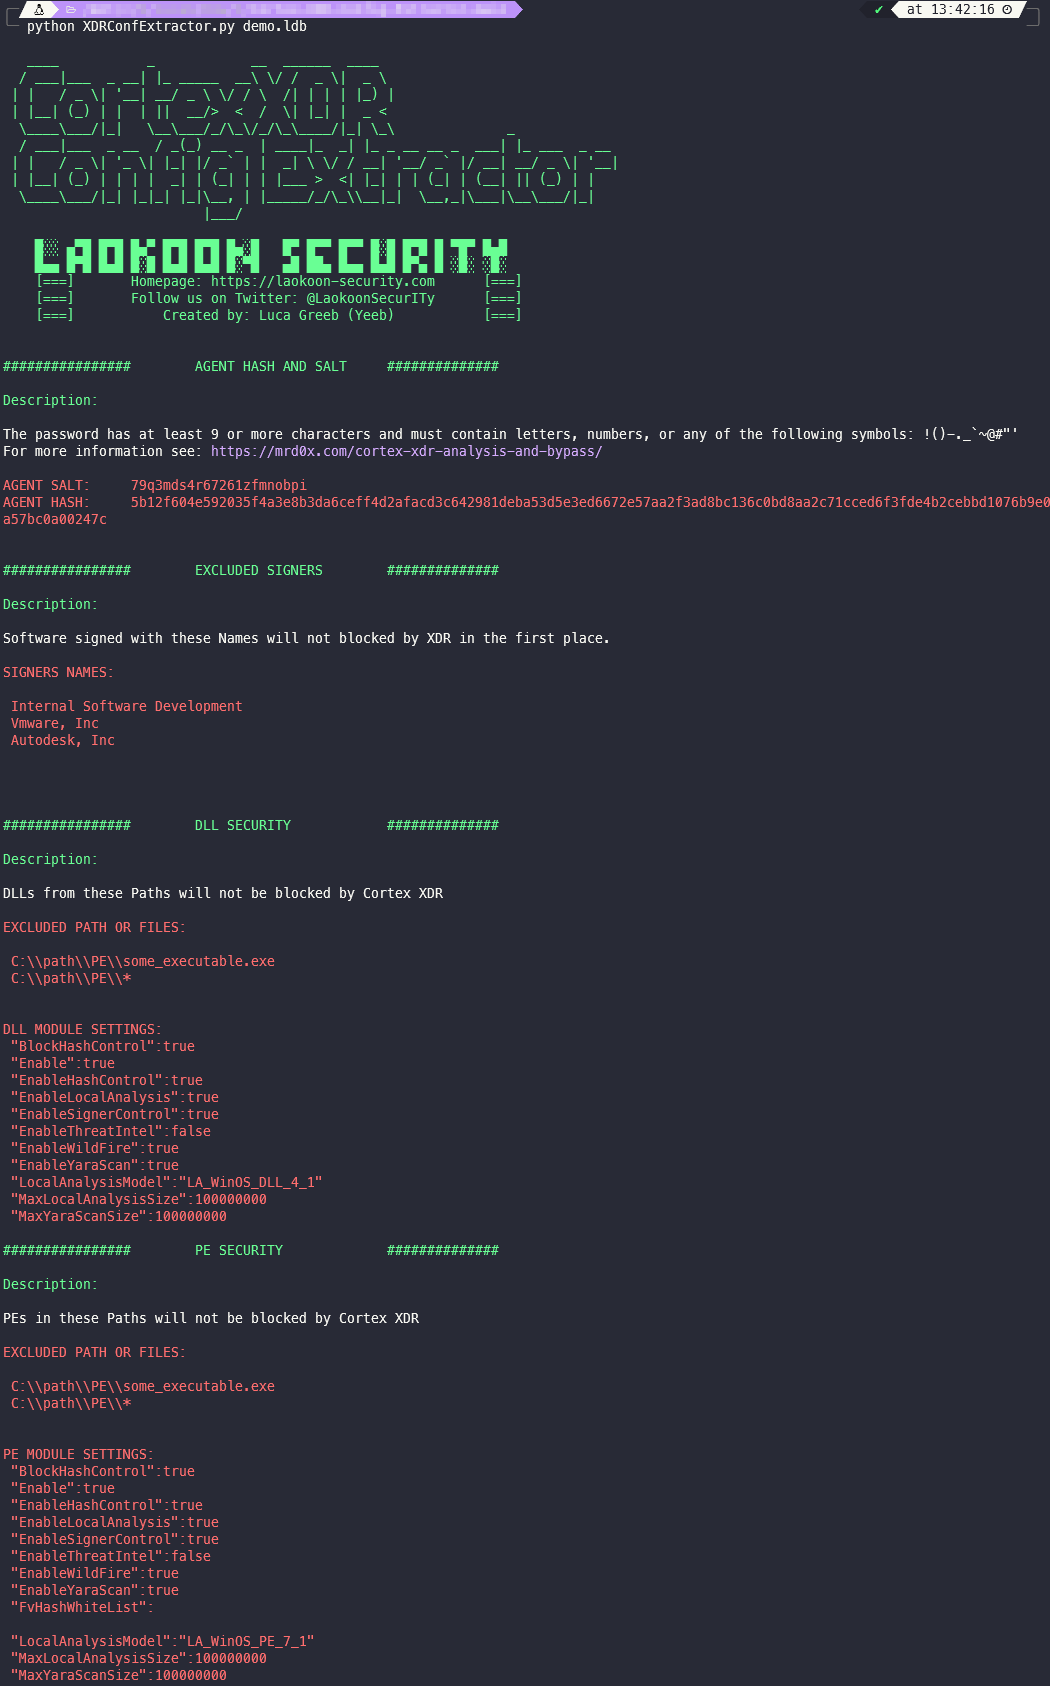 laokoon-security/cortex-xdr-config-extractor
Parses Cortex XDR agent database lock files to extract agent settings, uninstall password hash/salt, and security exclusions for red team assessments…
 ronf98/cve-2024-43451-poc
CVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.
 danyw24/zyxel-p870hn-hardware-hacking
From a bare PCB to root: hardware-hacking a ZyXEL P-870HN (BCM6368) over UART — CVE-2025-0890 + CVE-2024-40891, on my own hardware.
 petergabaldon/cve-2024-1346
Weak MySQL database root password in LaborOfficeFree affects version 19.10. This vulnerability allows an attacker to calculate the root password of…
 magicbytes/magicarch
MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
 ishaklaz/hash-eye
**HashEye** is a powerful Python CLI tool for instantly detecting and analyzing hash types. It provides detailed information about hash formats,…
 robertguetzkow/ets5-password-recovery
ETS5 Password Recovery Tool is a PoC for CVE-2021-36799
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
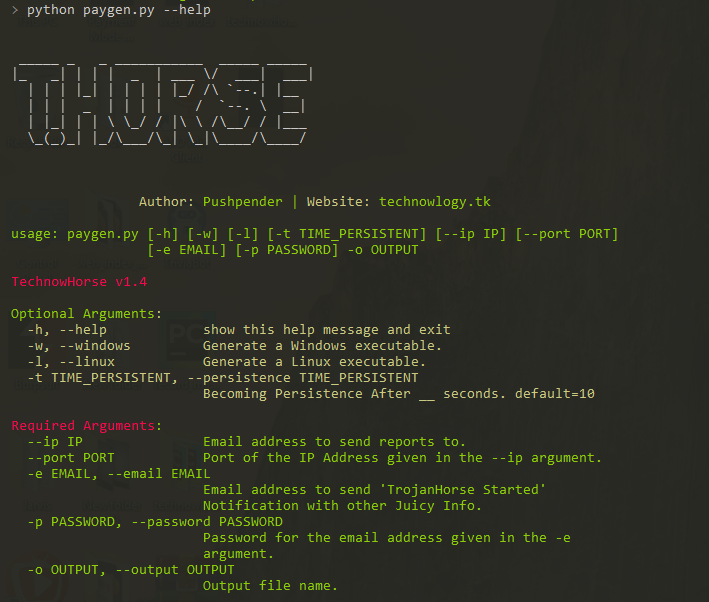 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 them4hd1/vayne-rat
An Advanced C# .NET Rat, It’s Stable and Contains Many Features.
 sofianehamlaoui/pentest-bookmarkz
A collection of useful links for Pentesters
 areebashoaib42/keepass-cve-2023-32784-exploitation-and-defense
Exploitation and defense-in-depth mitigation strategies for the KeePass memory leakage vulnerability (CVE-2023-32784).
 dev0558/cve-2023-32784-exploit-report
Educational demonstration of CVE-2023-32784 KeePass master password recovery via memory dump analysis, with step-by-step exploit setup and mitigation…
 chryzsh/darthsidious
Building an Active Directory domain and hacking it
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 skelsec/pypykatz
Mimikatz implementation in pure Python
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks