

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
55 results
NetExec preview

NetExec

GitHubpennyw0rth/netexec

Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…

command-and-controldatabase-securityexploitation+14
5.9k
1 day ago
impacket preview

impacket

GitHubfortra/impacket

Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…

authenticationcommand-and-controldatabase-security+17
16.2k4 days ago
Kousei preview

Kousei

GitHubnu11secur1ty/kousei

Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…

exploitationpassword-crackingpayload-generation+6
35 days ago
CVE-2026-89012 preview

CVE-2026-89012

GitHubfaceless0x7/cve-2026-89012

Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…

api-securitydata-exfiltrationexploitation+6
624 days ago
Exploit-CVE-2023-6063-PoC-Vuln preview

Exploit-CVE-2023-6063-PoC-Vuln

GitHubzhairiazzeddine/exploit-cve-2023-6063-poc-vuln

Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…

exploitationpassword-crackingpenetration-testing+4
26 days ago
CVE-2025-68999-POC preview

CVE-2025-68999-POC

GitHubfolks-iwd/cve-2025-68999-poc

PoC exploit for CVE-2025-68999 - Second-Order SQL Injection in Happy Addons for Elementor <= 3.20.4
educationexploitationpassword-cracking+3
11 month ago
wp2shell preview

wp2shell

GitHubiqbalx7/wp2shell

unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)

api-securityexploitationpassword-cracking+4
2 months ago
wp2shell preview

wp2shell

GitHub0xsha/wp2shell

CVE-2026-63030 + CVE-2026-60137 - “wp2shell”: unauthenticated RCE in WordPress core
command-and-controleducationexploitation+7
1142 months ago
WP-Contest-Gallery-28.1.4-Exploit preview

WP-Contest-Gallery-28.1.4-Exploit

GitHubcerberusmrxi/wp-contest-gallery-28.1.4-exploit

Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
exploitationpassword-crackingpayload-development+4
12 months ago
CVE-2026-52614 preview

CVE-2026-52614

GitHubchinesespeople/cve-2026-52614

There is a SQL injection vulnerability in the backend of Ruoyi v4.8.3

exploitationpassword-crackingpenetration-testing+2
2 months ago
Zero-Day-Legacy preview

Zero-Day-Legacy

GitHubayham-megdadi/zero-day-legacy

A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…

ctfeducationlabs-practice+6
23 months ago
cve-2019-9053-py3 preview

cve-2019-9053-py3

GitHubvedantrana73/cve-2019-9053-py3

Unauthenticated time-based blind SQL injection exploit for CMS Made Simple ≤ 2.2.9 (CVE-2019-9053), ported to Python 3.

educationexploitationpassword-cracking+3
3 months ago
mysqli preview

mysqli

GitHubrgkue/mysqli

Time-Based Blind SQL Injection tool for MySQL - CVE-2019-9053
ctfeducationpassword-cracking+3
3 months ago
CVE-2026-36670 preview

CVE-2026-36670

GitHubgabriel-lacorte/cve-2026-36670

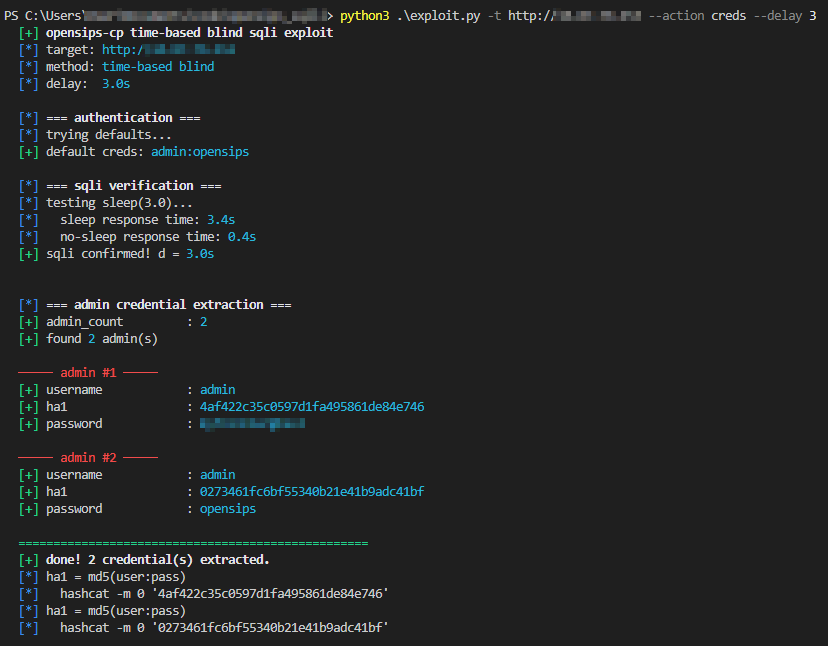
Time-Based Blind SQL Injection Exploit for the OpenSIPs Control Panel (or my first CVE!)
educationexploitationpassword-cracking+2
3 months ago
poc-CVE-2019-9053 preview

poc-CVE-2019-9053

GitHubrideckszz/poc-cve-2019-9053

PoC didático em Python 3 para a CVE-2019-9053, uma SQL Injection time-based blind no CMS Made Simple <= 2.2.9. Esta versão foi adaptada para uso em…
ctfeducationlabs-practice+3
13 months ago
CVE-2024-1698-NotificationX-WordPress-Plugin-SQL-Injection-to-Admin-Credential-Extraction preview

CVE-2024-1698-NotificationX-WordPress-Plugin-SQL-Injection-to-Admin-Credential-Extraction

GitHubdhananjayasj/cve-2024-1698-notificationx-wordpress-plugin-sql-injection-to-admin-credential-extraction

Unauthenticated time-based blind SQL injection exploit for NotificationX WordPress plugin (CVE-2024-1698) that extracts admin username and password…
exploitationinformation-gatheringpassword-cracking+3
4 months ago
CVE-2019-9053-exploit preview

CVE-2019-9053-exploit

GitHubjeanback1/cve-2019-9053-exploit

Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
exploitationinformation-gatheringpassword-cracking+3
4 months ago
Simple-CTF-Writeup preview

Simple-CTF-Writeup

GitHubimperialx1104/simple-ctf-writeup

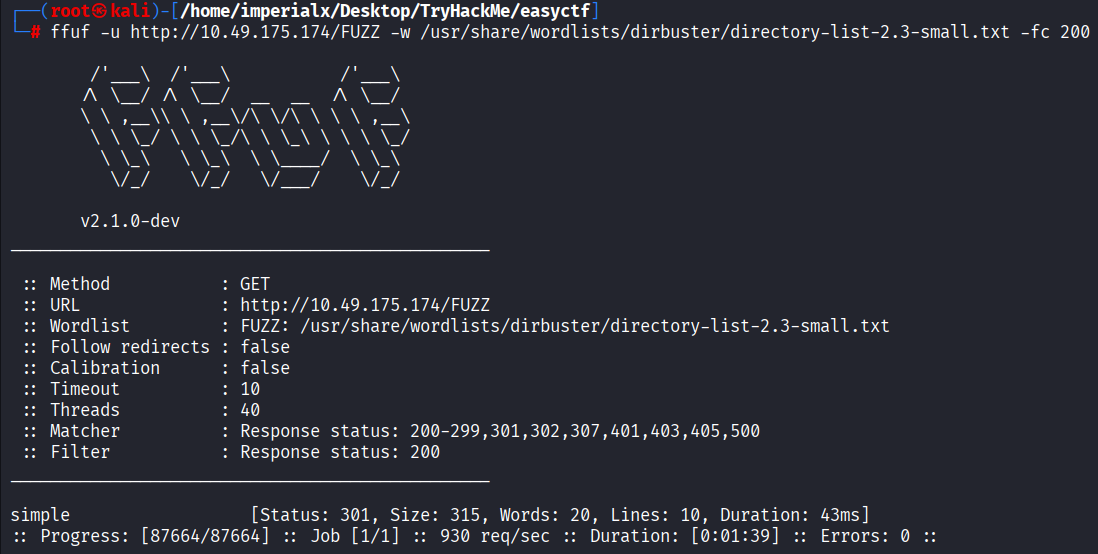
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…

ctfeducationexploitation+6
4 months ago
Previous1234Next