
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
30 results
Sudo-Agent-CTF- preview

Sudo-Agent-CTF-

GitHubnyxrecon/sudo-agent-ctf-

Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.
ctfeducationexploitation+7
2 months ago
poc-CVE-2019-9053 preview

poc-CVE-2019-9053

GitHubrideckszz/poc-cve-2019-9053

PoC didático em Python 3 para a CVE-2019-9053, uma SQL Injection time-based blind no CMS Made Simple <= 2.2.9. Esta versão foi adaptada para uso em…
ctfeducationlabs-practice+3
14 months ago
KeePass-CVE-2023-32784-Exploitation-and-Defense preview

KeePass-CVE-2023-32784-Exploitation-and-Defense

GitHubareebashoaib42/keepass-cve-2023-32784-exploitation-and-defense

Exploitation and defense-in-depth mitigation strategies for the KeePass memory leakage vulnerability (CVE-2023-32784).
configuration-auditingdefensive-toolseducation+5
4 months ago
CVE-2019-9053-exploit preview

CVE-2019-9053-exploit

GitHubjeanback1/cve-2019-9053-exploit

Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
exploitationinformation-gatheringpassword-cracking+3
4 months ago
Simple-CTF-Writeup preview

Simple-CTF-Writeup

GitHubimperialx1104/simple-ctf-writeup

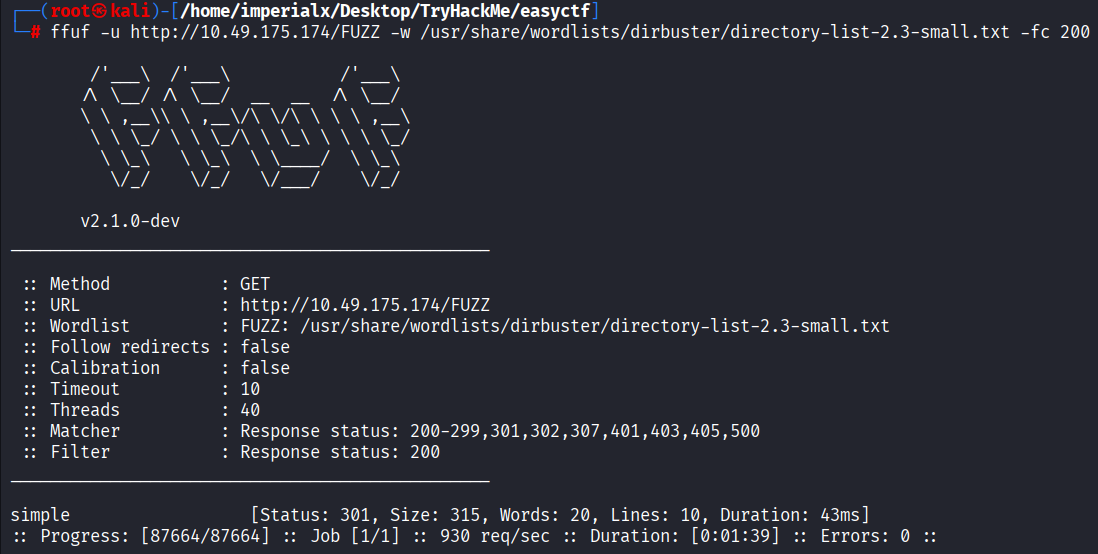
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…
ctfeducationexploitation+6
4 months ago
CVE-2018-14847 preview

CVE-2018-14847

GitHubthemalwareguardian/cve-2018-14847

Analysis and PoC for CVE-2018-14847, MikroTik RouterOS Winbox information disclosure vulnerability allowing unauthenticated read access to the…
embedded-systems-securityexploitationinformation-gathering+3
5 months ago
CVE-2019-9053-CMS-Made-Simple-2.2.10---SQL-Injection-Exploit preview

CVE-2019-9053-CMS-Made-Simple-2.2.10---SQL-Injection-Exploit

GitHubelizeuopain/cve-2019-9053-cms-made-simple-2.2.10---sql-injection-exploit

Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.
exploitationpassword-crackingpenetration-testing+2
56 months ago
CVE-2018-12633-TPLink-Auth-Bypass preview

CVE-2018-12633-TPLink-Auth-Bypass

GitHubwiliam227user/cve-2018-12633-tplink-auth-bypass

A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).
data-exfiltrationeducationembedded-systems-security+8
19 months ago
CVE-2019-9053-POC preview

CVE-2019-9053-POC

GitHubcaelumisme/cve-2019-9053-poc

Python 3 exploit for CVE-2019-9053, an unauthenticated time-based blind SQL injection in CMS Made Simple < 2.2.10, extracting admin credentials and…
educationexploitationpassword-cracking+3
1 year ago
Venom-JWT preview

Venom-JWT

GitHubz-bool/venom-jwt

针对JWT渗透开发的漏洞验证/密钥爆破工具,针对CVE-2015-9235/空白密钥/未验证签名攻击/CVE-2016-10555/CVE-2018-0114/CVE-2020-28042的结果生成用于FUZZ,也可使用字典/字符枚举(包括JJWT)的方式进行爆破(JWT Crack)
exploitationfuzzingpassword-cracking+3
2881 year ago
CVE-2023-6063-PoC preview

CVE-2023-6063-PoC

GitHubincommatose/cve-2023-6063-poc

A Proof on Concept for CVE-2023-6063, a time-based blind SQL injection vulnerability in WP Fastest Cache ≤1.2.2.
educationexploitationpassword-cracking+3
21 year ago
-exploit-lab preview

-exploit-lab

GitHubhackheart-tech/-exploit-lab

Exploits Python cve-2019-9053– by HackHeart
exploitationpassword-crackingpenetration-testing+2
1 year ago
CVE-2019-9053-port-py3 preview

CVE-2019-9053-port-py3

GitHubdel0x3/cve-2019-9053-port-py3

CVE-2019-9053.
educationexploitationpassword-cracking+3
1 year ago
CMS-Made-Simple-2.2.9-Unauthenticated-SQL-Injection-Exploit-CVE-2019-9053- preview

CMS-Made-Simple-2.2.9-Unauthenticated-SQL-Injection-Exploit-CVE-2019-9053-

GitHubhf3cyber/cms-made-simple-2.2.9-unauthenticated-sql-injection-exploit-cve-2019-9053-

Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…
exploitationinformation-gatheringpassword-cracking+3
1 year ago
CVE-2019-9053-Exploit-Python-3 preview

CVE-2019-9053-Exploit-Python-3

GitHubmahamedm/cve-2019-9053-exploit-python-3

The exploit is edited to work with different text encodings and Python 3 and is compatible with CMSMS version 2.2.9 and below.
exploitationpassword-crackingpenetration-testing+2
81 year ago
CVE-2023-32784-EXPLOIT-REPORT preview

CVE-2023-32784-EXPLOIT-REPORT

GitHubdev0558/cve-2023-32784-exploit-report

Educational demonstration of CVE-2023-32784 KeePass master password recovery via memory dump analysis, with step-by-step exploit setup and mitigation…
digital-forensicseducationexploitation+3
1 year ago
SimpleCTF-UpdatedExploit preview

SimpleCTF-UpdatedExploit

GitHubdh4nuj4/simplectf-updatedexploit

This script is a modified version of the original exploit by Daniele Scanu which exploits an unauthenticated SQL injection vulnerability in CMS Made…
exploitationpassword-crackingpenetration-testing+2
62 years ago
bw-dump preview

bw-dump

GitHubmarkuta/bw-dump

A proof-of-concept for (CVE-2023-38840) that extracts plaintext master passwords from a locked Bitwarden vault.

digital-forensicsexploitationforensics+4
422 years ago
Previous12Next