
CVE-2019-9053
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
exploitationpassword-crackingpenetration-testing+3
11
4nner/cve-2019-9053Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
 rideckszz/poc-cve-2019-9053
PoC didático em Python 3 para a CVE-2019-9053, uma SQL Injection time-based blind no CMS Made Simple <= 2.2.9. Esta versão foi adaptada para uso em…
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
 jeevananand1202/penetration-test
Full penetration test report against `IP` (Ubuntu VM). Attack chain: directory enumeration → backup file discovery → password cracking → CMS file…
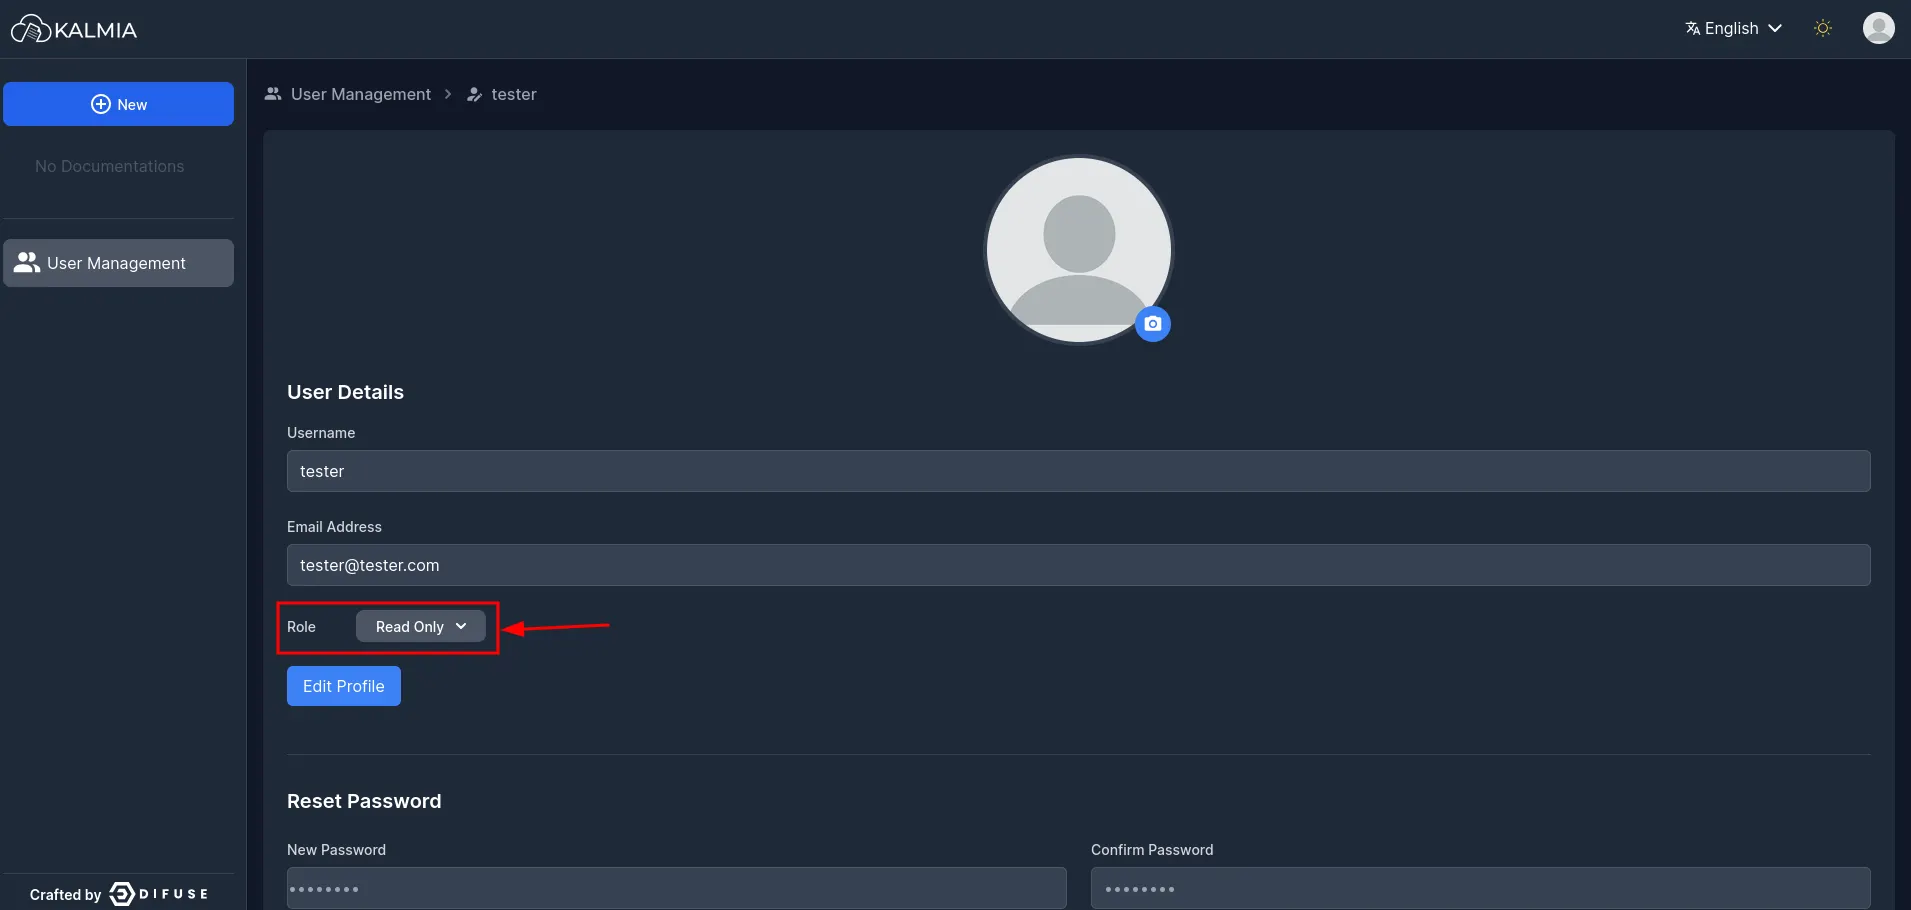 noxurge/cve-2025-65900
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…
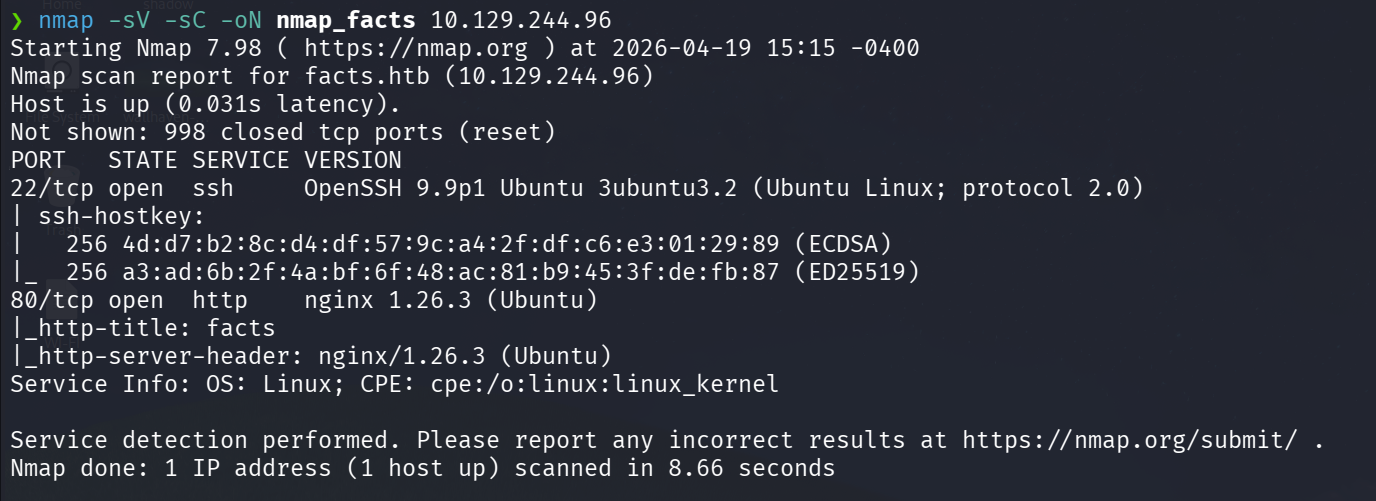 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
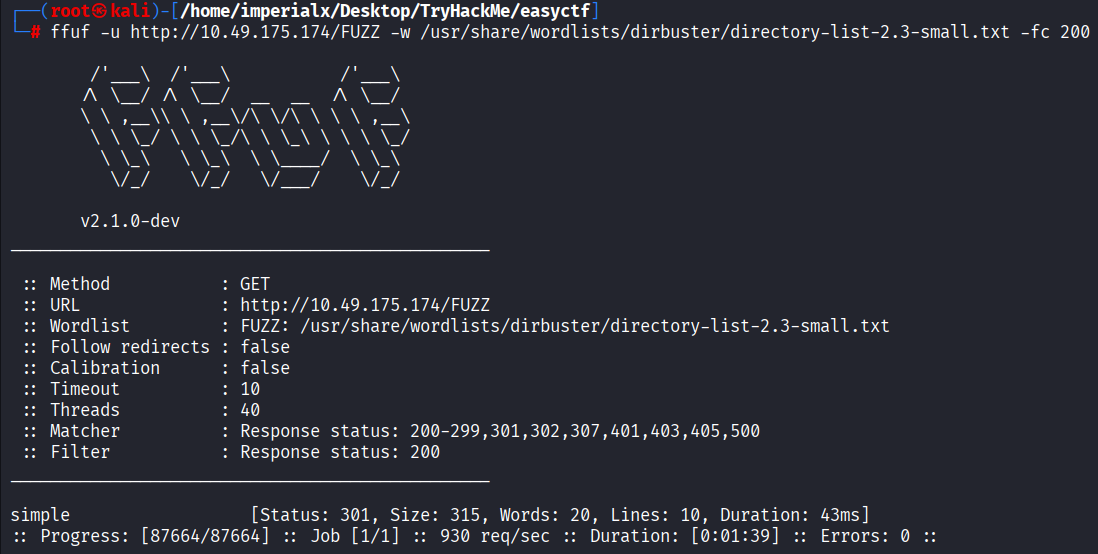 imperialx1104/simple-ctf-writeup
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…
 elizeuopain/cve-2019-9053-cms-made-simple-2.2.10---sql-injection-exploit
Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.
 perseus99999/cve-2019-9053-working-
CMS Made Simple < 2.2.10 - SQL Injection . Actual working version
 mahamedm/cve-2019-9053-exploit-python-3
The exploit is edited to work with different text encodings and Python 3 and is compatible with CMSMS version 2.2.9 and below.
 kalidas-7/cve-2019-9053
Unauthenticated time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9. Extracts admin credentials and optionally cracks password hashes…
 tim-karov/cmsms-sqli
Python3 exploit for CVE-2019-9053 (CMS Made Simple <= 2.2.9 SQLi). No deps, time-based blind SQLi → admin creds dump. HTB Writeup owned.
 jagdeepsinghceh/cms-made-simple-python3
Python3-converted exploit and research notes for CMS Made Simple (CVE-2019-9053) — Unauthenticated SQL Injection vulnerability. Includes original…
 jtoalu/ctf-cve-2019-9053-gtfobins
Step-by-step CTF walkthrough demonstrating CVE-2019-9053 SQL injection exploitation and GTFOBins-based privilege escalation on a CMS Made Simple…
 hf3cyber/cms-made-simple-2.2.9-unauthenticated-sql-injection-exploit-cve-2019-9053-
Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…
 del0x3/cve-2019-9053-port-py3
CVE-2019-9053.
 itzr1g/cve-2019-9053
Python exploit for CVE-2019-9053 targeting CMS Made Simple with SQL injection detection and password hash cracking via wordlist, featuring argparse…
 vedantrana73/cve-2019-9053-py3
Unauthenticated time-based blind SQL injection exploit for CMS Made Simple ≤ 2.2.9 (CVE-2019-9053), ported to Python 3.