
CVE-2019-9053
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
exploitationpassword-crackingpenetration-testing+3
11
4nner/cve-2019-9053Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
 nyxrecon/sudo-agent-ctf-
Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.
 rideckszz/poc-cve-2019-9053
PoC didático em Python 3 para a CVE-2019-9053, uma SQL Injection time-based blind no CMS Made Simple <= 2.2.9. Esta versão foi adaptada para uso em…
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
 wiliam227user/cve-2018-12633-tplink-auth-bypass
A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).
 z-bool/venom-jwt
针对JWT渗透开发的漏洞验证/密钥爆破工具,针对CVE-2015-9235/空白密钥/未验证签名攻击/CVE-2016-10555/CVE-2018-0114/CVE-2020-28042的结果生成用于FUZZ,也可使用字典/字符枚举(包括JJWT)的方式进行爆破(JWT Crack)
 dh4nuj4/simplectf-updatedexploit
This script is a modified version of the original exploit by Daniele Scanu which exploits an unauthenticated SQL injection vulnerability in CMS Made…
 hackheart-tech/-exploit-lab
Exploits Python cve-2019-9053– by HackHeart
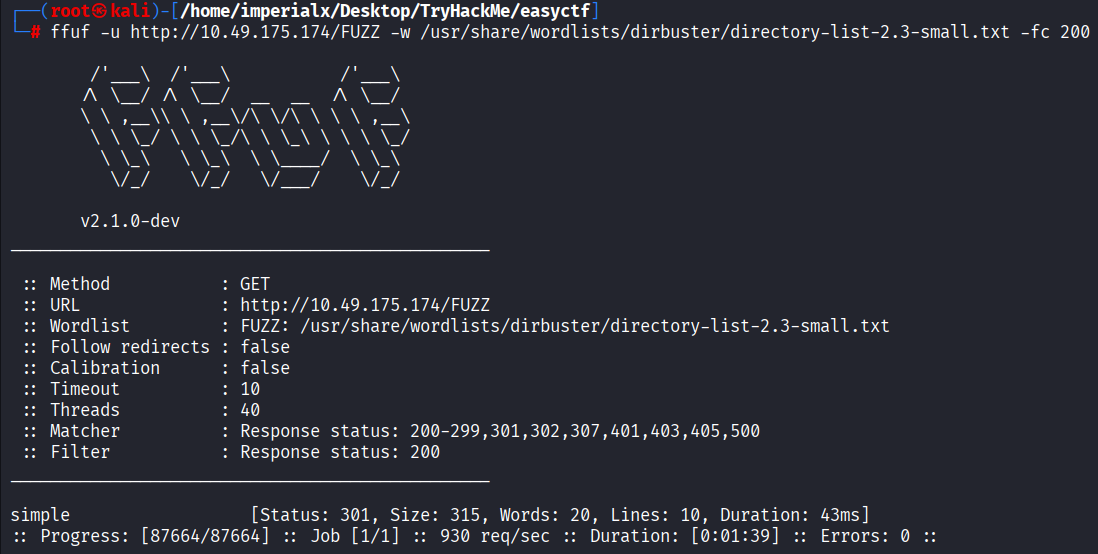 imperialx1104/simple-ctf-writeup
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…
 elizeuopain/cve-2019-9053-cms-made-simple-2.2.10---sql-injection-exploit
Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.
 mahamedm/cve-2019-9053-exploit-python-3
The exploit is edited to work with different text encodings and Python 3 and is compatible with CMSMS version 2.2.9 and below.
 xfox64x/cve-2016-5639
Crestron AirMedia AM-100 Traversal and Hashdump Metasploit Modules
 hf3cyber/cms-made-simple-2.2.9-unauthenticated-sql-injection-exploit-cve-2019-9053-
Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…
 hantwister/o5logon-fetch
Attempts to exploit CVE-2012-3137 on vulnerable Oracle servers
 gquere/cve-2018-16987
Technical disclosure of CVE-2018-16987: cleartext storage of external service passwords in Squash TM administration panel, with CVSS 4.1 scoring and…
 del0x3/cve-2019-9053-port-py3
CVE-2019-9053.
 davcwikla/cve-2019-9053-exploit
Working Python exploit for CVE-2019-9053 with optional password cracking via wordlist. Targets web applications via HTTP URI for automated…
 axcheron/crestron_getsudopwd
Tool to exploit CVE-2018-13341 and recover hidden account password on Crestron devices