

CVE-2022-0169
 x3rx3ssec/cve-2022-0169
CVE-2022-0169 - WordPress Photo Gallery SQLi PoC
educationexploitationinformation-gathering+3
x3rx3ssec/cve-2022-0169CVE-2022-0169 - WordPress Photo Gallery SQLi PoC
 offxec/thedoc
Automates SQL injection exploitation with SQLMAP, crawls for vulnerabilities, extracts database credentials, finds admin login pages, and cracks…
 jtoalu/ctf-cve-2019-9053-gtfobins
Step-by-step CTF walkthrough demonstrating CVE-2019-9053 SQL injection exploitation and GTFOBins-based privilege escalation on a CMS Made Simple…
 tim-karov/cmsms-sqli
Python3 exploit for CVE-2019-9053 (CMS Made Simple <= 2.2.9 SQLi). No deps, time-based blind SQLi → admin creds dump. HTB Writeup owned.
 an00brektn/shirocrack
Simple hash cracker for Apache Shiro hashes written in Golang. Useful for exploiting CVE-2024-4956.
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
 rideckszz/poc-cve-2019-9053
PoC didático em Python 3 para a CVE-2019-9053, uma SQL Injection time-based blind no CMS Made Simple <= 2.2.9. Esta versão foi adaptada para uso em…
 boon-rekcah/cms-made-simple-2.2.9-cve-2019-9053
Python 3 exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks…
 kalidas-7/cve-2019-9053
Unauthenticated time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9. Extracts admin credentials and optionally cracks password hashes…
 del0x3/cve-2019-9053-port-py3
CVE-2019-9053.
 vedantrana73/cve-2019-9053-py3
Unauthenticated time-based blind SQL injection exploit for CMS Made Simple ≤ 2.2.9 (CVE-2019-9053), ported to Python 3.
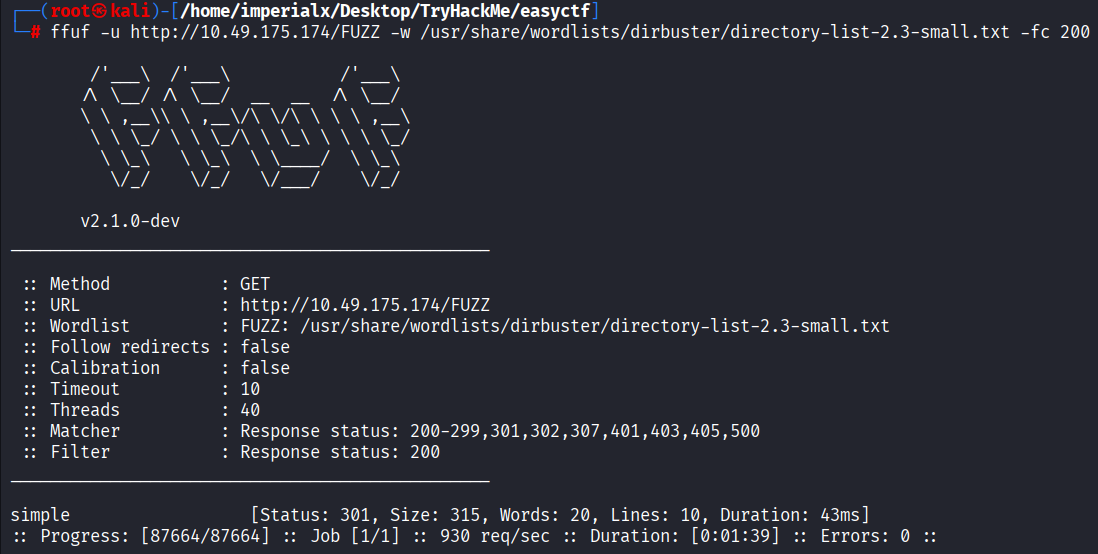 imperialx1104/simple-ctf-writeup
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…
 caelumisme/cve-2019-9053-poc
Python 3 exploit for CVE-2019-9053, an unauthenticated time-based blind SQL injection in CMS Made Simple < 2.2.10, extracting admin credentials and…
 perseus99999/cve-2019-9053-working-
CMS Made Simple < 2.2.10 - SQL Injection . Actual working version
 elizeuopain/cve-2019-9053-cms-made-simple-2.2.10---sql-injection-exploit
Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.
 azrenom/cms-made-simple-2.2.9-cve-2019-9053
Exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks the…
 hf3cyber/cms-made-simple-2.2.9-unauthenticated-sql-injection-exploit-cve-2019-9053-
Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…
 dh4nuj4/simplectf-updatedexploit
This script is a modified version of the original exploit by Daniele Scanu which exploits an unauthenticated SQL injection vulnerability in CMS Made…