
TeamFiltration
 flangvik/teamfiltration
Cross-platform framework for enumerating O365 accounts, password spraying, exfiltrating emails/Teams/OneDrive data, and backdooring EntraID accounts…
authenticationcloud-securitydata-exfiltration+3
1.4k
flangvik/teamfiltrationCross-platform framework for enumerating O365 accounts, password spraying, exfiltrating emails/Teams/OneDrive data, and backdooring EntraID accounts…
 urbanadventurer/username-anarchy
Username tools for penetration testing
 r3nt0n/bopscrk
Generates targeted password wordlists by combining personal info, applying case/leet transforms, and scraping artist lyrics for enhanced cracking…
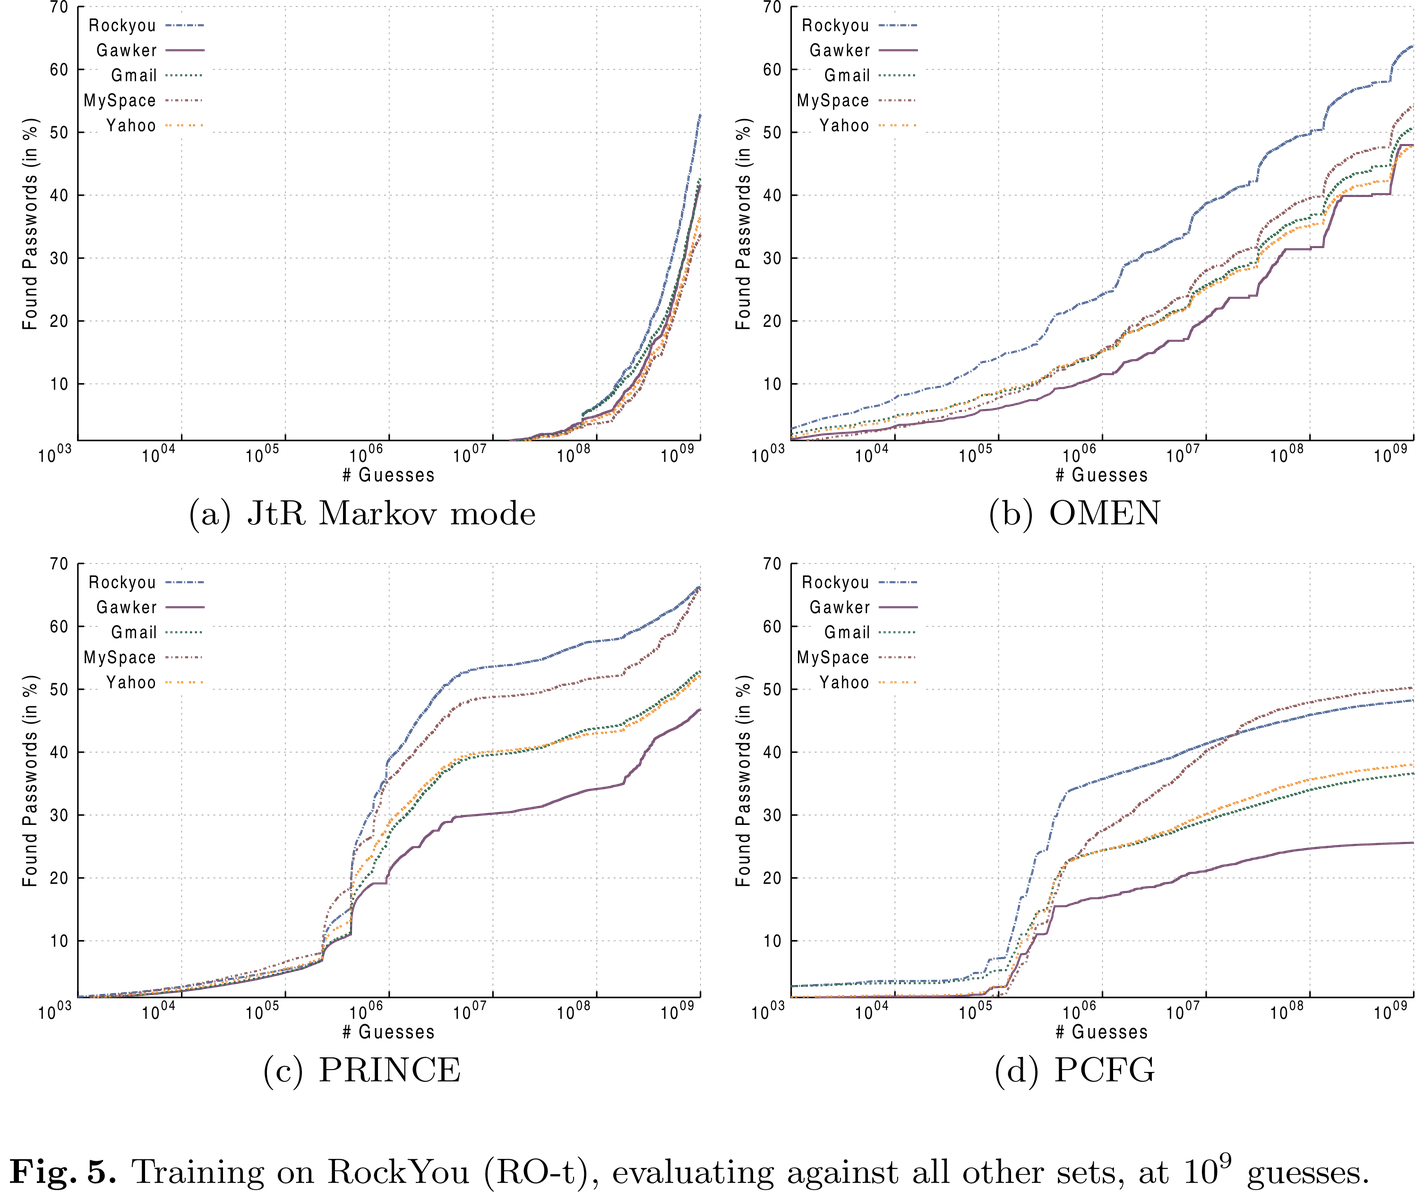 rub-syssec/omen
Markov model-based password guesser in C that enumerates candidates by probability, generating most likely passwords first for hash cracking via…
 m8sec/enumdb
Relational database brute force and post exploitation tool for MySQL and MSSQL
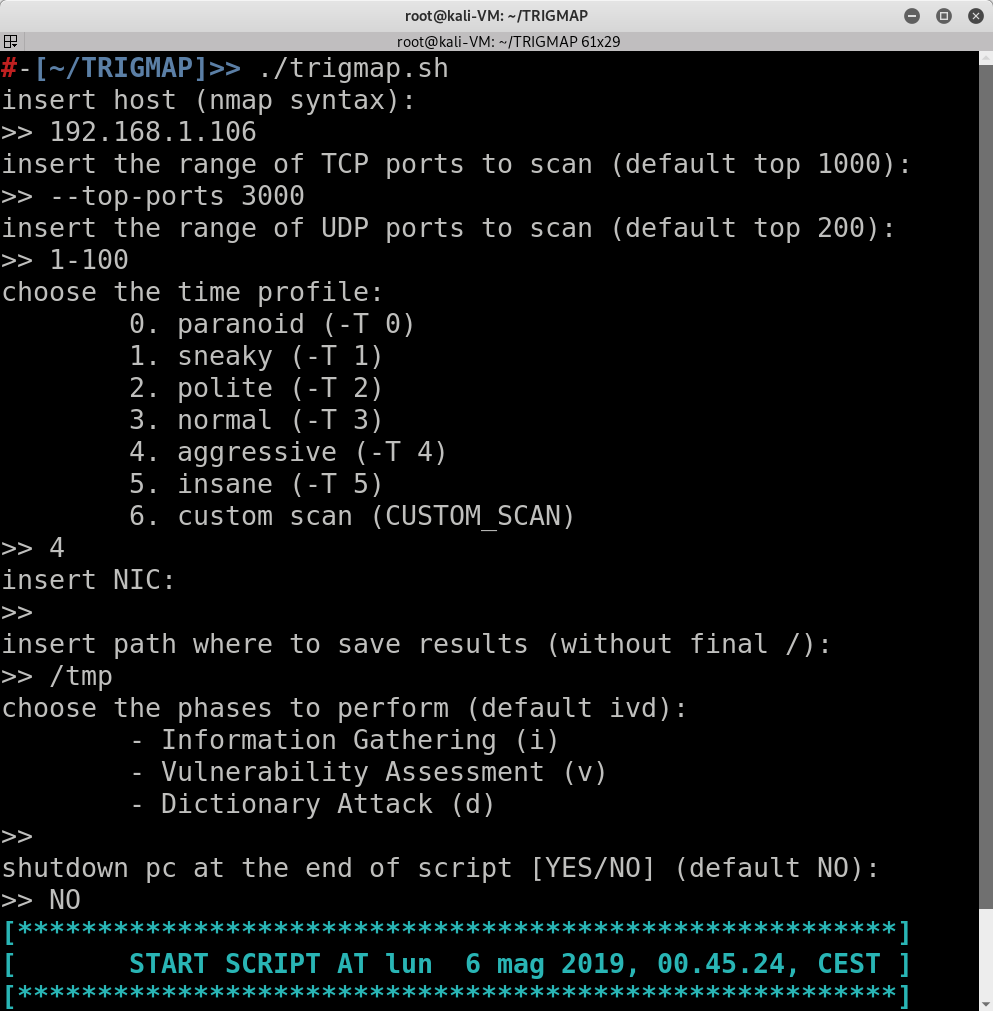 leviathan36/trigmap
A wrapper for Nmap to quickly run network scans
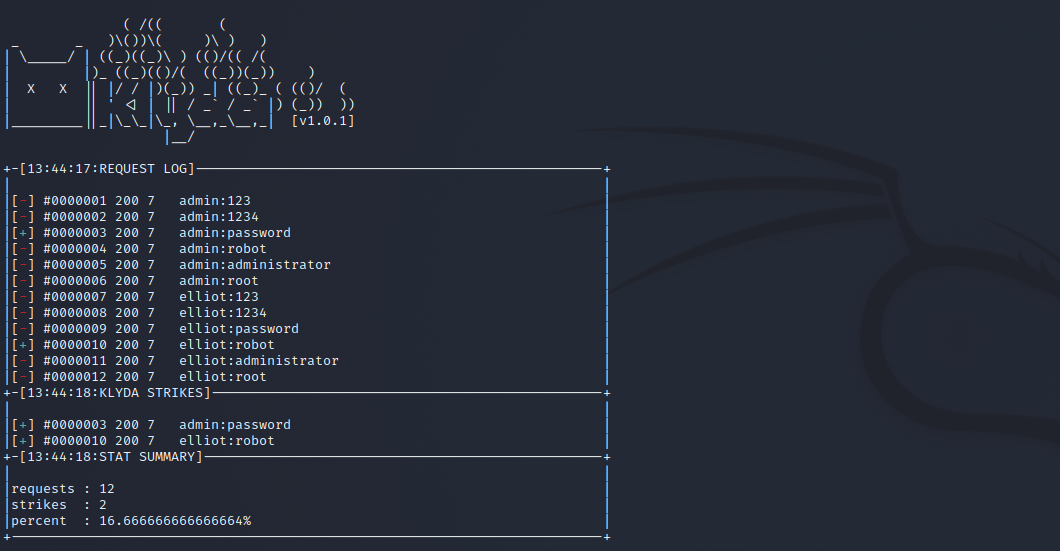 hcbaker/klyda
Highly configurable script for dictionary/spray attacks against online web applications.
 xewdy444/netgrave
A tool for retrieving login credentials from Netwave IP cameras using a memory dump vulnerability (CVE-2018-17240)
 emrekybs/pikachu-smtp
Simple python script for brute force attack to smtp users
 groppoxx/cve-2025-25198-poc
PoC for CVE-2025-25198: automated Host header poisoning test for Mailcow - HTTPS listener, automatic cookie/CSRF handling, captures first reset link.
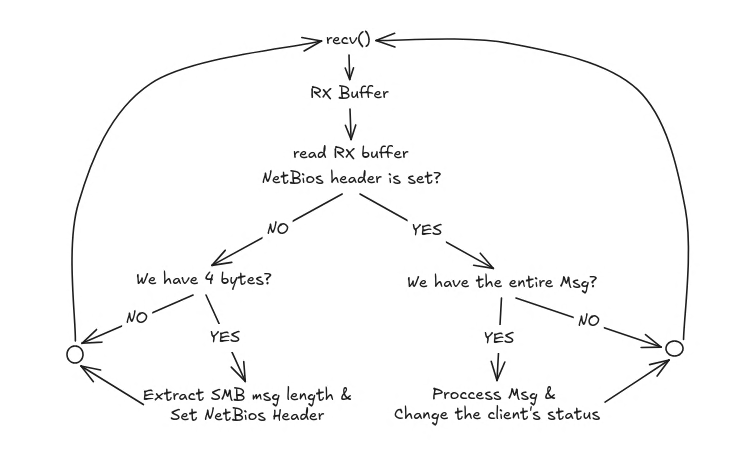 lcky00/impostor
SMB1 server for NTLMv2 hash interception, written in C.
 e-renna/cve-2019-9053
CVE-2019-9053 Exploit for Python 3
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 filipkarc/poc-ubuntutouch-pin-privesc
CVE-2022-40297 - Proof of Concept: Privilege escalation in Ubuntu Touch 16.04 - by PIN Bruteforce
 0x0mastermind0x0/instagram-brute-force-2024
Automated Instagram credential brute-forcing tool with CPU/GPU support, designed for password guessing attacks against target accounts using Chrome…
 revshellxd/lfi-destruction
This program Prompts you for the Local File Inclusion information and will automatically search the /etc/passwd and using the users names found will…

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 aramosf/cve-2026-61500
Python PoC and Docker lab for CVE-2026-61500: recovers Rejetto HFS V8 PRNG state to forge an admin session cookie and achieve RCE via server_code.