
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
combine_harvester — Rust in-memory dumper | Kitploit
Tools/GitHubGitHub/m3f157o/combine_harvester
Password AttacksPost-ExploitationPenetration TestingRed Teaming
GitHubm3f157o/combine_harvester

combine_harvester

Rust in-memory dumper

View Repository
10917353 years agoReviewed by Kitploit
Share

combine

Check your windows local security authority credential's safety with this awesome tool.

Coupled dump decoder @ https://github.com/ruggi99/combine-decoder

Introduction

By readapting the safetydump rust library (many thanks to the author!!!), I have been able to EASILY bypass all the countermeasures put in place by most EDRs, except Kaspersky EDR, and TrendMicro (new detection, from a couple hours ago)

dbghelp!MiniDumpWriteDump with a custom callback could be used, until a year ago, to bypass most antivirus/EDR solutions.

Now, most of them EASILY recognize statically or behaviorally the system API usage pattern, for programs written in languages such as C++, Delphi and C#. (it could be possible anyway thanks to undocumented NtOpenProcessEx but that's another story)

If you have a Go implementation, please give me feedback. I'm on it but still have some bugs related to memory size

I suspect that there is still no way to monitor the MiniDumpWriteDump callback, and all the protection against a possible credential dump via this technique is then entrusted to machine learning detections.
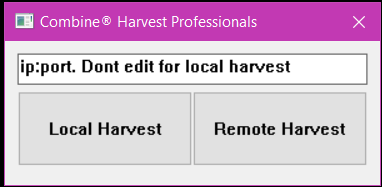
Usage

GUI

image

CMD

image

DECRYPT

image

References

Done thanks to

  • https://loong716.top/posts/lsass/
  • https://www.thehacker.recipes/ad/movement/credentials/dumping/lsass
  • https://danielsauder.com/2016/02/06/memdumps-volatility-mimikatz-vms-part-1-mimikatz-lsass-exe-dump/
  • https://www.whiteoaksecurity.com/blog/attacks-defenses-dumping-lsass-no-mimikatz/
  • https://www.ired.team/offensive-security/credential-access-and-credential-dumping/dumping-credentials-from-lsass.exe-process-memory

Many code snippets are from

  • https://github.com/postrequest/safetydump (very big help!!! thanks!!!)
  • https://github.com/azazelm3dj3d/lsass-dump/blob/main/Dump/Dump.cpp
  • https://rastamouse.me/dumping-lsass-with-duplicated-handles/

Disclaimer

I am not responsible for any improper usage of this tool. This is meant for research and security testing purpose.

Notes

The only effective mitigations (that I know of) against this sub-technique are RunAsPPL and CredentialGuard, but it's not always possible to enable these options.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    837
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    536
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    424
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    294
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    276

Explore all tools

Browse our collection of tools

View all tools →




