Magnohost-Vulnerabilities-pentest

Manual black-box penetration test of MagnoHost and MeteorCloud infrastructure, documenting exposed MariaDB, default credentials, CVE-2024-27102, and…

Manual black-box penetration test of MagnoHost and MeteorCloud infrastructure, documenting exposed MariaDB, default credentials, CVE-2024-27102, and…

Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…

Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…

Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…

Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…

110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.

PoC for CVE-2026-27912 - Windows Kerberos Elevation of Privilege (ResetNightmare). Unauthorized password reset via Kerberos flaw. For security…

A tool to query for the existence of pre-windows 2000 computer objects.

Enhanced version of secretsdump.py from Impacket. Adds multi-threading and accepts an input file with a list of target hosts for simultaneous secrets…

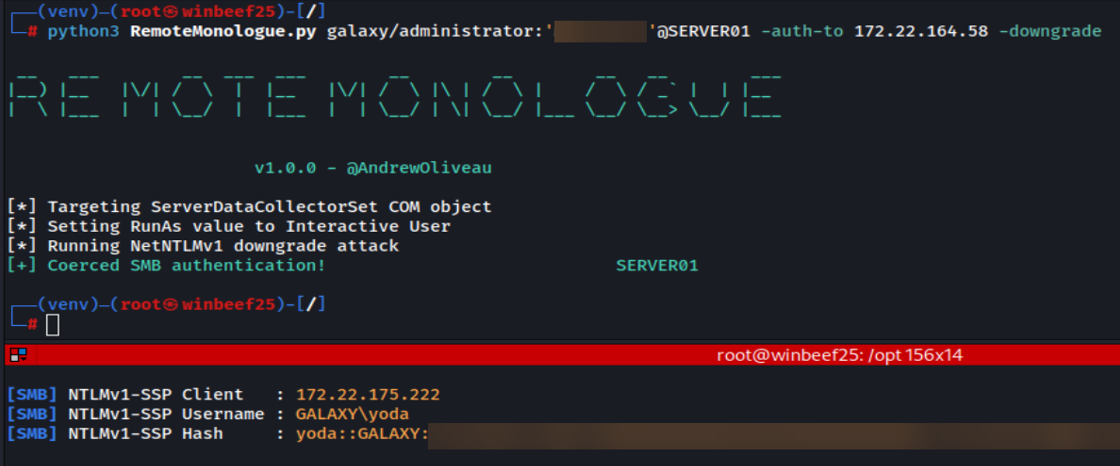
Weaponizing DCOM for NTLM Authentication Coercions

Weaponizing DCOM for NTLM Authentication Coercions

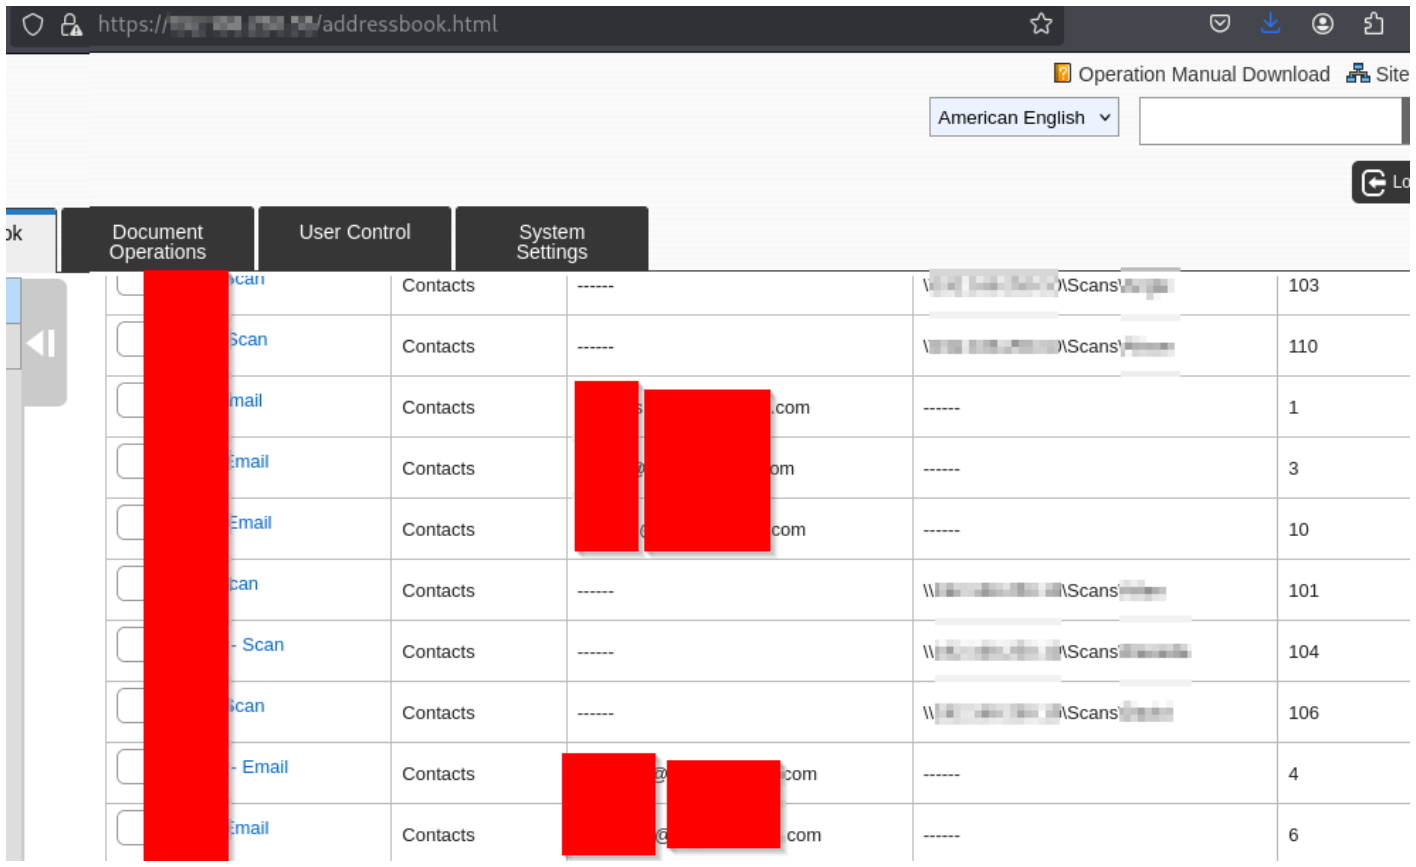
Unauthenticated Address Book Modification on Sharp MX/BP Multifunction Printers


CVE write-up for Active Directory credential exposure vulnerability in Suprema BioStar 2

Opens 1K+ IPs or Shodan search results and attempts to login

Rid_enum is a null session RID cycle attack for brute forcing domain controllers.

Zerologon Check and Exploit - Discovered by Tom Tervoort of Secura and expanded on @Dirkjanm's cve-2020-1472 coded example. This tool will check,…

Microsoft-Outlook-Remote-Code-Execution-Vulnerability